
Open Unified Identities › Human Identities, filter Providers to GCP Identities › User, then select a row to open its details.
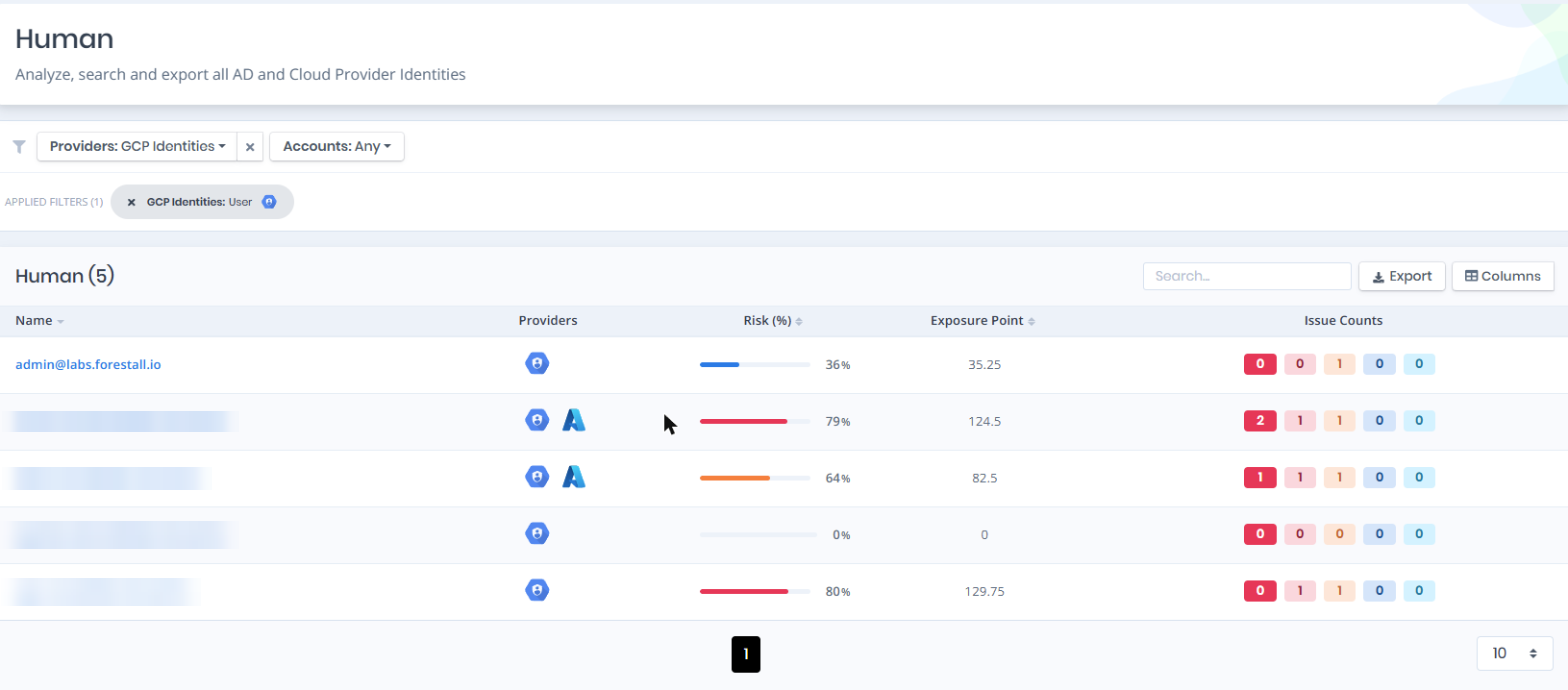
Users
Users Details
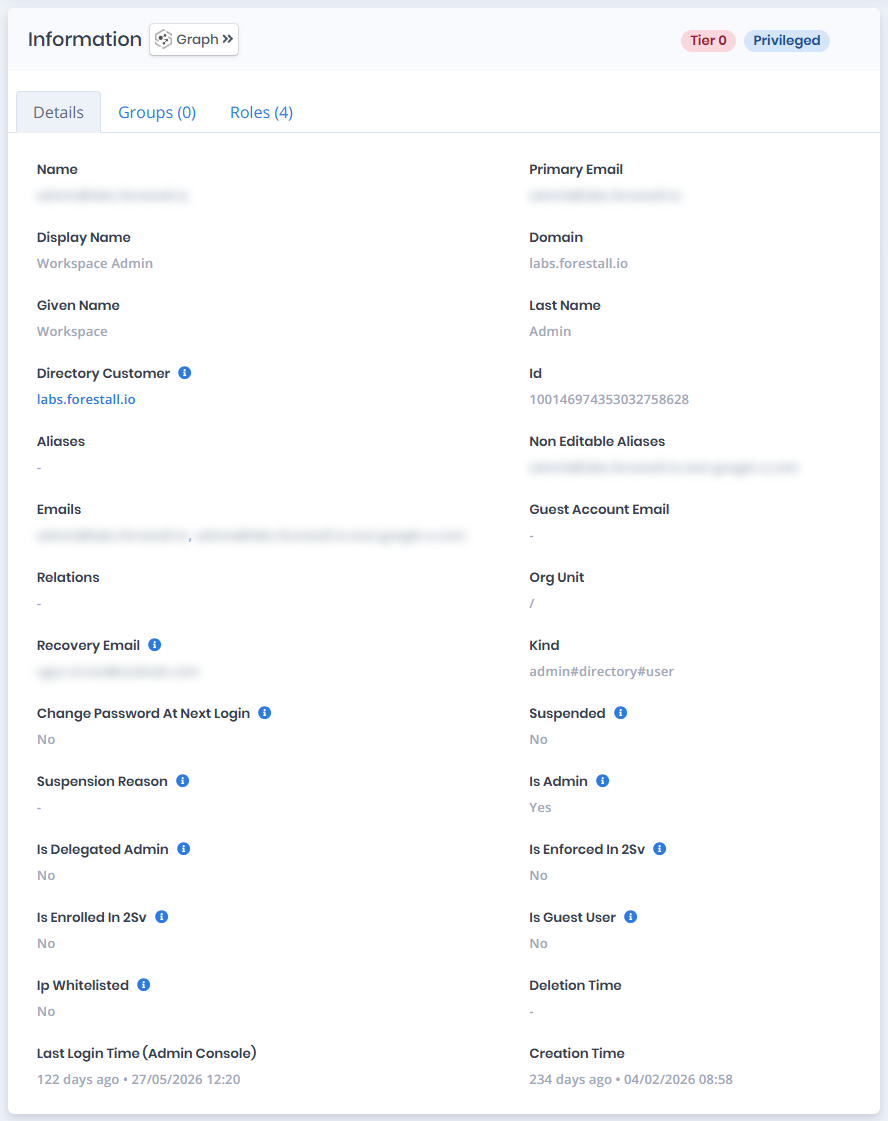
Opening a user shows the Risk and Exposure Point in the header, the Information card with the Details, Groups and Roles tabs, and an Issues panel when the user has issues.
You can analyze the object in the Graph by clicking the Graph » button next to the Information title. For a shadow admin the button reads Admin Path » and opens the shortest path to admin objects (see Object Detail Pages).
Users Details
Information
Information card can contain different badges to highlight important attributes.
| Badge | Description |
|---|---|
| Tier 0 / Tier 2 | The tier of the user. |
| Privileged | Indicates that the user is privileged. |
| Shadow | Indicates that the object can compromise admin objects with at least one attack path. |
The Details tab contains attributes about the GCP User account retrieved from Google Workspace Directory. Several attributes show an info icon next to their name with a short explanation.
| Attribute | Description |
|---|---|
| Name | The full email address used as the unique identifier for the user account. |
| Primary Email | The primary email address of the user. |
| Display Name | The display name of the user account. |
| Domain | The Google Workspace domain the user belongs to (e.g., labs.forestall.io). |
| Given Name | The first name of the user. |
| Last Name | The last name (family name) of the user. |
| Directory Customer | The Google Workspace customer of the user (e.g., labs.forestall.io); links to the customer details. |
| Id | The unique numeric identifier of the user account. |
| Aliases | Additional email aliases assigned to the user. |
| Non Editable Aliases | System-assigned aliases that cannot be modified (e.g., [email protected]). |
| Emails | All email addresses associated with the user account. |
| Guest Account Email | The email address if the account is a guest account. |
| Relations | Relationships defined for the user in the directory. |
| Org Unit | The organizational unit the user belongs to (e.g., Developers); links to the organizational unit details, or shows the path if the OU was not enumerated. |
| Recovery Email | The recovery email address configured for the user account. |
| Kind | The type identifier of the directory resource (e.g., admin#directory#user). |
| Change Password At Next Login | Indicates whether the user is required to change their password on next login. |
| Suspended | Indicates whether the user account is currently suspended. |
| Suspension Reason | The reason provided for the account suspension, if applicable. |
| Is Admin | Indicates whether the user has super administrator privileges in Google Workspace. |
| Is Delegated Admin | Indicates whether the user has been granted delegated administrator privileges. |
| Is Enforced In 2Sv | Indicates whether two-step verification (2SV) is enforced for the user. |
| Is Enrolled In 2Sv | Indicates whether the user is enrolled in two-step verification (2SV). |
| Is Guest User | Indicates whether the account is classified as a guest user. |
| Ip Whitelisted | Indicates whether the user’s access is restricted to specific whitelisted IP addresses. |
| Deletion Time | The timestamp when the user account was deleted, if applicable. |
| Last Login Time (Admin Console) | The most recent login time recorded for the user in the Admin Console. |
| Creation Time | The timestamp when the user account was created. |
Groups
The Groups tab lists all parent groups above the current User. The Name column links to the group details.
Roles
The Roles tab lists all assigned roles to the current user. The Name column links to the role details.