
User Assigned Identities
Open Unified Identities › Non Human Identities, filter Providers to Azure Resource Management › User Assigned Identity, then select a row to open its details. A user-assigned identity is a standalone managed identity that Azure resources can run as.
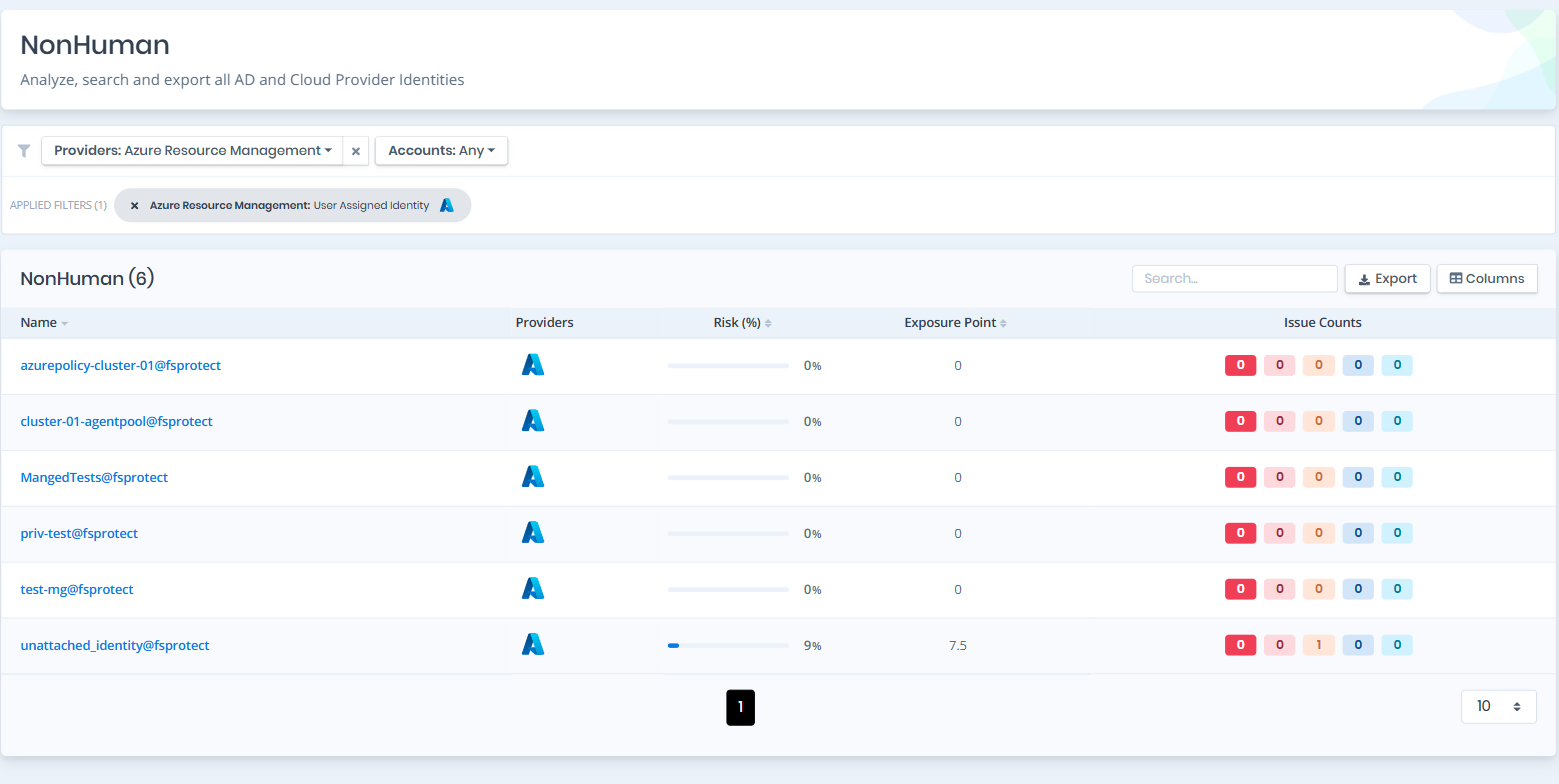
User Assigned Identities
User Assigned Identities Details
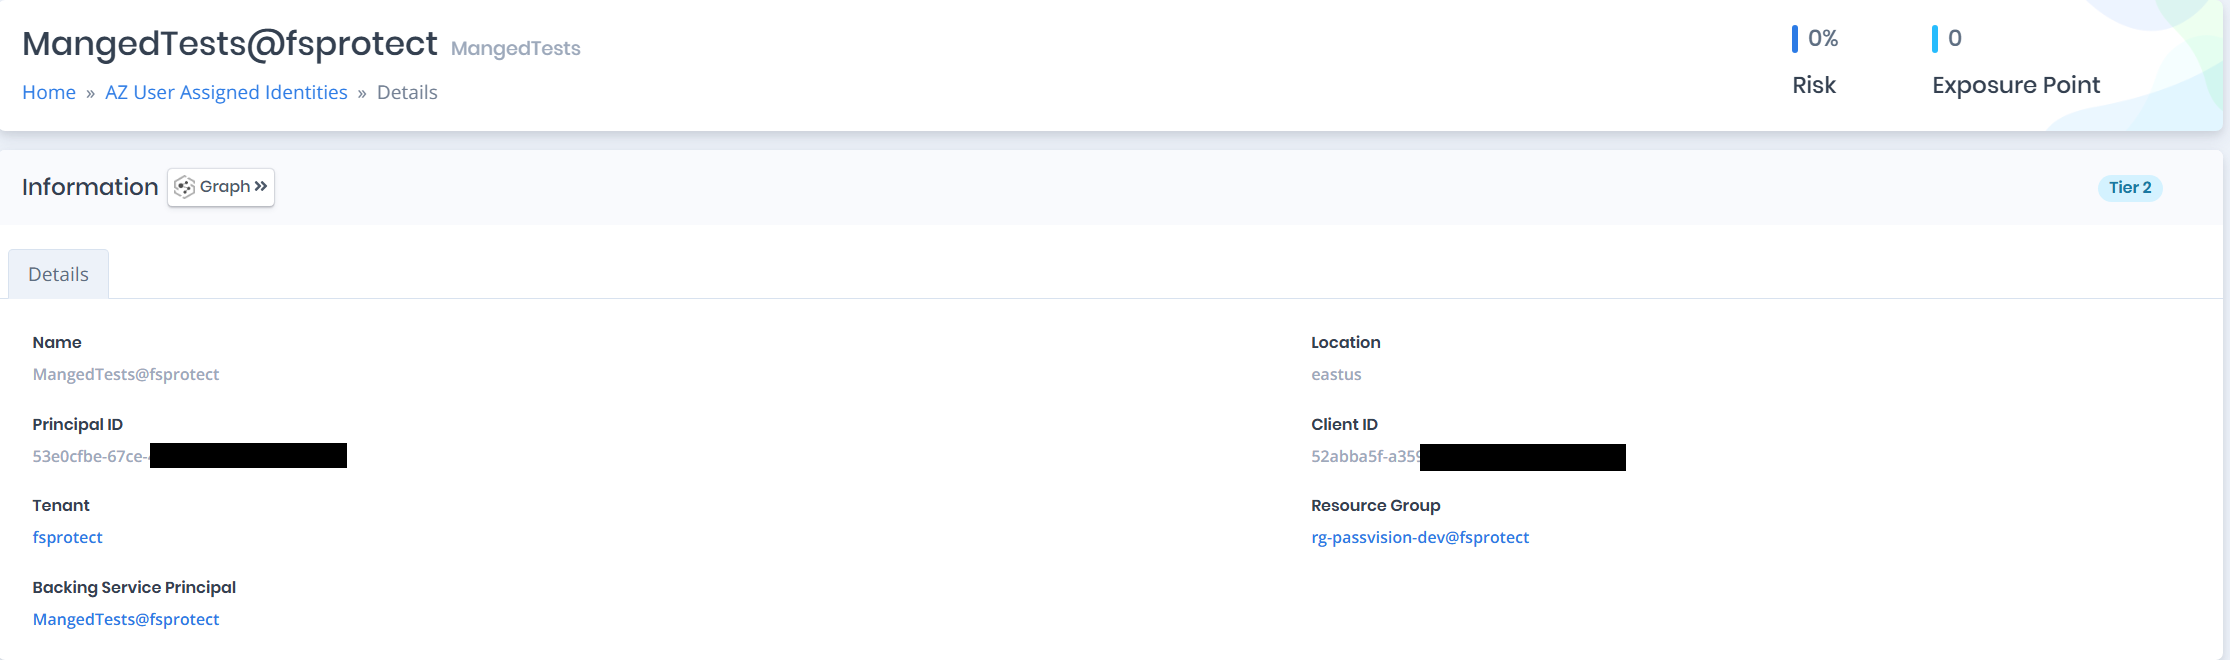
Details page contains the Risk and Exposure Point of the user-assigned identity and the Information pane.
You can analyze the object in the Graph by clicking the Graph » button next to the Information title.
User Assigned Identities Details
Information
Information Pane contains Details.
A Tier 0 or Tier 2 badge on the right of the Information title shows the tier of the user-assigned identity.
Details
Details tab contains attributes below about the AZ user-assigned identity.
| Attribute | Description |
|---|---|
| Name | The display name of the user-assigned identity with tenant suffix |
| Location | The Azure region where the user-assigned identity is deployed |
| Principal ID | The object ID of the service principal in Entra ID that backs this identity |
| Client ID | The client (application) ID associated with this identity |
| Tenant | The tenant the user-assigned identity belongs to |
| Resource Group | The resource group the user-assigned identity is associated with |
| Backing Service Principal | The Entra ID service principal that the user-assigned identity runs as |
A user-assigned managed identity is an identity itself: it is backed by a service principal in Entra ID and can be assigned to multiple Azure resources.