
Open Unified Identities › Resources, filter Providers to Azure Resource Management › ARM Role, then select a row to open its details.
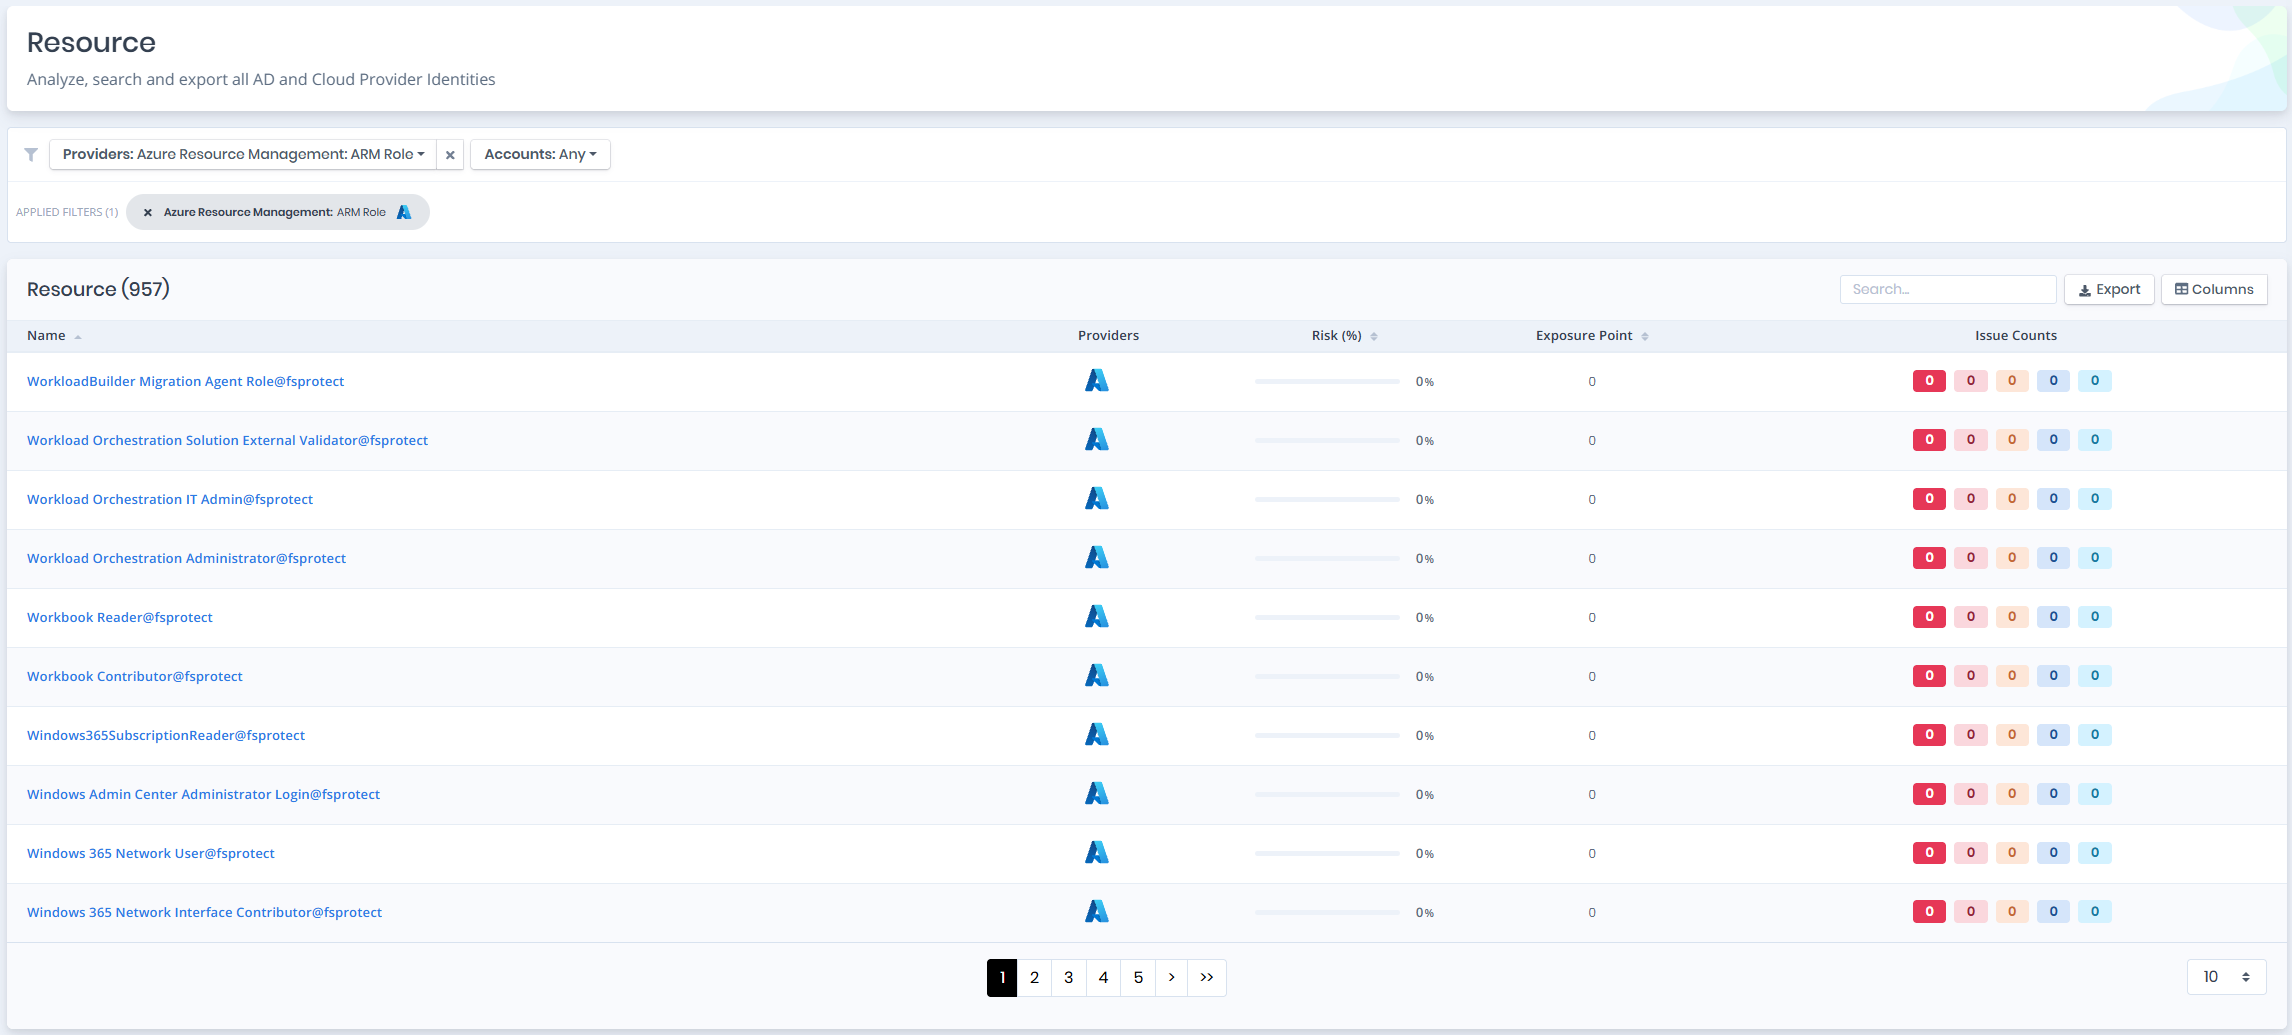
Azure Resource Management Roles
ARM Roles Details
Details page contains the Risk and Exposure Point of the role and the Information pane.
You can analyze the object in the Graph by clicking the Graph » button next to the Information title.
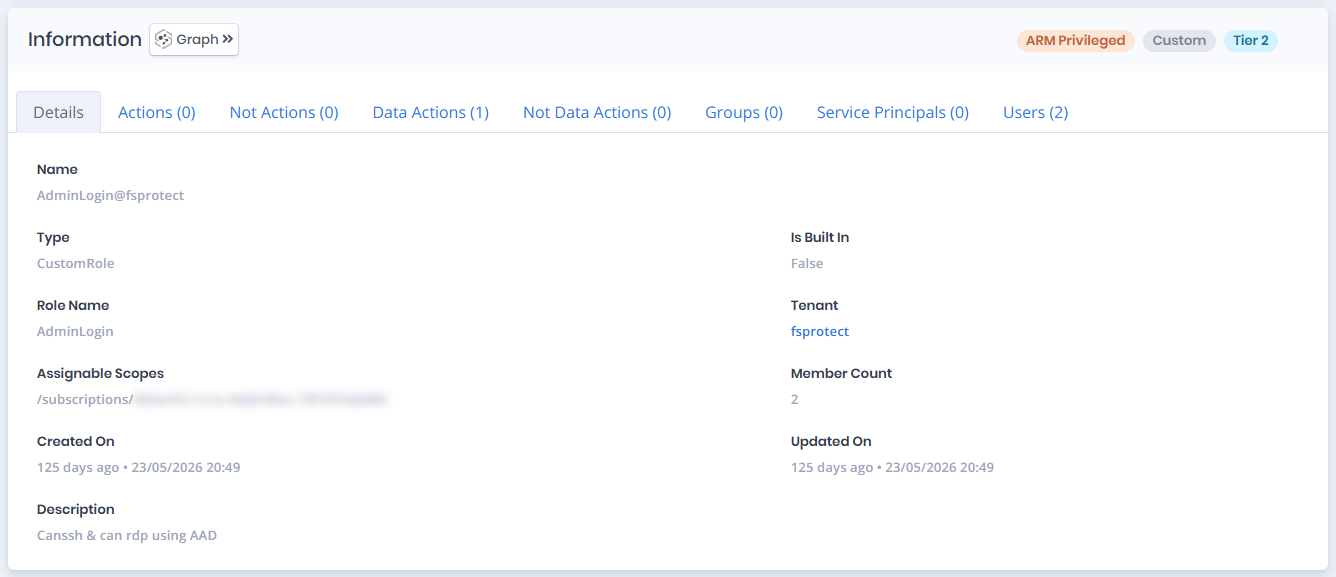
ARM Roles Details
Information
Information Pane can contain different badges to highlight important attributes.
| Badge | Description |
|---|---|
| Privileged | Indicates the role has privileged permissions |
| ARM Privileged | Indicates the role grants privileged actions in the Azure Resource Manager plane |
| Built-In | Indicates the role is a built-in Azure ARM role |
| Custom | Indicates the role is a custom role |
| Tier 0 | Indicates the role is classified as Tier 0 |
| Tier 2 | Indicates the role is classified as Tier 2 |
Information Pane contains Details, Actions, Not Actions, Data Actions, Not Data Actions, Groups, Service Principals and Users tabs. Each tab except Details shows the number of rows in its label.
Details
Details tab contains attributes below about the AZ ARM role.
| Attribute | Description |
|---|---|
| Name | The display name of the role with tenant suffix |
| Type | The type of the role (e.g., BuiltInRole) |
| Role Name | The original name of the role without tenant suffix |
| Is Built In | Indicates whether the role is a built-in Azure role |
| Description | A brief description of the role and its permissions |
| Tenant | The tenant the role belongs to |
| Assignable Scopes | The scopes at which the role can be assigned |
| Member Count | The number of members assigned to this role |
| Created On | The date and time when the role was created |
| Updated On | The date and time when the role was last updated |
Actions
Actions tab contains a list of management actions that the role allows. This list identifies the operations that can be performed on Azure resources when the role is assigned.
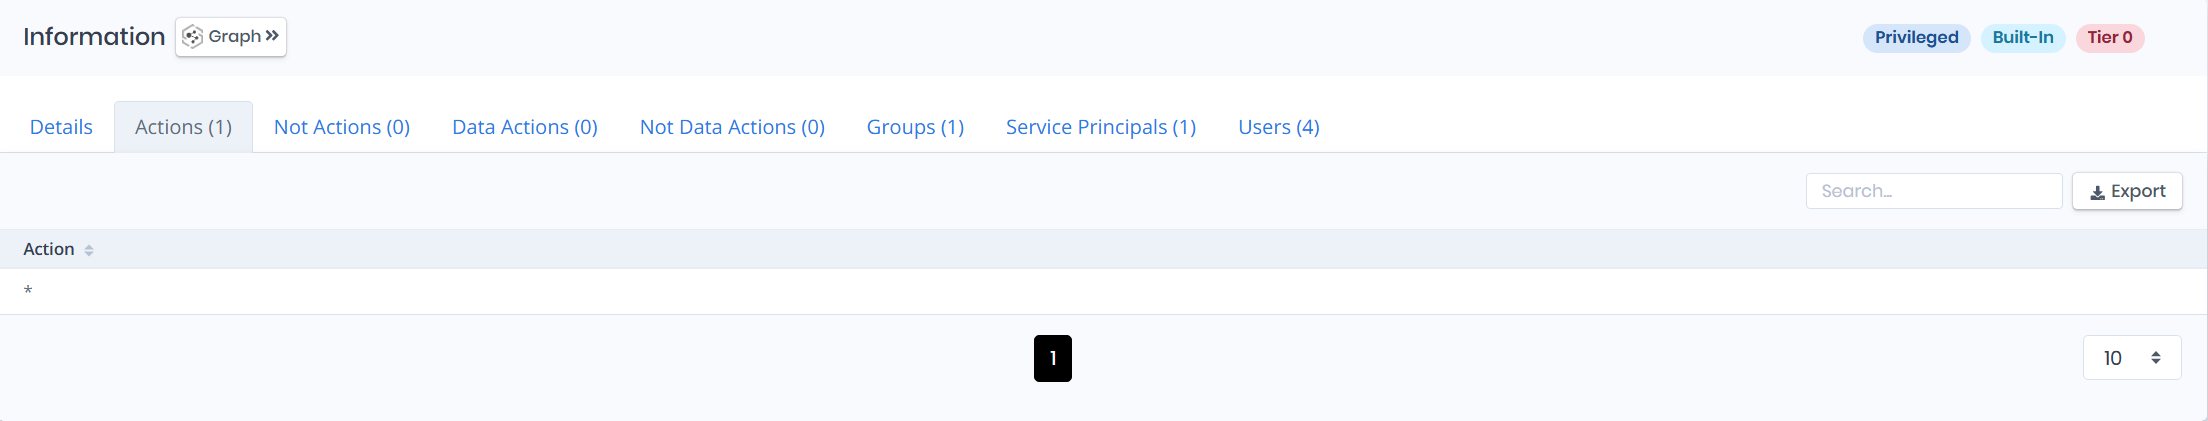
Actions
Not Actions
Not Actions tab contains a list of management actions that are excluded from the role. These are operations that are explicitly denied even if allowed by Actions.
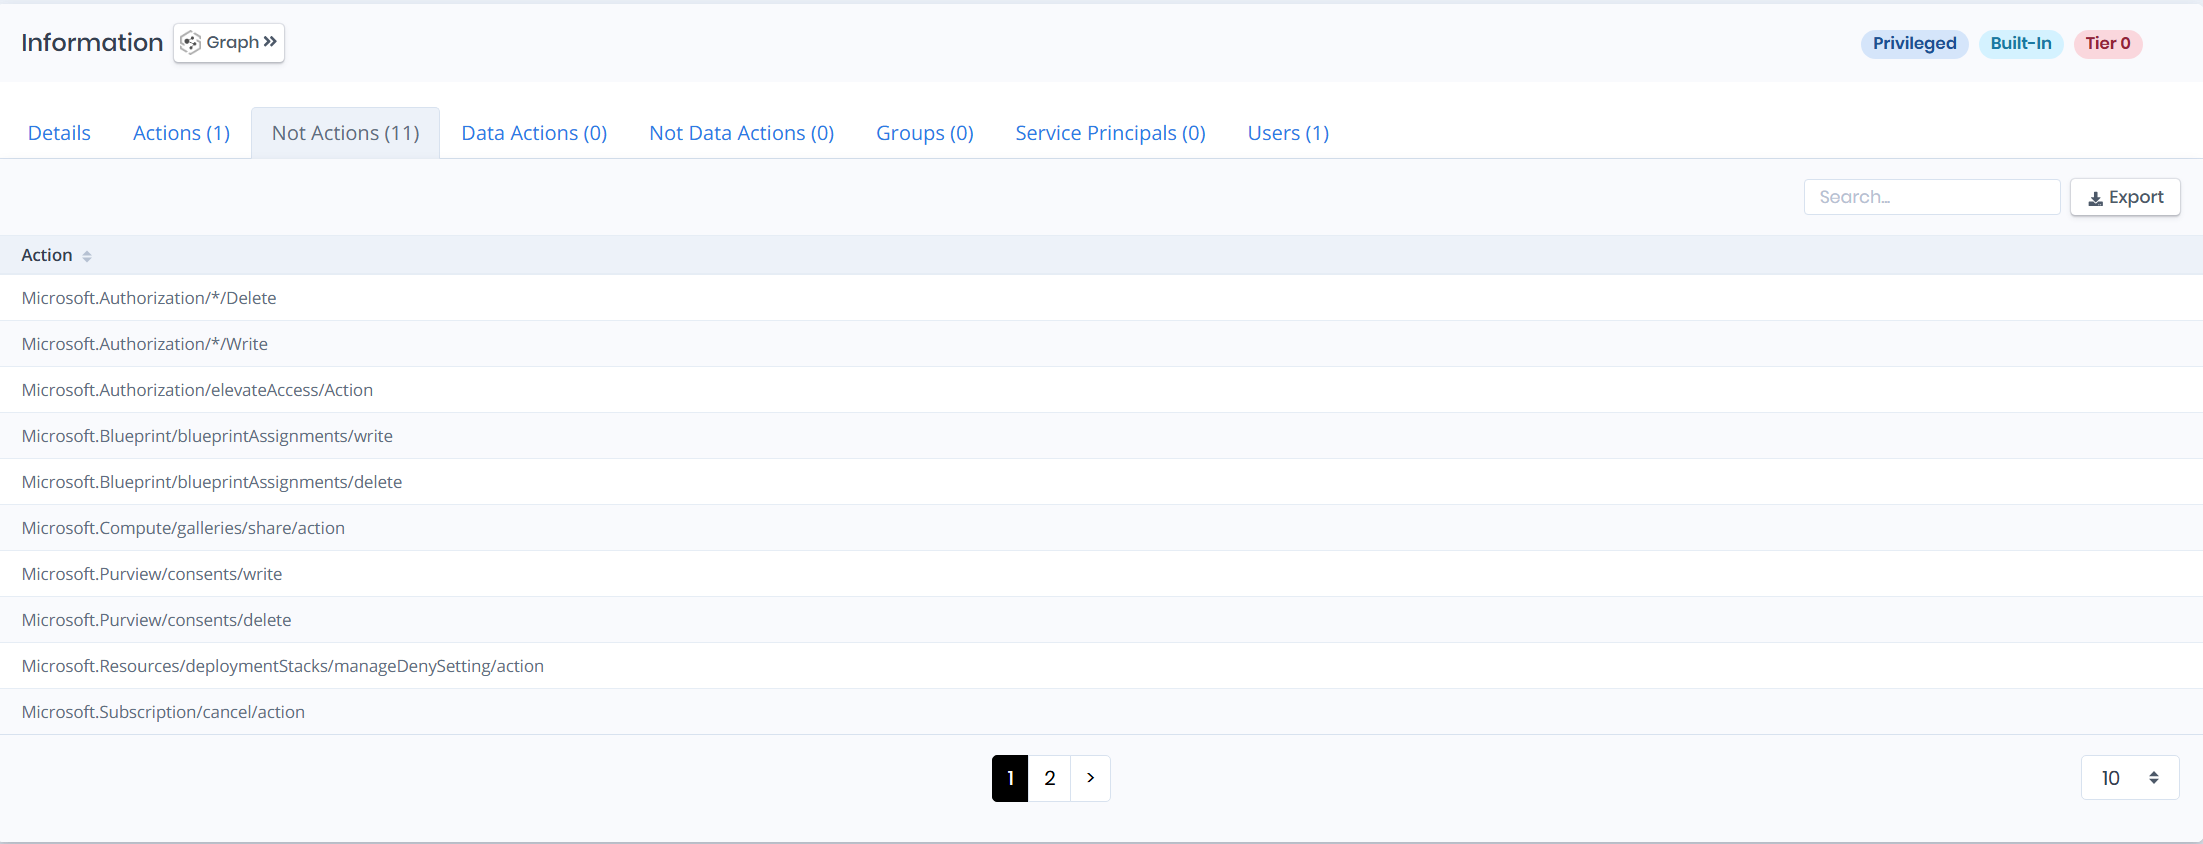
Not Actions
Data Actions
Data Actions tab contains a list of data operations that the role allows. These are operations performed on data within Azure resources (e.g., reading blob data).
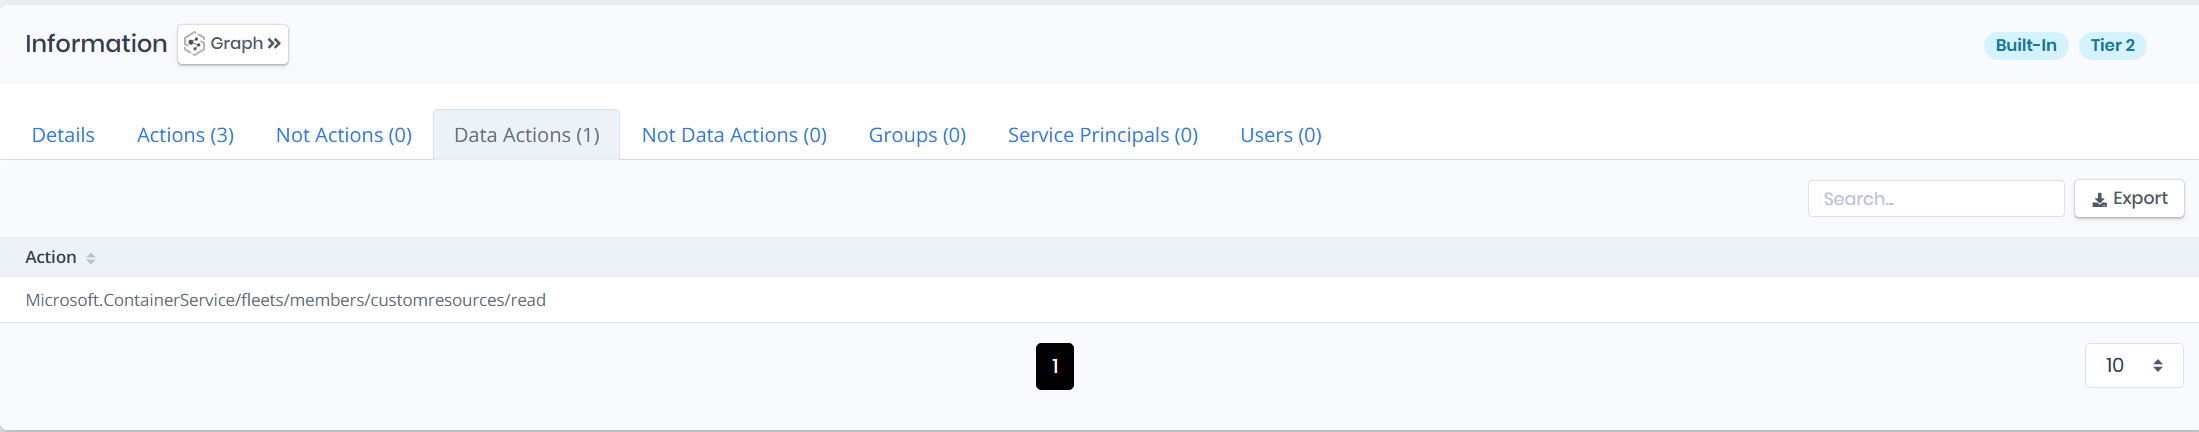
Data Actions
Not Data Actions
Not Data Actions tab contains a list of data operations that are excluded from the role. These are data operations that are explicitly denied even if allowed by Data Actions.
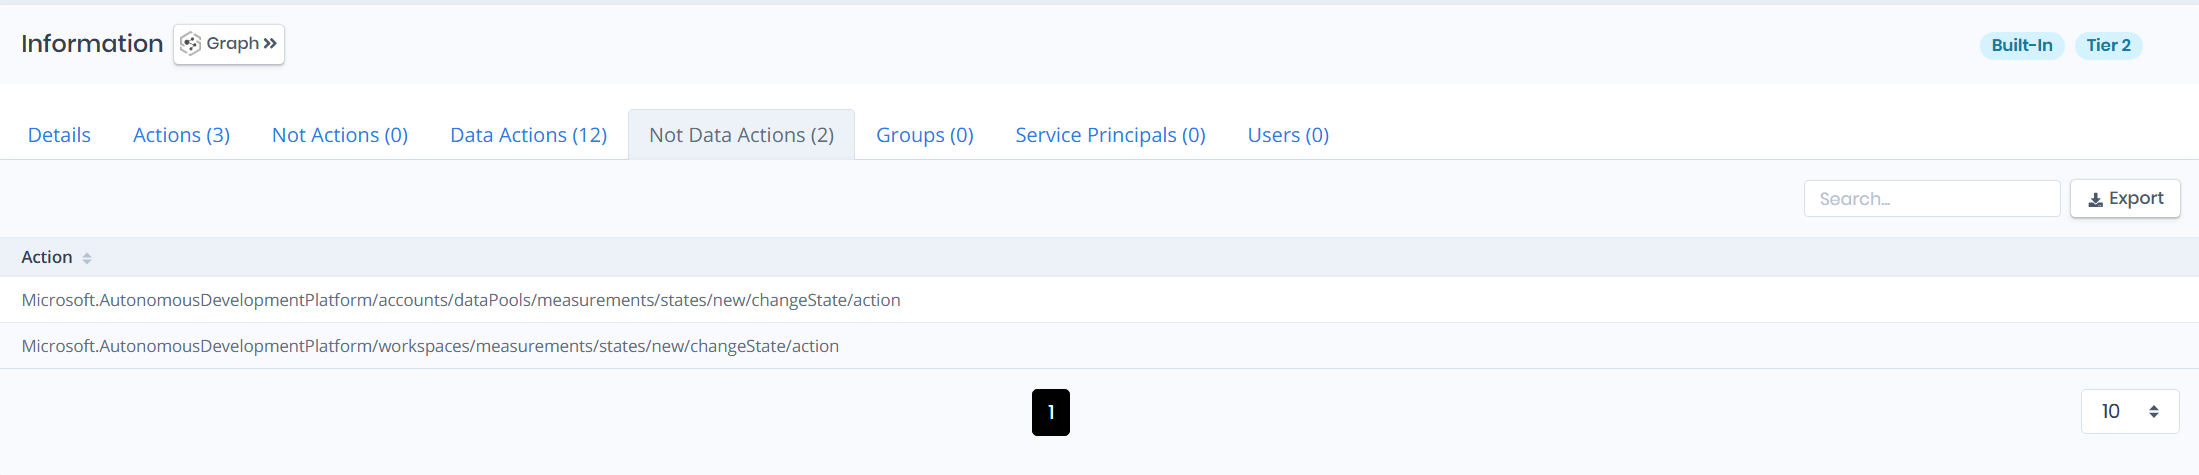
Not Data Actions
Groups
Groups tab contains a list of groups that have been assigned this role. This list also contains Enabled and On Prem Sync Enabled columns to identify the status of these groups.
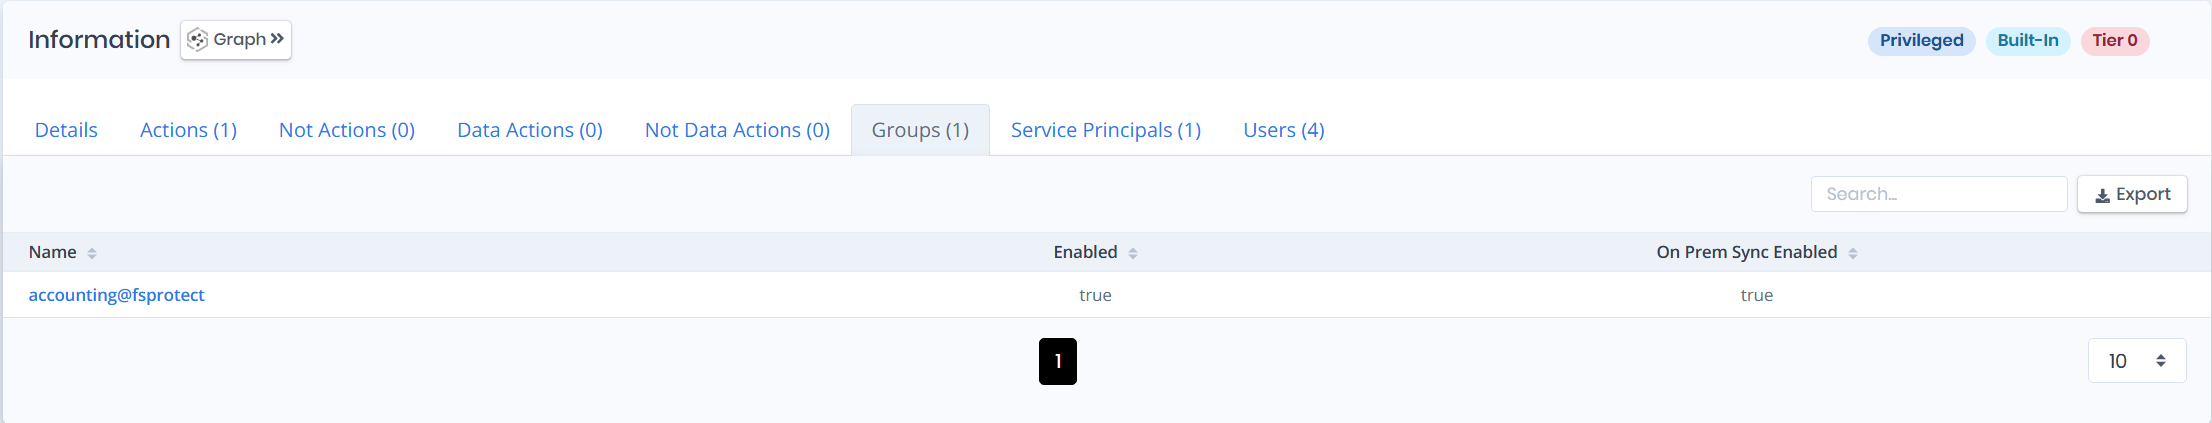
Groups
Service Principals
Service Principals tab contains a list of service principals that have been assigned this role. This list also contains Enabled, App Display Name, Service Principal Type columns to identify the status of these service principals.
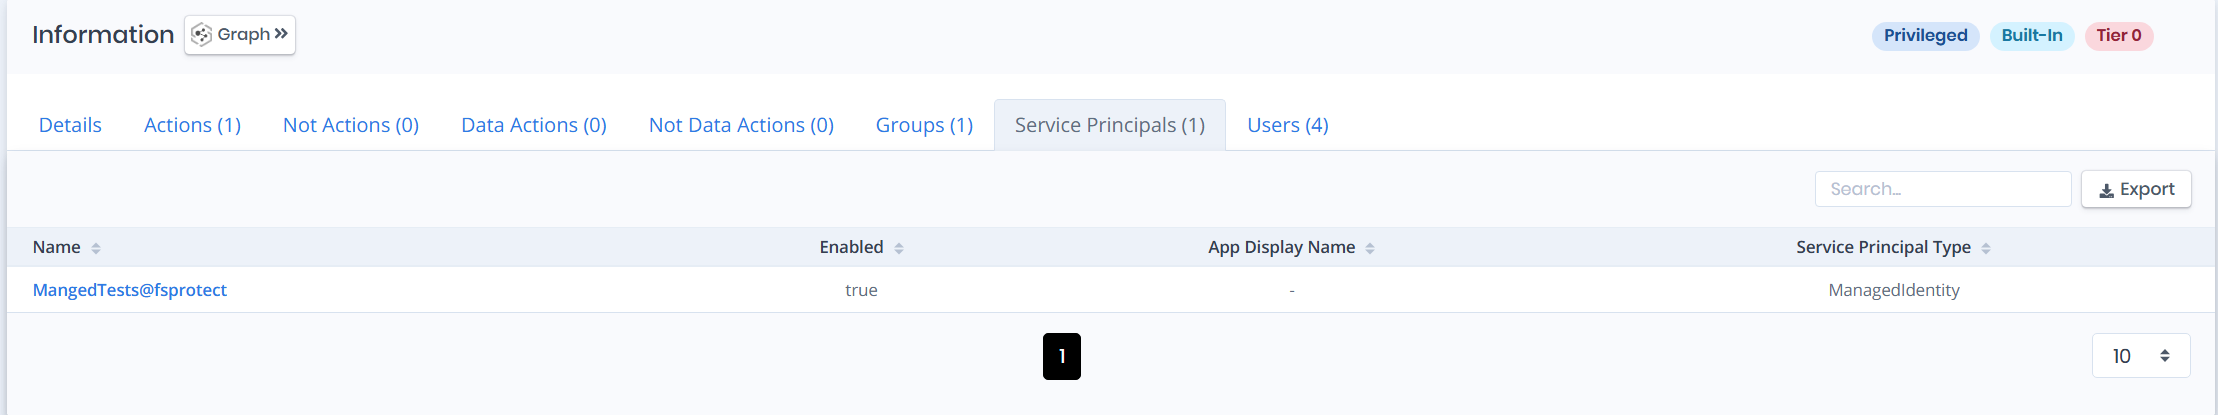
Service Principals
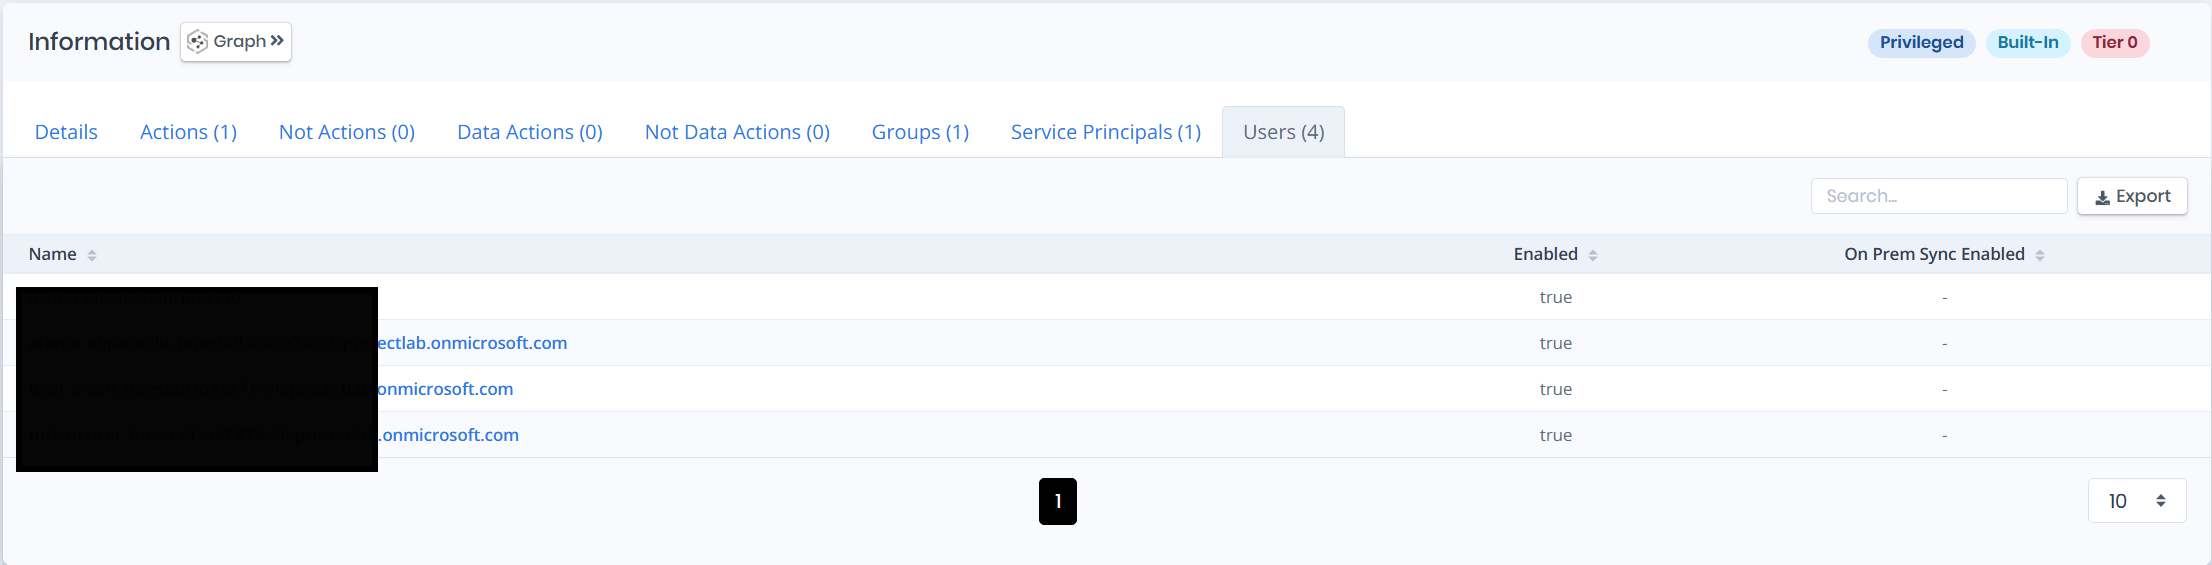
Users
Users tab contains a list of users that have been assigned this role. This list also contains Enabled and On Prem Sync Enabled columns to identify the status of these users.
Users