> For the complete documentation index, see [llms.txt](https://docs.forestall.io/forestall/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.forestall.io/forestall/unified-identities/aws-identities/permission-sets.md).
# Permission Sets
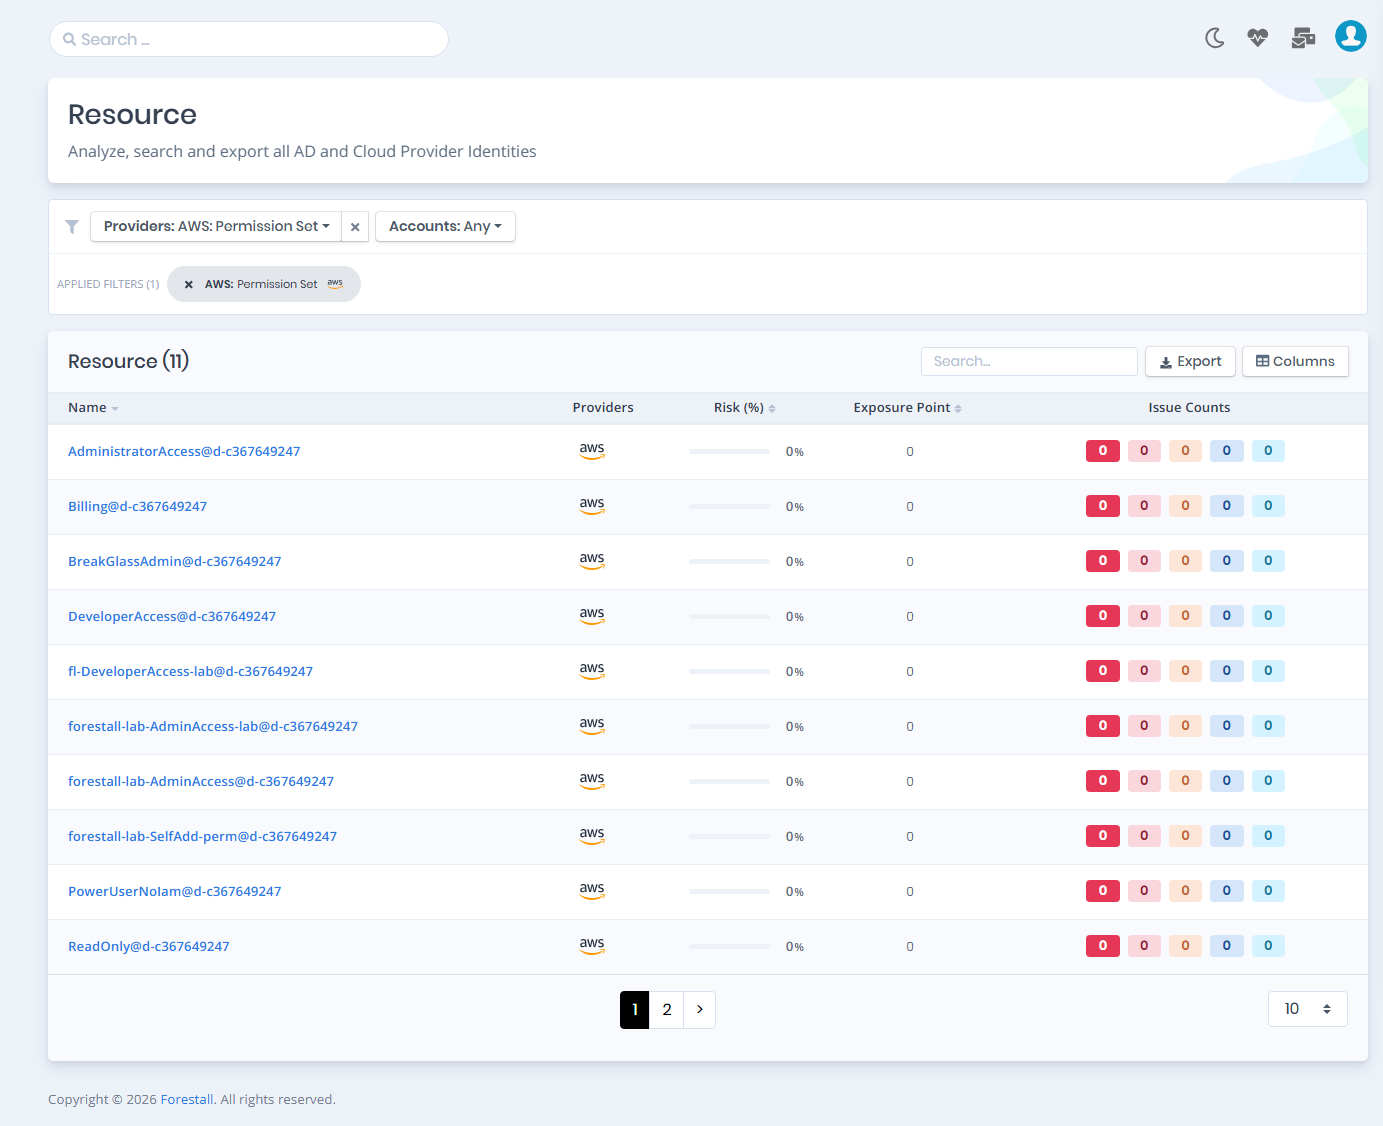
Open **Unified Identities › Resources**, filter **Providers** to **AWS › Permission Set**, then select a row to open its details.
Permission Sets
## Permission Set Details
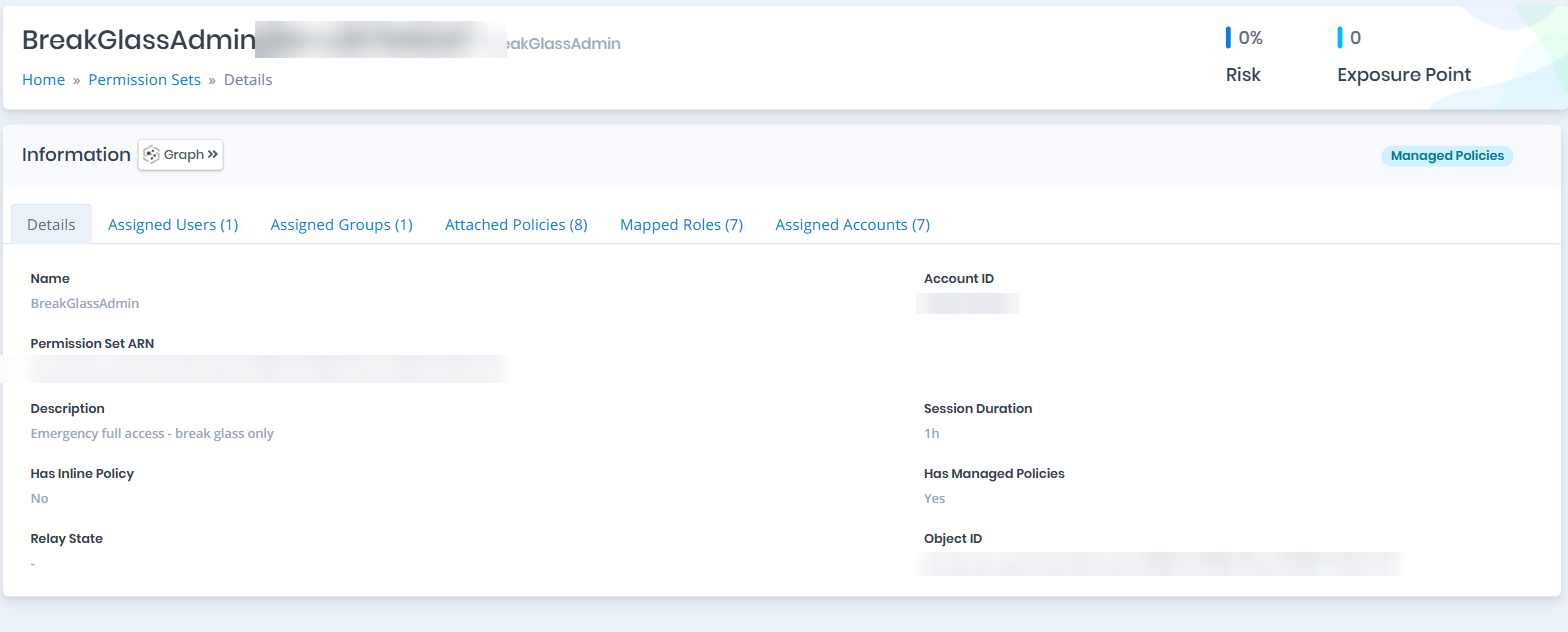
Details page contains the `Risk` and `Exposure Point` of the permission set, and the Information and Issues panes.
{% hint style="info" %}
A permission set is a template. Identity Center provisions it into each assigned account as a real IAM role, and the assigned users and groups assume that role at sign-in. So a permission set that carries `AdministratorAccess` grants admin in every account it reaches.
{% endhint %}
Permission Set Details
## Information
Information Pane can contain different badges to highlight important attributes.
| Badge | Description |
| ---------------- | ---------------------------------------------------------------------------- |
| Inline Policy | Indicates that the permission set has an inline policy. |
| Managed Policies | Indicates that the permission set has one or more attached managed policies. |
Information Pane contains Details, Assigned Users, Assigned Groups, Attached Policies, Mapped Roles and Assigned Accounts tabs.
## Details
Details tab contains attributes below about the permission set object.
| Attribute | Description |
| -------------------- | ------------------------------------------------------------------------------- |
| Name | The permission set name. |
| Account ID | The AWS account ID the permission set belongs to. |
| Permission Set ARN | The ARN of the permission set in Identity Center. |
| Description | The permission set description, if one is set. |
| Session Duration | The maximum session length for the role the permission set provisions. |
| Has Inline Policy | Indicates whether the permission set has an inline policy. |
| Has Managed Policies | Indicates whether the permission set has one or more attached managed policies. |
| Relay State | The URL users are redirected to after federated sign-in, if set. |
| Object ID | The unique identifier of the permission set object. |
## Assigned Users
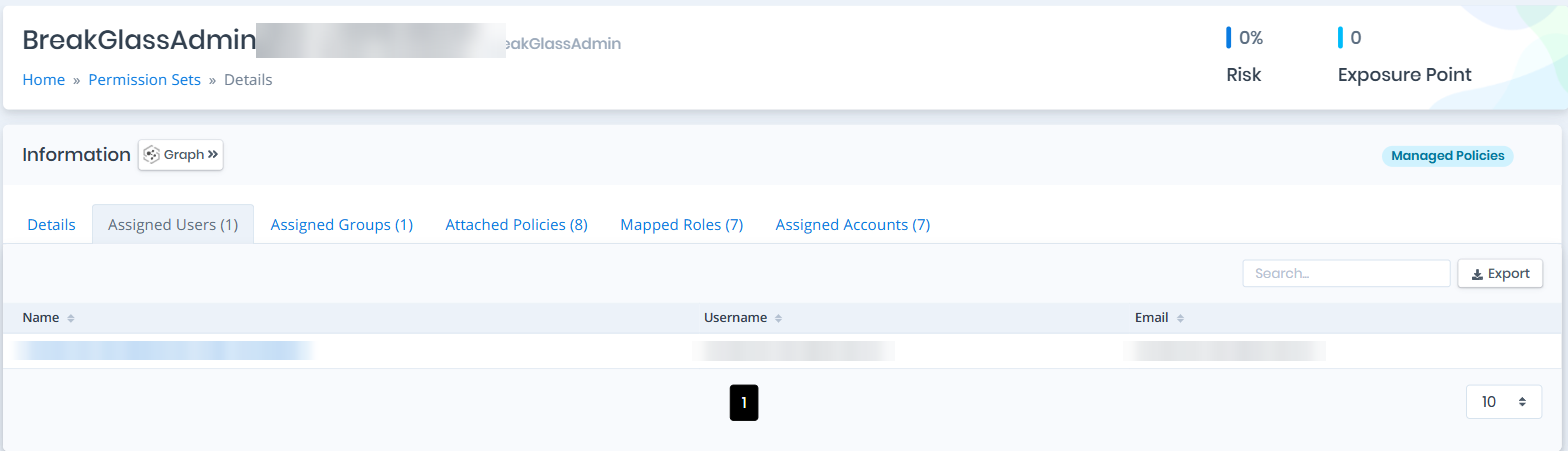
Assigned Users tab contains the SSO users assigned this permission set directly. Each assignment grants the user an assumable role in the accounts the permission set is provisioned to. The list contains the Name, Username and Email columns.
Assigned Users
## Assigned Groups
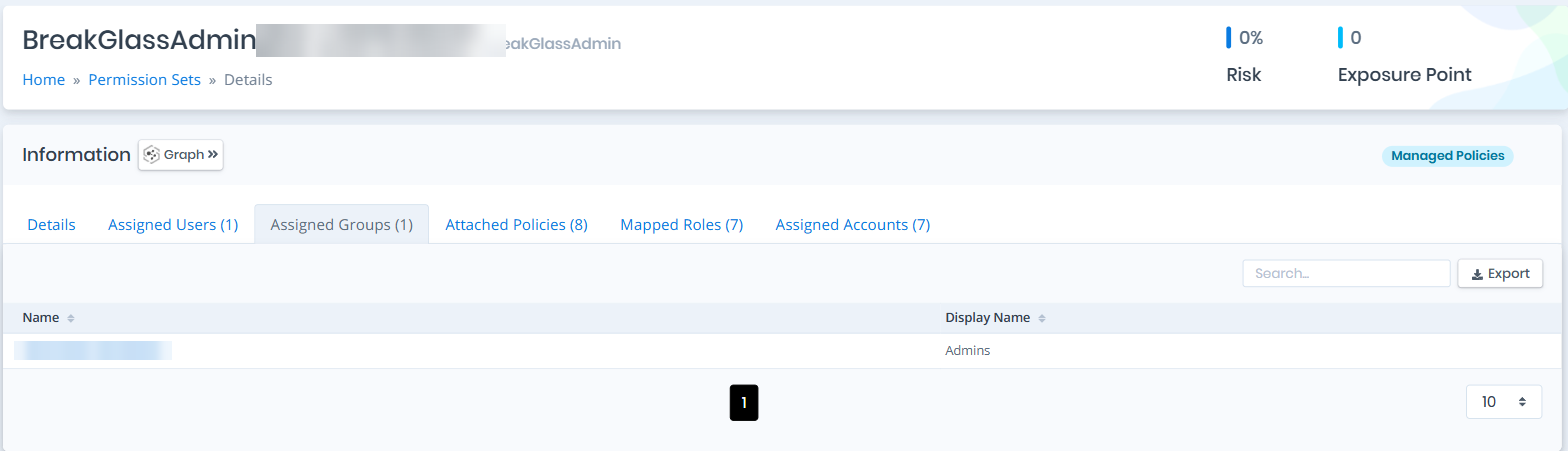
Assigned Groups tab contains the SSO groups assigned this permission set. Every member of an assigned group inherits the access. The list contains the Name and Display Name columns.
Assigned Groups
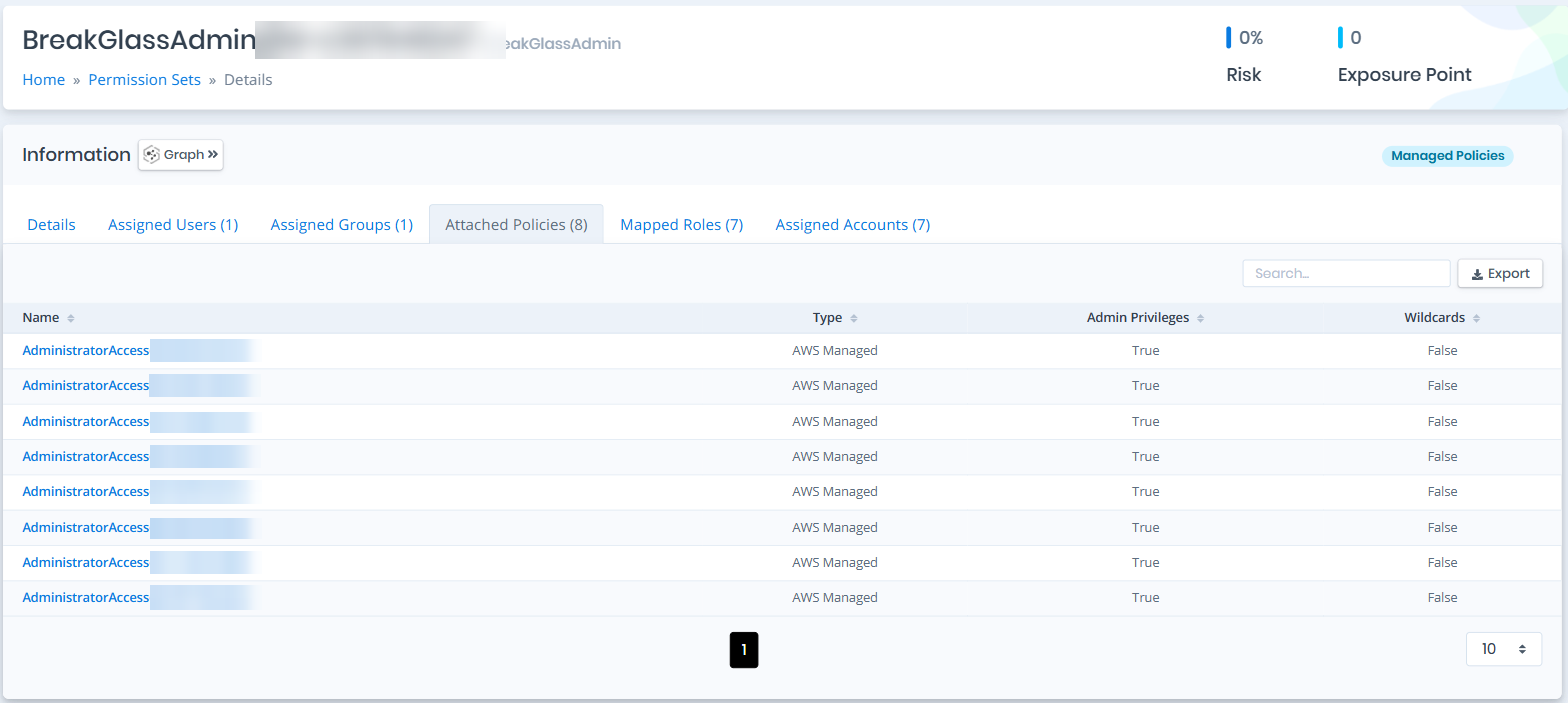
## Attached Policies
Attached Policies tab lists the managed and inline policies bound to the permission set.
| Column | Description |
| ---------------- | -------------------------------------------------------------------- |
| Name | The policy name. |
| Type | AWS Managed or Customer Managed. |
| Admin Privileges | Indicates whether the policy grants administrator-level privileges. |
| Wildcards | Indicates whether the policy uses wildcards in actions or resources. |
Attached Policies
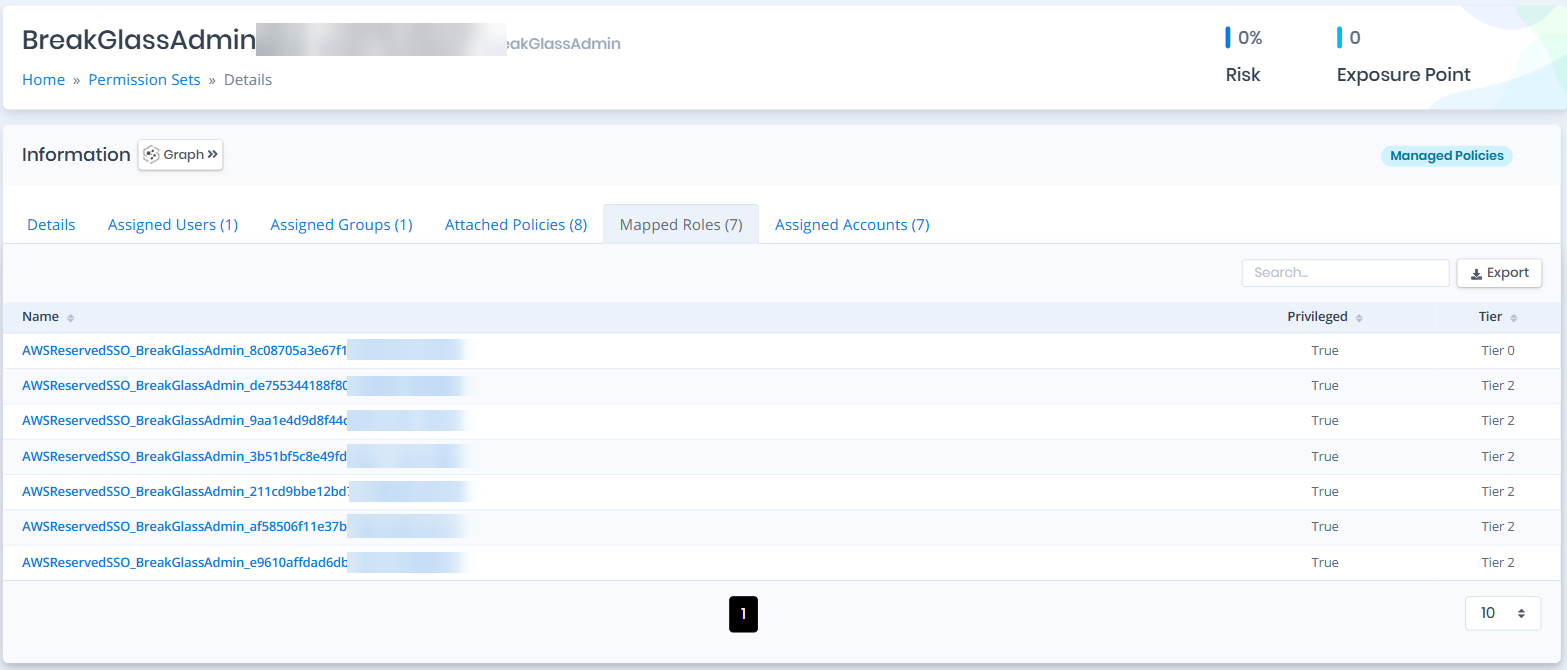
## Mapped Roles
Mapped Roles tab lists the IAM roles the permission set maps to in each provisioned account. These are the `AWSReservedSSO__` roles Identity Center creates, and they are the concrete grant a user assumes. The list contains the Name, Privileged and Tier columns.
Mapped Roles
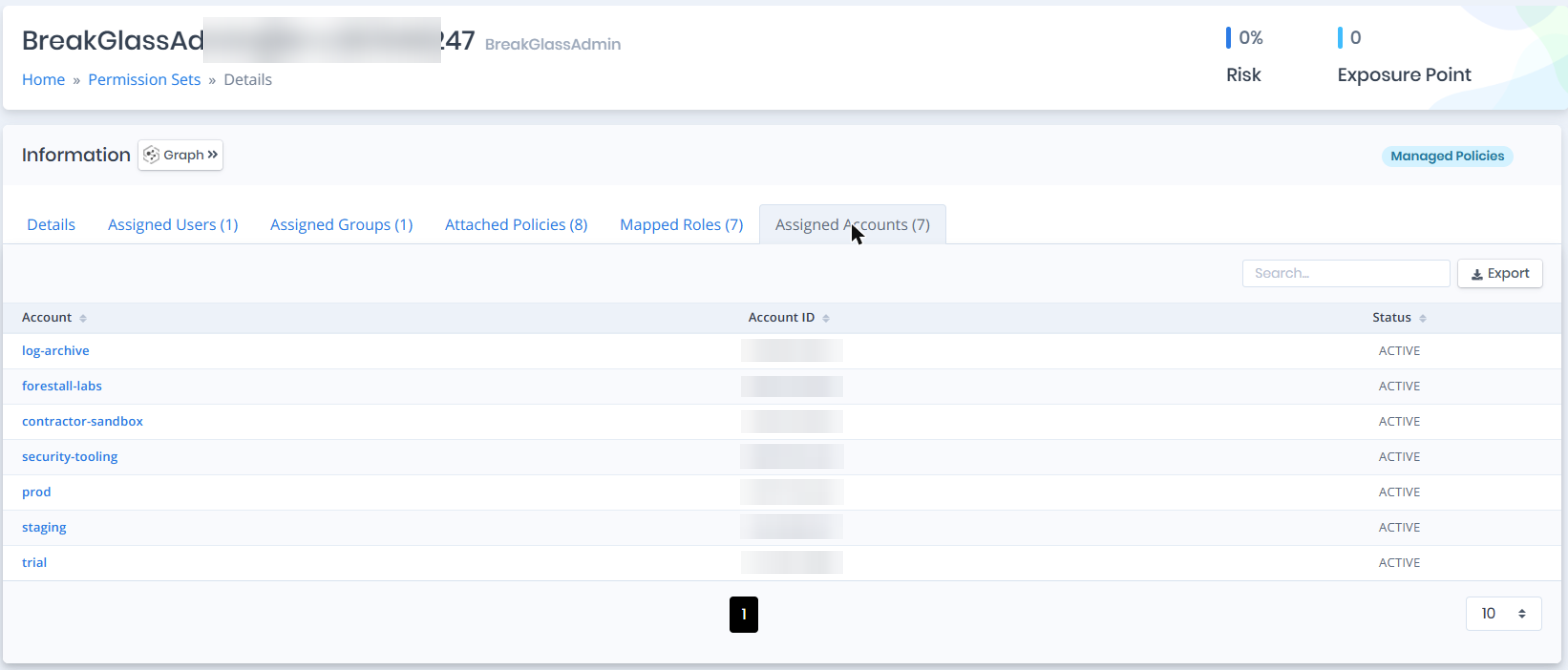
## Assigned Accounts
Assigned Accounts tab lists the accounts the permission set is provisioned to. These are the accounts where the permission set exists as an assumable IAM role. The list contains the Account, Account ID and Status columns.
Assigned Accounts
## Issues
Issues pane contains identified security issues on the permission set object.