> For the complete documentation index, see [llms.txt](https://docs.forestall.io/forestall/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.forestall.io/forestall/unified-identities/ad-identities/gmsas.md).
# GMSAs
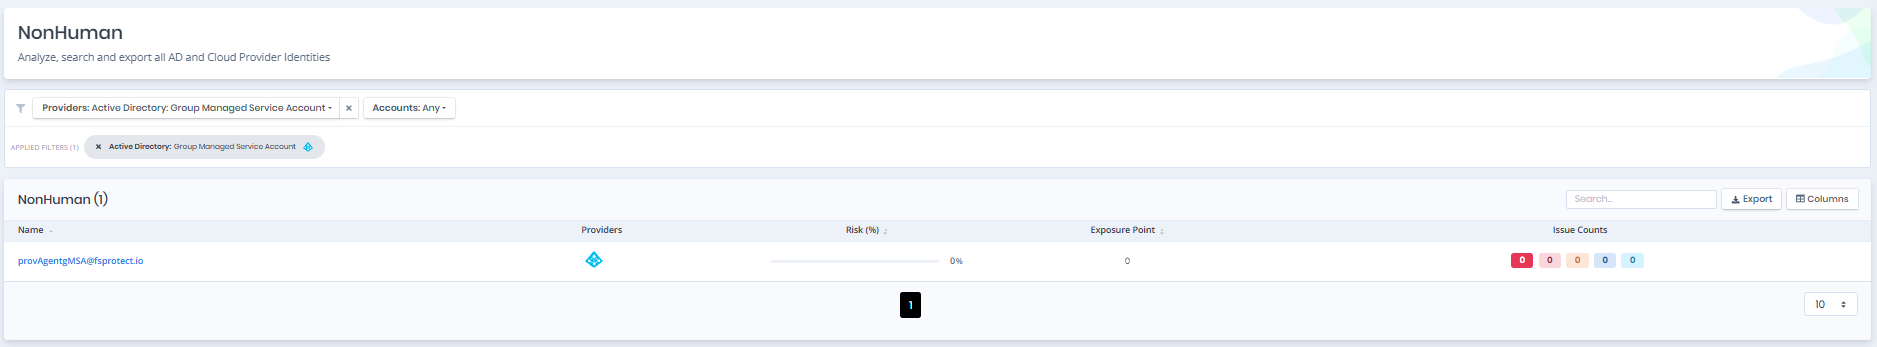
Open **Unified Identities › Non Human Identities**, filter **Providers** to **Active Directory › Group Managed Service Account**, then select a row to open its details.
Group Managed Service Accounts
## Group Managed Service Account Details
Opening a group managed service account shows the `Risk` and `Exposure Point` in its header, and the `Information` and `Issues` panes. The `Issues` pane is shown only when the object has issues.
{% hint style="info" %}
You can analyze the object in the [Graph](/forestall/visualize/visualize.md) by clicking the **Graph »** button next to the `Information` title. For a shadow admin the button reads **Admin Path »** and opens the shortest path to admin objects (see [Object Detail Pages](/forestall/unified-identities.md#object-detail-pages)).
{% endhint %}
Group Managed Service Account Details
## Information
`Information Pane` can contain different badges to highlight important attributes.
| Badge | Description |
| ------------------- | ------------------------------------------------------------------------------------------------------------------ |
| **Shadow** | Indicates that the object can compromise admin objects with at least one attack path. |
| **Sensitive** | Indicates that the object is marked as not delegated or a member of the Protected Users group. |
| **Privileged** | Indicates that the object is Privileged. |
| **Admin** | Indicates that the object is Admin. |
| **Local Admin** | Indicates that the object is a member (direct or nested) of a local administrators group in at least one computer. |
| **Inactive** | Indicates that the enabled object has not logged on within the inactivity threshold of the scan policy. |
| **Enabled** | Indicates that the object is enabled. |
| **Disabled** | Indicates that the object is disabled. |
| **Tier0**/**Tier2** | Indicates the tier of the object (`Tier0` or `Tier2`). |
`Information Pane` contains `Details`, `Groups`, `Sessions`, `SPNs`, and `Local Memberships` tabs respectively.
## Details
Details tab contains attributes below about group managed service account object.
| Attribute | Description |
| -------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **SAM AccountName** | The logon name used to support clients and servers running earlier versions of the operating system, such as Windows NT 4.0, Windows 95, Windows 98, and LAN Manager. (**Ldap Display Name**: sAMAccountName) |
| **Distinguished Name** | Active Directory distinguished name of the object. (**Ldap Display Name**: distinguishedName) |
| **Object Category** | An object class name used to group objects of this or derived classes. (**Ldap Display Name**: objectCategory) |
| **Object Sid** | Active Directory security identifier of object. (**Ldap Display Name**: objectSid) |
| **Created Time** | The date when this object was created. (**Ldap Display Name**: whenCreated) |
| **Last Changed Time** | The date when this object was last changed. (**Ldap Display Name**: whenChanged) |
| **Parent OU** | The direct parent Organizational Unit of the object. |
| **Name** | Name of the specified object. (**Ldap Display Name**: name) |
| **Bad Password Count** | The number of times the user tried to log on to the account using an incorrect password. (**Ldap Display Name**: badPwdCount) |
| **Primary Group ID** | Contains the relative identifier (RID) for the primary group of the object. By default, this is the RID for the Domain Computers group for group managed service accounts. |
| **Admin Count** | Indicates that a given object has had its ACLs changed to a more secure value by the system because it was a member of one of the administrative groups (directly or transitively). (**Ldap Display Name**: adminCount) |
| **Logon Count** | The number of times the account has successfully logged on. This attribute is not replicated to other Domain Controllers. (**Ldap Display Name**: logonCount) |
| **Constrained Delegation** | Indicates whether the Constrained Delegation is active or not. |
| **Email** | E-mail address of the object. (**Ldap Display Name**: mail) |
| **Common Name** | Common name of the object. (**Ldap Display Name**: cn) |
| **DNS Host Name** | Name of the account as registered in DNS. (**Ldap Display Name**: dNSHostName) |
| **AltSecurityIdentities** | Alternative identities, such as certificate subjects or issuers, that can be used to authenticate as this account. (**Ldap Display Name**: altSecurityIdentities) |
## Groups
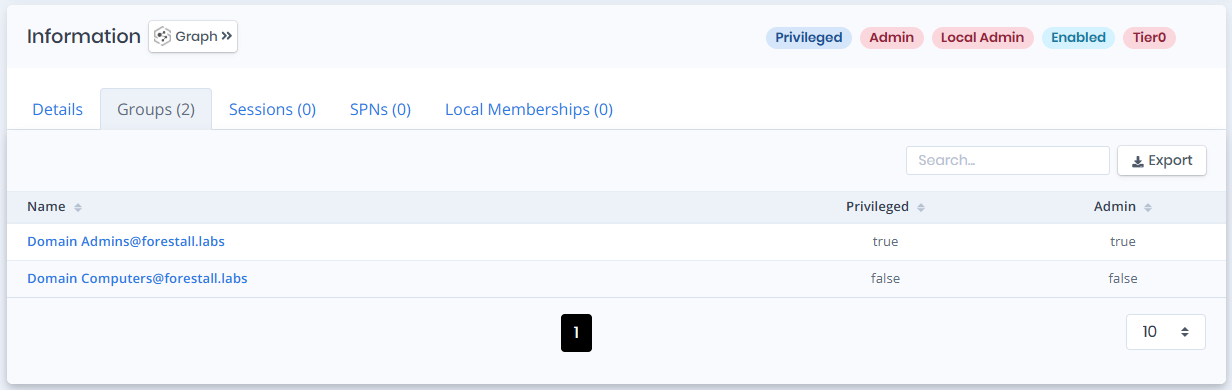
Groups tab contains a list of groups that the group managed service account is a member of. This list also contains `Privileged` and `Admin` columns to identify the privilege levels of these groups.
Groups
## Sessions
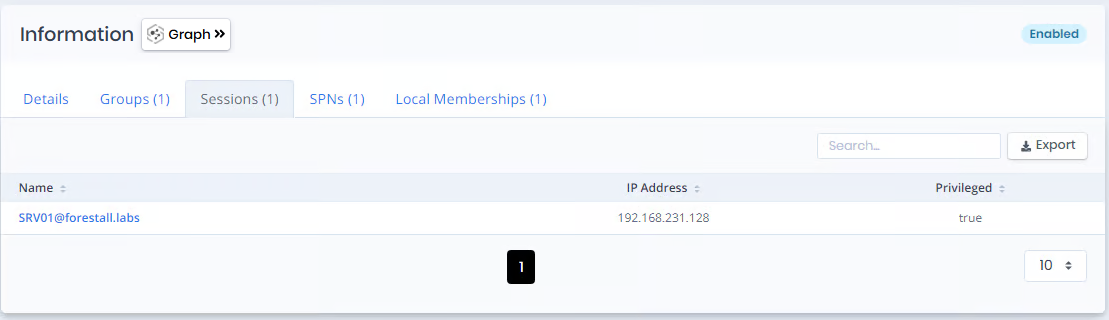
Sessions tab contains a list of computers that the group managed service account has a session on. This list also contains `IP Address`, and `Privileged` columns to identify the network address and privilege levels of these computers.
Sessions
## SPNs
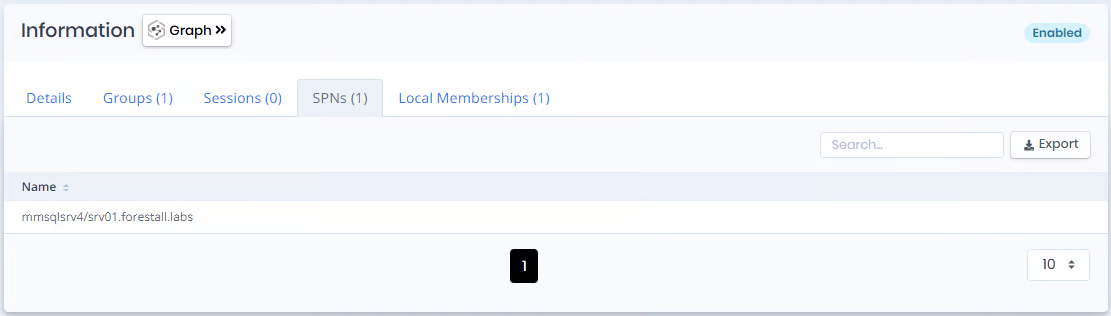
SPNs tab contains a list of `Service Principal Names` that are defined on the group managed service account object.
SPNs
## Local Memberships
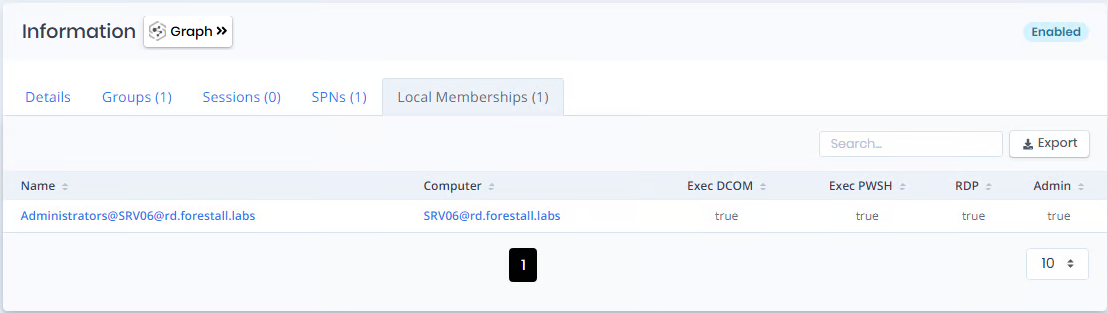
Local Memberships tab contains a list of local groups that the group managed service account is a member of.
Local Memberships
**Local Group Name**: Name of the local group that the user is a member of.
**Computer**: Name of the computer object that contains the local group.
**Exec DCOM**: Indicates whether the local group can have enough privilege to execute commands with DCOM(Distributed Component Object Model) protocol on the computer.
**Exec PWSH**: Indicates whether the local group can have enough privilege to execute commands with Powershell on the computer.
**RDP**: Indicates whether the local group can have enough privilege to connect with RDP (Remote Desktop Protocol) to the computer.
**Admin**: Indicates whether the local group can have admin privilege on the computer.
## Issues
Issues pane contains identified issues on the group managed service account object.