
Open Unified Identities › Non Human Identities, filter Providers to GCP Identities › Principal, then select a row to open its details. A Principal represents an identity (or set of identities) that can be granted IAM roles, such as a federated user, service account, or a principal set matched via a workforce/workload identity pool.
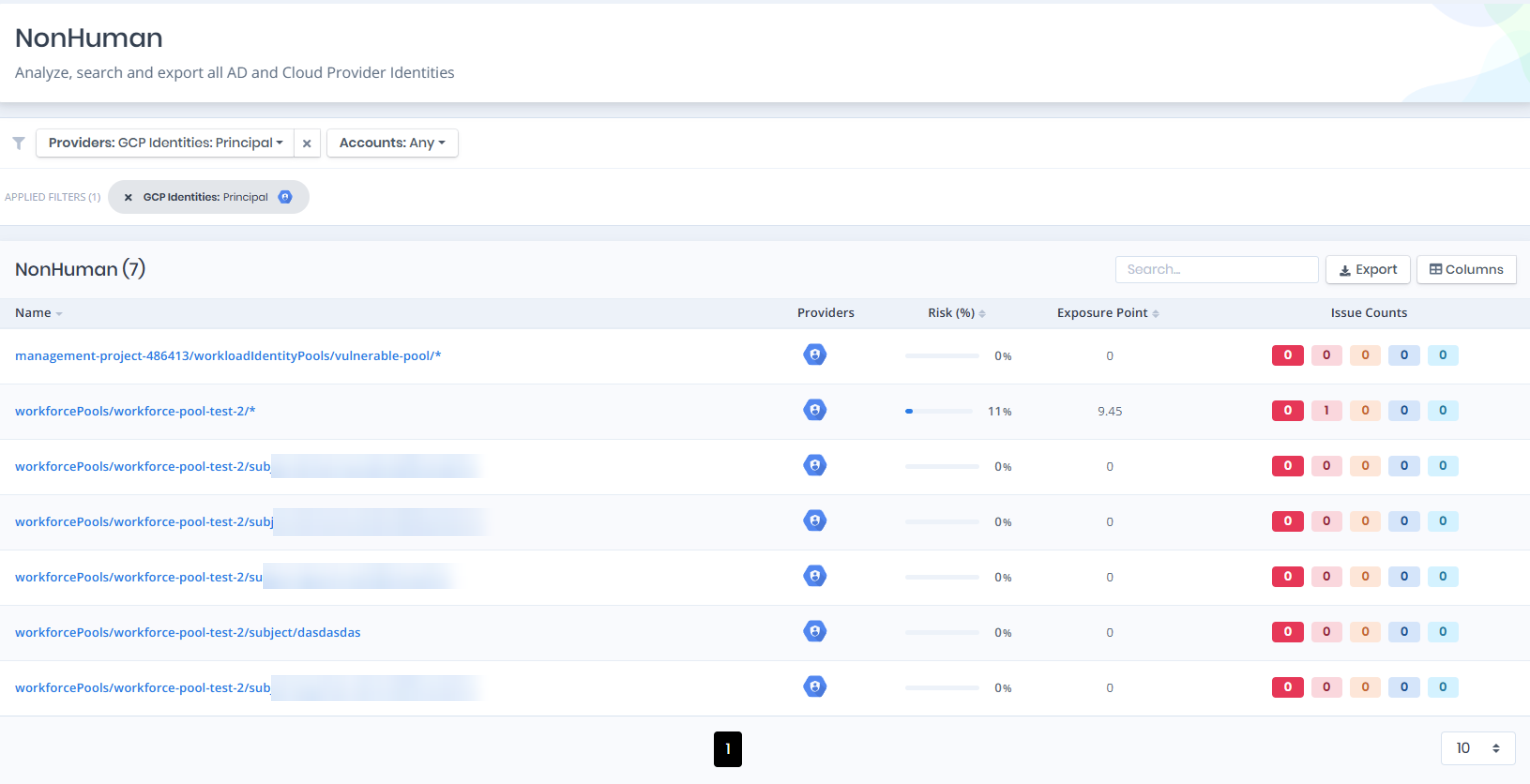
Principals
Principals Details
Opening a principal shows the Details tab. The card title can carry a Tier 0/Tier 2 badge.
You can analyze the object in the Graph by clicking the Graph » button next to the Information title.
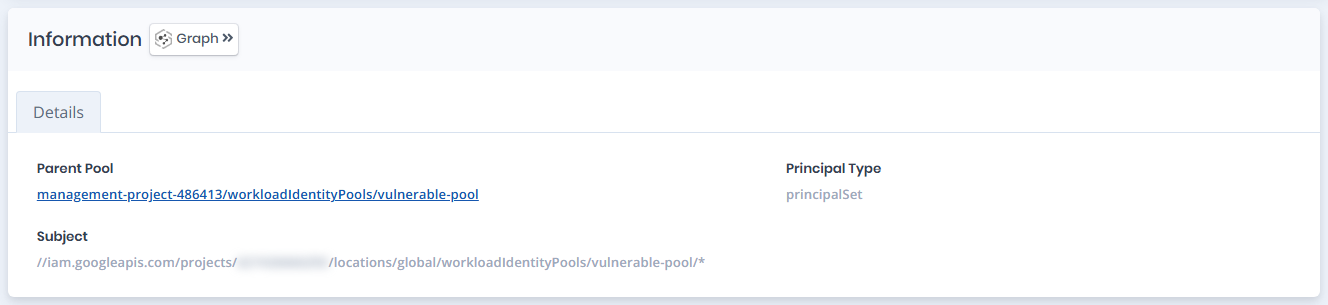
GCP Principal Details
The Details tab contains attributes about the Principal. The page also includes an Issues panel that lists any security findings related to the principal, along with a Risk score and Exposure Point.
Information
| Attribute | Description |
|---|---|
| Parent Pool | The workforce or workload identity pool this principal belongs to (e.g., workforce-pool-test-2). |
| Principal Type | The classification of the principal (e.g., principalSet). |
| Subject | The fully-qualified subject identifier of the principal (e.g., //iam.googleapis.com/locations/global/workforcePools/workforce-pool-test-2/*). |
Issues
Lists security findings associated with the principal (e.g., Role Assigned to Entire Federated Identity Pool), each tagged with relevant categories such as Least Privilege or Privilege Escalation, and a severity rating (e.g., High).