> For the complete documentation index, see [llms.txt](https://docs.forestall.io/forestall/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.forestall.io/forestall/unified-identities/azure-identities/entra-id/administrative-units.md).
# Administrative Units
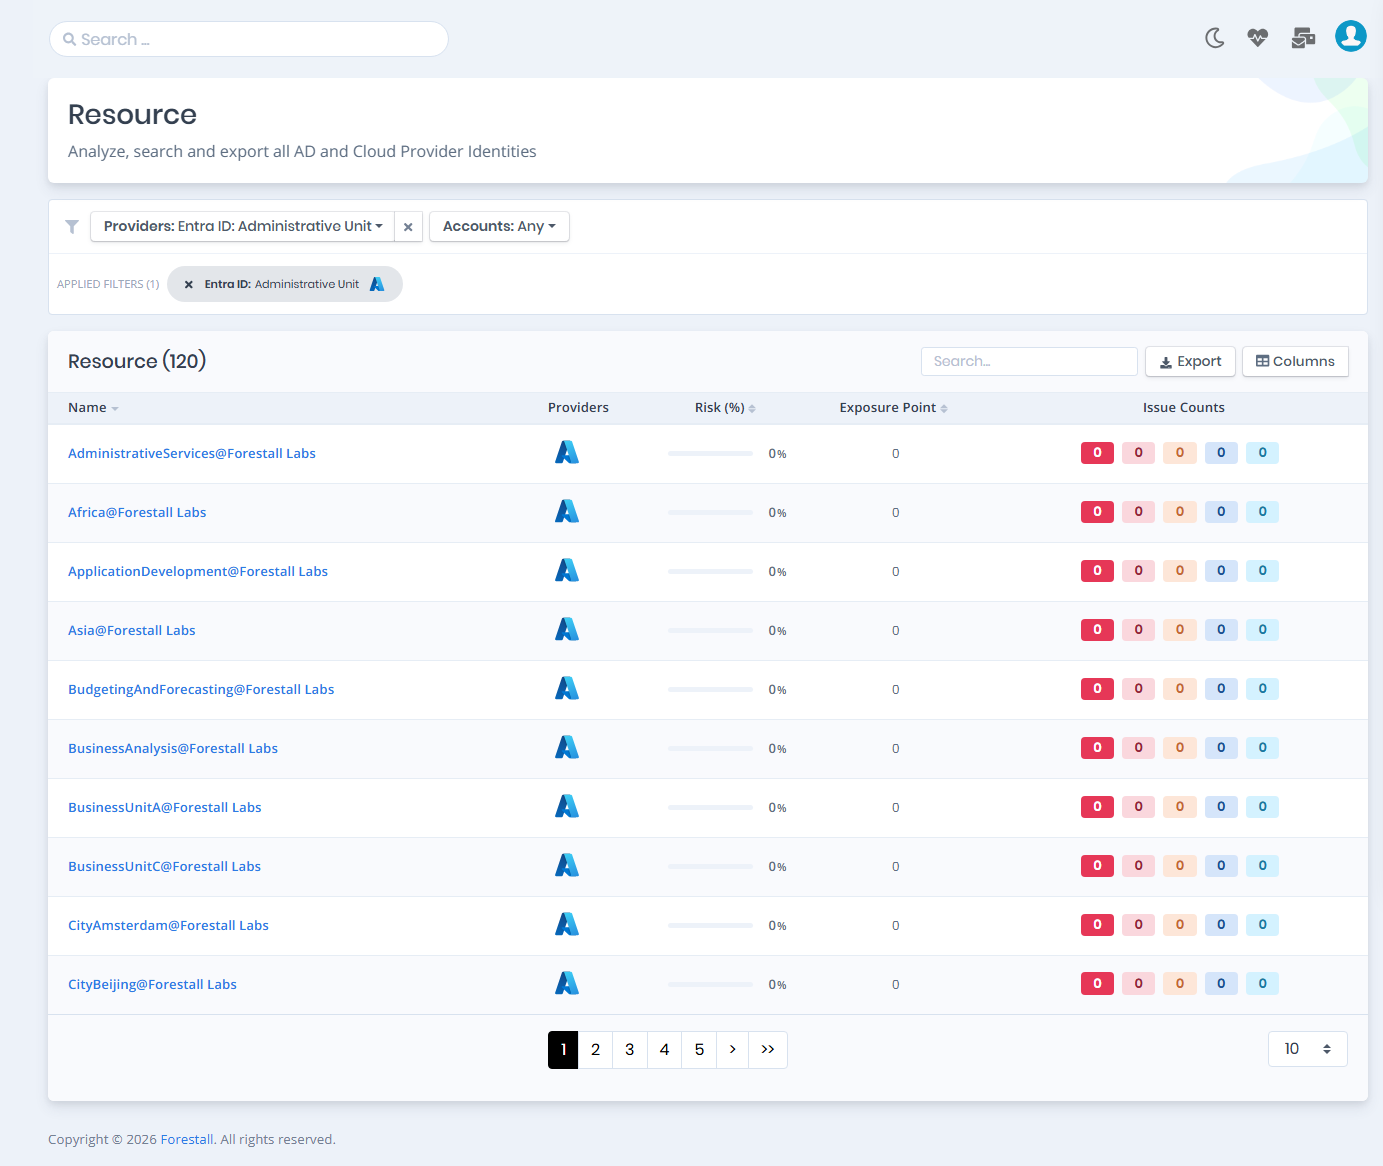
Open **Unified Identities › Resources**, filter **Providers** to **Entra ID › Administrative Unit**, then select a row to open its details.
Administrative Units
## Administrative Unit Details
Opening an administrative unit shows the `Risk` and `Exposure Point` in the header, and the page contains the `Information` pane.
{% hint style="info" %}
You can analyze the object in the [Graph](/forestall/visualize/visualize.md) by clicking the **Graph »** button next to the `Information` title.
{% endhint %}
Administrative Unit Details
## Information
`Information Pane` can contain different badges to highlight important attributes.
| Badge | Description |
| ----------------------- | --------------------------------- |
| **Tier 0** / **Tier 2** | Indicates the tier of the object. |
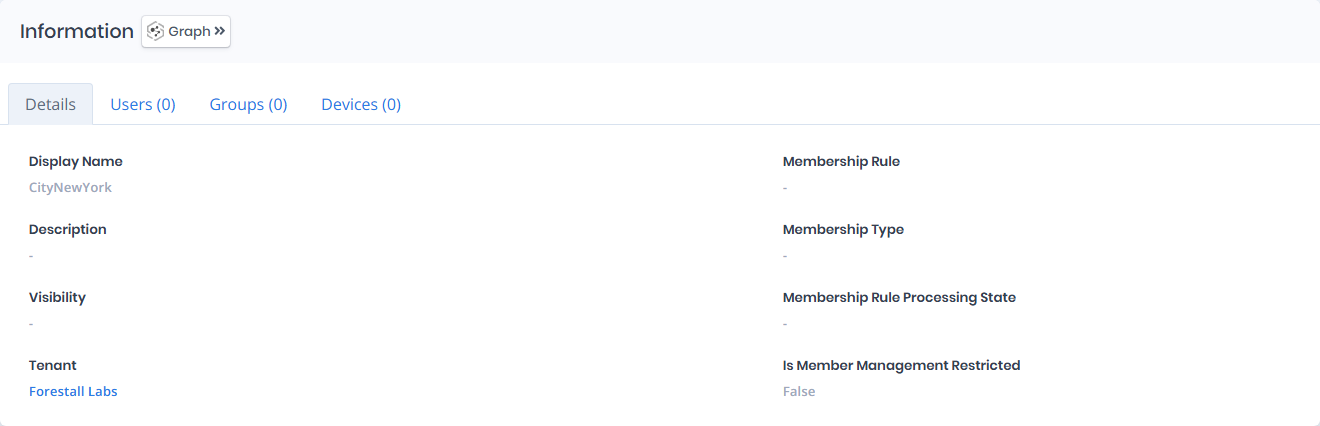
`Information Pane` contains `Details`, `Users`, `Groups`, and `Devices` tabs respectively. Each tab except `Details` carries the number of rows it holds in its label.
## Details
Details tab contains attributes below about administrative unit object.
| Attribute | Description |
| ------------------------------------ | ----------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Display Name** | The name of the Administrative Unit as shown in the Azure portal; used to identify and organize groups of users, devices, or groups for delegated administration. |
| **Membership Rule** | This field defines the dynamic membership criteria, if any. It's blank when the AU uses manual (static) membership. |
| **Description** | An optional text field describing the purpose or usage of the Administrative Unit; this is blank if not set. |
| **Membership Type** | Indicates whether members are added **dynamically** (based on rules) or **assigned manually**. If not specified, the AU is likely using manual assignments. |
| **Visibility** | Defines who can see the Administrative Unit. When blank, it defaults to standard visibility within the tenant based on assigned permissions. |
| **Membership Rule Processing State** | Shows the status of dynamic rule evaluation (e.g., `Processing`, `Completed`, or `NotStarted`). If blank, the AU does not use dynamic membership. |
| **Tenant** | The Entra ID tenant where the Administrative Unit resides, linking to its [Tenant](/forestall/unified-identities/azure-identities/entra-id/tenants.md) page. |
| **Is Member Management Restricted** | When set to `False`, it means global administrators and other authorized roles can manage members without restrictions. |
## Users
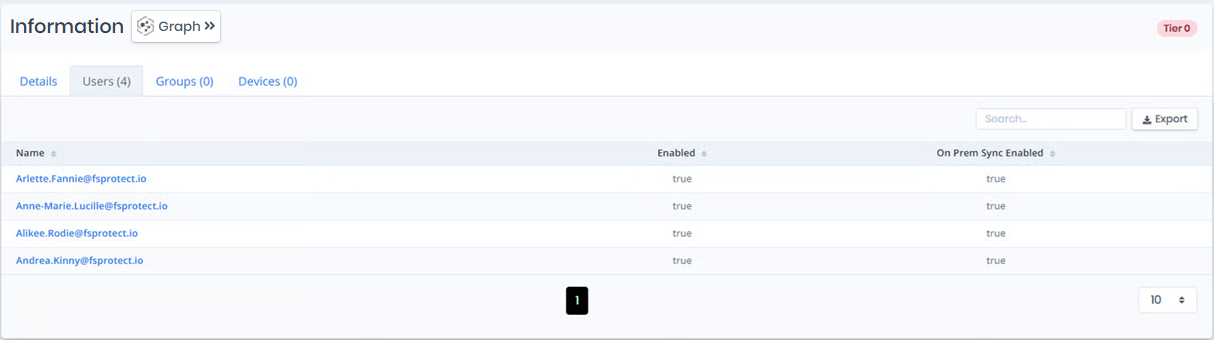
Users tab contains a list of users that are members of the administrative unit. This list also contains `Enabled` and `On Prem Sync Enabled` columns to identify the status of these users.
Users
## Groups
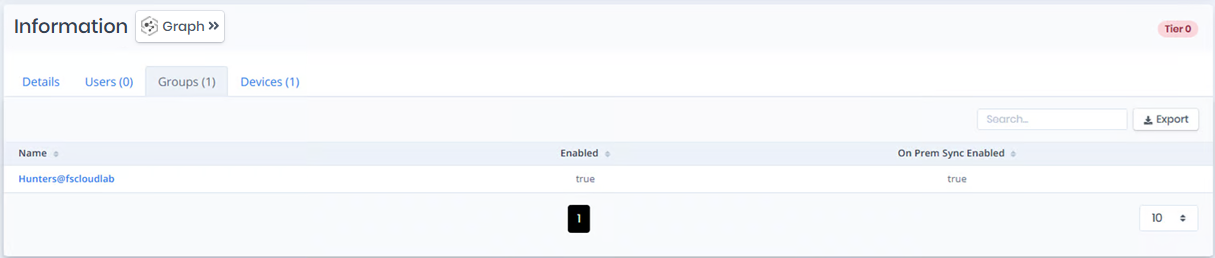
Groups tab contains a list of groups that are members of the administrative unit. This list also contains `Enabled` and `On Prem Sync Enabled` columns to identify the status of these groups.
Groups
## Devices
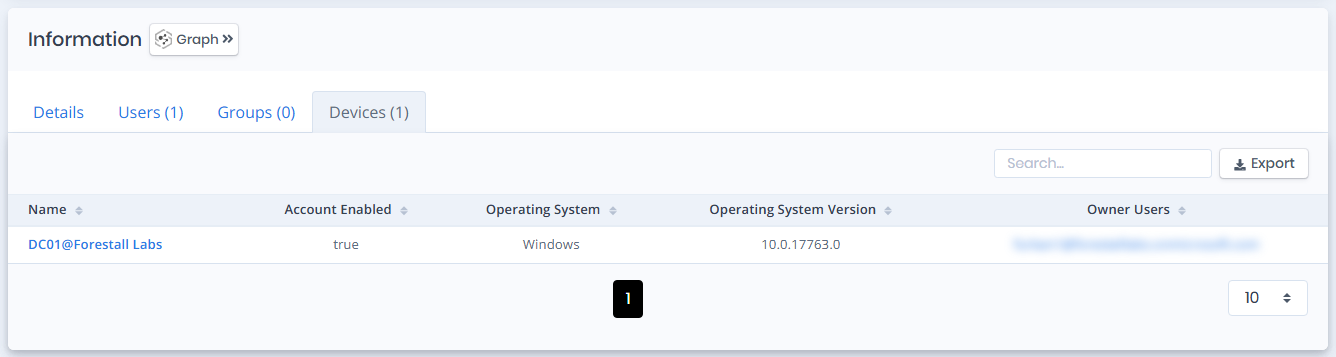
Devices tab contains a list of devices that are members of the administrative unit. This list also contains `Account Enabled` , `Operating System` , `Operating System Version` and `Owner Users` columns to identify the status of these devices.