
Dashboard summarizes the security posture of the scanned AWS environments in the selected scan.
Risk Pane (AWS Dashboard)
This Risk Pane summarizes key risk metrics from the scan, including the overall Risk and Exposure Scores, Tier 0 Identities, Dangerous Paths, Shadow Admins, and severity levels (Critical to Info). It breaks down risks by MITRE ATT&CK Tactics (e.g., Persistence, Privilege Escalation, Initial Access), Tags (e.g., Identity Governance, Account Security, Access Management), Impacts (e.g., Privilege Escalation via Policy Manipulation, Shadow Admin via Dangerous Permissions, Credential Exposure), and AWS Entity Types (e.g., AWSIAMUser, AWSIAMRole, AWSIAMGroup, AWSIAMPolicy, AWSIAMAccount, AWSOrganization, AWSOrganizationalUnit, AWSIdentityCenter, AWSPermissionSet, AWSSSOUser, AWSSSOGroup). This layout helps quickly identify high-risk areas and prioritize remediation actions within AWS environments.
The Tier 0 Identities card is shown when the scan policy enables the Tier0 Analysis module for AWS. The Tier Analysis Statistics and Top Choke Points sections below the entity cards are described on the Dashboard page.
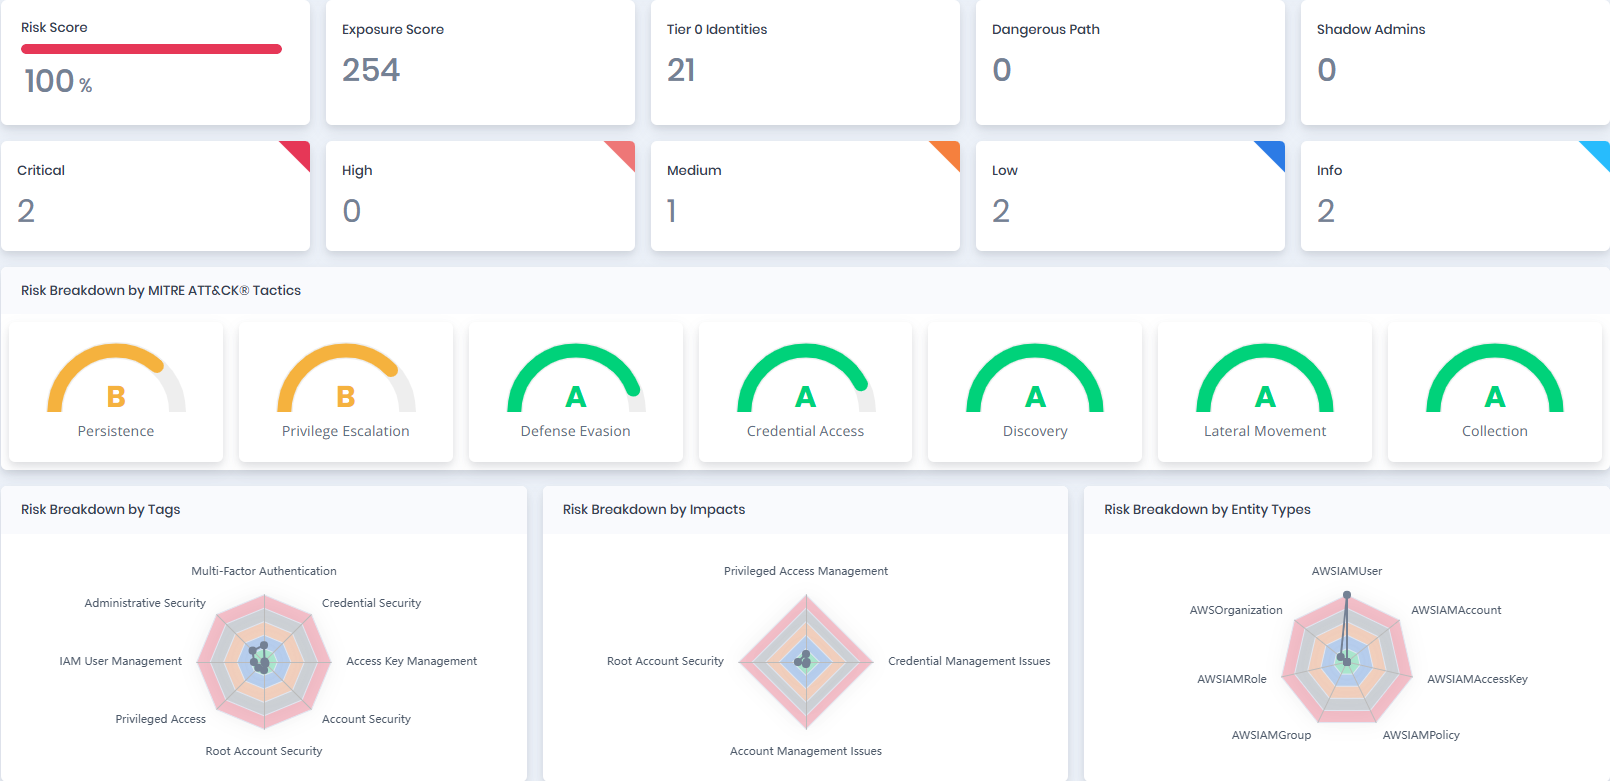
Risk Pane
Risk Breakdown by Tags, Impacts and Entity Types
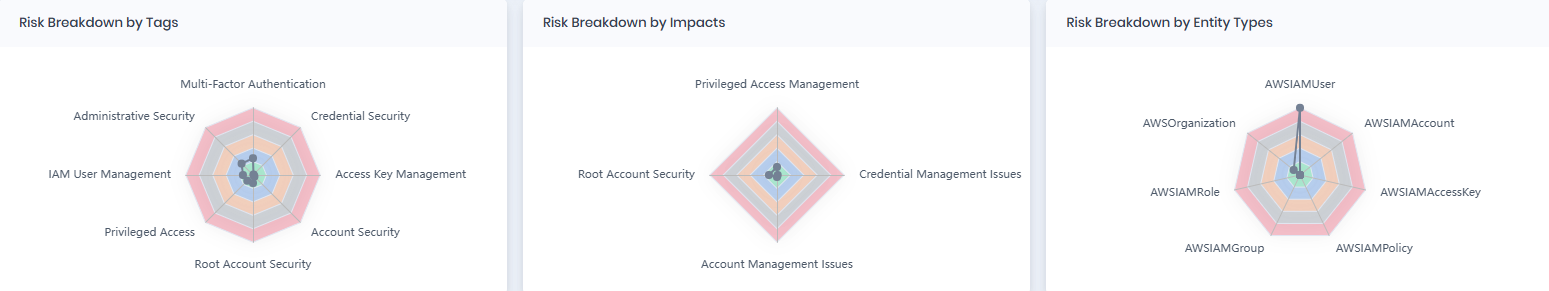
Risk Breakdown by Tags, Impacts and Entity Types
Risk Breakdown by Tags: Risk scores based on Tags.
Risk Breakdown by Impacts: Risk scores based on Impacts.
Risk Breakdown by Entity Types: Risk scores based on Entity Types.
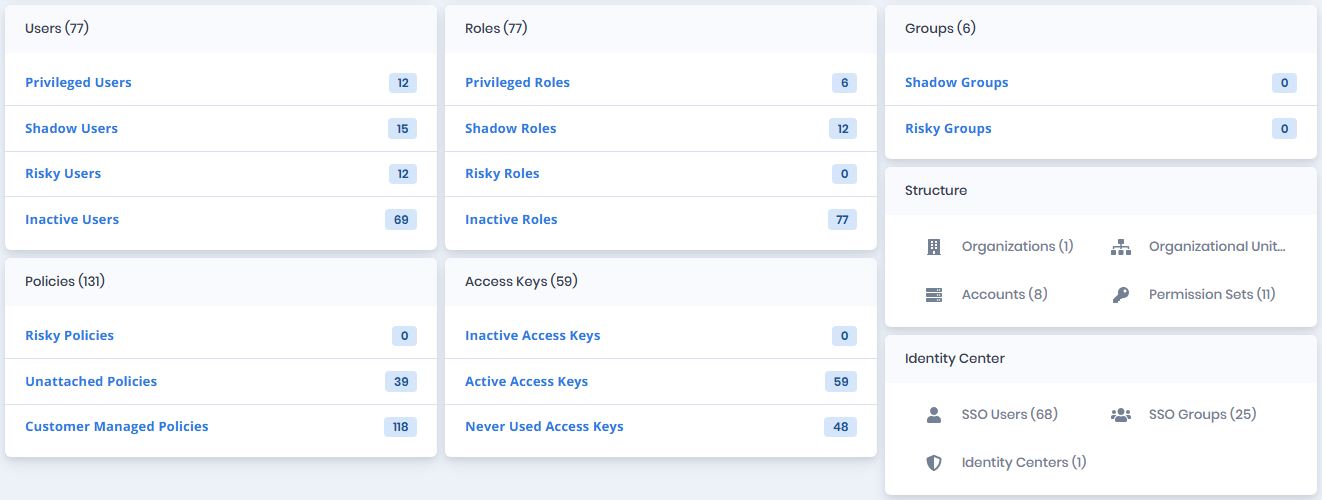
AWS Entity Pane
The header of each card shows the total number of objects of that type, for example Users (77).
Users Table
| Statistic | Description |
|---|---|
| Privileged Users | The number of privileged IAM user accounts. |
| Shadow Users | The number of shadow admin user accounts. |
| Risky Users | The number of user accounts that have a risk score greater than 50. |
| Inactive Users | The number of inactive user accounts. |
Policies Table
| Statistic | Description |
|---|---|
| Risky Policies | The number of policies that have a risk score greater than 50. |
| Unattached Policies | The number of policies that are not attached to any user, group or role. |
| Customer Managed Policies | The number of policies created and managed in the account, not by AWS. |
Roles Table
| Statistic | Description |
|---|---|
| Privileged Roles | The number of privileged roles. |
| Shadow Roles | The number of shadow admin roles. |
| Risky Roles | The number of roles that have a risk score greater than 50. |
| Inactive Roles | The number of inactive roles. |
Access Keys Table
| Statistic | Description |
|---|---|
| Inactive Access Keys | The number of inactive access keys. |
| Active Access Keys | The number of access keys with Active status. |
| Never Used Access Keys | The number of access keys that were never used. |
Groups Table
| Statistic | Description |
|---|---|
| Shadow Groups | The number of shadow admin groups. |
| Risky Groups | The number of groups that have a risk score greater than 50. |
Structure
The Structure card shows the AWS organization layout discovered during the scan: Organizations, Organizational Units, Accounts and Permission Sets, each with its count.
Identity Center
The Identity Center card shows the IAM Identity Center objects discovered during the scan: SSO Users, SSO Groups and Identity Centers, each with its count.