> For the complete documentation index, see [llms.txt](https://docs.forestall.io/forestall/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.forestall.io/forestall/scans/scan-health.md).

# Scan Health

Scan Health provides an overview of configuration, permission, and connectivity issues that may affect the completeness of an Active Directory scan.
It helps identify whether required scan data was successfully collected and highlights conditions that may cause security checks to return incomplete results. As the page itself states, these results describe scan completeness and reliability, not vulnerabilities.

The page is opened from the heartbeat icon inside the **Finished** badge of a scan on the [Scans](/forestall/scans/scans.md) list. The icon is shown for finished scans that include Active Directory.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-85de6b769ebe338e7d39027288d0a16a74111184%2Fdashboard-scan-health-image-1.png?alt=media" alt=""><figcaption><p>Scan Health</p></figcaption></figure>

The page is made up of the sections below, in this order. Each section ends with two lines:

* **Impact** describes which security checks may be incomplete when the section reports a problem.
* **Recommendation** describes what to change, usually with a reference to the Forestall [Requirements](/forestall/introduction/requirements.md).

Computer counts in the sections can be selected to open the corresponding computers in [Search & Reports](/forestall/search-and-reports.md).

### Local Enumeration Module

#### Local Enumeration Status

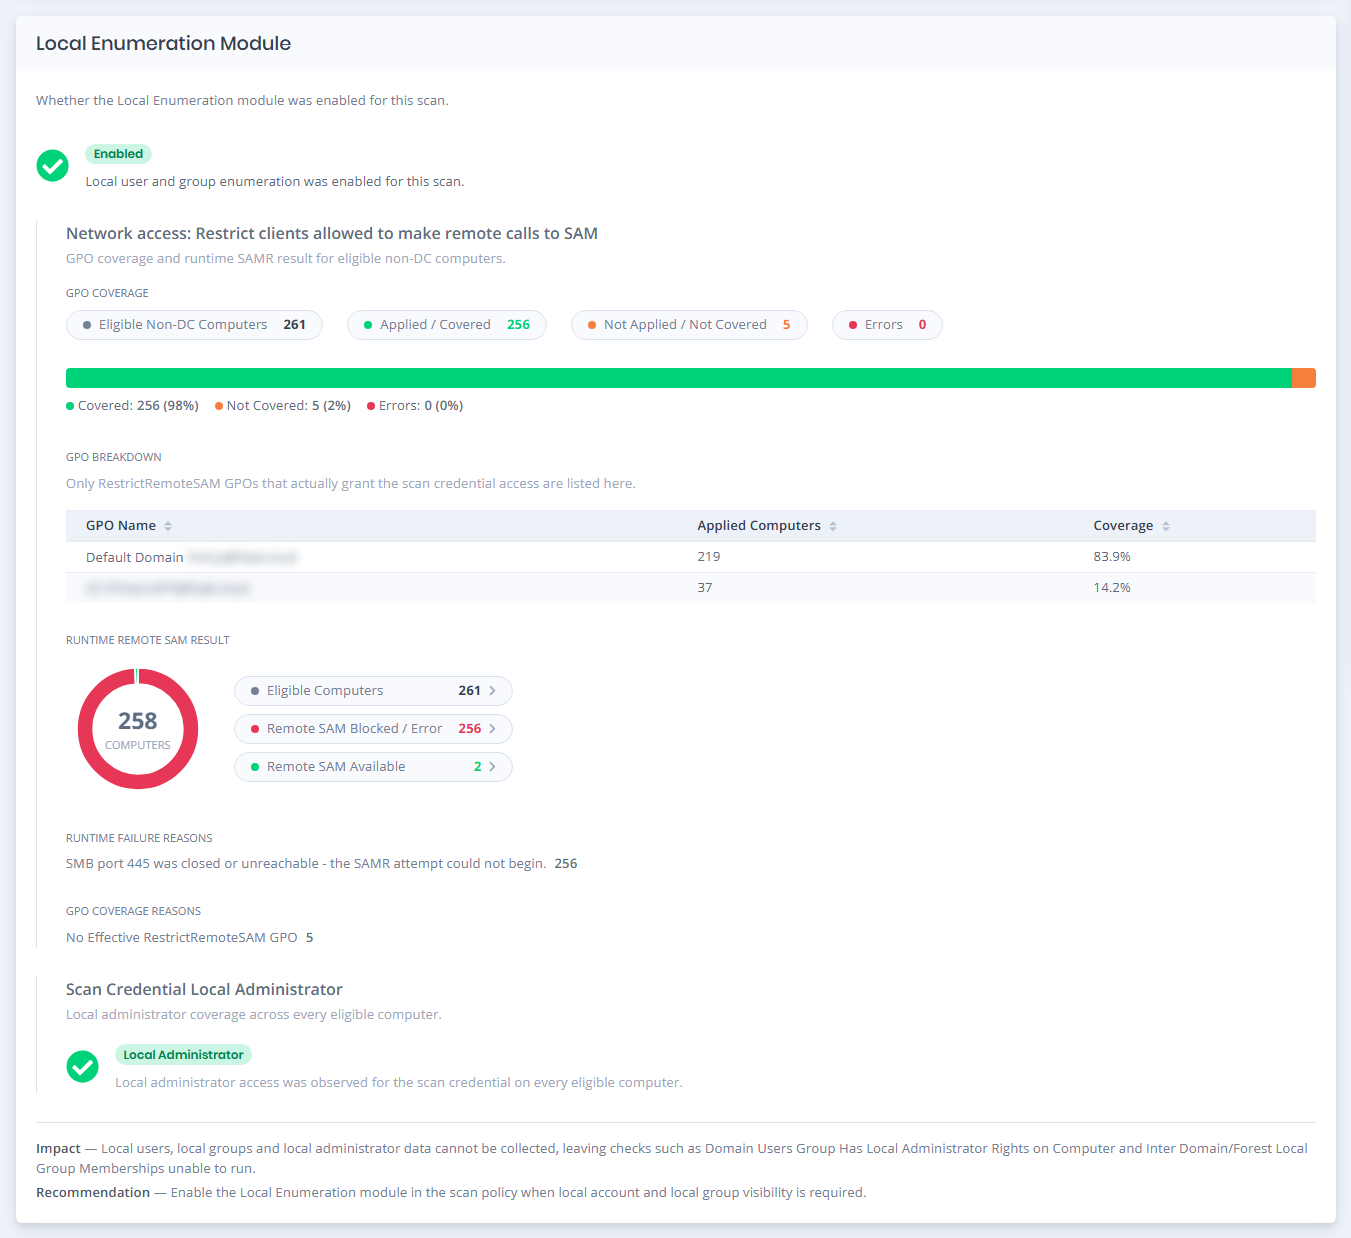
Shows whether the **Local Enumeration** module was enabled for the selected scan (**Enabled** or **Disabled**). When enabled, the scan can collect local user, local group, and local administrator information from eligible computers.

#### Network access: Restrict clients allowed to make remote calls to SAM

Shows whether eligible non-Domain Controller computers are covered by the required Remote SAM policy and whether SAM access succeeded during the scan. The section contains:

* **GPO COVERAGE**: **Eligible Non-DC Computers**, **Applied / Covered**, **Not Applied / Not Covered** and **Errors**, with the covered, not covered and error shares.
* **GPO BREAKDOWN**: the GPOs that configure the setting, with **GPO Name**, **Applied Computers** and **Coverage** columns.
* **RUNTIME REMOTE SAM RESULT**: **Eligible Computers**, **Remote SAM Blocked / Error** and **Remote SAM Available**.
* **RUNTIME FAILURE REASONS** and **GPO COVERAGE REASONS**: the number of computers for each reason, for example `SMB port 445 was closed or unreachable - the SAMR attempt could not begin.` or `No Effective RestrictRemoteSAM GPO`.

#### Scan Credential Local Administrator

Shows whether local administrator access was observed for the scan credential across eligible computers (**Local Administrator** or **Not Local Administrator**).

This helps indicate whether the credential has the expected local administrator coverage for local enumeration.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-70b551f4fc29fd6a9fb68f4ea7fb59c4ef7042c8%2Fdashboard-scan-health-image-7.png?alt=media" alt=""><figcaption><p><strong>Local Enumeration Module</strong></p></figcaption></figure>

### SMB Share Enumeration

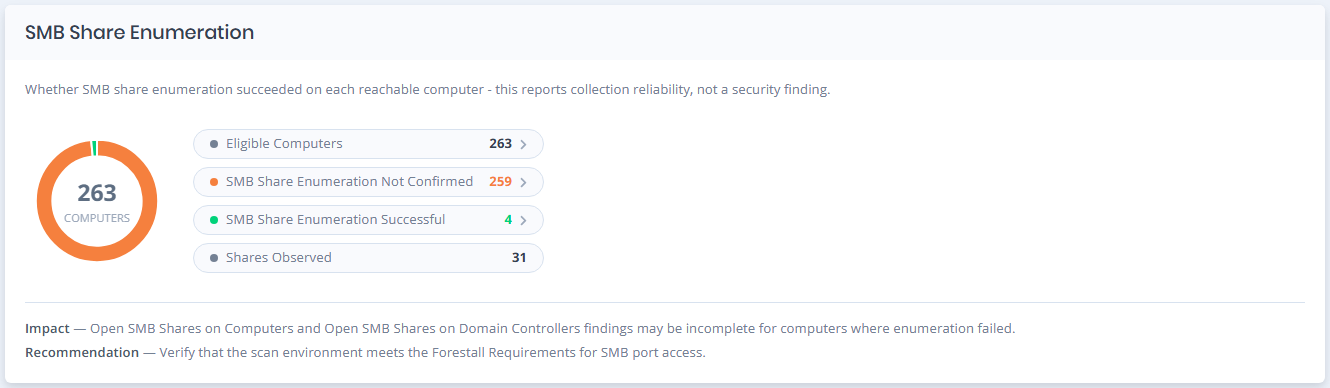
SMB Share Enumeration shows whether SMB share collection was successfully completed for eligible computers. It reports collection reliability, not a security finding.

The section displays **Eligible Computers**, **SMB Share Enumeration Not Confirmed**, **SMB Share Enumeration Successful**, **Shares Observed**, and the **COLLECTION FAILURE REASONS** when available.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-44ea7246b166803747d90d81941323aebb5b06f5%2Fdashboard-scan-health-image-6.png?alt=media" alt=""><figcaption><p><strong>SMB Share Enumeration</strong></p></figcaption></figure>

### Certificate Services

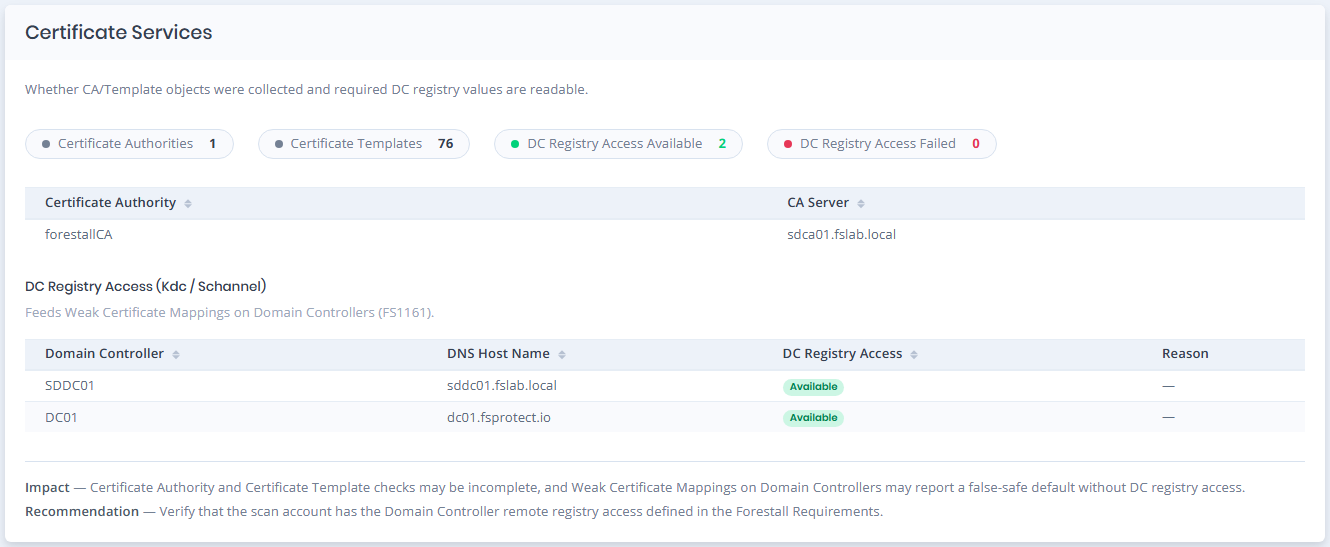
Certificate Services shows whether Certificate Authority and Certificate Template objects were collected successfully and whether the required registry information can be read from Domain Controllers.

The section displays the number of **Certificate Authorities**, **Certificate Templates**, **DC Registry Access Available** and **DC Registry Access Failed**, followed by the discovered Certificate Authorities (**Certificate Authority**, **CA Server**). When no Certificate Authority was returned, a notice says that the forest may not contain an Enterprise CA, or that the scan credential may not have visibility of CA objects.

The **DC Registry Access (Kdc / Schannel)** table feeds the **Weak Certificate Mappings on Domain Controllers (FS1161)** check. It lists each **Domain Controller** with its **DNS Host Name**, the **DC Registry Access** result and the **Reason** when the Kdc and Schannel values could not be read.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-3060e6828123fa01a094fc7b059b6dc81d1de58e%2Fdashboard-scan-health-image-5.png?alt=media" alt=""><figcaption><p><strong>Certificate Services</strong></p></figcaption></figure>

### DNS Node Read Access

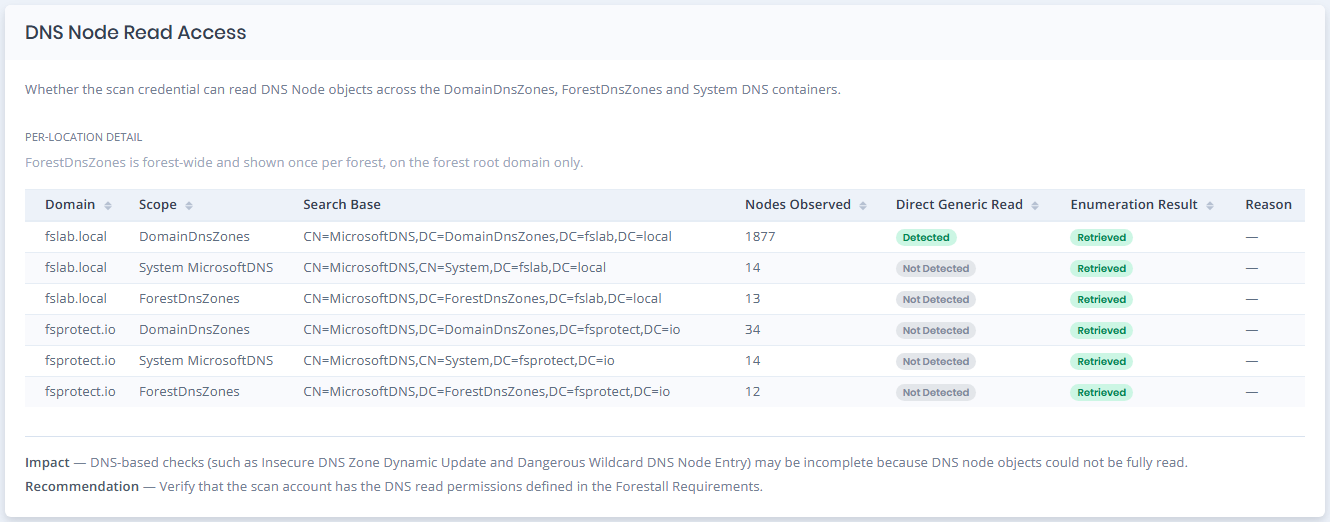
DNS Node Read Access shows whether the scan credential can read DNS Node objects from the required Active Directory DNS locations.

The section displays results separately for **DomainDnsZones**, **System MicrosoftDNS**, and **ForestDnsZones**, with the **Domain**, **Scope**, **Search Base**, **Nodes Observed**, **Direct Generic Read**, **Enumeration Result** and **Reason** columns. ForestDnsZones is forest-wide, so it is shown once per forest, on the forest root domain only.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-d482670188e0021d79f17add20dec52b534d627f%2Fdashboard-scan-health-image-3.png?alt=media" alt=""><figcaption><p><strong>DNS Node Read Access</strong></p></figcaption></figure>

### WSUS Access

WSUS Access shows whether configured WSUS references match servers detected during the scan and whether those servers are reachable.

The section displays the number of **Configured References** and **Detected Servers**, and a table with the **Target**, **Source**, **Defined In** (the GPO where the WSUS setting is defined), **Reachability** and **Reason** columns.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-46c76dc264e0ce67b42103796791d73280da3be9%2Fdashboard-scan-health-image-4.png?alt=media" alt=""><figcaption><p><strong>WSUS Access</strong></p></figcaption></figure>

#### Example: WSUS Access Not Reachable

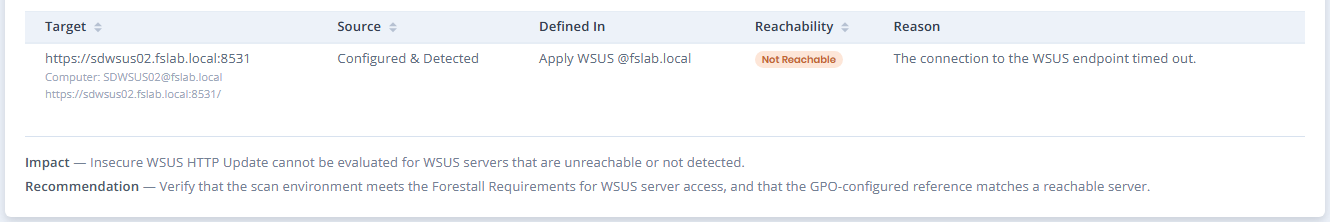
This example shows a WSUS server that was detected and matched to a configured WSUS reference, but the endpoint could not be reached during the scan.

The **Reachability** result is shown as **Not Reachable**, and the **Reason** field explains the connection issue.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-36dc76aa50bdca7f71e5e29a24880970ad7aa83e%2Fdashboard-scan-health-image-10.png?alt=media" alt=""><figcaption><p>WSUS Access: Not Reachable</p></figcaption></figure>

### DMSA Read Access

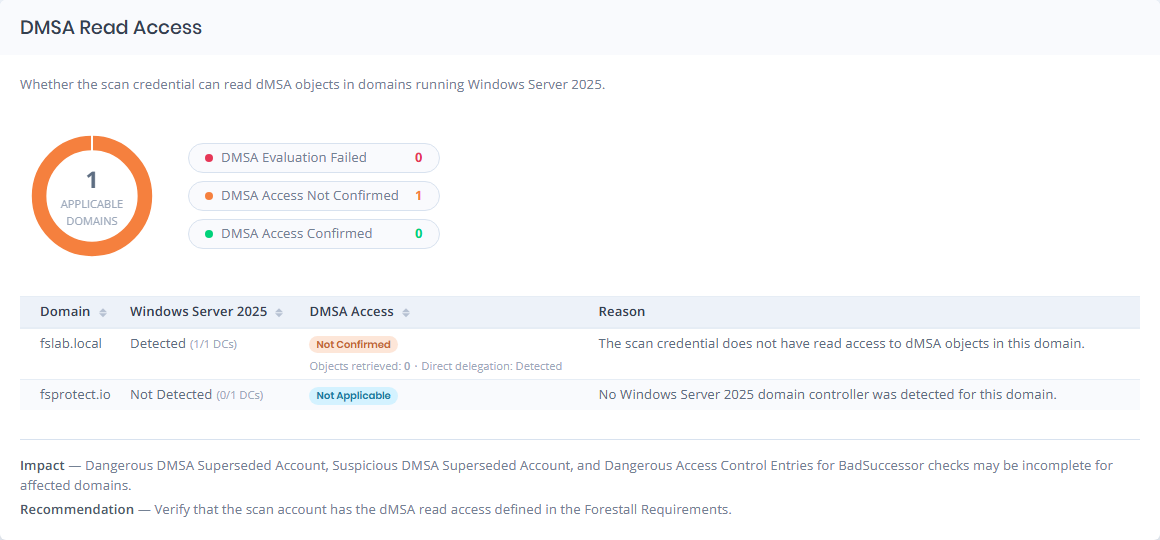
DMSA Read Access shows whether the scan credential can read **Delegated Managed Service Account (dMSA)** objects in domains running Windows Server 2025.

The section displays the number of applicable domains and whether dMSA access was confirmed, not confirmed, or could not be evaluated. The domain table lists the **Domain**, the detected **Windows Server 2025** Domain Controllers, the **DMSA Access** result and the **Reason** for the result.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-b746c0b6e03e0bf5b651a771100b64f889628c9d%2Fdashboard-scan-health-image-2.png?alt=media" alt=""><figcaption><p><strong>DMSA Read Access</strong></p></figcaption></figure>

#### Example 1: DMSA Access Not Confirmed

This example shows a domain where dMSA access could not be confirmed for the scan credential.

No direct dMSA delegation was detected and no dMSA objects were retrieved. This may indicate insufficient read access or that the domain does not contain any dMSA objects. The **Reason** field explains the condition behind the result.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-1ed240789b5f6bed809805ab8963ff51b00b1b1e%2Fdashboard-scan-health-image-8.png?alt=media" alt=""><figcaption><p>DMSA Access Not Confirmed</p></figcaption></figure>

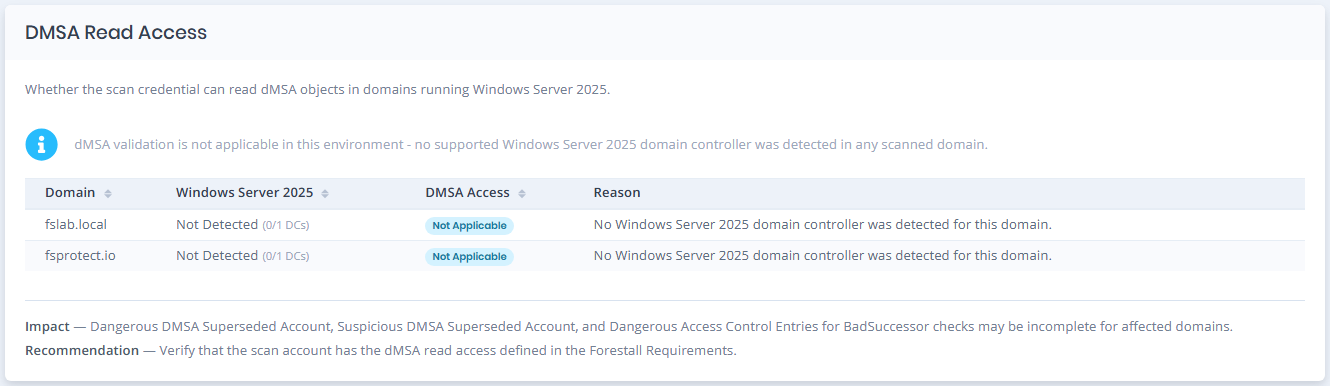
#### Example 2: DMSA Read Access Not Applicable

This example shows an environment where DMSA Read Access evaluation is not applicable because no supported Windows Server 2025 Domain Controller was detected.

The domain is marked as **Not Applicable**, and the **Reason** field explains why DMSA validation was not performed.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-2bfd0c58bf2dbd98c3b0b50e32018f0dc319482e%2Fdashboard-scan-health-image-9.png?alt=media" alt=""><figcaption><p>DMSA Read Access: Not Applicable</p></figcaption></figure>

### Permission Audit Coverage

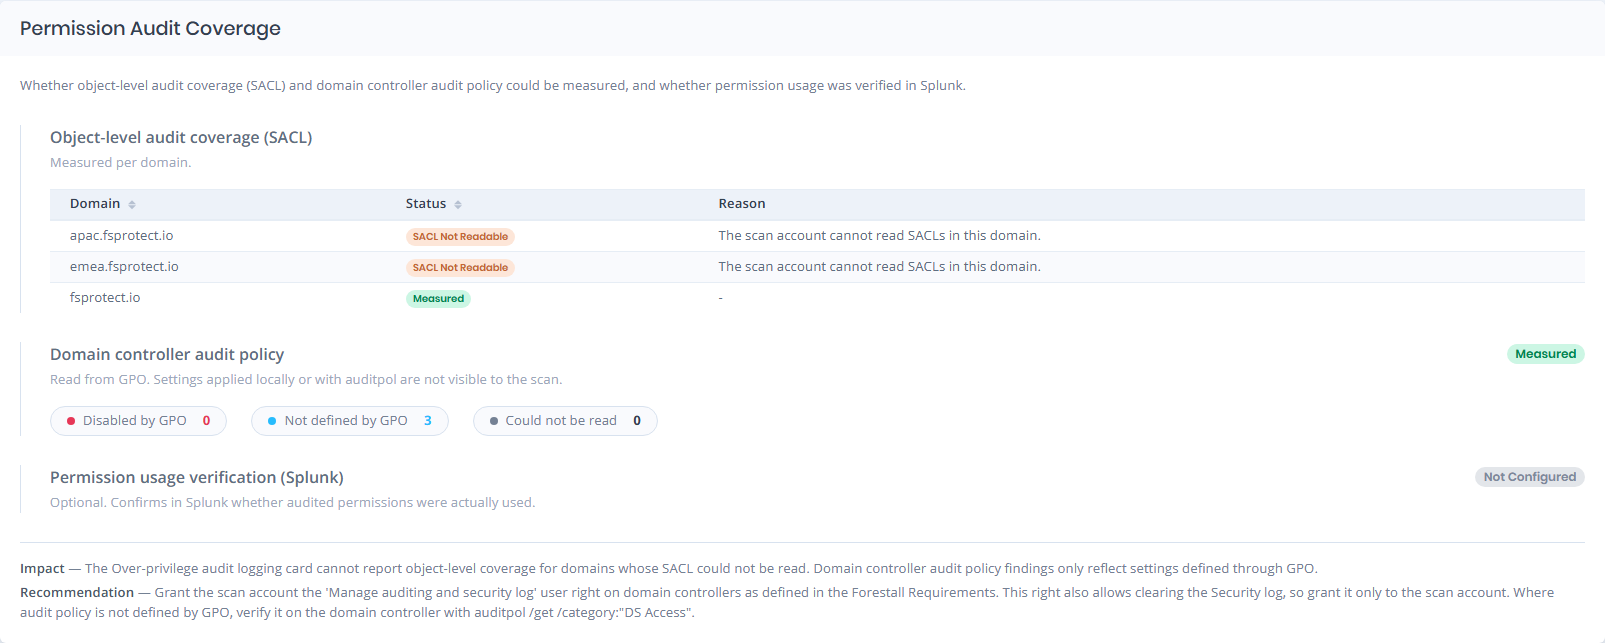
Permission Audit Coverage shows what could be measured for the [Over-privilege audit logging](/forestall/dashboard.md#over-privilege-audit-logging) card on the Dashboard. The section is always shown. When the scan policy does not enable the **Over-Privilege Analysis (Beta)** module, it states: "The Over-Privilege Analysis module was not enabled for this scan, so audit coverage was not measured."

The **Object-level audit coverage (SACL)** table lists each domain as **Measured**, **SACL Not Readable** or **Read Failed**. **SACL Not Readable** means the Forestall user does not have the `Manage auditing and security log` right on the Domain Controllers of that domain (Requirement 15 in [Requirements](/forestall/introduction/requirements.md)).

The **Domain controller audit policy** section displays the number of Domain Controllers whose required audit settings are **Disabled by GPO**, **Not defined by GPO**, or **Could not be read**. Audit settings applied locally or with `auditpol` are not read by the scan, so Domain Controllers without a GPO setting should be checked on the server.

The **Permission usage verification (Splunk)** section shows whether audited permissions were checked in Splunk. The result is **Verified**, **Not Configured**, **Failed** or **Skipped**.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-0f674bf76671ac6493c0737a52c0c4ffac5d2ab7%2Fdashboard-scan-health-image-11.png?alt=media" alt=""><figcaption><p><strong>Permission Audit Coverage</strong></p></figcaption></figure>