> For the complete documentation index, see [llms.txt](https://docs.forestall.io/forestall/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.forestall.io/forestall/unified-identities/gcp-identities/roles.md).
# Roles
Open **Unified Identities › Resources**, filter **Providers** to **GCP Identities › Role**, then select a row to open its details.
Roles
## Roles Details
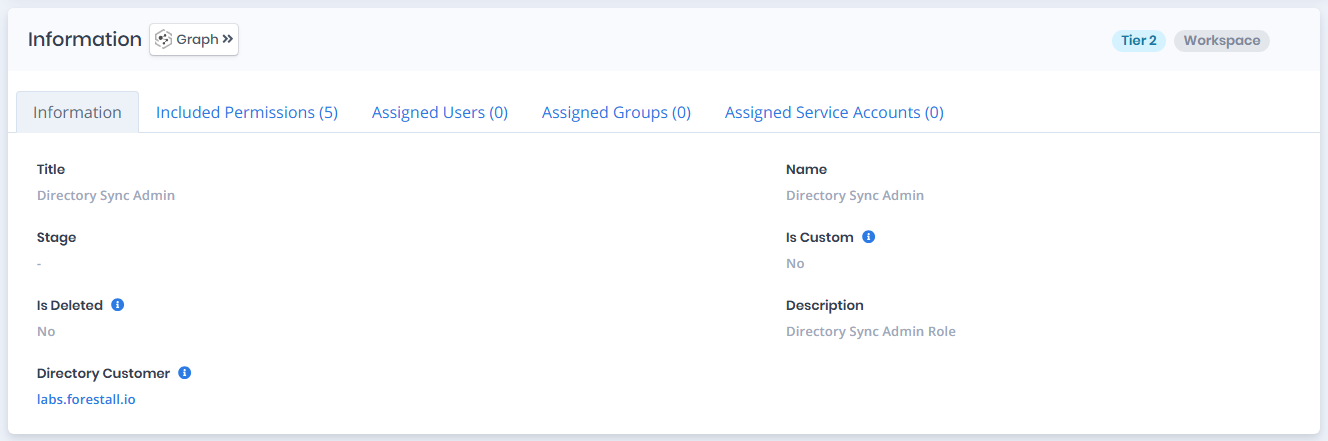
Opening a role shows the `Information` card with the `Information`, `Included Permissions`, `Assigned Users`, `Assigned Groups` and `Assigned Service Accounts` tabs, and an `Issues` panel when the role has issues. The role header has no risk score.
{% hint style="info" %}
You can analyze the object in the [Graph](/forestall/visualize/visualize.md) by clicking the **Graph »** button next to the `Information` title. For a shadow admin the button reads **Admin Path »** and opens the shortest path to admin objects (see [Object Detail Pages](/forestall/unified-identities.md#object-detail-pages)).
{% endhint %}
Role Details
## Information
`Information` card can contain different badges to highlight important attributes.
| Badge | Description |
| ----------------------- | ------------------------------------------------------------------------------------- |
| **Tier 0** / **Tier 2** | The tier of the role. |
| **Privileged** | Indicates that the role is privileged. |
| **IAM** / **Workspace** | The source of the role: a Google Cloud IAM role or a Google Workspace admin role. |
| **Shadow** | Indicates that the object can compromise admin objects with at least one attack path. |
The Information tab contains attributes about the GCP Role.
| Attribute | Description |
| ------------------ | ------------------------------------------------------------------------------------------------------------- |
| Title | The human-readable title of the role (e.g., `Custom Org Role 1`). |
| Name | The full resource name of the role (e.g., `organizations/749862357432/roles/CustomOrgRole1`). |
| Stage | The launch stage of the role indicating its maturity level (e.g., `Alpha`). |
| Is Custom | Indicates whether the role is a custom role created by the organization, as opposed to a predefined GCP role. |
| Is Deleted | Indicates whether the role has been deleted. |
| Description | A text description of the role's purpose and creation details. |
| Directory Customer | The customer domain associated with this role (e.g., `labs.forestall.io`). Shown for Workspace roles only. |
Each of the tabs below lists its rows in a `Name` column.
### Included Permissions
Lists all permissions granted by this role.
### Assigned Users
Lists all users who have been assigned this role.
### Assigned Groups
Lists all groups that have been assigned this role.
### Assigned Service Accounts
Lists all service accounts that have been assigned this role.