
Summary
| Forestall ACL Alias | AZ_ADD_MEMBERS |
| Entra ID Alias | Add Members (Group) |
| Affected Object Types | AZ Group |
| Exploitation Certainty | Certain |
| Graph Permission / Role | Directory roles (e.g., Groups Administrator, User Administrator) or being a Group Owner |
Description
AZ_ADD_MEMBERS represents the ability for a principal (user, service principal, or group owner) to add members to a Microsoft Entra ID group. By adding themselves (or a controlled identity) into a privileged group, an attacker can:
- Inherit Azure RBAC permissions if the group is assigned to subscriptions/resource groups/resources.
- Inherit directory roles when the group is role-assignable (
isAssignableToRole = true).
Therefore, any identity with add-member capability on sensitive groups can quickly escalate privileges by modifying group membership.
Identification
PowerShell
# Requires: Install-Module Microsoft.Graph -Scope CurrentUser# Connect-MgGraph -Scopes "Directory.Read.All","Group.Read.All","RoleManagement.Read.Directory"
# Get users in privileged roles that can add group members$roles = @('Global Administrator','Privileged Role Administrator','Groups Administrator','User Administrator')$roleMembers = Get-MgDirectoryRole -All | Where-Object { $_.DisplayName -in $roles } | ForEach-Object {    $role = $_.DisplayName    Get-MgDirectoryRoleMember -DirectoryRoleId $_.Id -All | ForEach-Object {        [pscustomobject]@{ Role = $role; Member = $_.AdditionalProperties['displayName']; Id = $_.Id }    }}
# Get all group owners$groupOwners = Get-MgGroup -All | ForEach-Object {    $g = $_    Get-MgGroupOwner -GroupId $g.Id -All -ErrorAction SilentlyContinue | ForEach-Object {        [pscustomobject]@{            Group = $g.DisplayName            Owner = $_.AdditionalProperties['displayName']            Type  = ($_.AdditionalProperties['@odata.type'] -replace '#microsoft.graph.','')        }    }}
"=== PRIVILEGED ROLE MEMBERS ==="$roleMembers | Format-Table -AutoSize"=== GROUP OWNERS ==="$groupOwners | Sort-Object Group | Format-Table -AutoSize
Azure CLI
Check owners and (if you are owner or hold the right role) add a member:
# List group ownersaz ad group owner list --group "<GroupObjectIdOrName>" --query "[].{displayName:displayName,id:id}"
# Add a member (requires owner/appropriate role)az ad group member add --group "<GroupObjectIdOrName>" --member-id "<ObjectIdOfUserOrSP>"
Azure Portal
-
Open Microsoft Entra admin center -> Groups -> select the target group.
-
Go to Owners and list all identities shown there.
- Anyone listed as Owner can add members to this group.
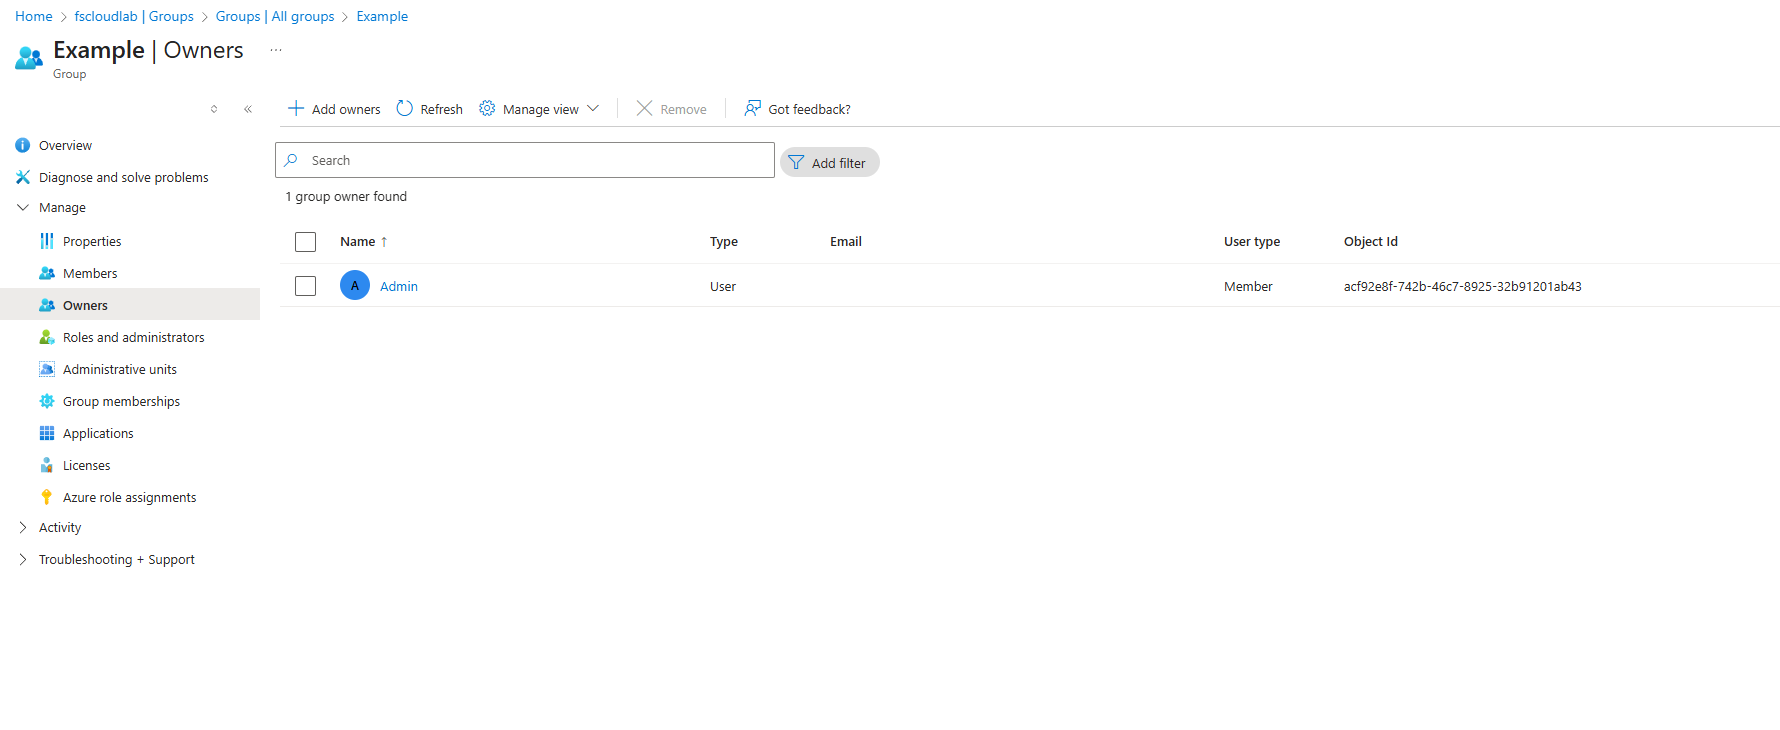
Group owners in the Entra admin center
-
Go to Properties and check “Is this group assignable to roles in Entra ID?”
- If True (role-assignable): only Global Administrator (GA) and Privileged Role Administrator (PRA) (besides Owners) can add members.
- If False: GA, PRA, Groups Administrator (GAd), User Administrator (UAd) (besides Owners) can add members.
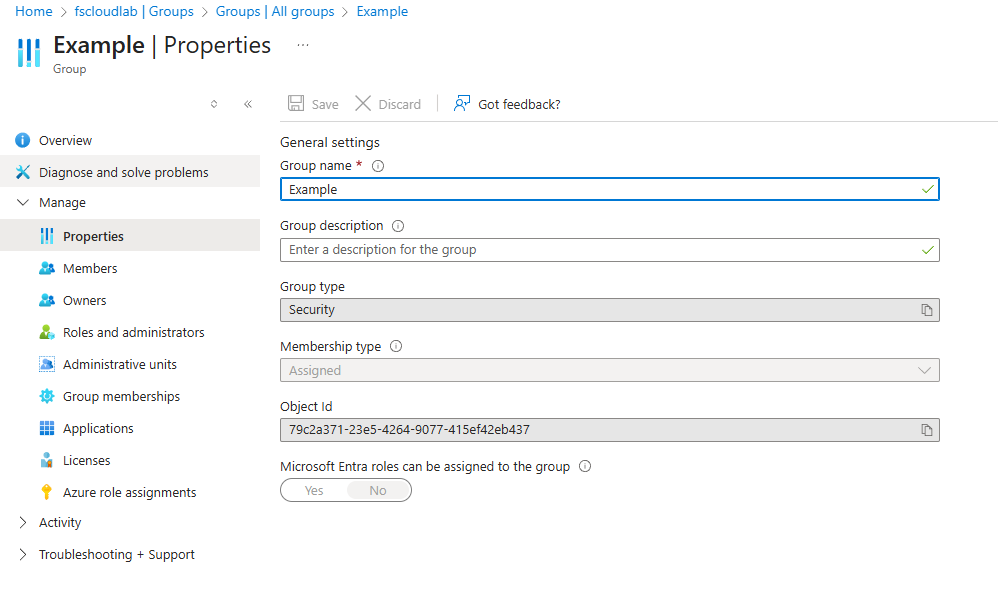
Group role-assignable property in the Entra admin center
-
Go to Roles & administrators and open each relevant role (GA, PRA, GAd, UAd).
-
In each role -> Assignments: list the users and groups that hold the role.
-
If a group holds the role, enumerate its transitive members (nested included) to get the effective users who can add members.
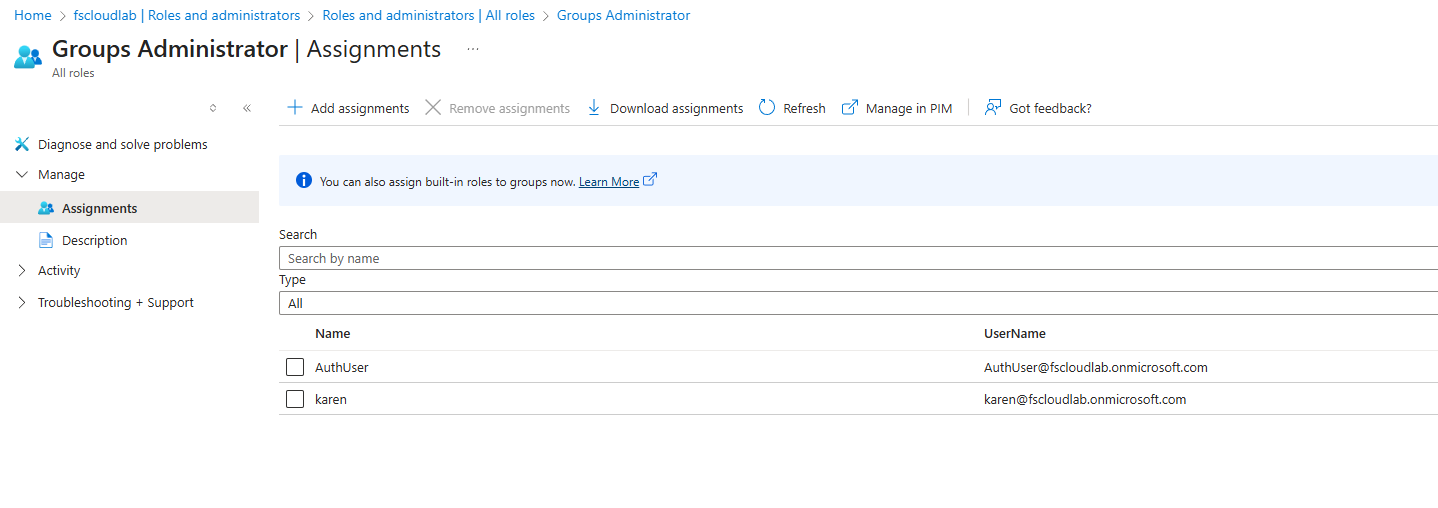
Groups Administrator role assignments in Entra admin center
-
Exploitation
Group ownership is one of the primary ways to obtain add-member capability over a group. See the AZ_OWNER edge for how object ownership in Entra ID grants this and related privileges.
PowerShell
# Using Microsoft Graph PowerShell SDKConnect-MgGraph -Scopes "GroupMember.ReadWrite.All"$group = Get-MgGroup -Filter "displayName eq 'IT Admins'"New-MgGroupMember -GroupId $group.Id -DirectoryObjectId $user.Id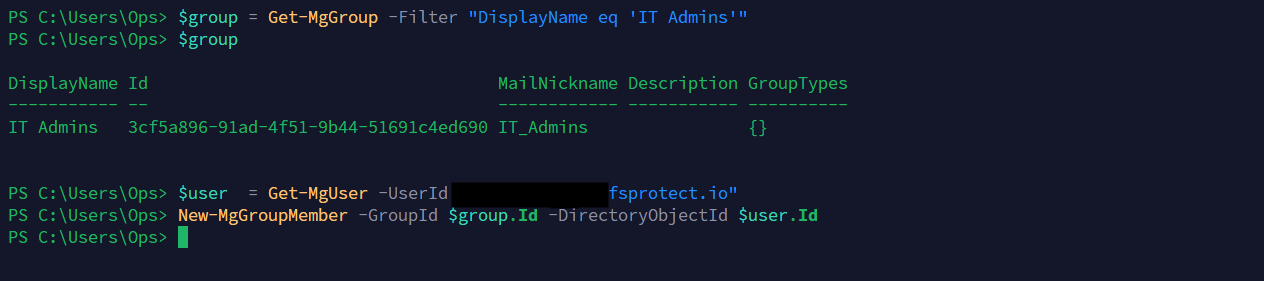
Add a group member with Microsoft Graph PowerShell
Azure Portal
- Go to Microsoft Entra ID -> Groups.
- Locate the target group using Search or filters, and open the group.
- Open Members (left menu of the group blade).
- Click Add members.
- In the picker dialog:
- Search for the identity you want to insert.
- Select the identity and click Select (or Add) to confirm.
Mitigation
- Fewer Owners means fewer identities that can add members; this directly reduces lateral-movement and privilege-escalation risk, especially for role-assignable or production-impacting groups.
- Go to Microsoft Entra ID -> Groups -> All groups.
- Filter or search to find groups that you want to remove owner(s).
- Open a target group.
- Open Owners.
- Remove any vulnerable/high-risk identities.
- Remove unnecessary / vulnerable user assignees from a role
- Go to Microsoft Entra ID -> Roles & administrators.
- In the search box, type the exact role name (e.g., Global Administrator) and click the role.
- In the left menu, click Assignments.
- Ensure Active assignments is selected.
- Find the user you want to remove.
- At the right of that row, click … (More options) -> Remove assignment.
- In the confirmation dialog, click Remove.
Detection
Use the Microsoft Entra admin center:
- Open Microsoft Entra ID -> Audit logs.
- Click Category: All -> select GroupManagement -> Apply.
- Filter or review Activity for Add member to group.
- Review Initiated by (actor), Target, Date, and Status for unexpected group membership additions.
- Use Manage view -> Edit columns if any of those fields are hidden.
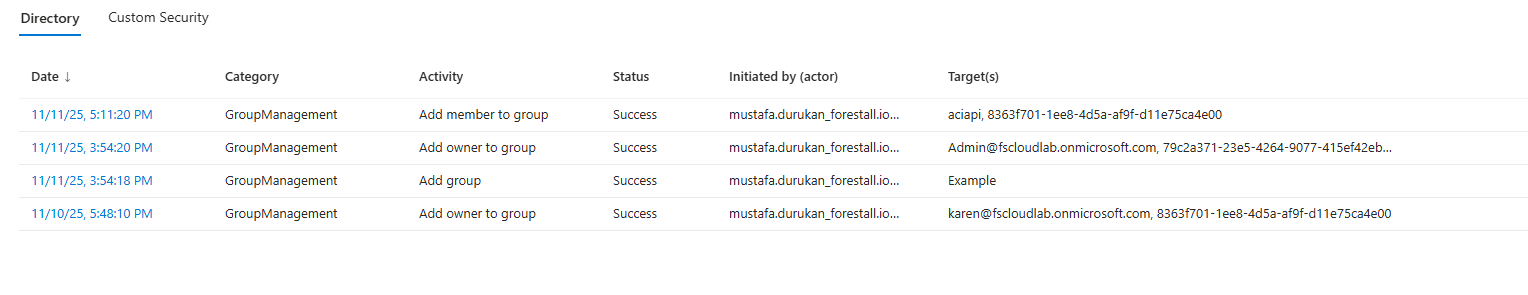
Group membership changes in directory audit logs
References
- https://learn.microsoft.com/en-us/cli/azure/ad/group/member?view=azure-cli-latest
- https://learn.microsoft.com/en-us/entra/identity/monitoring-health/concept-activity-log-schemas
- https://learn.microsoft.com/en-us/powershell/microsoftgraph/overview
- https://learn.microsoft.com/en-us/graph/api/group-post-members