
Summary
| Forestall ACL Alias | AZ_ADD_OWNER |
| Entra ID Alias | Add Owners |
| Affected Object Types | AZ App Registration, AZ Service Principal |
| Exploitation Certainty | Certain |
| Role | Directory roles: Global Administrator, Hybrid Identity Administrator, Partner Tier1 Support, Partner Tier2 Support, Directory Synchronization Accounts, or being an existing Owner |
Description
AZ_ADD_OWNER represents the ability for a principal to add new owners to an App Registration or Service Principal in Microsoft Entra ID.
Owners of an App Registration or Service Principal have full administrative control, including the ability to:
- Add or remove other owners.
- Add credentials (secrets or certificates) to the application.
- Modify application permissions and API access.
- Use the Service Principal’s identity to authenticate and access resources.
Therefore, any identity capable of adding owners to App Registrations or Service Principals can escalate privileges by granting themselves or a controlled identity full control over these objects.
Identification
PowerShell
# Requires: Install-Module Microsoft.Graph -Scope CurrentUser# Connect-MgGraph -Scopes "Directory.Read.All","Application.Read.All","RoleManagement.Read.Directory"
# Get users in privileged roles that can add owners to Apps/SPs$roles = @('Global Administrator','Hybrid Identity Administrator','Partner Tier1 Support','Partner Tier2 Support','Directory Synchronization Accounts')$roleMembers = Get-MgDirectoryRole -All | Where-Object { $_.DisplayName -in $roles } | ForEach-Object {    $role = $_.DisplayName    Get-MgDirectoryRoleMember -DirectoryRoleId $_.Id -All | ForEach-Object {        [pscustomobject]@{ Role = $role; Member = $_.AdditionalProperties['displayName']; Id = $_.Id }    }}
# Get all App Registration owners$appOwners = Get-MgApplication -All | ForEach-Object {    $app = $_    Get-MgApplicationOwner -ApplicationId $app.Id -All -ErrorAction SilentlyContinue | ForEach-Object {        [pscustomobject]@{            AppName = $app.DisplayName            AppId   = $app.AppId            Owner   = $_.AdditionalProperties['displayName']            Type    = ($_.AdditionalProperties['@odata.type'] -replace '#microsoft.graph.','')        }    }}
# Get all Service Principal owners$spOwners = Get-MgServicePrincipal -All | ForEach-Object {    $sp = $_    Get-MgServicePrincipalOwner -ServicePrincipalId $sp.Id -All -ErrorAction SilentlyContinue | ForEach-Object {        [pscustomobject]@{            SPName = $sp.DisplayName            SPId   = $sp.Id            Owner  = $_.AdditionalProperties['displayName']            Type   = ($_.AdditionalProperties['@odata.type'] -replace '#microsoft.graph.','')        }    }}
"=== PRIVILEGED ROLE MEMBERS ==="$roleMembers | Format-Table -AutoSize"=== APP REGISTRATION OWNERS ==="$appOwners | Sort-Object AppName | Format-Table -AutoSize"=== SERVICE PRINCIPAL OWNERS ==="$spOwners | Sort-Object SPName | Format-Table -AutoSize
Azure CLI
List and add owners to App Registrations or Service Principals:
# List App Registration ownersaz ad app owner list --id "<AppObjectId>" --query "[].{displayName:displayName,id:id}"
# Add owner to App Registrationaz ad app owner add --id "<AppObjectId>" --owner-object-id "<ObjectIdOfUserOrSP>"
# List Service Principal ownersaz ad sp owner list --id "<SPObjectId>" --query "[].{displayName:displayName,id:id}"
Azure Portal
-
Open Microsoft Entra admin center -> Applications -> App registrations (or Enterprise applications for Service Principals).
-
Select the target application.
-
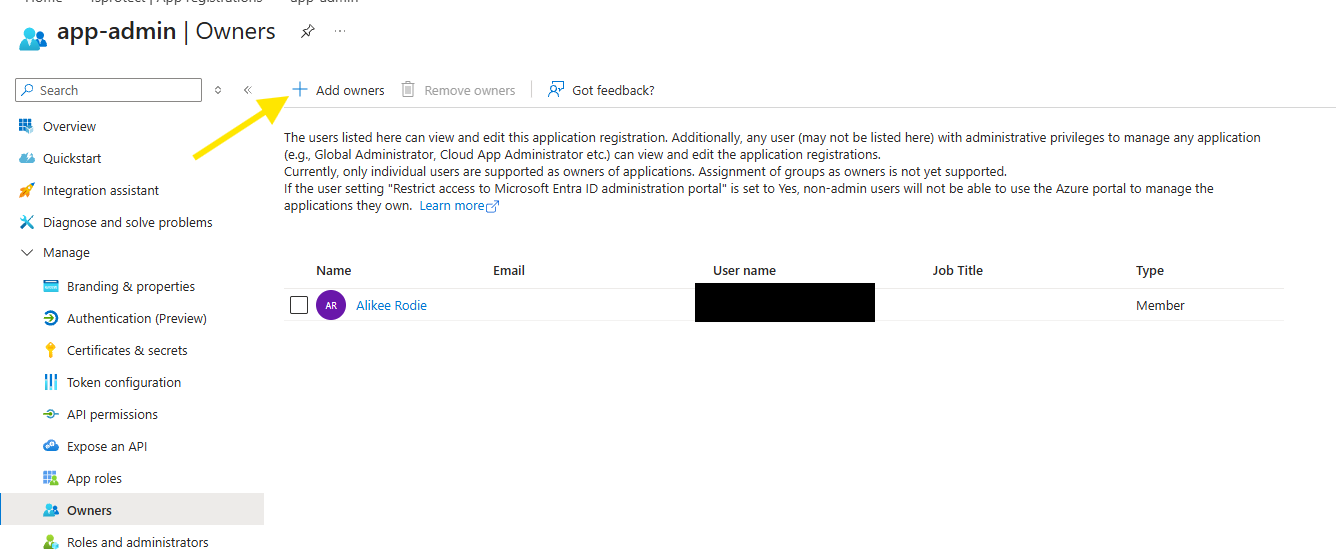
Go to Owners (left menu).
- Anyone listed as Owner can add other owners.
- Click Add owners -> search for the identity -> click Select.
-
Go to Roles & administrators to view who holds the privileged roles:
- Global Administrator
- Hybrid Identity Administrator
- Partner Tier1 Support
- Partner Tier2 Support
- Directory Synchronization Accounts
Note: You will not see these role-based privileges when auditing permissions in the Azure portal or API. These are implicit permissions granted by the directory roles.
Exploitation
PowerShell (Microsoft Graph SDK)
Connect-MgGraph -Scopes "Application.ReadWrite.All"$app = Get-MgApplication -Filter "displayName eq 'TargetApp'"
$params = @{ "@odata.id" = "https://graph.microsoft.com/v1.0/directoryObjects/$($user.Id)" }New-MgApplicationOwnerByRef -ApplicationId $app.Id -BodyParameter $params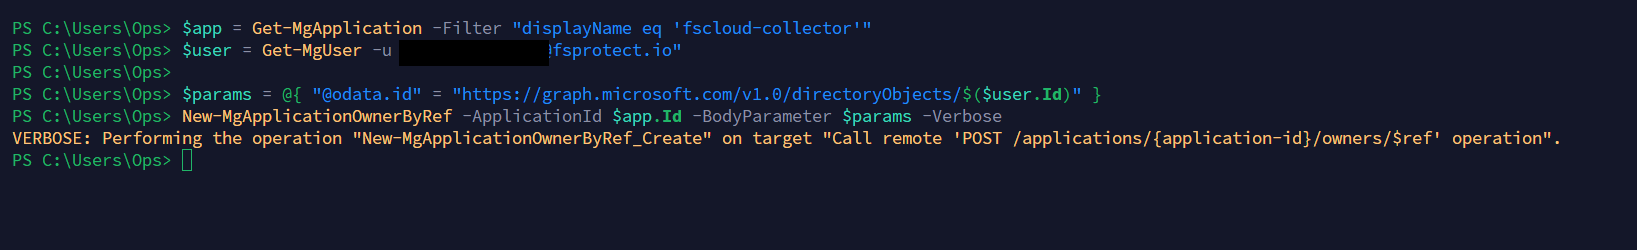
Add an application owner with PowerShell
Mitigation
- Limit owners on sensitive App Registrations and Service Principals
- Go to Microsoft Entra ID -> App registrations or Enterprise applications.
- Open the target application.
- Go to Owners.
- Remove any unnecessary or high-risk identities.
- Review and limit privileged role assignments
- Go to Microsoft Entra ID -> Roles & administrators.
- Review assignments for: Global Administrator, Hybrid Identity Administrator, Partner Tier1 Support, Partner Tier2 Support, Directory Synchronization Accounts.
- Remove unnecessary assignments.
Detection
Use the Microsoft Entra admin center:
- Open Microsoft Entra ID -> Audit logs.
- Filter Category for ApplicationManagement.
- Filter or review Activity for Add owner to application and Add owner to service principal.
- Review Initiated by (actor), Target, Date, and Status for unexpected owner additions.
- Use Manage view -> Edit columns if any of those fields are hidden.
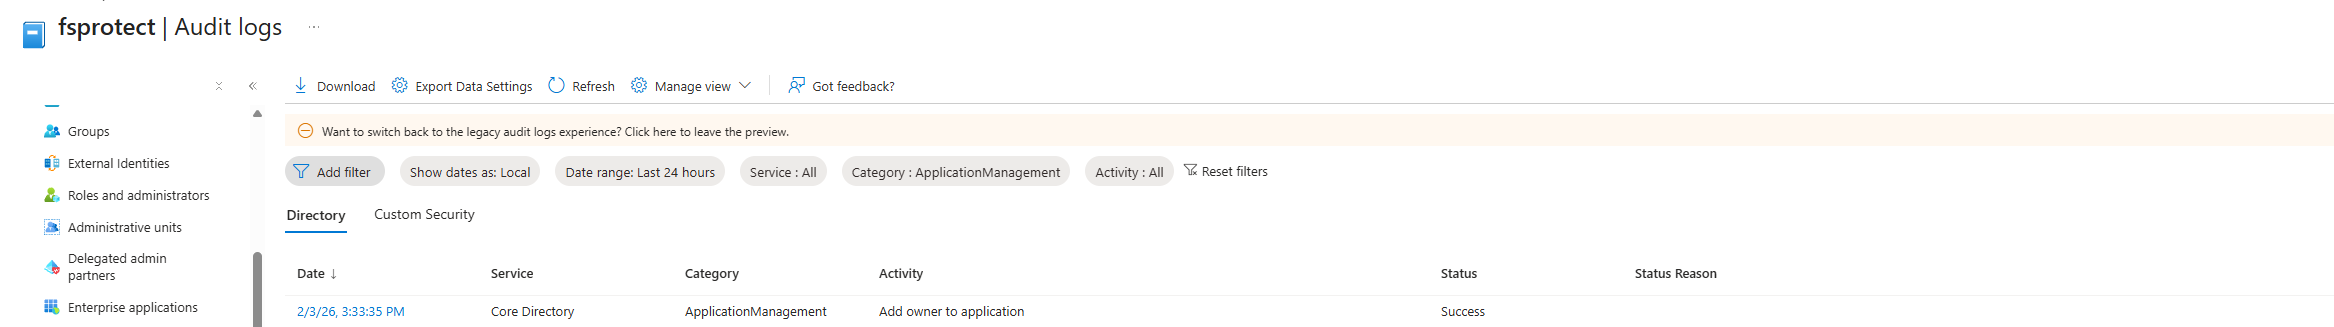
Add owner to application audit logs