
Summary
| Forestall ACL Alias | AZ_RDP |
| Azure Alias | Virtual Machine User Login / RDP with Entra ID |
| Affected Object Types | Windows Virtual Machines |
| Exploitation Certainty | Certain |
| Azure RBAC Roles | Virtual Machine User Login (fb879df8-f326-4884-b1cf-06f3ad86be52), Virtual Machine Administrator Login (1c0163c0-47e6-4577-8991-ea5c82e286e4) |
Custom Role Data Actions:
Microsoft.Compute/virtualMachines/login/actionMicrosoft.Compute/virtualMachines/loginAsAdmin/action
Filter: Windows VMs with the AADLoginForWindows extension and a system-assigned managed identity
Description
AZ_RDP represents the ability to RDP into Windows Azure VMs using Microsoft Entra ID credentials. This is a data-plane permission that enables interactive desktop access without requiring local VM credentials.
Prerequisites for this edge:
- The VM must have the AADLoginForWindows extension installed.
- The VM must have a system-assigned managed identity enabled.
- The principal must have Virtual Machine User Login (standard user) or Virtual Machine Administrator Login (local admin) role.
| Role | Access Level |
|---|---|
| Virtual Machine User Login | Remote Desktop Users group |
| Virtual Machine Administrator Login | Local Administrators group |
This edge is distinct from:
- AZ_EXECUTE_COMMAND - Uses RunCommand API, no interactive session.
- AZ_VM_ADMIN_LOGIN - Broader scope including SSH to Linux.
Identification
PowerShell (Az Module)
Connect-AzAccount
# List Virtual Machine User Login assignmentsGet-AzRoleAssignment -RoleDefinitionName "Virtual Machine User Login" |    Select-Object DisplayName, SignInName, ObjectType, Scope |    Format-Table -AutoSize
# List Virtual Machine Administrator Login assignmentsGet-AzRoleAssignment -RoleDefinitionName "Virtual Machine Administrator Login" |    Select-Object DisplayName, SignInName, ObjectType, Scope |    Format-Table -AutoSize
# Find Windows VMs with the Microsoft Entra login extensionGet-AzVM | ForEach-Object {    $extensions = Get-AzVMExtension -ResourceGroupName $_.ResourceGroupName -VMName $_.Name    $aadExt = $extensions | Where-Object { $_.Name -eq "AADLoginForWindows" }    if ($aadExt) {        [PSCustomObject]@{            VMName = $_.Name            ResourceGroup = $_.ResourceGroupName            OSType = $_.StorageProfile.OsDisk.OsType            AADExtension = $aadExt.Name            Identity = $_.Identity.Type        }    }} | Format-Table -AutoSize
Azure Portal
- Open Azure Portal -> navigate to the target Windows VM.
- Go to Extensions + applications -> verify AADLoginForWindows is installed.
- Go to Identity -> verify System assigned identity is enabled.
- Go to Access control (IAM) -> check for login role assignments.
Exploitation
RDP with Entra ID Credentials
Method 1: RDP File Configuration (Legacy - Disables NLA)
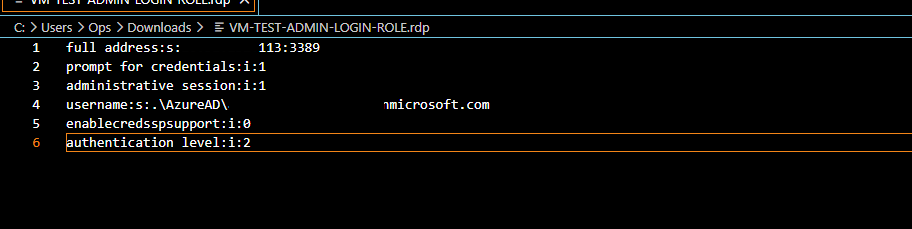
Standard RDP connection with Entra credentials requires modifying an RDP file. This method disables Network Level Authentication (NLA).
- Open Remote Desktop Connection (
mstsc.exe). - Enter the VM’s IP address or hostname.
- Click Show Options -> Save As to save the
.rdpfile locally. - Open the saved
.rdpfile in Notepad. - Add the following lines at the bottom:
enablecredsspsupport:i:0authentication level:i:2- Save the file and double-click to connect.
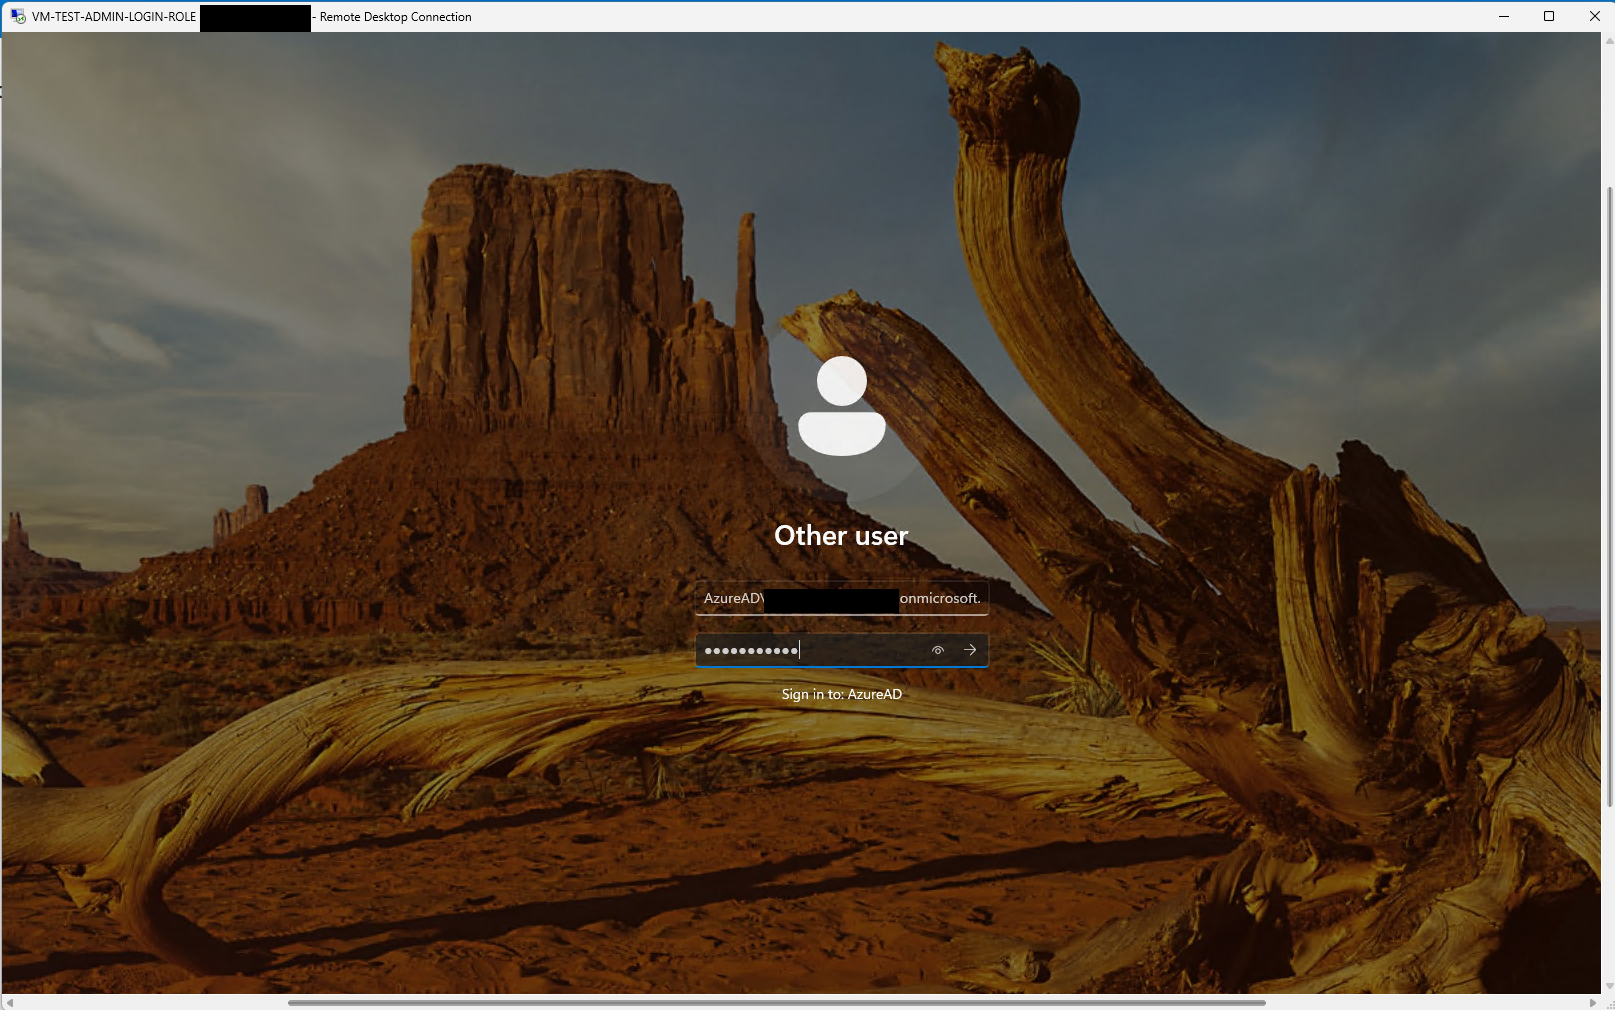
- Enter credentials in format:
.\AzureAD\[email protected]
Note: The leading
.\beforeAzureAD\prevents caching issues when the VM auto-locks and you need to sign back in. Without it, you may need to re-enterAzureAD\each time.
Method 2: Modern Entra Authentication (Keeps NLA Enabled)
For Windows 10 1809+ and Azure VMs, use modern Entra authentication which maintains NLA security:
- Save an RDP file as described above.
- Add the following lines instead:
enablerdsaadauth:i:1targetisaadjoined:i:1- Important: You must connect using the VM’s hostname (not IP address). The hostname must:
- Match the computer name registered in Entra ID.
- Be resolvable via DNS or local hosts file.
- Connect using your UPN:
[email protected]
Alternatively, in mstsc.exe:
- Click Show Options -> Advanced tab.
- Check Use a web account to sign in to the remote computer.
This method triggers a modern authentication prompt supporting MFA and Conditional Access policies.
Post-Exploitation - Standard User
With Virtual Machine User Login (Remote Desktop Users):
# Access managed identity token$response = Invoke-RestMethod -Uri "http://169.254.169.254/metadata/identity/oauth2/token?api-version=2018-02-01&resource=https://management.azure.com/" -Headers @{Metadata="true"}$response.access_token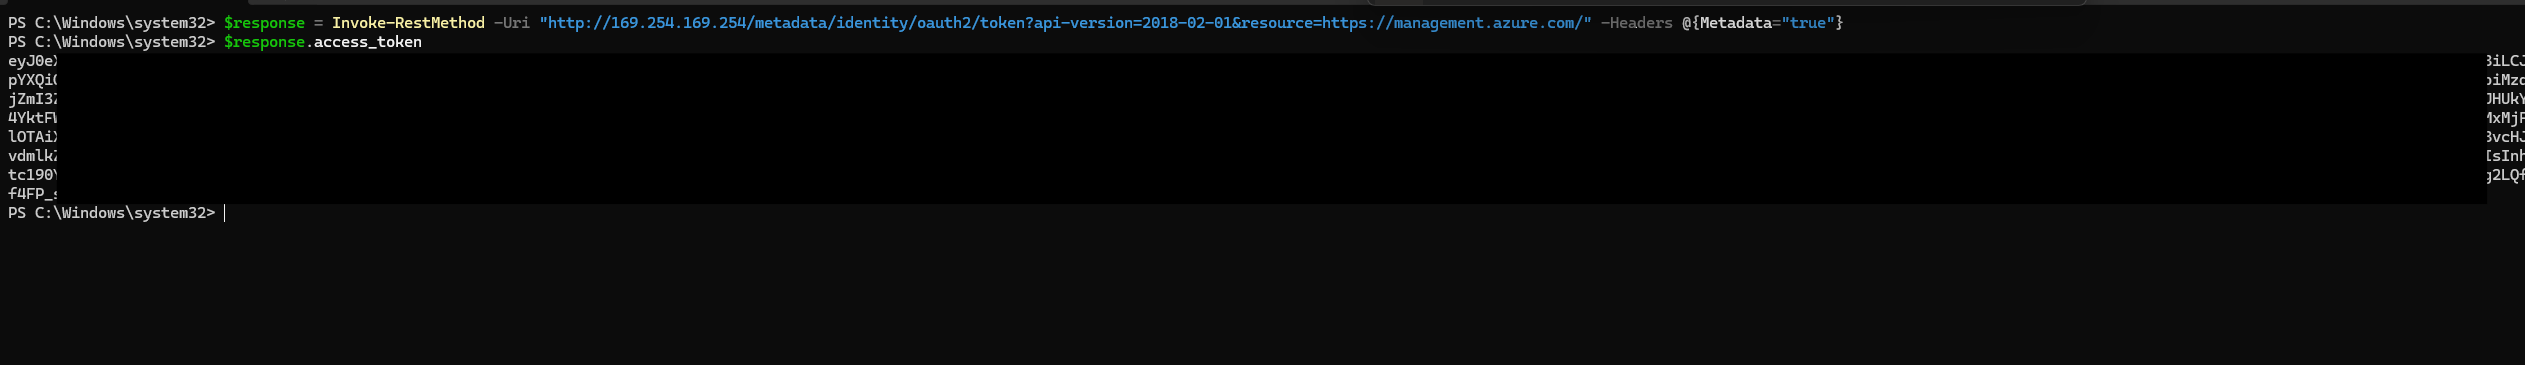
Access managed identity token powershell
Post-Exploitation - Administrator
With Virtual Machine Administrator Login (Local Administrators):
# Steal managed identity token$response = Invoke-RestMethod -Uri "http://169.254.169.254/metadata/identity/oauth2/token?api-version=2018-02-01&resource=https://management.azure.com/" -Headers @{Metadata="true"}$response.access_tokenAccess managed identity token powershell
Mitigation
-
Minimize login role assignments
- Remove Virtual Machine User/Administrator Login from identities that dont need interactive access.
- Use AZ_EXECUTE_COMMAND (RunCommand) for automated tasks instead.
-
Use Virtual Machine User Login instead of Administrator Login
- Grant standard user access unless admin is specifically required.
-
Restrict Microsoft Entra login extension deployment
- Only deploy the extension on VMs that require Entra-based authentication.
- Use Azure Policy to audit extension deployments.
-
Network security
- Restrict RDP (port 3389) access via NSGs.
- Use Azure Bastion for secure access without public endpoints.
- Enable Just-in-Time VM access.
-
Enable endpoint protection
- Deploy Microsoft Defender for Endpoint.
- Enable Credential Guard on supported Windows versions.
Detection
Use the Azure Portal and Microsoft Entra admin center:
- In Azure Portal, open the target Windows VM.
- Open Activity log and filter Operation for
loginorloginAsAdmin. - Review
Microsoft.Compute/virtualMachines/login/actionandMicrosoft.Compute/virtualMachines/loginAsAdmin/actionevents. - Open Microsoft Entra ID -> Sign-in logs and filter Application for Azure Windows VM Sign-In.
- Review User, IP address, Location, Date, and Status for unexpected RDP logins.
- On the VM blade, review Access control (IAM) for Virtual Machine User Login and Virtual Machine Administrator Login assignments.
- Open Extensions + applications and confirm whether AADLoginForWindows is present.
References
- https://learn.microsoft.com/en-us/azure/role-based-access-control/built-in-roles#virtual-machine-user-login
- https://learn.microsoft.com/en-us/entra/identity/devices/howto-vm-sign-in-azure-ad-windows
- https://learn.microsoft.com/en-us/azure/bastion/bastion-overview
- https://bradleyschacht.com/remote-desktop-to-azure-ad-joined-computer
- https://learn.microsoft.com/en-us/windows-server/remote/remote-desktop-services/remotepc/remote-desktop-connection-single-sign-on
- https://learn.microsoft.com/en-us/azure/virtual-desktop/rdp-properties