
Summary
| Forestall ACL Alias | AZ_IN_GROUP |
| Entra ID (Azure AD) Alias | Group Member |
| Affected Object Types | Users, Service Principals, Groups |
| Exploitation Certainty | Certain |
Description
AZ_IN_GROUP represents that a principal (user, service principal, or another group) is a member of a Microsoft Entra (Azure AD) group. Group membership in Entra ID is fundamental to identity management and access control, as groups are used to assign:
- Azure RBAC permissions on subscriptions, resource groups, and resources.
- Directory roles when the group is role-assignable (
isAssignableToRole = true). - Application access through Conditional Access policies and app assignments.
- License assignments for Microsoft 365 and other services.
By being a member of a group, a principal inherits all the permissions and privileges assigned to that group. This transitive relationship means that if an attacker compromises an account that is a member of a privileged group, they gain access to all resources and capabilities granted to that group.
Identification
PowerShell
Connect-MgGraph -Scopes "Group.Read.All","GroupMember.Read.All"
# Get all groups and their members$groups = Get-MgGroup -All$results = foreach ($group in $groups) {    $members = Get-MgGroupMember -GroupId $group.Id -All    foreach ($member in $members) {        [PSCustomObject]@{            GroupName  = $group.DisplayName            GroupId    = $group.Id            MemberName = $member.AdditionalProperties.displayName            MemberType = ($member.AdditionalProperties.'@odata.type' -replace '#microsoft.graph.', '')            MemberId   = $member.Id        }    }}$results | Export-Csv -Path ".\AzureGroupMembers.csv" -NoTypeInformation -Encoding UTF8
To check membership for a specific user:
Connect-MgGraph -Scopes "User.Read.All","GroupMember.Read.All"
$user = Get-MgUser -UserId $userUPN
# Get groups the user is a member of$userGroups = Get-MgUserMemberOf -UserId $user.Id -All | Where-Object { $_.AdditionalProperties.'@odata.type' -eq '#microsoft.graph.group'}
$userGroups | ForEach-Object { [PSCustomObject]@{ DisplayName = $_.AdditionalProperties.displayName Id = $_.Id }} | Format-Table -AutoSizeTo enumerate transitive group memberships (including nested groups):
Connect-MgGraph -Scopes "User.Read.All","GroupMember.Read.All"
$user = Get-MgUser -UserId $userUPN
# Get transitive group memberships (includes nested groups)$transitiveGroups = Get-MgUserTransitiveMemberOf -UserId $user.Id -All | Where-Object { $_.AdditionalProperties.'@odata.type' -eq '#microsoft.graph.group'}
$transitiveGroups | ForEach-Object { [PSCustomObject]@{ GroupName = $_.AdditionalProperties.displayName GroupId = $_.Id }} | Format-Table -AutoSizeAzure CLI
# List all groups a user is a member ofaz ad user get-member-groups --id "<UserObjectIdOrUPN>" --security-enabled-only false
# List all members of a specific groupaz ad group member list --group "<GroupObjectIdOrName>" --query "[].{displayName:displayName,id:id,type:['@odata.type']}"
# Check if a user is a member of a specific groupaz ad group member check --group "<GroupObjectIdOrName>" --member-id "<UserObjectId>"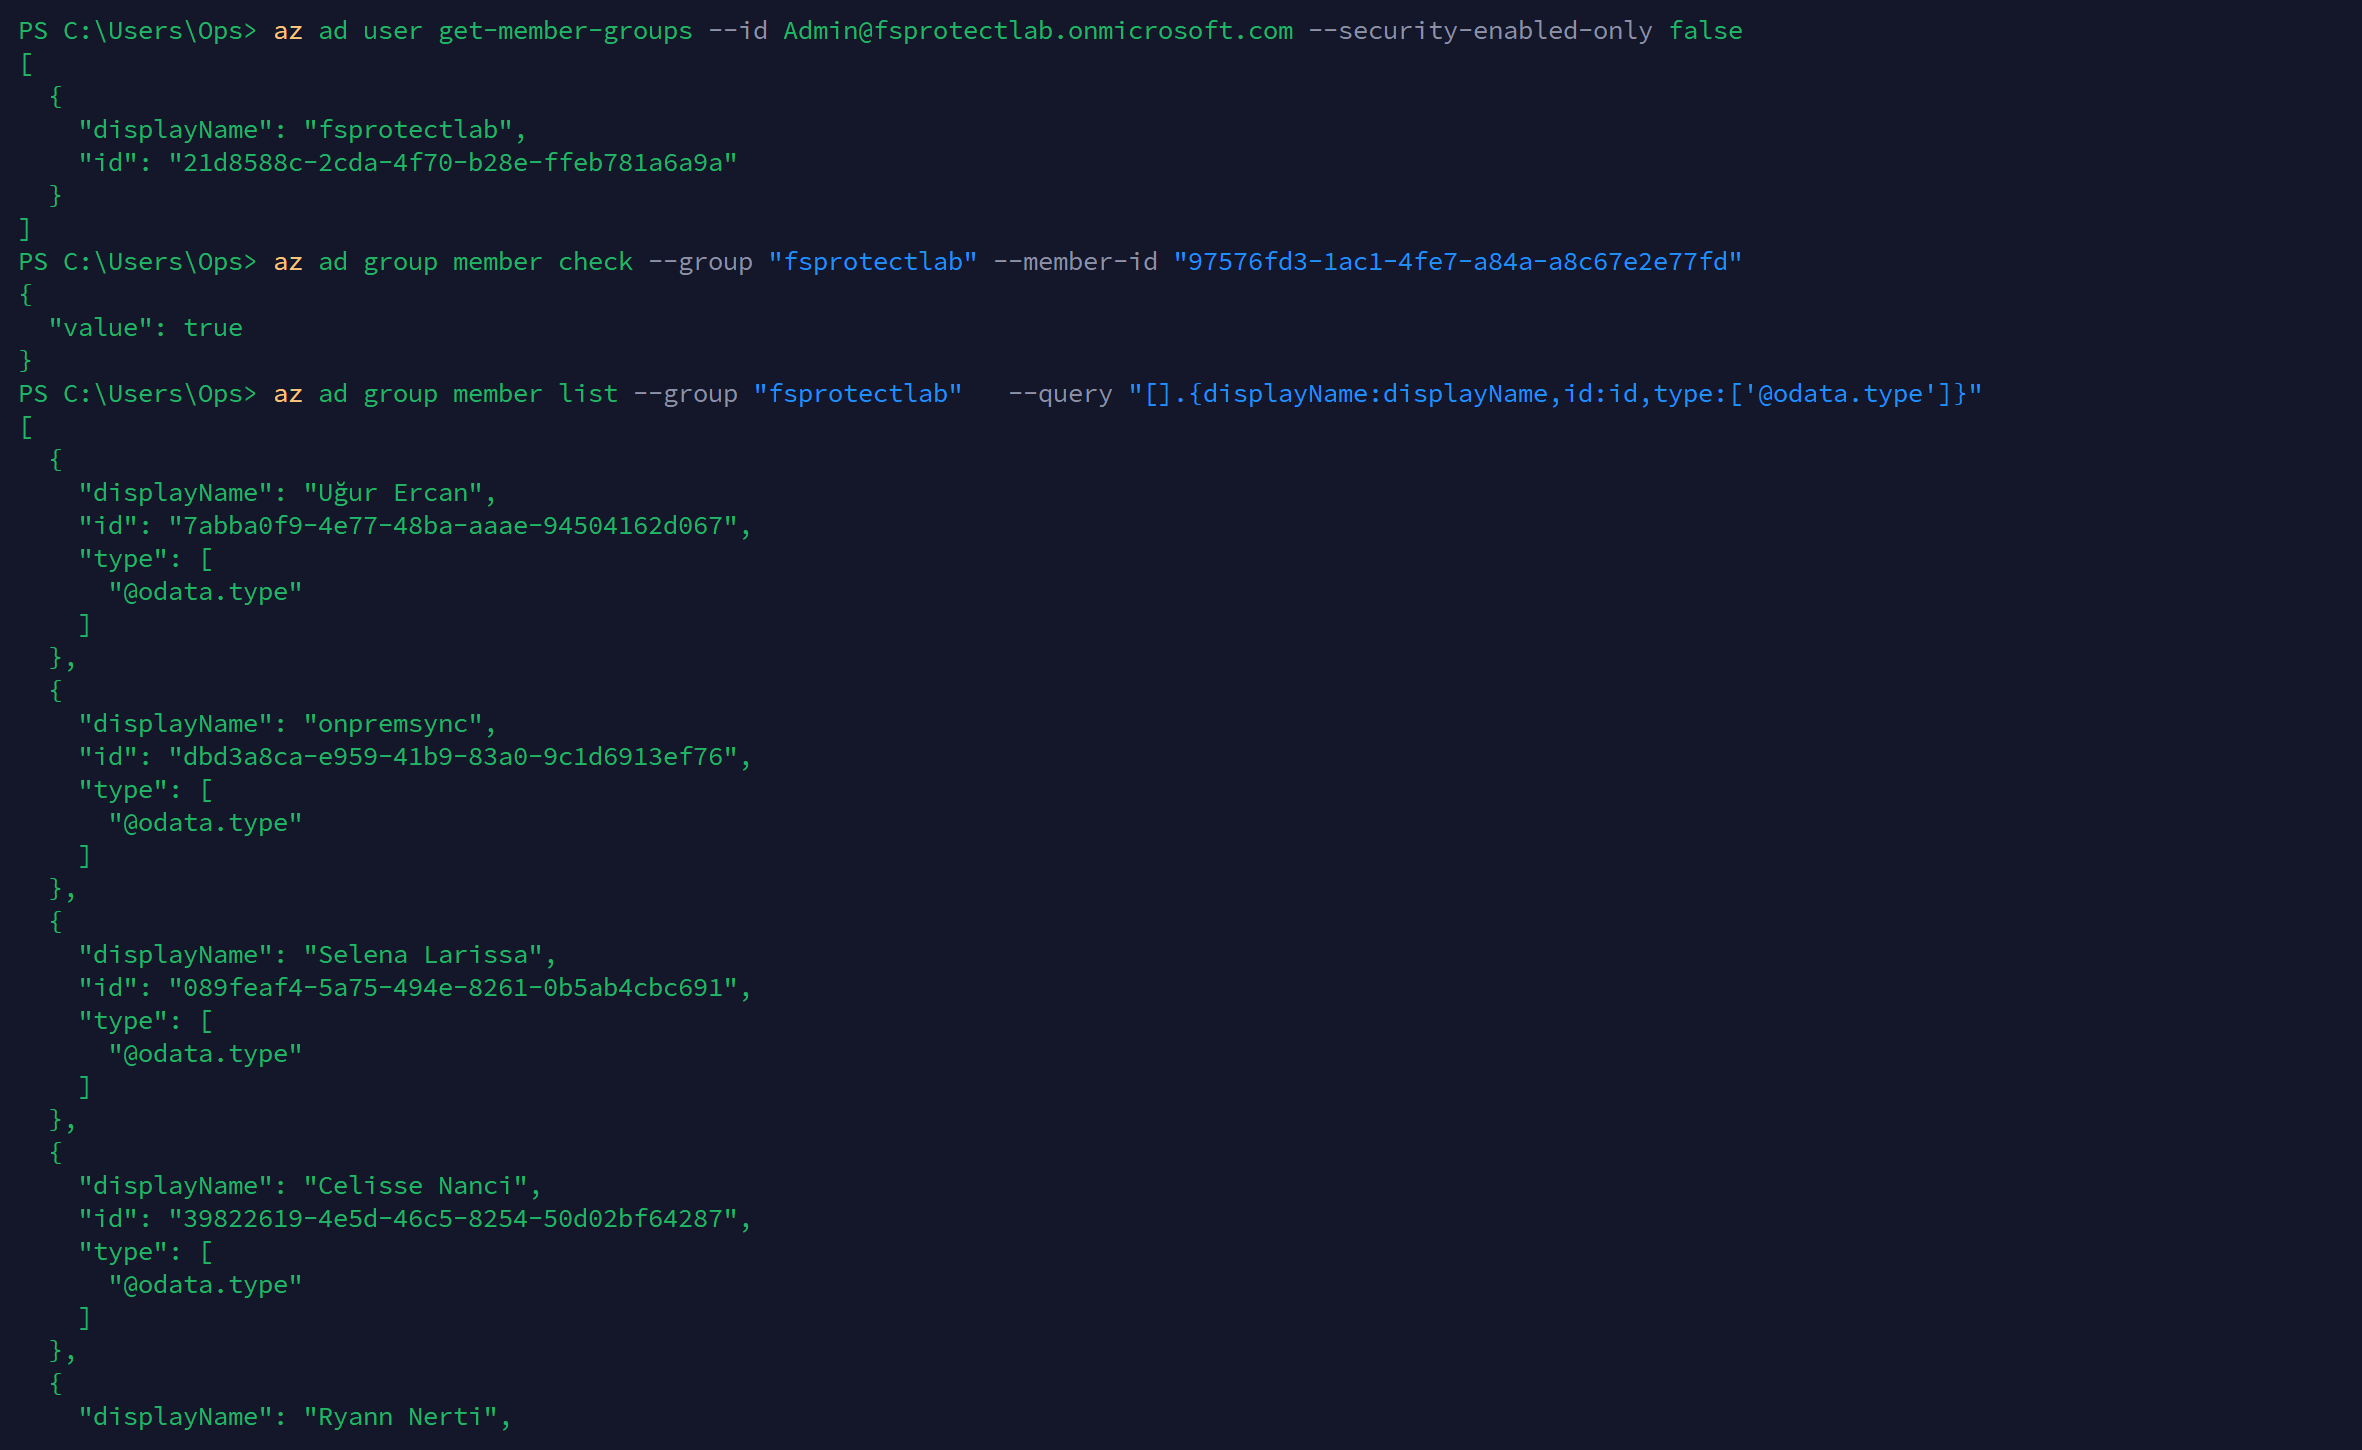
Enumerate group membership with Azure CLI
Azure Portal
-
Open Microsoft Entra admin center -> Users -> select the target user.
-
Go to Groups in the left menu to see all group memberships.
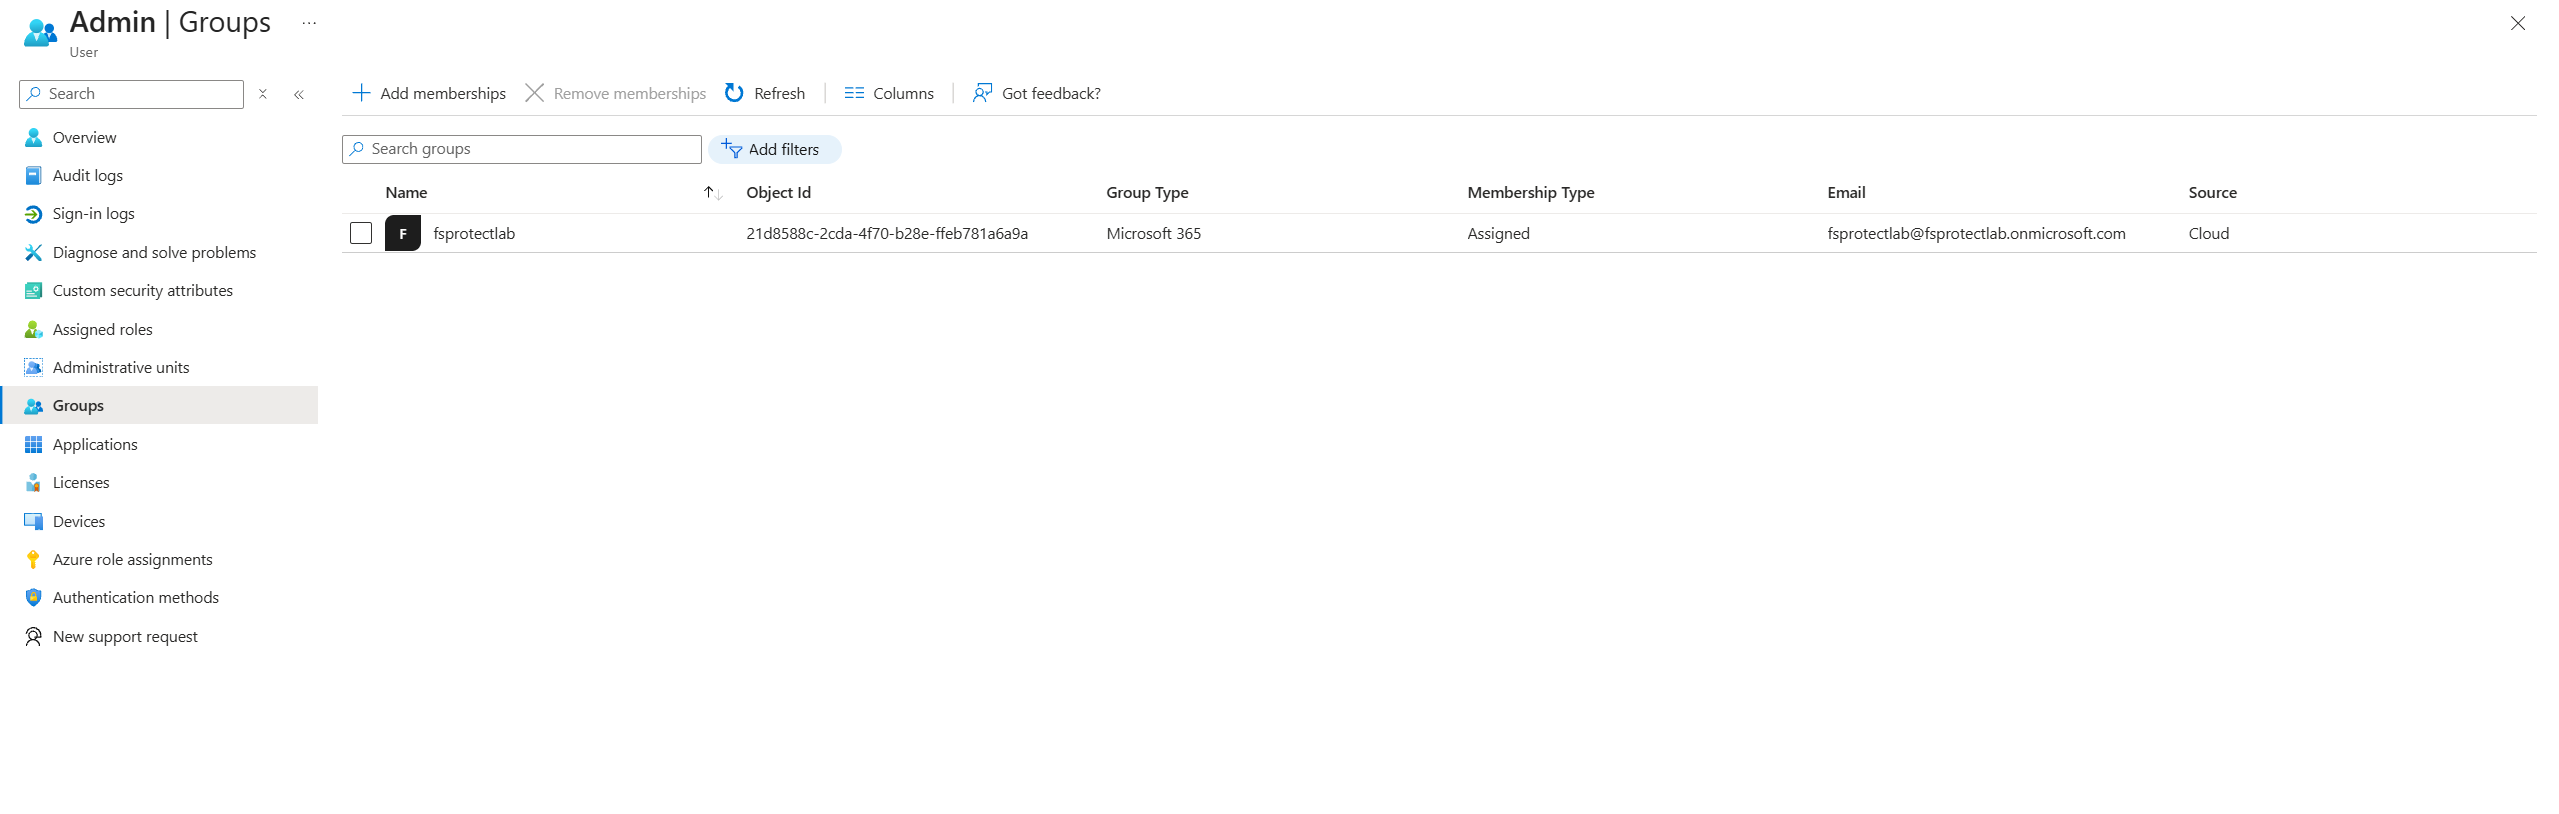
User group memberships in the Entra admin center
-
Alternatively, go to Groups -> select a target group -> Members to see all members.
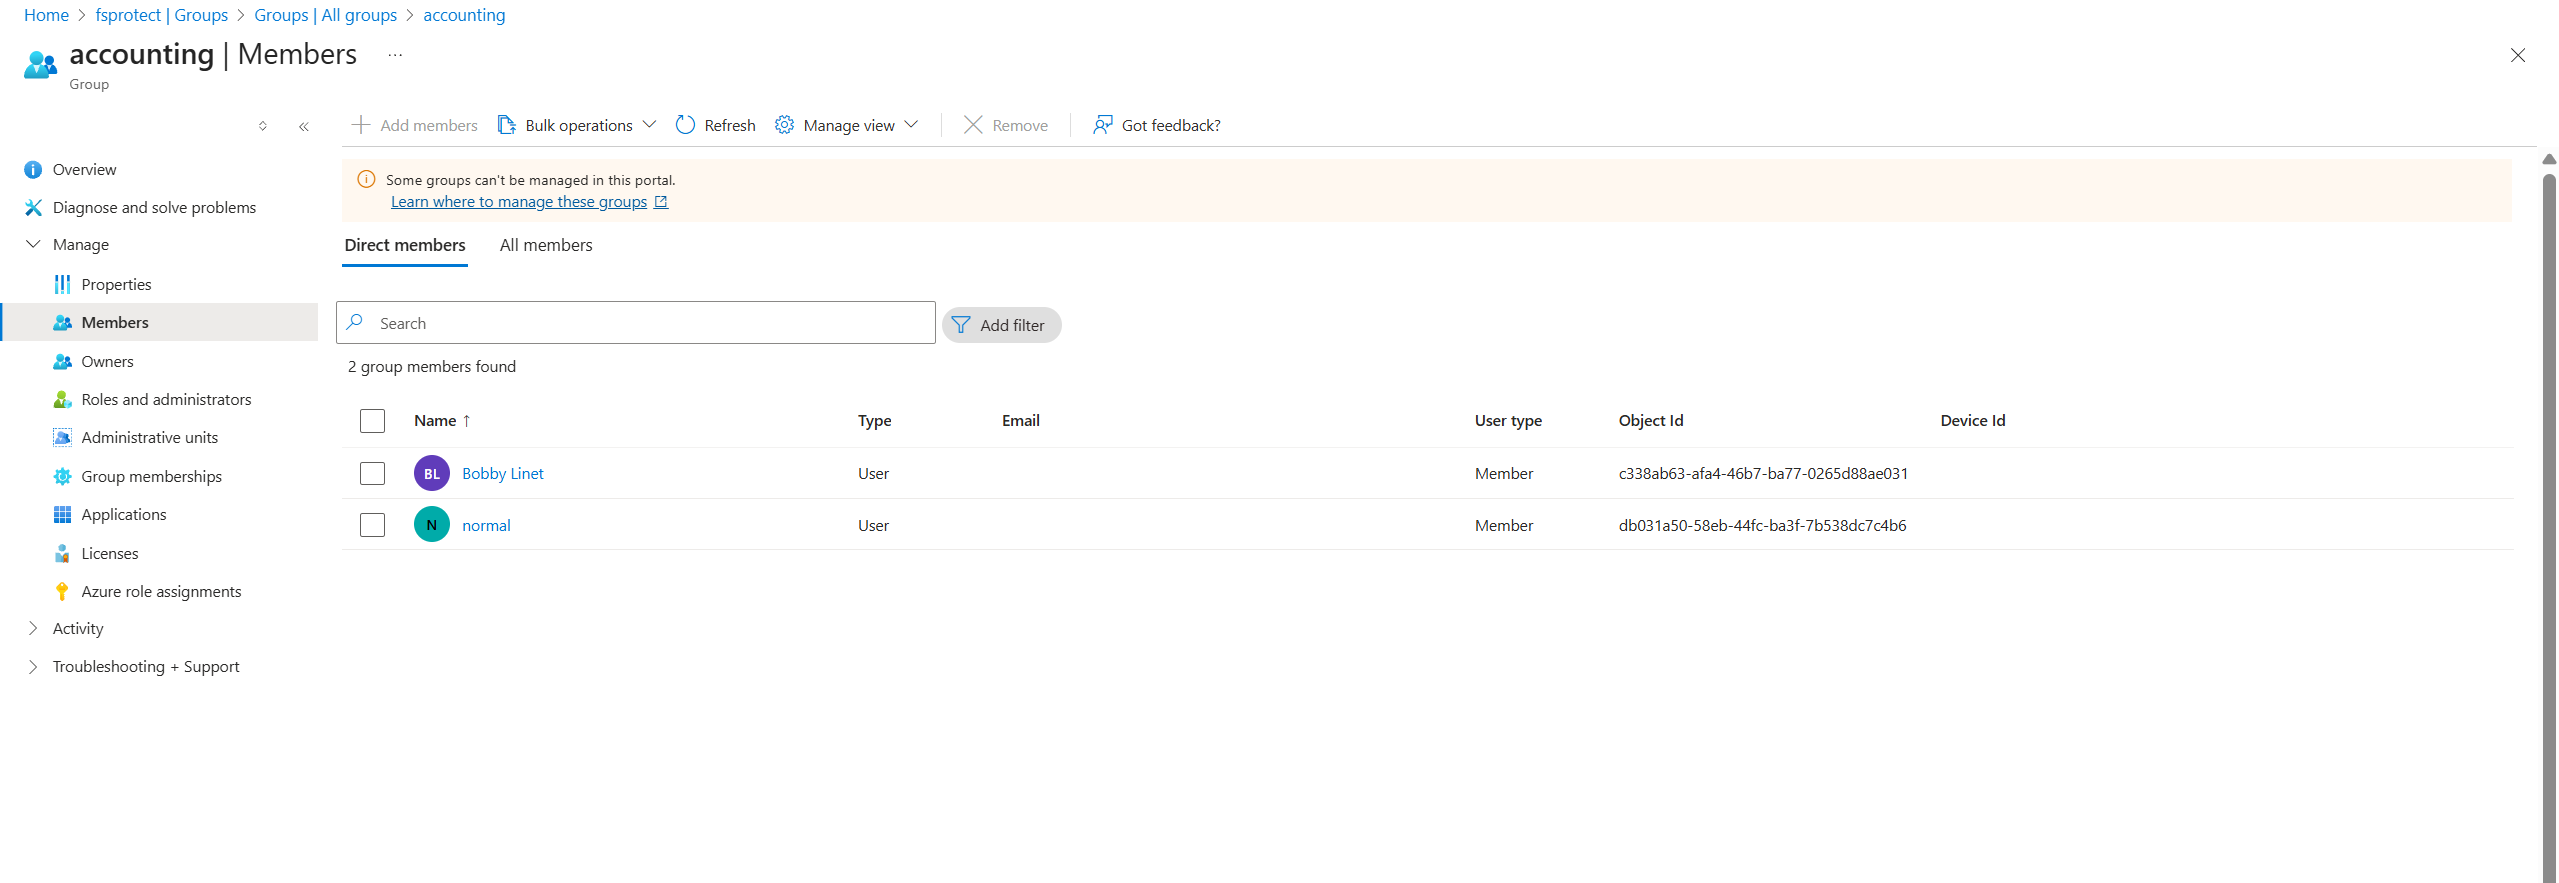
Group members in the Entra admin center
Exploitation
There is no direct exploit path for this edge. AZ_IN_GROUP indicates that a principal is a member of a group, representing a relationship rather than an exploitable permission. The privileges inherited through group membership depend on what permissions are assigned to that group (Azure RBAC roles, directory roles, application access, etc.).
Mitigation
No specific mitigation is required for this edge, as it represents a membership relationship. However, organizations should regularly audit group memberships to ensure only authorized principals are members of sensitive groups.
Detection
Use the Microsoft Entra admin center:
- Open Microsoft Entra ID -> Audit logs.
- Click Category: All -> select GroupManagement -> Apply.
- Filter or review Activity for:
- Add member to group
- Remove member from group
- Review Initiated by (actor), Target, Date, and Status for unexpected group membership changes.
- Open the affected group and review the Members blade.
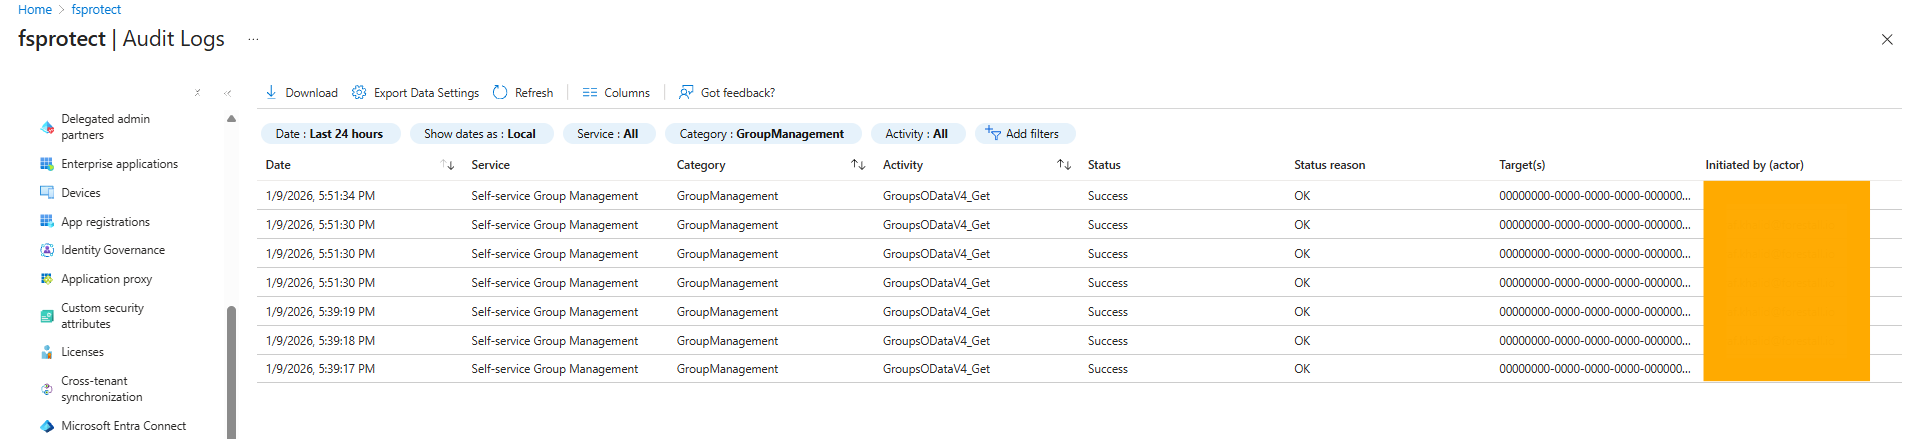
Group management audit logs in Entra ID
References
- https://learn.microsoft.com/en-us/entra/fundamentals/how-to-manage-groups
- https://learn.microsoft.com/en-us/powershell/module/az.resources/get-azadgroup
- https://learn.microsoft.com/en-us/powershell/module/az.resources/get-azadgroupmember
- https://learn.microsoft.com/en-us/powershell/module/az.resources/get-azaduser
- https://learn.microsoft.com/en-us/cli/azure/ad/group/member
- https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/groups-concept