
Summary
| Forestall ACL Alias | AZ_OWNER |
| Entra ID (Azure AD) Alias | Owner |
| Affected Object Types | Groups, Applications, Service Principals, Devices |
| Exploitation Certainty | Certain |
| Graph Permission / Role | Object-level owner assignment via Group Owners, Application Owners, or Service Principal Owners |
Description
AZ_OWNER represents the ownership relationship in Microsoft Entra ID (Azure AD) where a principal (user or service principal) has been designated as an Owner of an object. Ownership in Entra ID grants significant privileges depending on the object type:
- Group Owner: Can add/remove members, modify group properties, and manage group settings. For role-assignable groups, this allows privilege escalation by adding members who inherit directory roles.
- Application Owner: Can modify application configurations, add credentials (secrets/certificates), change redirect URIs, and manage API permissions. This can lead to credential theft and unauthorized access.
- Service Principal Owner: Can modify the service principal configuration, add credentials, and change authentication settings. Compromising this can allow impersonation of the application.
- Device Owner: Can manage device properties and settings.
Ownership is a critical control point that attackers target for privilege escalation and persistence.
Identification
PowerShell
Comprehensive Owner Enumeration
Import-Module Microsoft.Graph.GroupsImport-Module Microsoft.Graph.ApplicationsImport-Module Microsoft.Graph.Identity.DirectoryManagement
Connect-MgGraph -Scopes "Group.Read.All", "Application.Read.All", "Device.Read.All"
function Get-AllAzureOwnership {    $allOwnership = [System.Collections.Generic.List[PSCustomObject]]::new()
    # Groups - use ExpandProperty to get owners in single call per group batch    Write-Host "Fetching groups with owners..."    $groups = Get-MgGroup -All -ExpandProperty "owners"    foreach ($g in $groups) {        foreach ($o in $g.Owners) {            $odataType = $o.AdditionalProperties['@odata.type']            $ownerType = if ($odataType) { ($odataType -replace '^#microsoft\.graph\.', '') } else { 'Unknown' }            $allOwnership.Add([PSCustomObject]@{                TargetType  = "Group"                TargetName  = $g.DisplayName                TargetId    = $g.Id                OwnerName   = $o.AdditionalProperties.displayName                OwnerType   = $ownerType                OwnerId     = $o.Id            })        }    }    Write-Host "Found $($groups.Count) groups"
    # Applications - use ExpandProperty to get owners in single call per app batch    Write-Host "Fetching applications with owners..."    $apps = Get-MgApplication -All -ExpandProperty "owners"    foreach ($a in $apps) {        foreach ($o in $a.Owners) {            $odataType = $o.AdditionalProperties['@odata.type']            $ownerType = if ($odataType) { ($odataType -replace '^#microsoft\.graph\.', '') } else { 'Unknown' }            $allOwnership.Add([PSCustomObject]@{                TargetType  = "Application"                TargetName  = $a.DisplayName                TargetId    = $a.Id                OwnerName   = $o.AdditionalProperties.displayName                OwnerType   = $ownerType                OwnerId     = $o.Id            })        }    }    Write-Host "Found $($apps.Count) applications"
    # Service Principals - use ExpandProperty to get owners in single call per SP batch    Write-Host "Fetching service principals with owners..."    $sps = Get-MgServicePrincipal -All -ExpandProperty "owners"    foreach ($s in $sps) {        foreach ($o in $s.Owners) {            $odataType = $o.AdditionalProperties['@odata.type']            $ownerType = if ($odataType) { ($odataType -replace '^#microsoft\.graph\.', '') } else { 'Unknown' }            $allOwnership.Add([PSCustomObject]@{                TargetType  = "ServicePrincipal"                TargetName  = $s.DisplayName                TargetId    = $s.Id                OwnerName   = $o.AdditionalProperties.displayName                OwnerType   = $ownerType                OwnerId     = $o.Id            })        }    }    Write-Host "Found $($sps.Count) service principals"
    # Devices - use ExpandProperty for registered owners    Write-Host "Fetching devices with owners..."    $devices = Get-MgDevice -All -ExpandProperty "registeredOwners"    foreach ($d in $devices) {        foreach ($o in $d.RegisteredOwners) {            $odataType = $o.AdditionalProperties['@odata.type']            $ownerType = if ($odataType) { ($odataType -replace '^#microsoft\.graph\.', '') } else { 'Unknown' }            $allOwnership.Add([PSCustomObject]@{                TargetType  = "Device"                TargetName  = $d.DisplayName                TargetId    = $d.Id                OwnerName   = $o.AdditionalProperties.displayName                OwnerType   = $ownerType                OwnerId     = $o.Id            })        }    }    Write-Host "Found $($devices.Count) devices"
    $allOwnership}
$ownership = Get-AllAzureOwnership$ownership | Export-Csv -Path ".\AllAzureOwnership.csv" -NoTypeInformation -Encoding UTF8Write-Host "Total ownership relationships: $($ownership.Count)"$ownership | Sort-Object TargetType, TargetName | Format-Table -AutoSize
Azure CLI
# List owners of a groupaz ad group owner list --group "<GroupObjectIdOrName>" --query "[].{displayName:displayName,id:id}"
# List owners of an applicationaz ad app owner list --id "<AppObjectIdOrAppId>" --query "[].{displayName:displayName,id:id}"
# List owners of a service principalaz ad sp owner list --id "<SPObjectIdOrAppId>" --query "[].{displayName:displayName,id:id}"
# List registered owners of a device (using Graph API)az rest --method GET --url "https://graph.microsoft.com/v1.0/devices/<DeviceObjectId>/registeredOwners" --query "value[].{displayName:displayName,id:id}"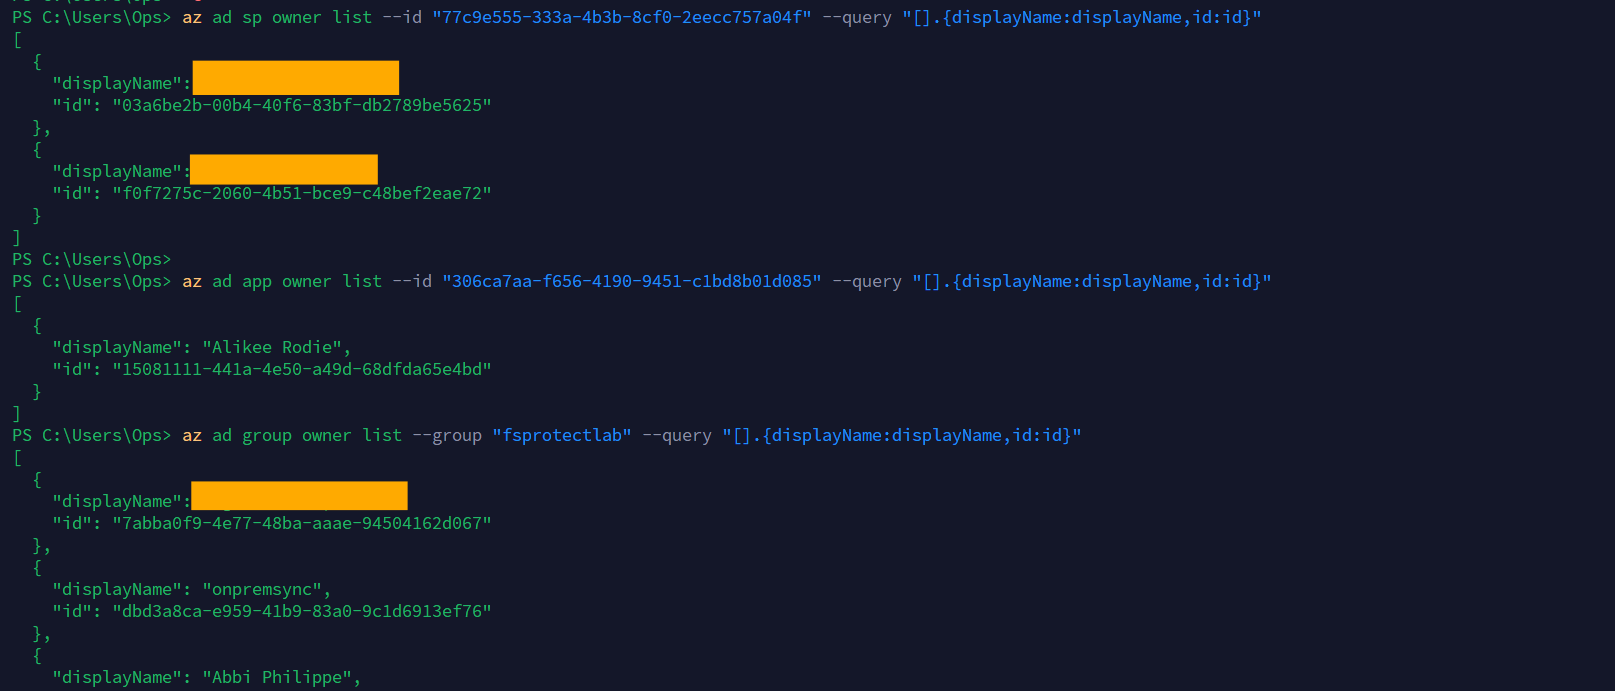
List Azure resource owners with Azure CLI
Azure Portal
Group Owners
-
Open Microsoft Entra admin center -> Groups -> select the target group.
-
Go to Owners in the left menu.
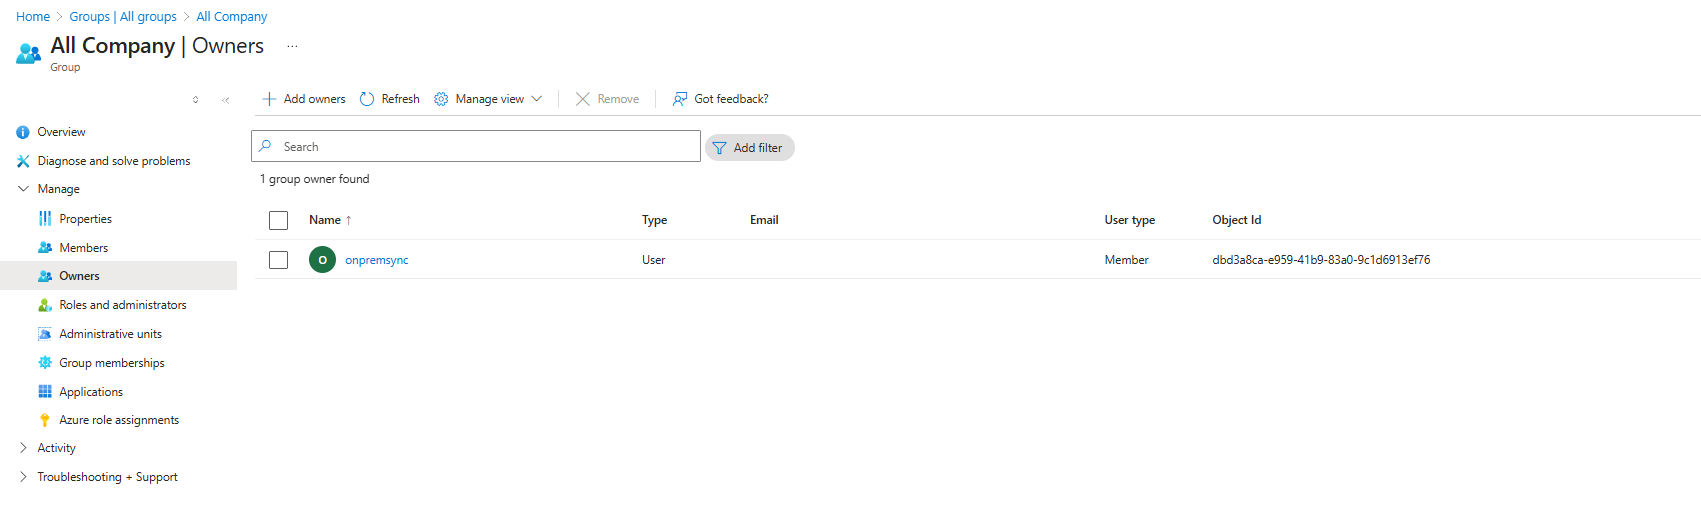
Group owners in the Entra admin center
Application Owners
-
Open Microsoft Entra admin center -> Applications -> App registrations -> select the target app.
-
Go to Owners in the left menu.
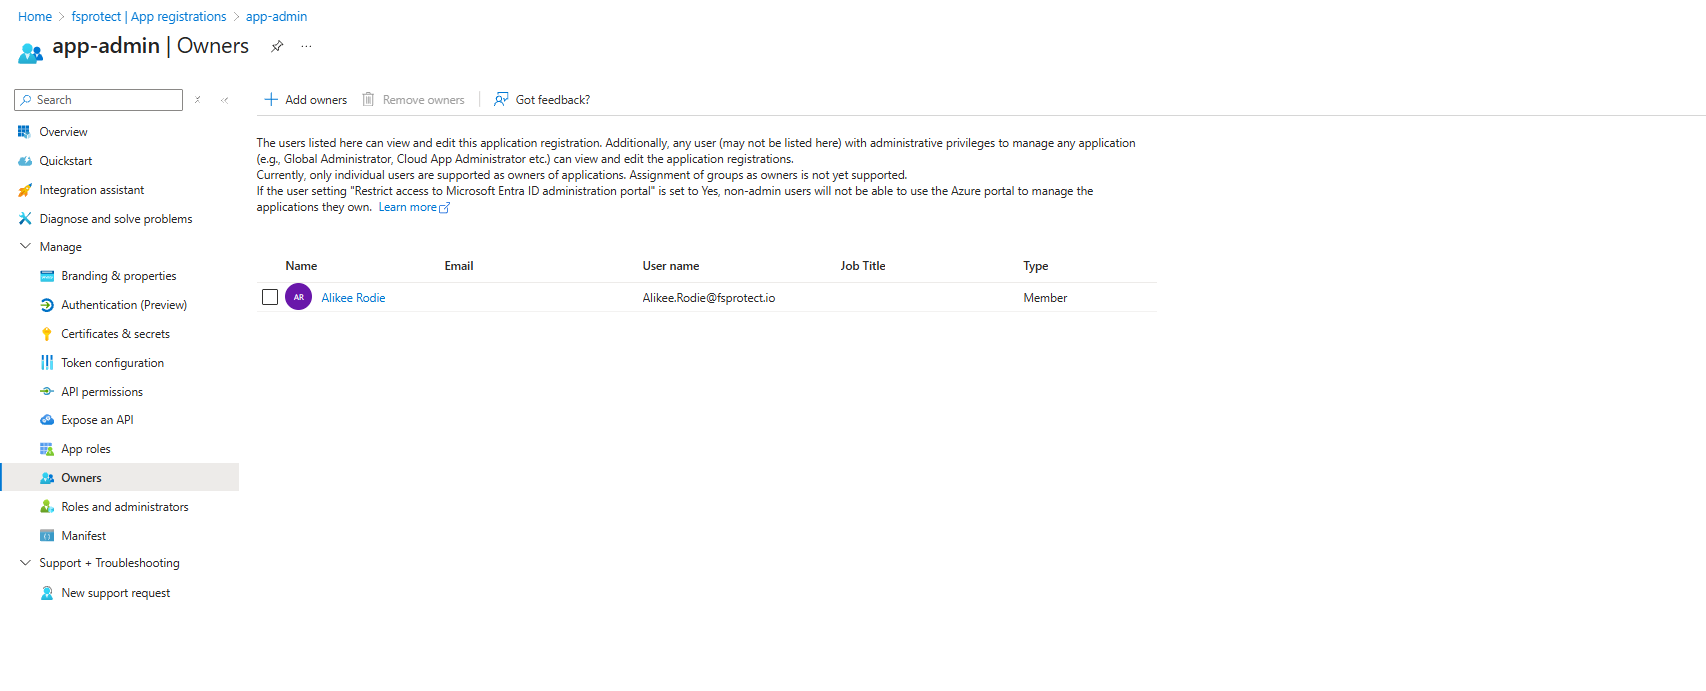
Application owners in the Entra admin center
Service Principal Owners
-
Open Microsoft Entra admin center -> Applications -> Enterprise applications -> select the target app.
-
Go to Owners in the left menu.
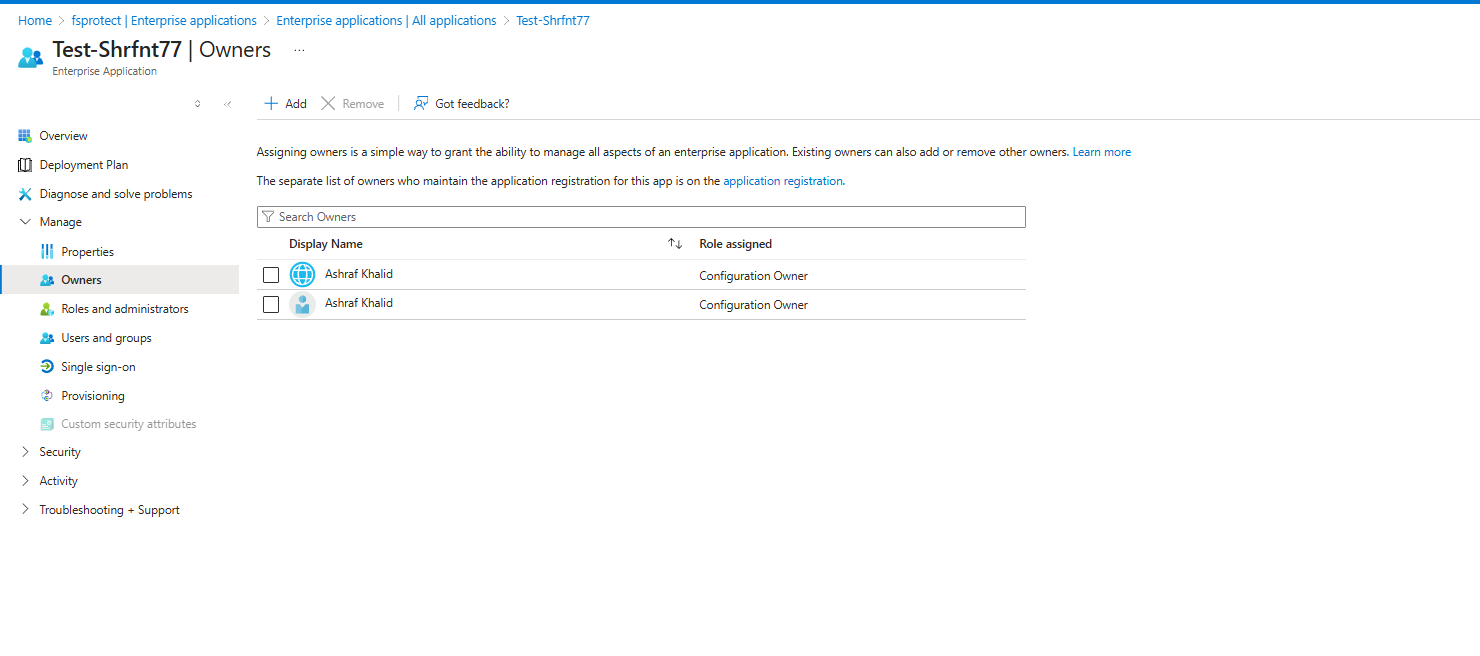
Service principal owners in the Entra admin center
Device Owners
- Open Microsoft Entra admin center -> Devices -> All devices -> select the target device.
- Go to Registered owners in the device details.
Exploitation
Related Attack Paths:
- AZ_ADD_OWNER - Grants the ability to add owners to objects, which can then be exploited via this edge.
- AZ_ADD_SECRET - Application/SP owners can add secrets to impersonate the application.
- AZ_ADD_MEMBERS - Group owners can add members to groups.
- AZ_MG_APPLICATION_READWRITE_ALL - Applications with this permission can modify any app, similar to ownership.
- AZ_MG_APPROLEASSIGNMENT_READWRITE_ALL - After compromising an app via ownership, grant it dangerous permissions.
- AZ_MG_ROLEMANAGEMENT_READWRITE_DIRECTORY - Escalate to Global Admin after gaining control of an application.
Ownership exploitation depends on the object type:
| Owner Type | Exploitation Method | See Edge |
|---|---|---|
| Group Owner | Add members to gain group privileges | AZ_ADD_MEMBERS |
| Application Owner | Add credentials to impersonate app | AZ_ADD_SECRET |
| Service Principal Owner | Add credentials to impersonate SP | AZ_ADD_SECRET |
| Device Owner | Limited - modify properties, disable device | N/A |
Mitigation
-
Minimize the number of owners for sensitive objects (groups, applications, service principals).
- Go to Microsoft Entra ID -> Groups / App registrations / Enterprise applications.
- Select the object -> Owners -> remove unnecessary owners.
-
Use Privileged Identity Management (PIM) for just-in-time owner access to sensitive objects.
-
Monitor owner assignments and alert on unexpected changes.
-
Avoid assigning ownership to regular users for applications that have sensitive permissions.
-
Implement Access Reviews for application and group owners:
- Go to Identity Governance -> Access Reviews -> New access review.
- Select the target and configure owner reviews.
Detection
Use the Microsoft Entra admin center:
- Open Microsoft Entra ID -> Audit logs.
- Filter Activity for:
- Add owner to group
- Remove owner from group
- Add owner to application
- Remove owner from application
- Add owner to service principal
- Remove owner from service principal
- Review Initiated by (actor), Target, Date, and Status for unexpected ownership changes.
- Open the affected group, application, or service principal and review the Owners blade.
- Use Manage view -> Edit columns if any of those fields are hidden.
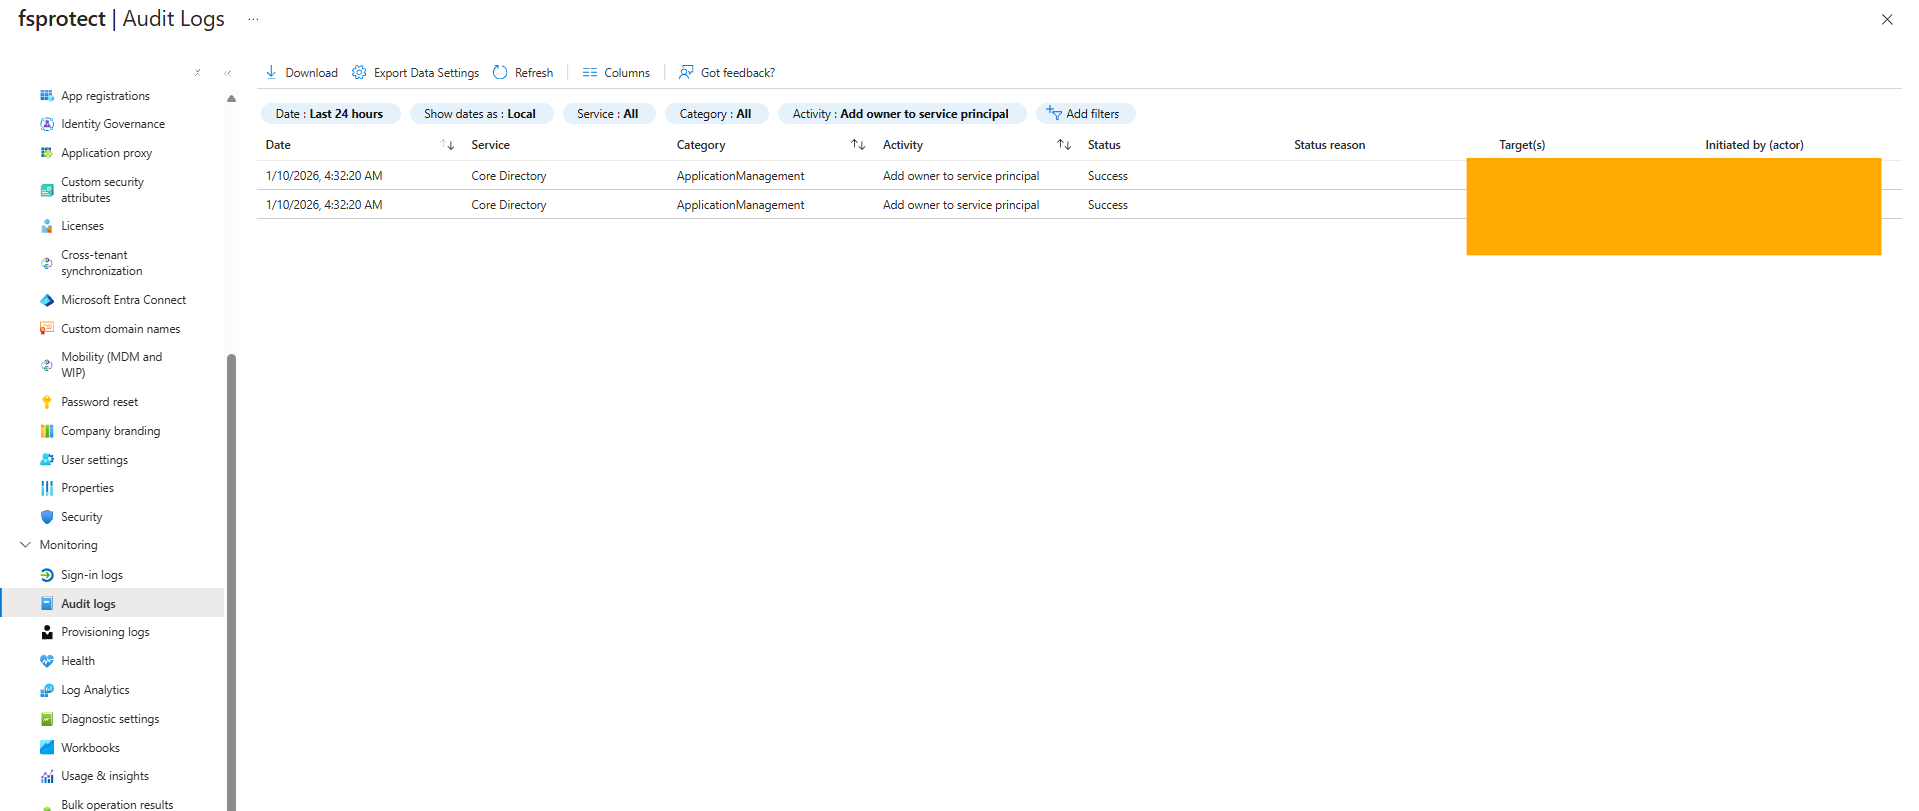
Owner changes in Entra audit logs
References
- https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/groups-concept
- https://learn.microsoft.com/en-us/powershell/module/az.resources/get-azadgroupowner
- https://learn.microsoft.com/en-us/powershell/module/az.resources/get-azadapplication
- https://learn.microsoft.com/en-us/powershell/module/az.resources/get-azadserviceprincipal
- https://learn.microsoft.com/en-us/powershell/module/az.resources/new-azadappcredential
- https://learn.microsoft.com/en-us/powershell/module/az.resources/add-azadgroupmember
- https://learn.microsoft.com/en-us/cli/azure/ad/group/owner
- https://learn.microsoft.com/en-us/cli/azure/ad/app/owner