> For the complete documentation index, see [llms.txt](https://docs.forestall.io/fsprotect/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.forestall.io/fsprotect/issues.md).

# Issues

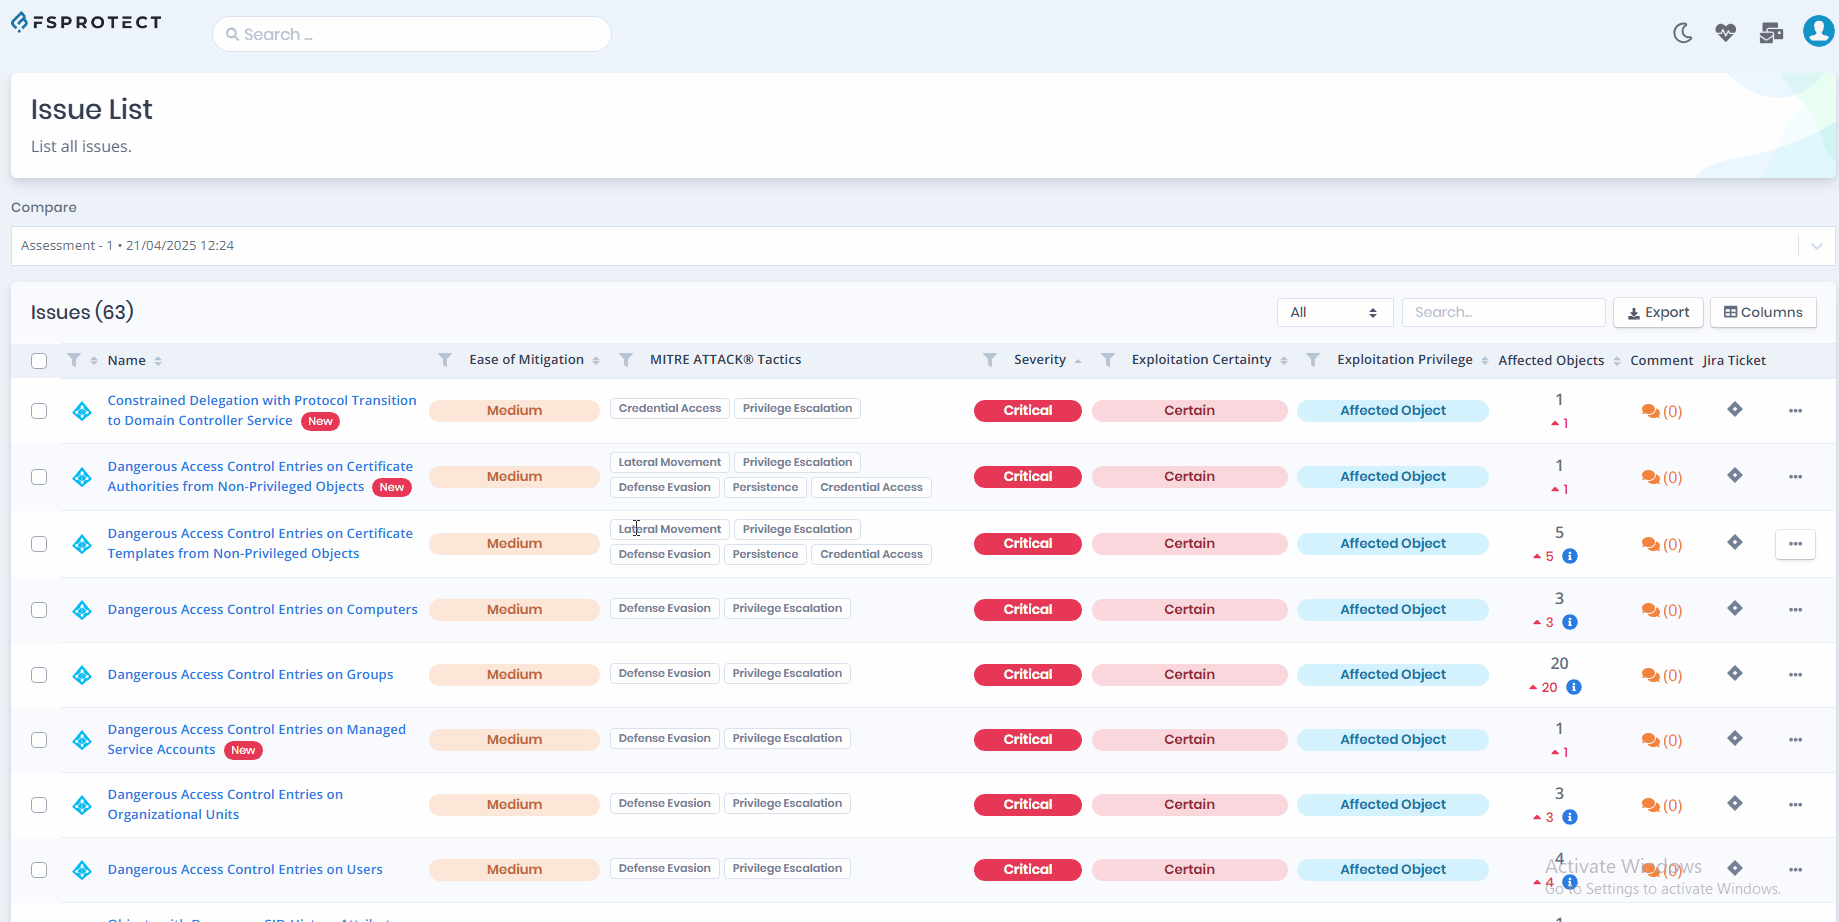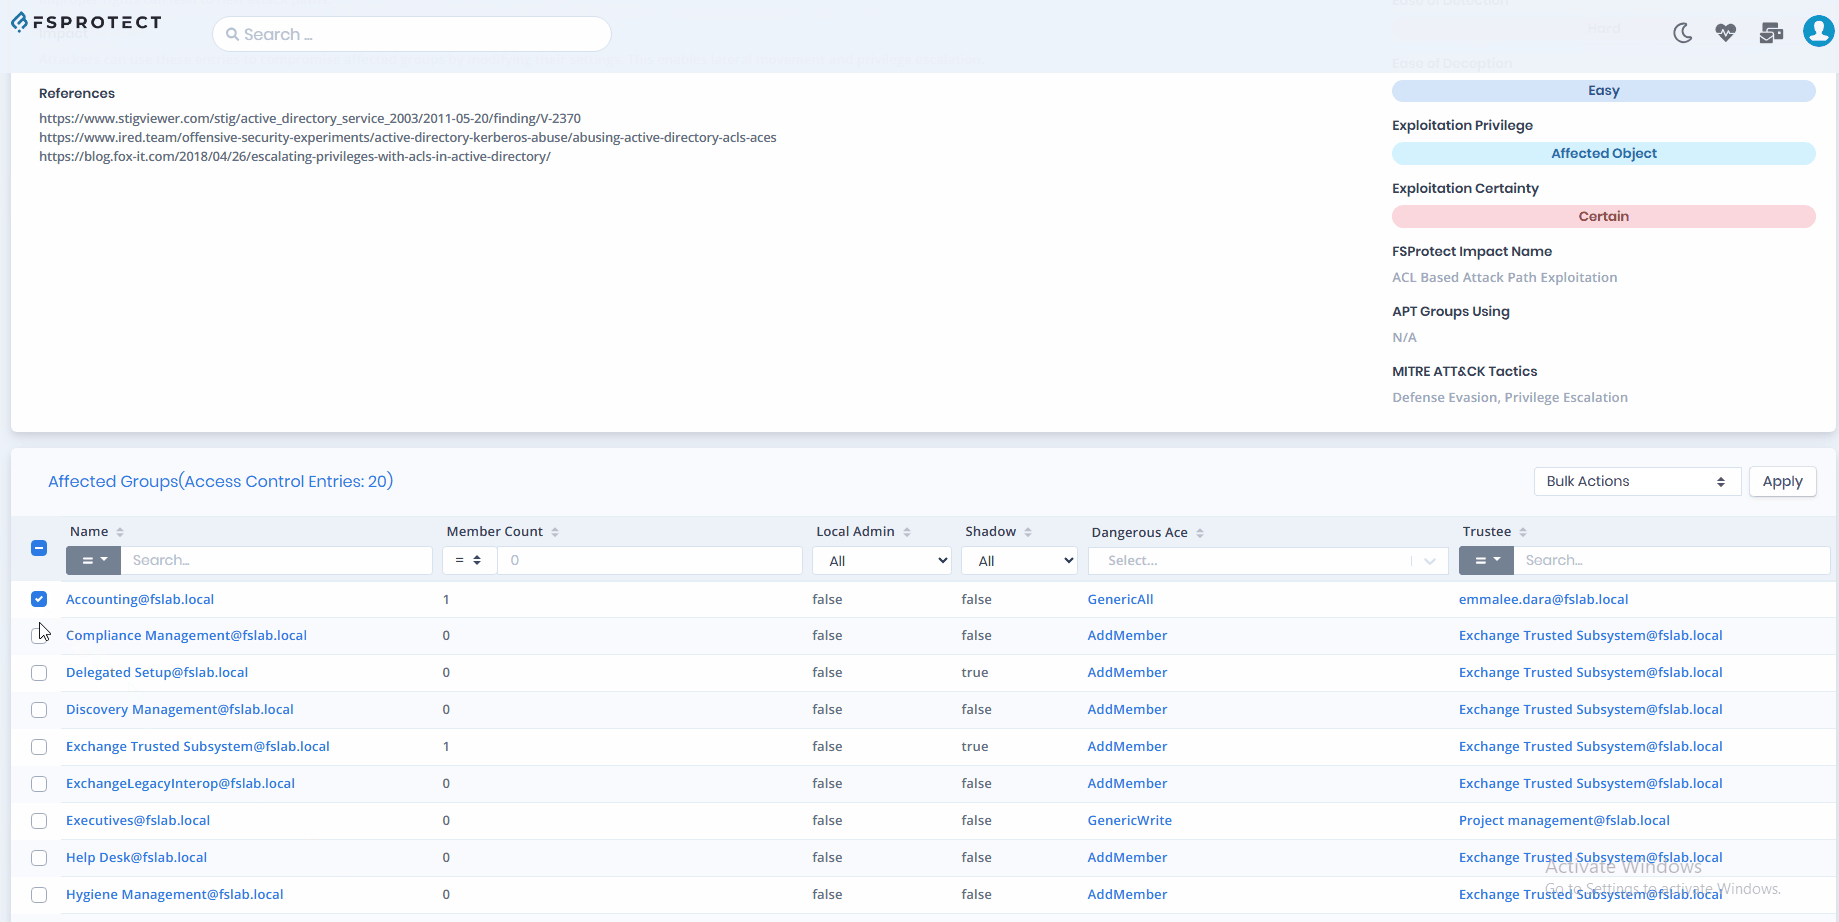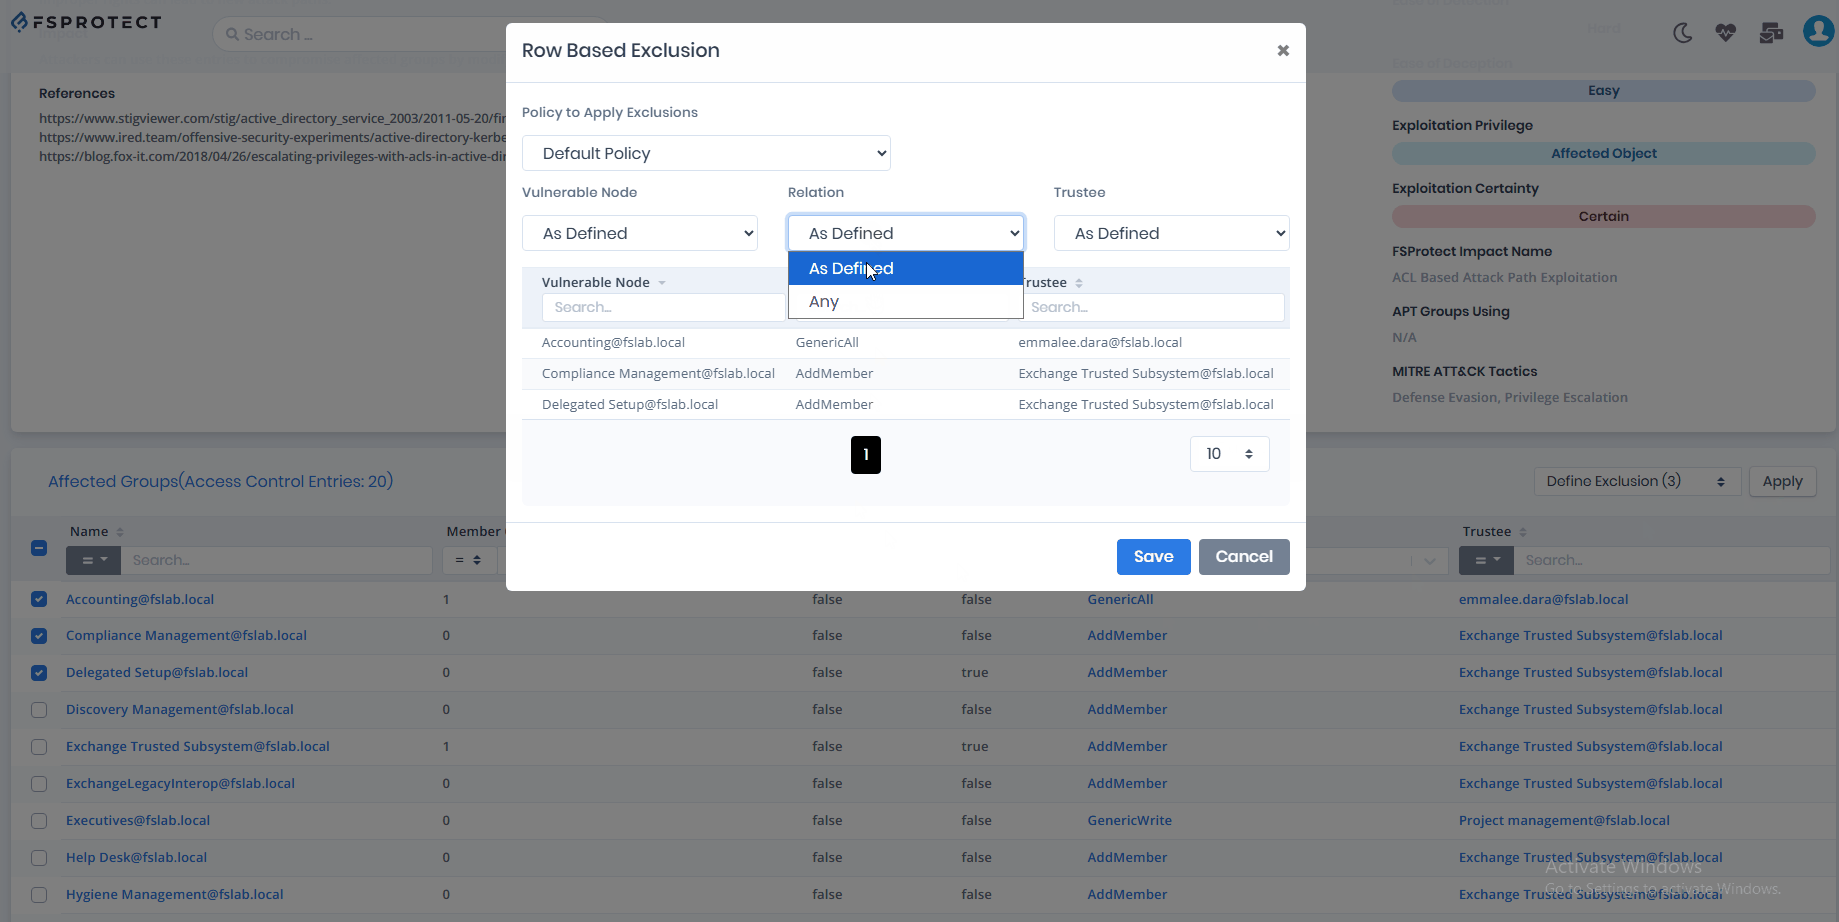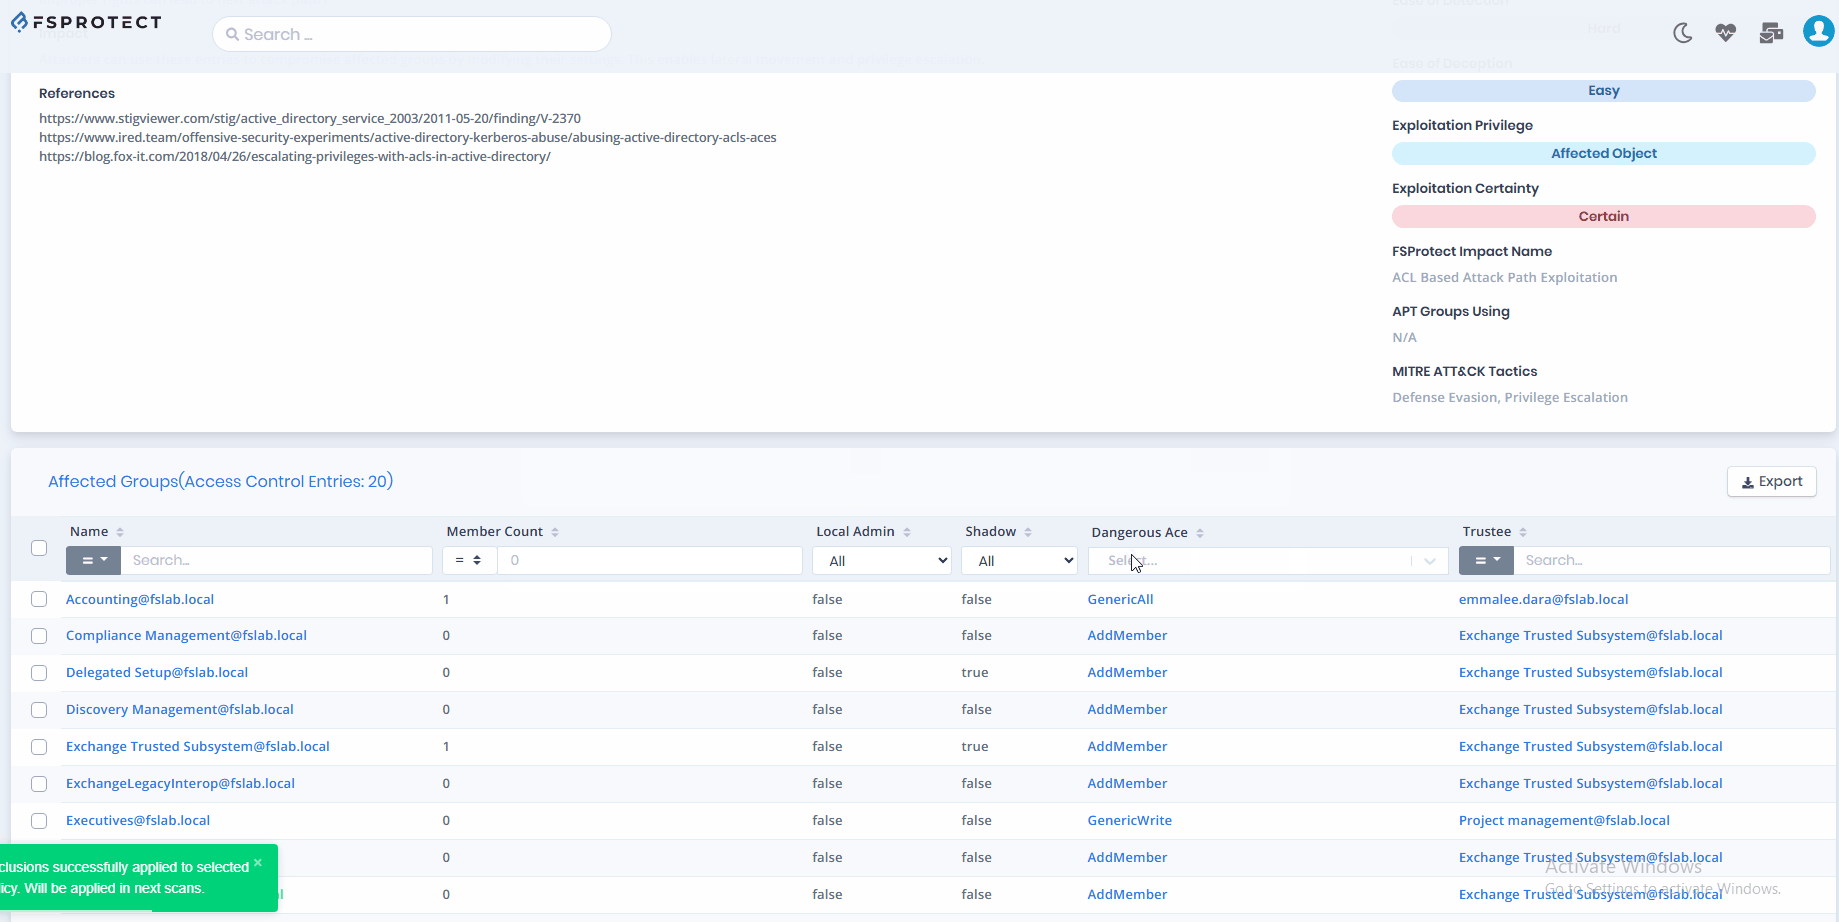
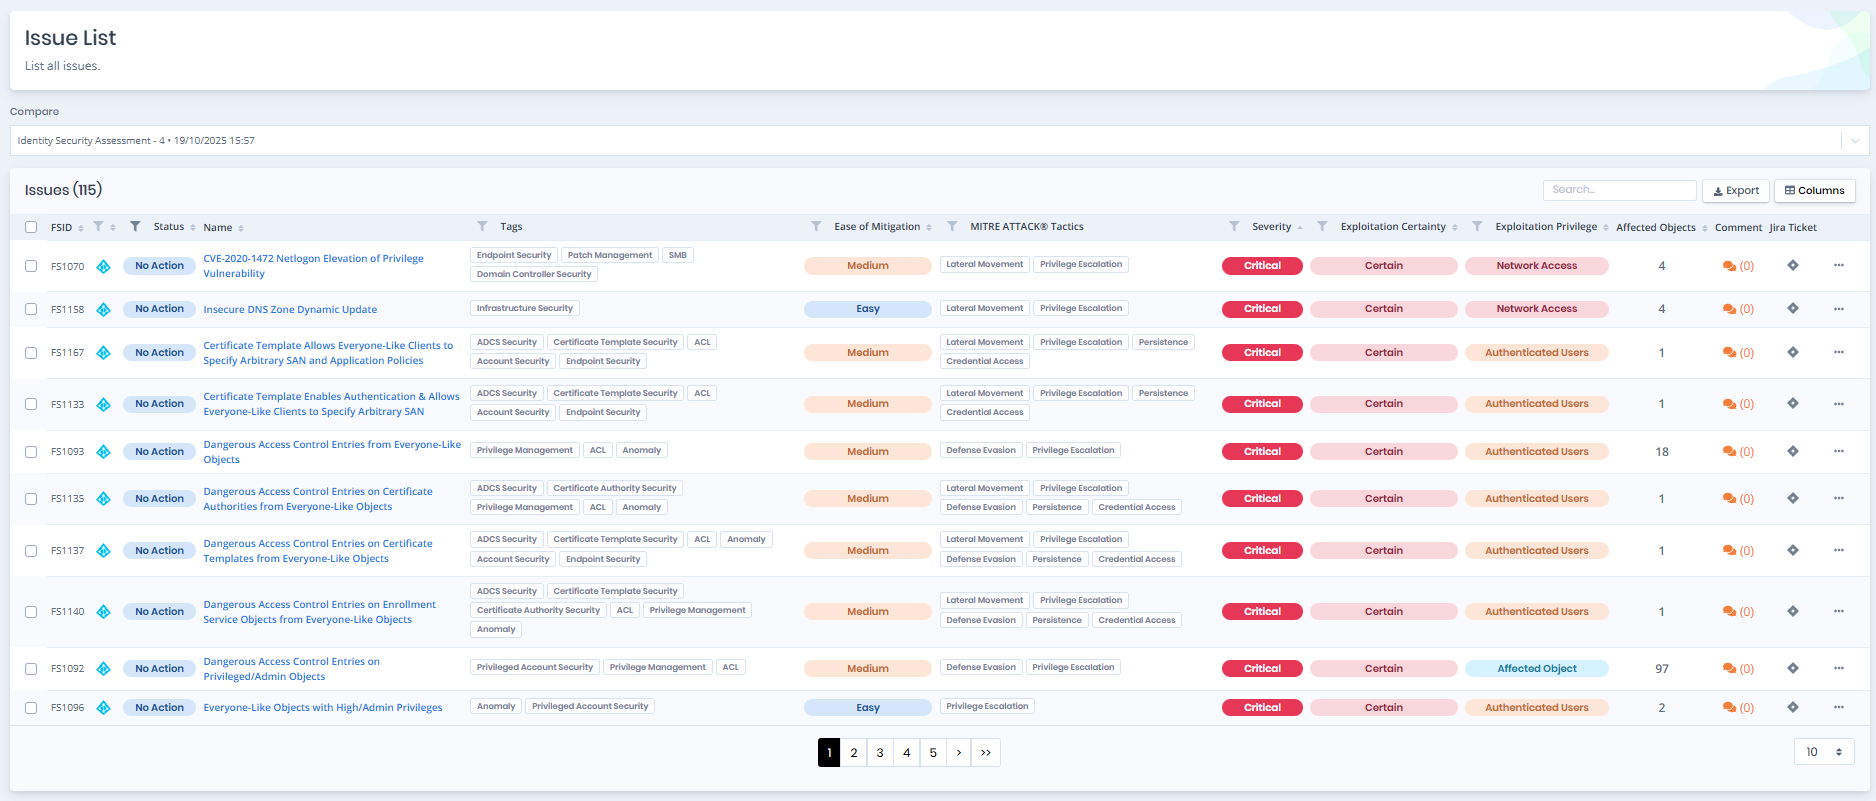
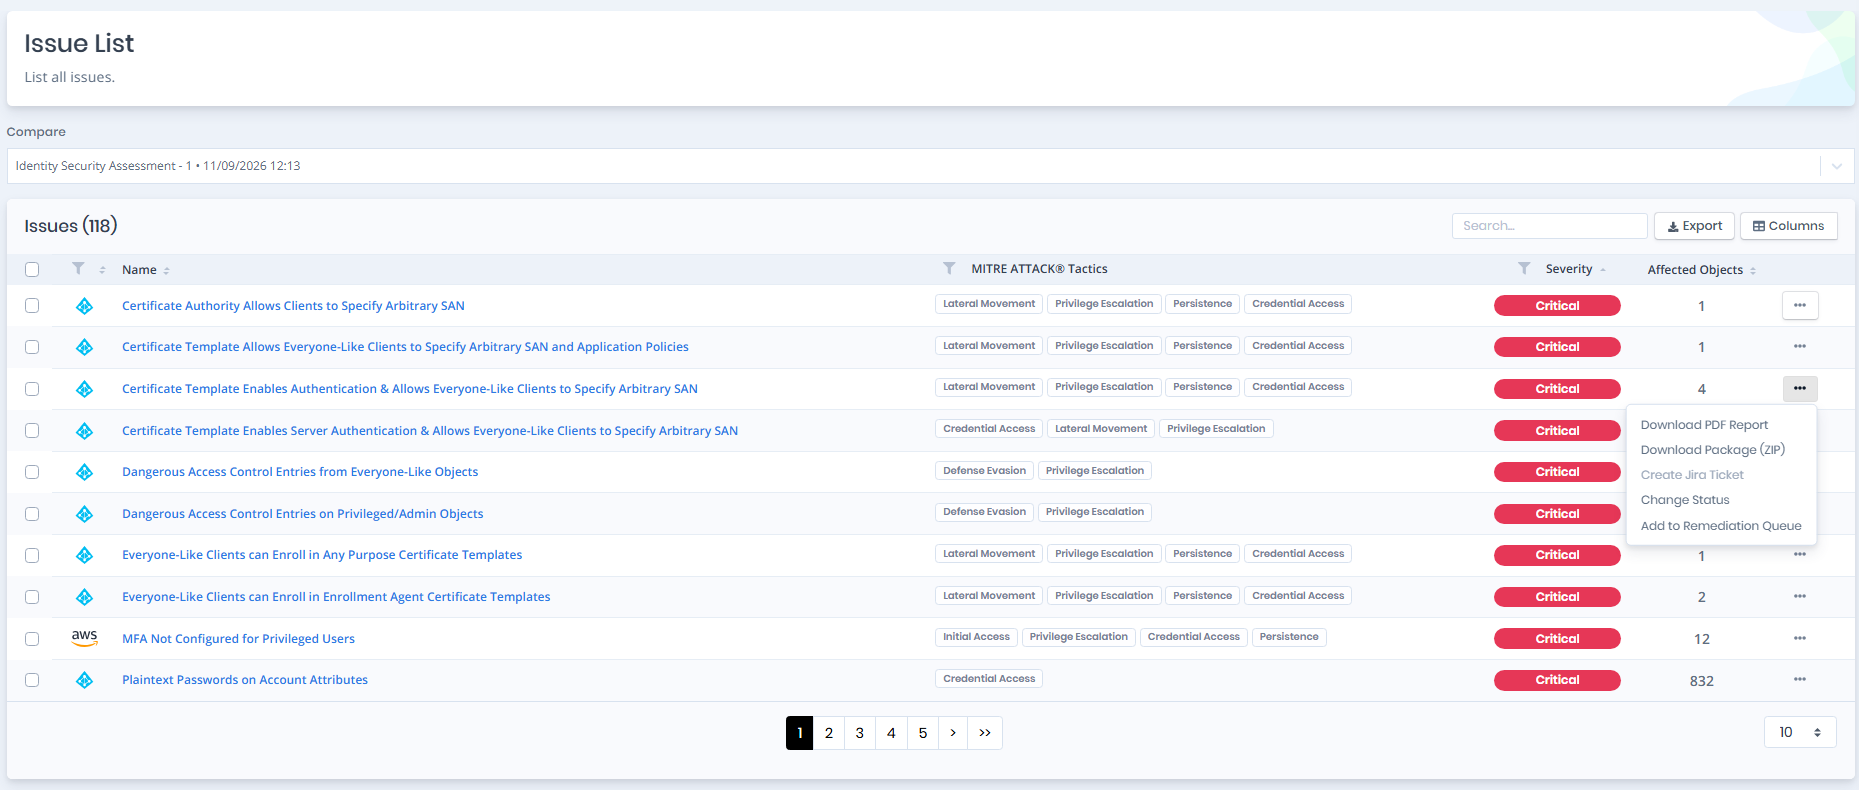
Issues page provides a list of identified issues in the selected scan, sorted by severity.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-a81284a88e428299f7933c625785d491f90ff405%2Fissues-image-1.png?alt=media" alt=""><figcaption><p>Issues</p></figcaption></figure>

Two selectors sit above the table. **Remediation** picks a remediation scan to view the re-verified results of, and is empty until a remediation scan has been run. **Compare** picks another scan to compare the current one against, so issues that were introduced or resolved between two scans can be identified.

The issues table provides the following functionalities.

**Sort**: Issues can be sorted by `Status`, `Name`, `Ease of Mitigation`, `Severity`, `Exploitation Certainty`, `Exploitation Privilege`, and `Affected Objects` columns.

**Search**: Issues can be searched and filtered by `Name` column using the `Search input` on the upper-right side.

**Export**: Issues can be exported as CSV using the `Export button` on the upper-right side.

**Limit and Pagination**: Issue table limit can be defined with input on the bottom-right side. Result pages can be navigated through a widget at the bottom.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-d2d9461cc01a99214010cc7ee42b6acfe01eaf0f%2Fissues-image-2.png?alt=media" alt=""><figcaption></figcaption></figure>

**Download PDF Report**: Issues can be exported as PDF separately using the `Download PDF Report` button on the right side of each row.

**Download Package (ZIP)**: Exports a self-contained archive containing the finding report together with the evidence for every affected entity. The action requires the `DownloadReportPackage` permission and the offline report package to be enabled in [Report Settings](/fsprotect/settings/report.md).

**Create Jira Ticket**: Issues can be imported to Jira as separate tickets using the `Create Jira Ticket` button on the right side of each row. But first, you need to integrate FSProtect with cloud or on-prem Jira instance through API. You can visit [`Integration > Jira`](/fsprotect/configuration-center/jira.md) to learn how to integrate FSProtect with Jira.

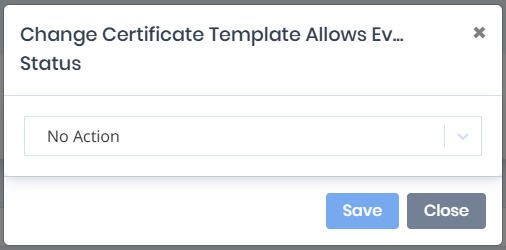
**Change Status:** The actions taken regarding the vulnerabilities found are changed in this section. Actions that can be taken: `No Action`, `In Progress`, `Done` and `Accepted Risk`. Column is turned off by default. Status filter shows vulnerabilities with no action and in progress selected by default. Vulnerabilities selected as `Done` or `Accepted Risk` will be hidden on issues table unless filter manually enabled.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-c7696f9cd490639de21273bff646cc306778d77b%2Fissues-image-3.png?alt=media" alt="Change Issue Status"><figcaption><p>Change Issue Status</p></figcaption></figure>

### Remediation Scan

A Remediation Scan allows you to re-verify previously detected issues after remediation actions have been applied. Instead of creating a new scan configuration, the remediation scan uses the access information and scan policy of the original scan and verifies the issues or affected entities added to the **Remediation Queue**.

#### Adding Issues to the Remediation Queue

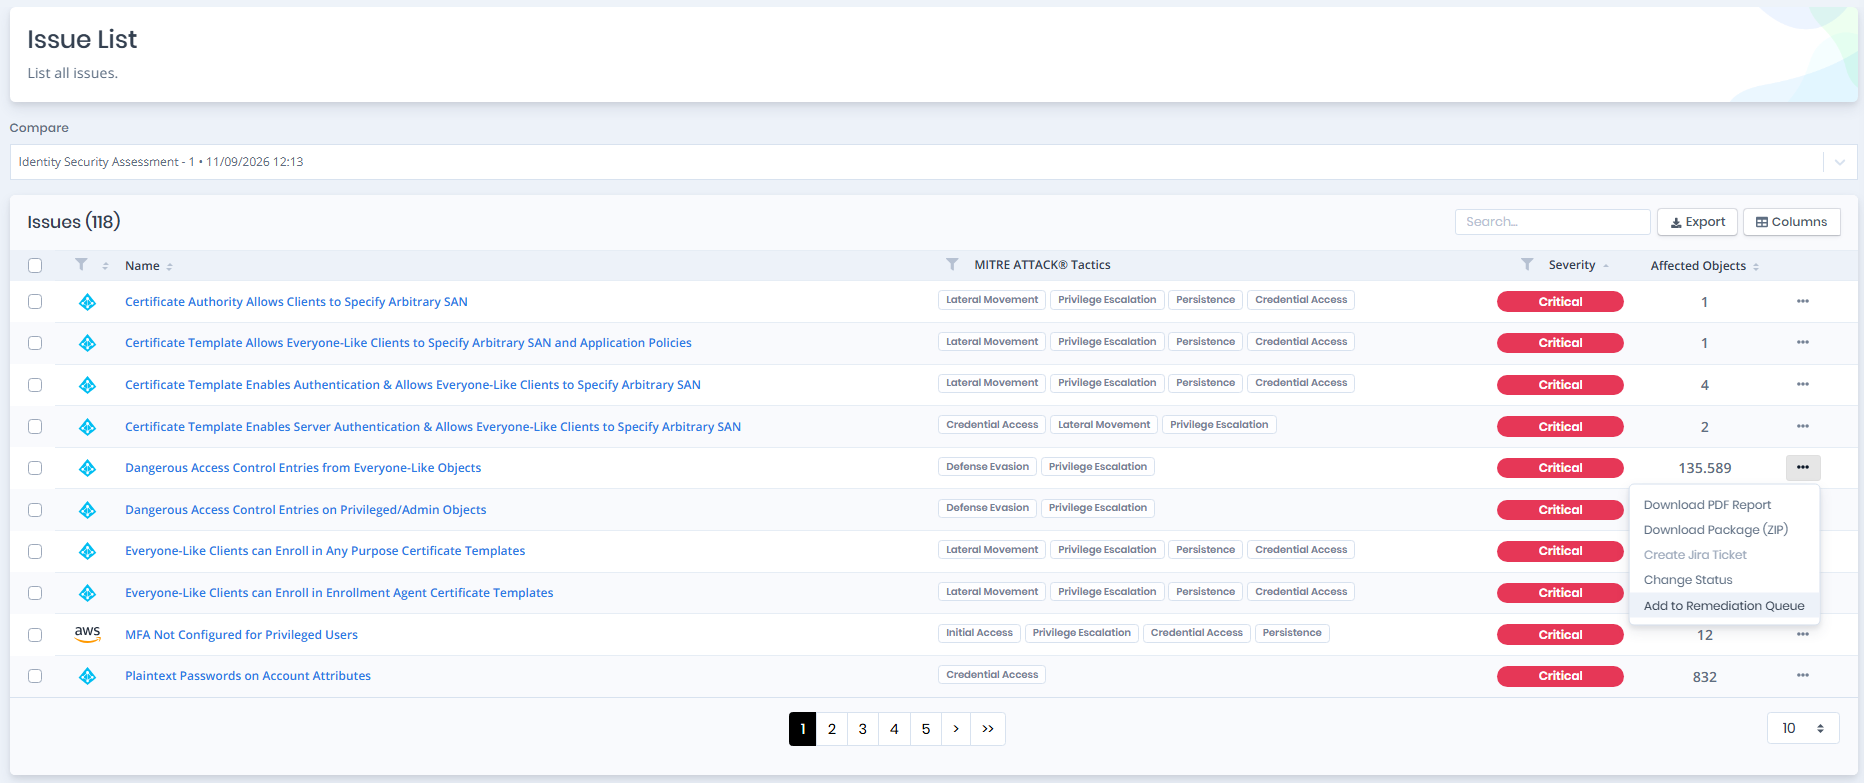
To verify an issue again, open the **Actions** menu for the issue and select **Add to Remediation Queue**.

An issue that is already in the queue carries an `In queue` badge in the list, so it is clear which findings the next remediation scan will re-verify without opening the queue.

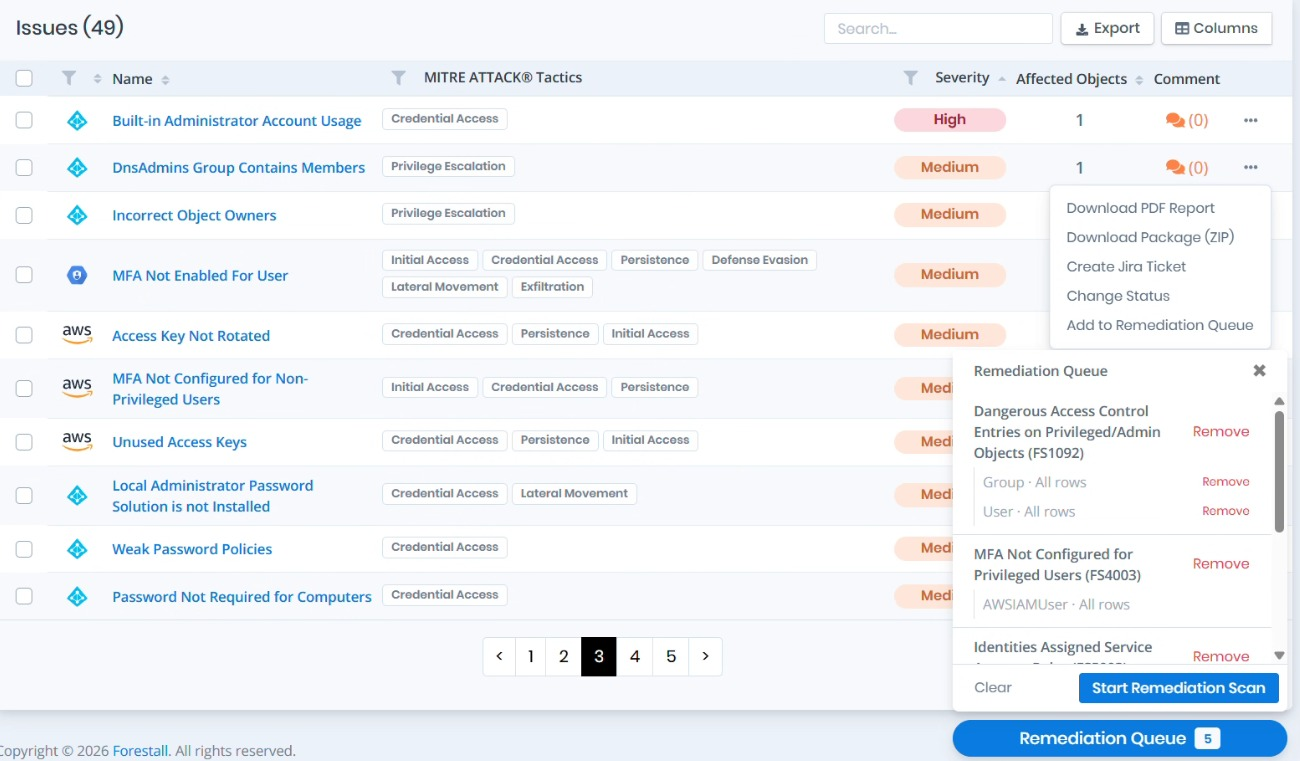
Multiple issues can be added to the same queue. The **Remediation Queue** appears at the bottom of the page and shows the issues and affected entity types currently selected for verification.

Items can be removed individually, or the entire queue can be cleared before starting the scan.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-d4107dec1f04ec02d0aba97becfb87aff0dc9c0a%2Fissues-image-4.png?alt=media" alt=""><figcaption><p><strong>Add to Remediation Queue</strong></p></figcaption></figure>

#### **Adding Multiple Issues**

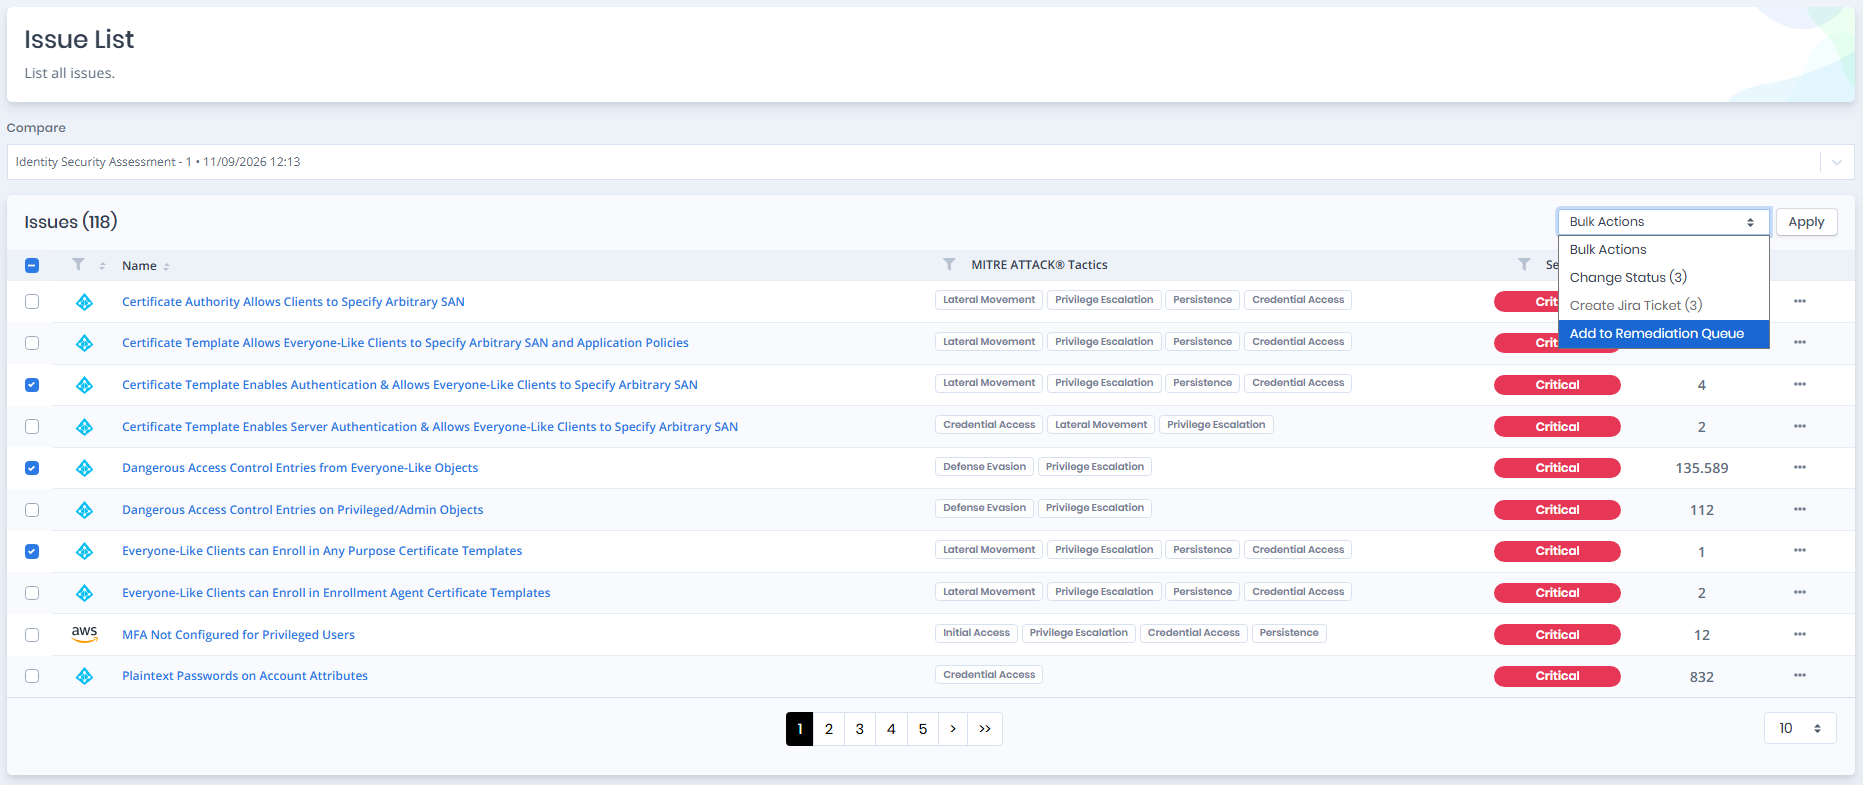
If you want to verify several issues at once, select the required rows from the Issues list and use **Bulk Actions** to add them to the **Remediation Queue**.

This allows multiple issues to be queued and verified together in a single remediation scan.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-b63d2ee381294a6b5731448d2292c61fea874255%2Fissues-image-5.png?alt=media" alt=""><figcaption><p>Bulk Actions</p></figcaption></figure>

#### Starting a Remediation Scan

After adding the required issues or affected entities, open the **Remediation Queue** and click **Start Remediation Scan**.

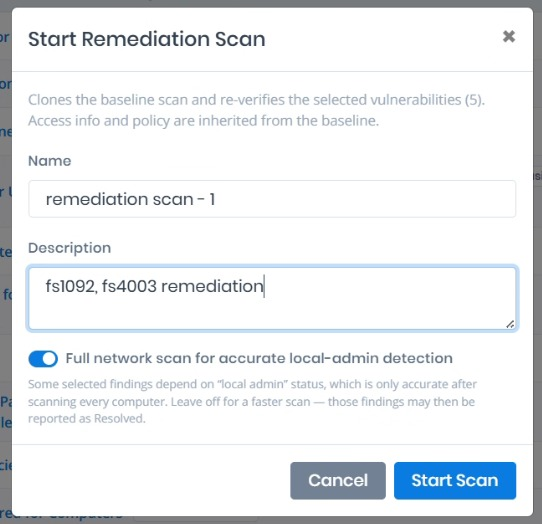
The **Start Remediation Scan** window allows you to define a name and description for the scan.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-4fd57fb55362b5c9a989e162d614b1e5f99bf031%2Fissues-image-6.png?alt=media" alt=""><figcaption><p>Adding issues to the Remediation Queue</p></figcaption></figure>

The following options are available:

| Option                                                   | Description                                                                                                                                           |
| -------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Name**                                                 | Specifies the name of the remediation scan.                                                                                                           |
| **Description**                                          | Optional information describing the purpose of the scan.                                                                                              |
| **Full network scan for accurate local-admin detection** | Performs a broader computer scan when the selected findings depend on local administrator information. This option is displayed only when applicable. |

The access information and scan policy are inherited from the original scan and do not need to be configured again.

Click **Start Scan** to begin the verification.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-832a5e2eecac6d21dfdf932c566eeb0cc51792cd%2Fissues-image-7.png?alt=media" alt=""><figcaption><p><strong>Start Scan</strong></p></figcaption></figure>

#### Reviewing Remediation Scan Results

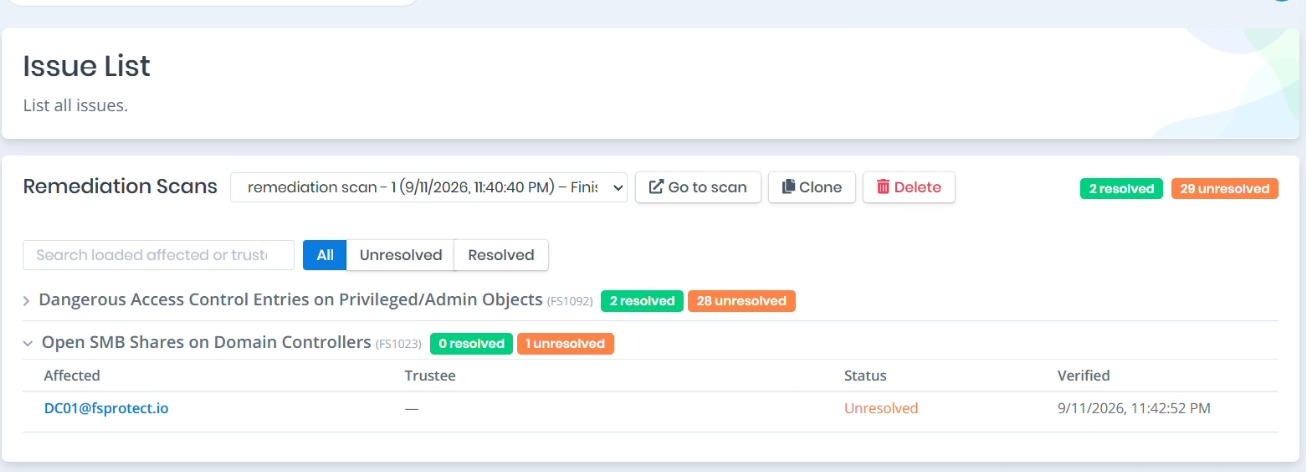
After the scan completes, its results are displayed in the **Remediation Scans** section of the original scan's Issues page.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-c9da766646bb6f24ad3c15a4286928207eebb66c%2Fissues-image-8.png?alt=media" alt=""><figcaption><p><strong>Remediation Scans results</strong></p></figcaption></figure>

Results are reported for each verified affected entity as:

* **Resolved** — the condition detected in the original scan is no longer present.
* **Unresolved** — the condition is still present.

The summary at the top of the section shows the total number of resolved and unresolved results.

Use **All**, **Unresolved**, and **Resolved** to filter the displayed results. Each issue can be expanded to review the affected entity, trustee when applicable, verification status, and the date and time the result was verified.

The **Remediation Scans** selector can also be used to switch between previous remediation runs associated with the same original scan.

Available actions include:

* **Go to scan** — opens the selected remediation scan.
* **Clone** — starts another remediation scan using the same selection.
* **Delete** — removes the selected remediation scan.

Remediation scans are associated with their original scan and are managed from the **Remediation Scans** section on the Issues page rather than the main Scans list.

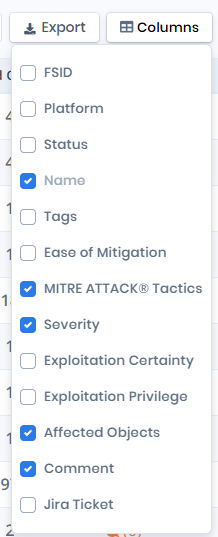
### Columns

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-1394e0f6de1755e94f3b6dc889f646418b4f35e8%2Fissues-image-9.png?alt=media" alt=""><figcaption><p>list of columns</p></figcaption></figure>

**FSID:** Unique identifier of the issue within the system.

**Platform:** Indicates the platform or technology related to the issue. The cell shows the provider logo rather than a name, so Active Directory, Entra ID, AWS, GCP and GitHub findings can be told apart at a glance in a scan that covers more than one provider. The column filter lists the same logos.

**Status:** Shows the current status of the issue (e.g. open, resolved).

**Name:** The name and short description of the detected issue.

**Tags:** Additional labels used to categorize or group issues.

**Ease of Mitigation:** Indicates how easily the issue can be mitigated.

**MITRE ATT\&CK® Tactics:** Shows the MITRE ATT\&CK tactics associated with the issue.

**Severity:** Indicates the risk level of the issue (e.g. Critical, High).

**Exploitation Certainty:** Shows how likely the issue can be exploited.

**Exploitation Privilege:** Indicates the privilege level required to exploit the issue.

**Affected Objects:** Shows the number of objects impacted by the issue.

**Comment:** Displays comments added to the issue.

**Jira Ticket:** Shows the Jira ticket associated with the issue, if available.

### Column-Based Filtering

The Issue List supports **column-based filtering**, allowing users to filter issues directly by specific column values.\
This enables faster analysis by narrowing down results based on attributes such as severity, MITRE ATT\&CK® tactics, or affected objects.

***

### Affected Objects Filter

The **Affected Objects** filter allows users to filter issues based on the **number of impacted objects**.\
By applying this filter, only issues affecting the specified number of objects or range are displayed, helping prioritize issues with wider impact.

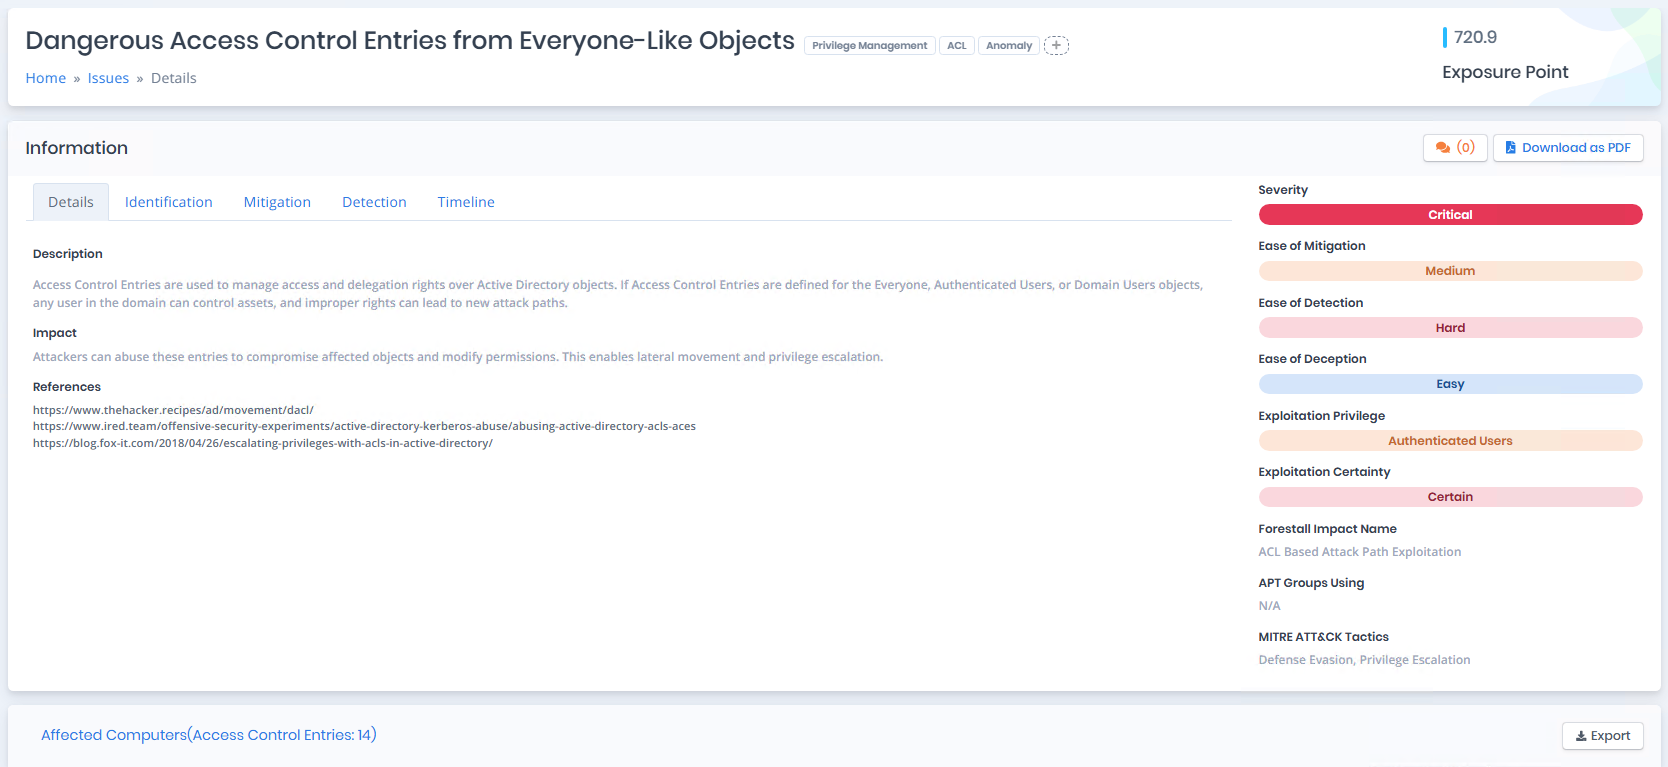
## Issue Details

Issue Details page provides all information and metrics about the identified Issue.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-5b3690eec6a9f46ca100910b789d2935c9bc37c6%2Fissue-details-1.png?alt=media" alt=""><figcaption><p>Issue Details</p></figcaption></figure>

The first pane contains `Issue Name` , `Tags`, `Global Custom Tags`, `Custom Tags`, and `Exposure Point`.

**Tags:** When adding custom tags, you can choose between two options:

`Global Custom Tag` or `Scan Specific Custom Tag`.

A `Global Custom Tag` will show up on the same issue in future scans, while a `Scan Specific Custom Tag` will only appear on issues related to a specific scan.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-3424a68468a11b8f5d45d406fd5a6d9bd1b6bb7b%2Fadd%20tag.png?alt=media" alt=""><figcaption><p>Add Issue Tag</p></figcaption></figure>

The `Information` pane contains 6 tabs; `Details`, `Identification`, `Mitigation`, `Detection`, `Timeline` and `Compliance`. Also, there is a summary pane on the right side that shows different metrics about the issue.

The `Download` button on the upper-right side of this pane offers two options; `Finding (PDF)` exports the issue as a PDF report, and `Finding Package (ZIP)` exports a self-contained archive with the report and its affected-entity evidence. The package option requires the `DownloadReportPackage` permission.

Details tab contains `Description`, `Impact` and `References`.

**Exposure Point**: vulnerabilities are assessed based on their risk level. A higher Exposure Point indicates a more critical security flaw, while a lower Exposure Point represents a less risky vulnerability.

**Description**: Description contains detailed information about the root cause of the issue and how to exploit it. Also, explanations about related technologies, services, protocols, and inventory types reside here.

**Impact**: Impact explains, how attackers can exploit this issue and what is the effect of this process on Active Directory.

**References**: References contain multiple articles and blog posts for further reading about this issue.

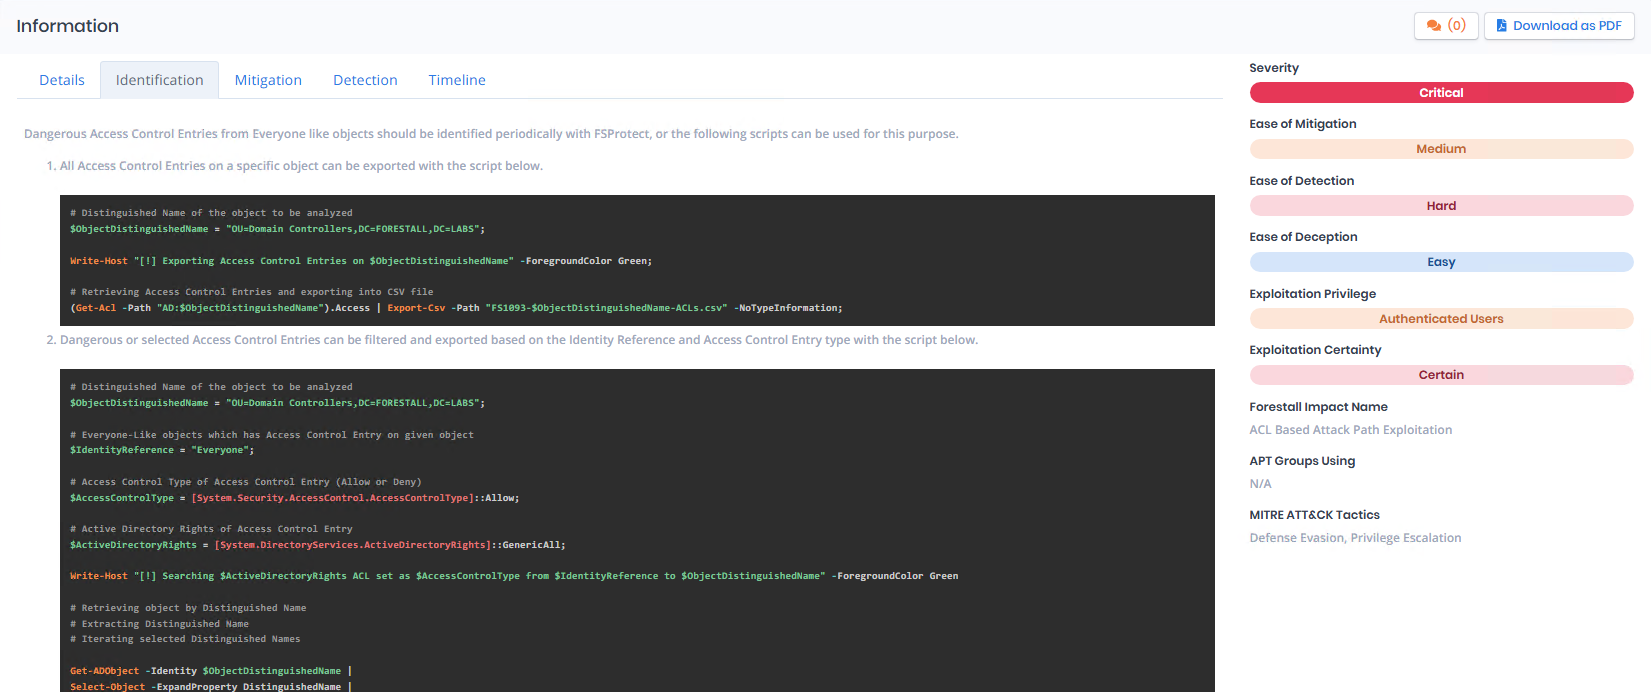
### Identification

Identification tab contains a detailed step-by-step walkthrough about how to identify and verify this issue manually. This walkthrough contains screenshots, manuals, and Powershell or Batch scripts to automatize the identification process. With this roadmap, analysts can manually identify and verify the issue for eliminating false positives.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-ef2d440678bc595f3f9aafe66e9c6851bd732847%2Fissue-identification-1.png?alt=media" alt=""><figcaption><p>Identification</p></figcaption></figure>

### Mitigation

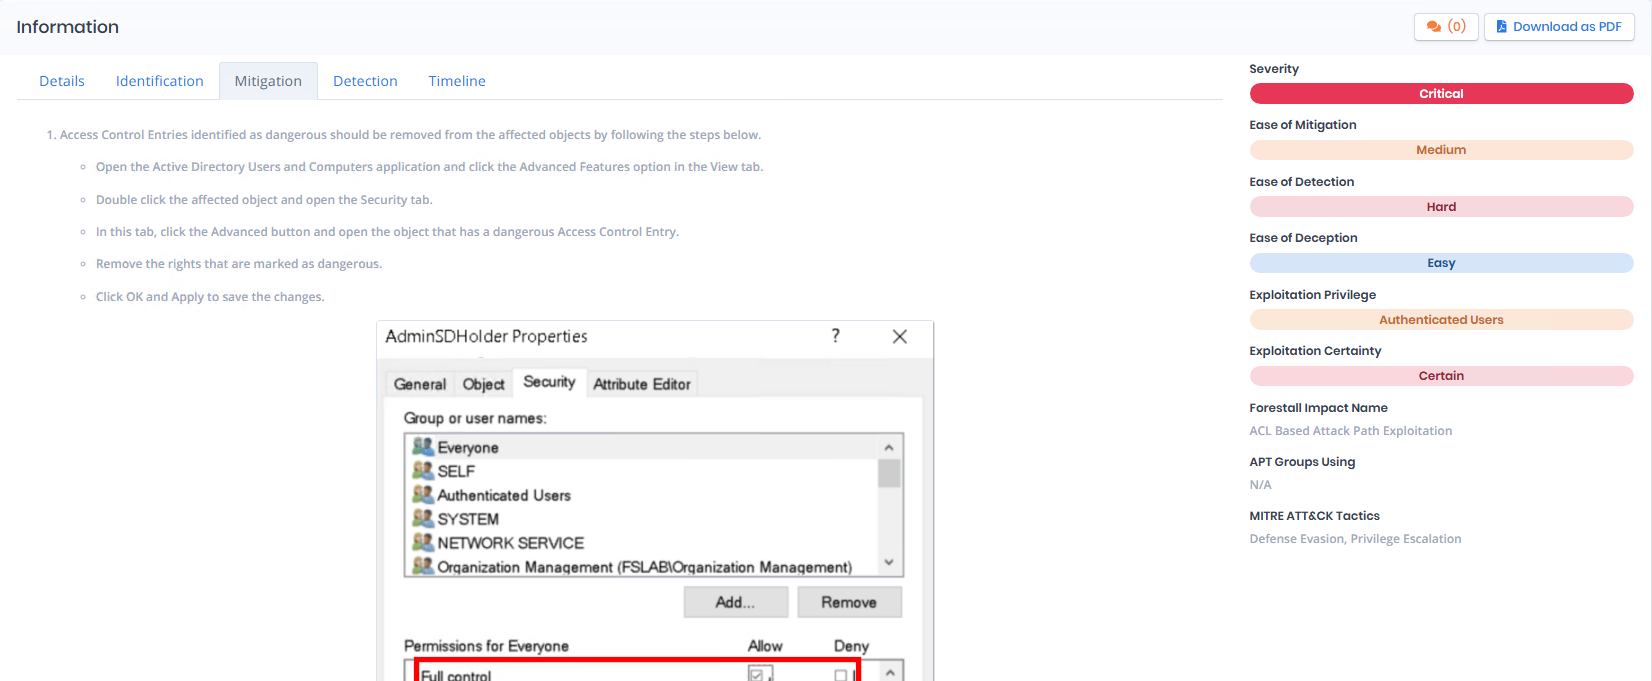
Mitigation tab also contains a detailed step-by-step walkthrough about how to mitigate/remediate issues or implement a workaround with minimum effort. This walkthrough contains manuals and Powershell or Batch scripts to automatize the mitigation process. With these manuals, system administrators can easily and safely remediate identified issues.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-68c94da1f0abe05683f46eab8fefff9192bc7be5%2Fissue-mitigation-1.png?alt=media" alt=""><figcaption><p>Mitigation</p></figcaption></figure>

### Detection

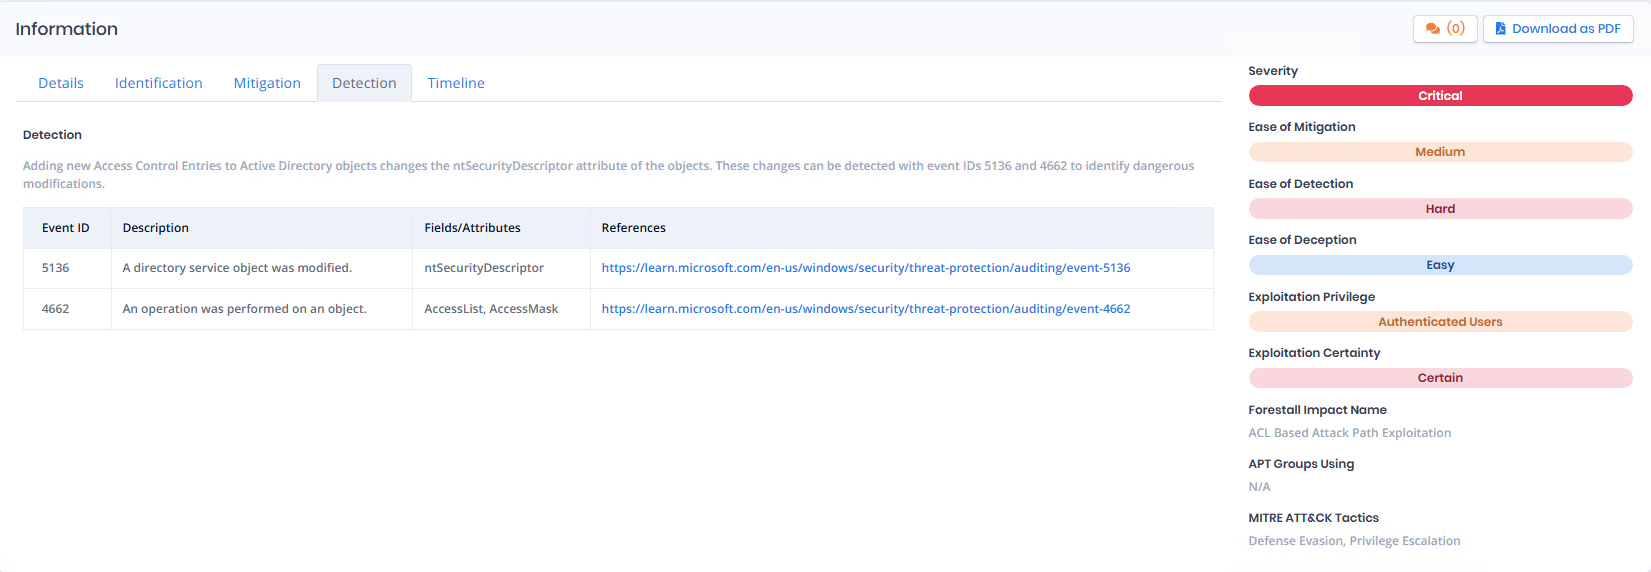
Detection tab contains methods, log sources, and Event Log IDs to detect possible exploitations of this issue. With this information, analysts can speed up their process to create detection rules for SIEM or different security products.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-ce07c1074f2cd53c5c9d2f497106ea3c231d6281%2Fissue-detection-1.png?alt=media" alt=""><figcaption><p>Detection</p></figcaption></figure>

### Timeline

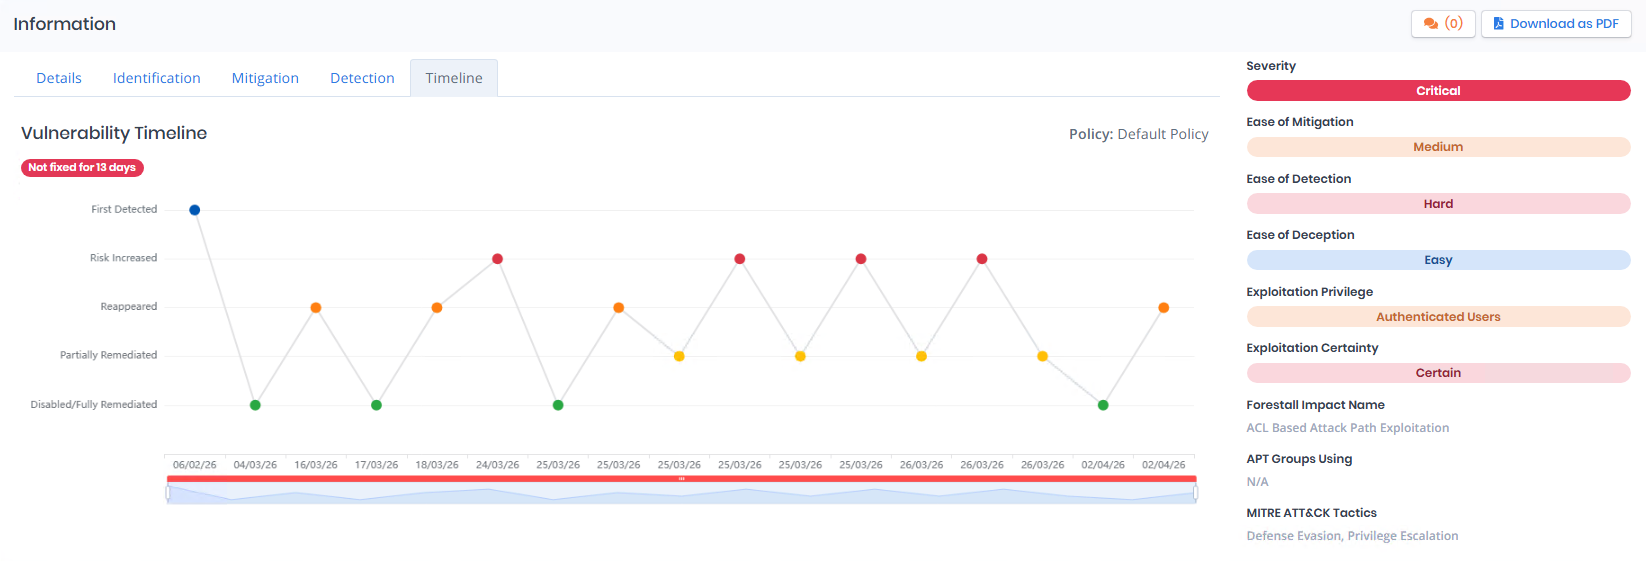
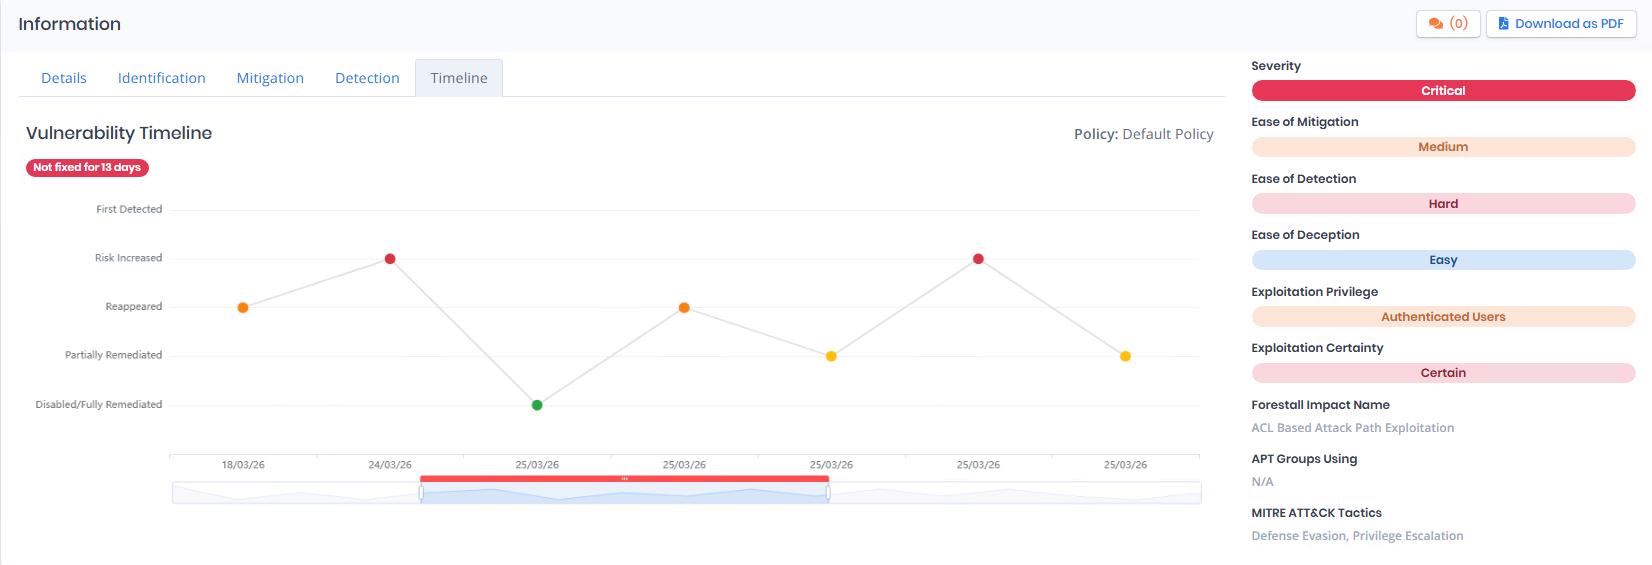
Timeline tab contains a Timeline chart. This chart displays the distribution of issue statuses over time, along with other scans that share the same policy as the selected scan. Additionally, this tab allows viewing the policy used in the scan and the number of days the vulnerability has remained unresolved.

Five status changes are shown in the chart: `First Detected`**,** `Risk Increased`**,** `Reappeared`**,** `Partially Remediated` and `Disabled` or `Fully Remediated`.

With this chart, issue statuses can be easily tracked over time.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-ef93e0a071cc6468ab7b6a2a12f3aaa09fef3eb1%2Fscan-timeline-1.PNG?alt=media" alt=""><figcaption><p>Timeline Chart</p></figcaption></figure>

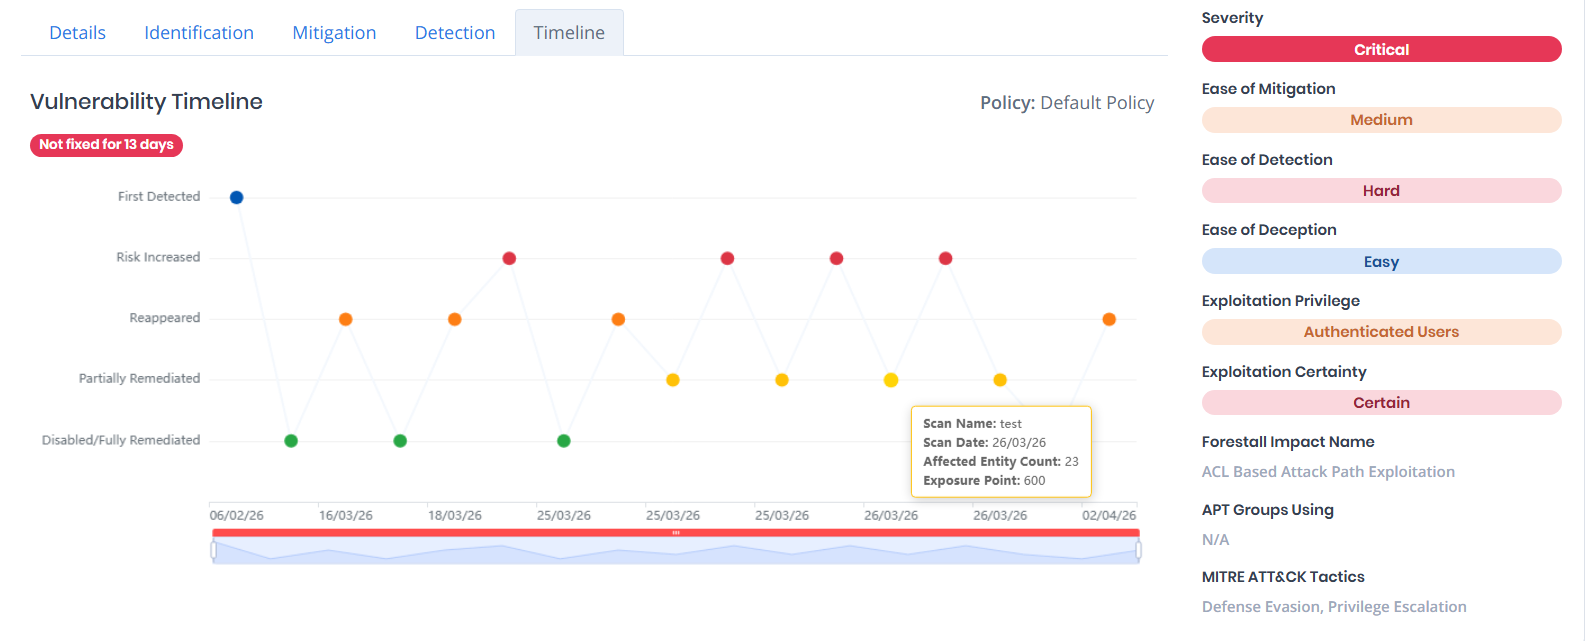
Each data point in the chart represents a scan. Hovering over a data point provides detailed information about the corresponding scan. Fields such as `Scan Name`, `Date`, `Affected Entity Count,` and `Exposure Point` are displayed. In addition, a badge is displayed when the status is Disabled or Fully Remediated.

Furthermore, clicking on a data point allows affected entity comparison with the current scan.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-c8a85530a6b9cf7dd6652af12abf37feecd09a9f%2Fscan-timeline-2.PNG?alt=media" alt=""><figcaption><p>Data Point Hovered Timeline Chart</p></figcaption></figure>

The chart can also be resized from the bottom to control how many scans are displayed and can be navigated across different dates.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-c0b8138080ab407765ab6cb5c17ad64e34061862%2Fscan-timeline-3.png?alt=media" alt=""><figcaption><p>Resized Timeline Chart</p></figcaption></figure>

### Compliance

The Compliance tab lists the compliance frameworks and controls this issue is mapped to, and the tab label shows how many controls are affected. Each entry links to the matching control on the [Compliance](/fsprotect/compliance.md) page.

Only the frameworks selected on the scan policy are listed. See [Compliance Frameworks](/fsprotect/scans/policies.md#compliance-frameworks).

### Affected Objects

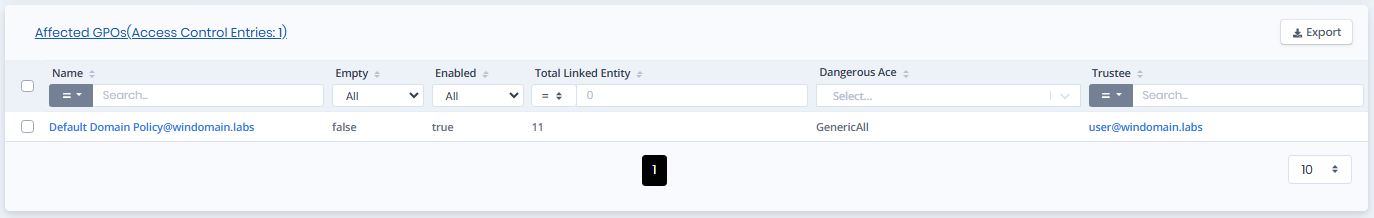
This area can contain multiple tables for each entity type that is affected by this issue. These tables contain affected entities and different issue-related information. These tables also provide `Sort`, `Search`, `Export`, `Limit`, and `Pagination` functions like other tables in the web interface. For further analysis, you can go to the affected object's details page by clicking the `Name`.

Once a [Remediation Scan](#remediation-scan) has run for the issue, the tables also contain a `Remediation` column showing whether each object was verified as `Resolved`, `Unresolved` or `Unverified`, together with the date of the last check. The column can be filtered by remediation status.

When the Splunk integration is configured, the stale-reason cell reads `Actively in use` with a date for a permission that recent activity confirms is still being used.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-fb4d1820bcb88dbcf81b0712ec7d448ad56a47ca%2Fissues-image-10.png?alt=media" alt=""><figcaption><p>Affected Objects</p></figcaption></figure>

### Row Based Exclusion

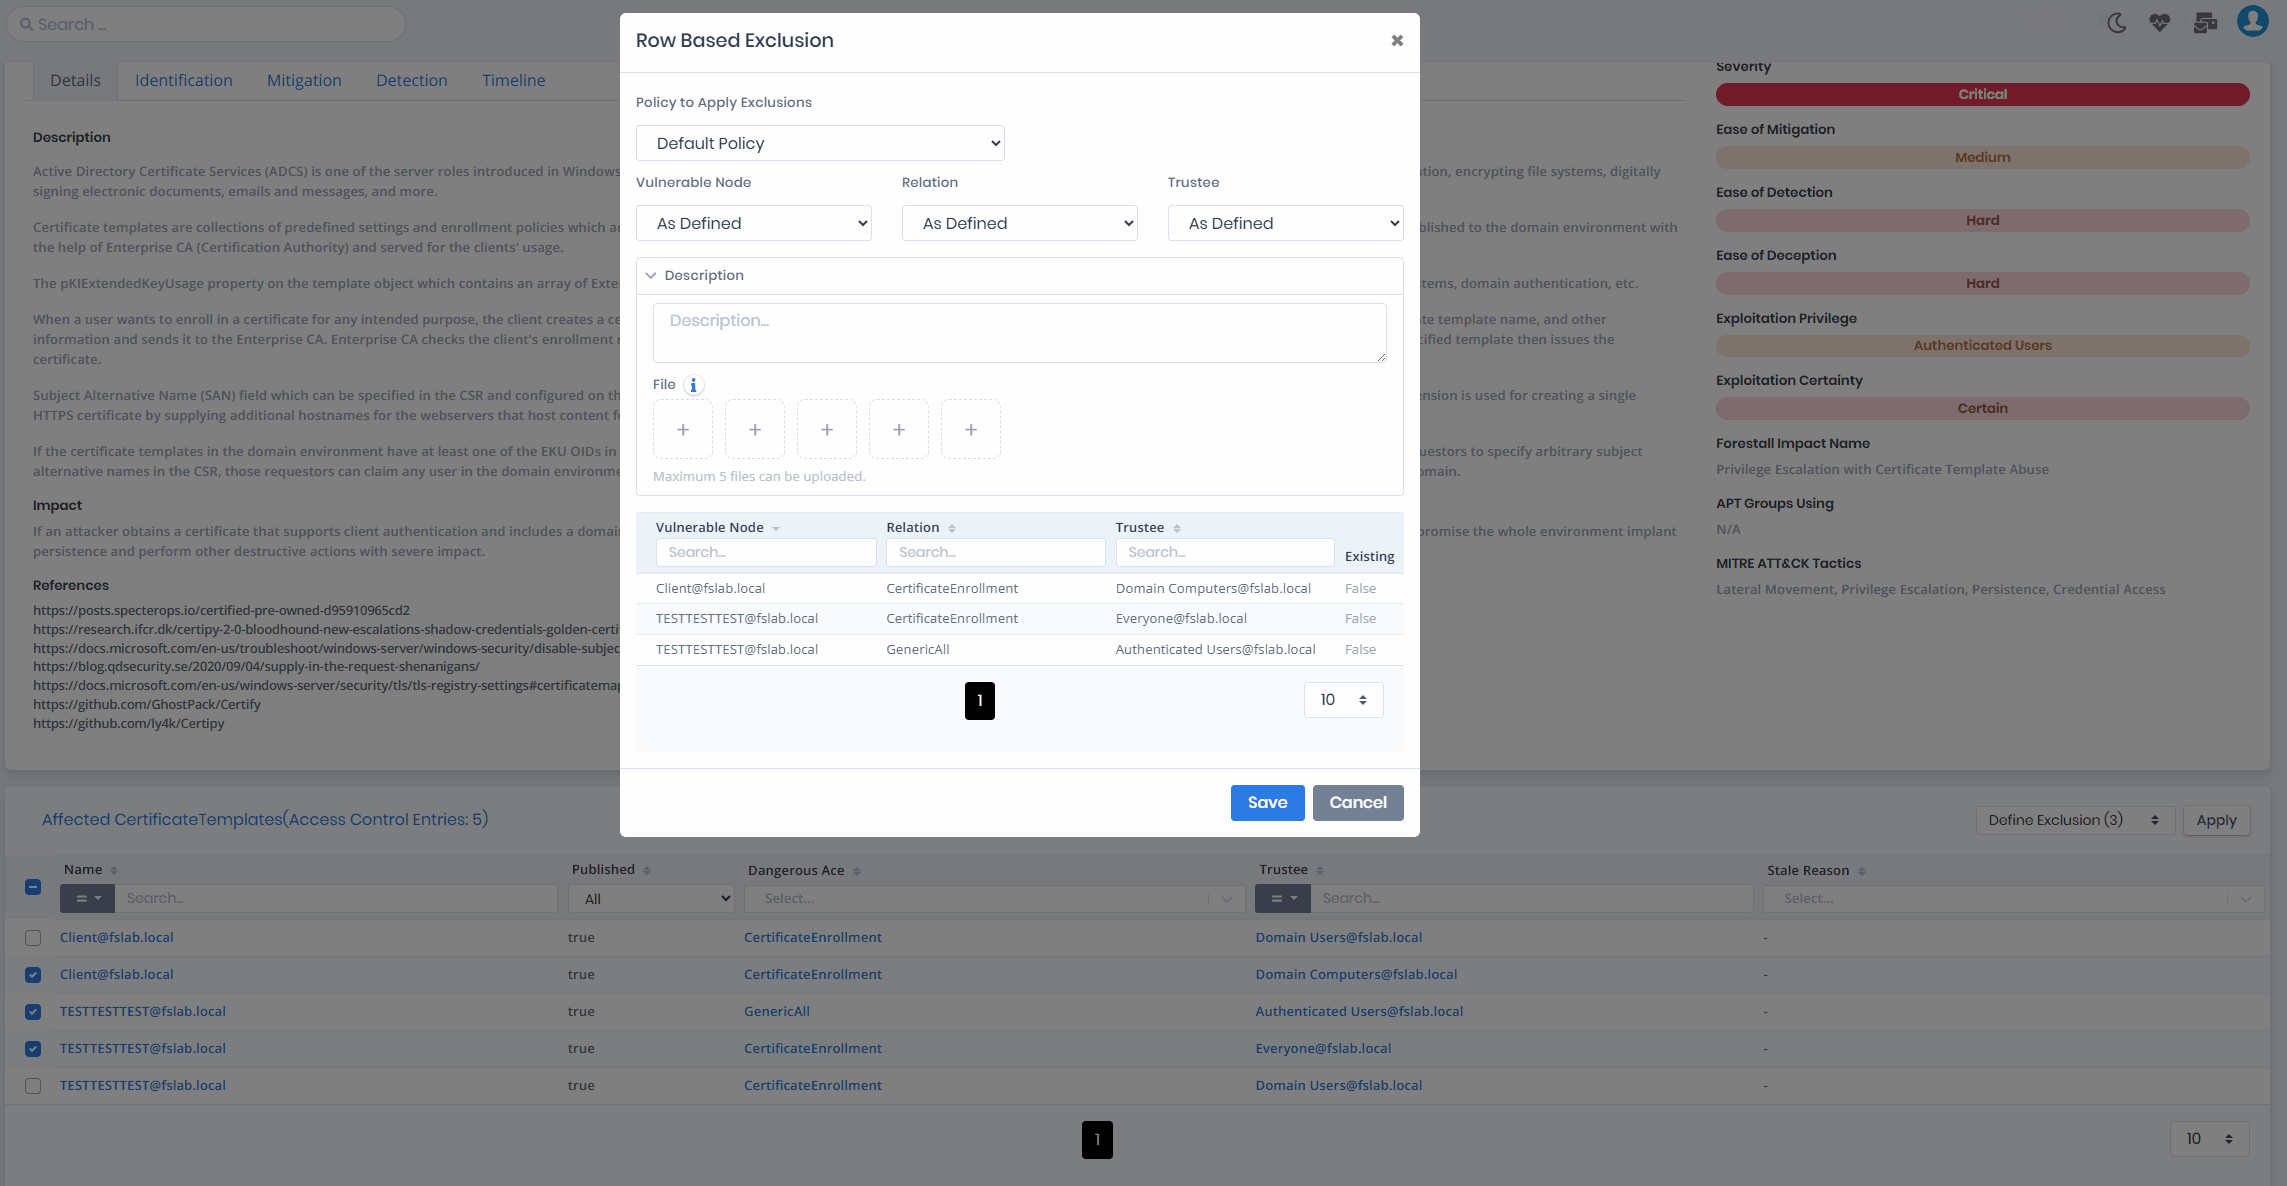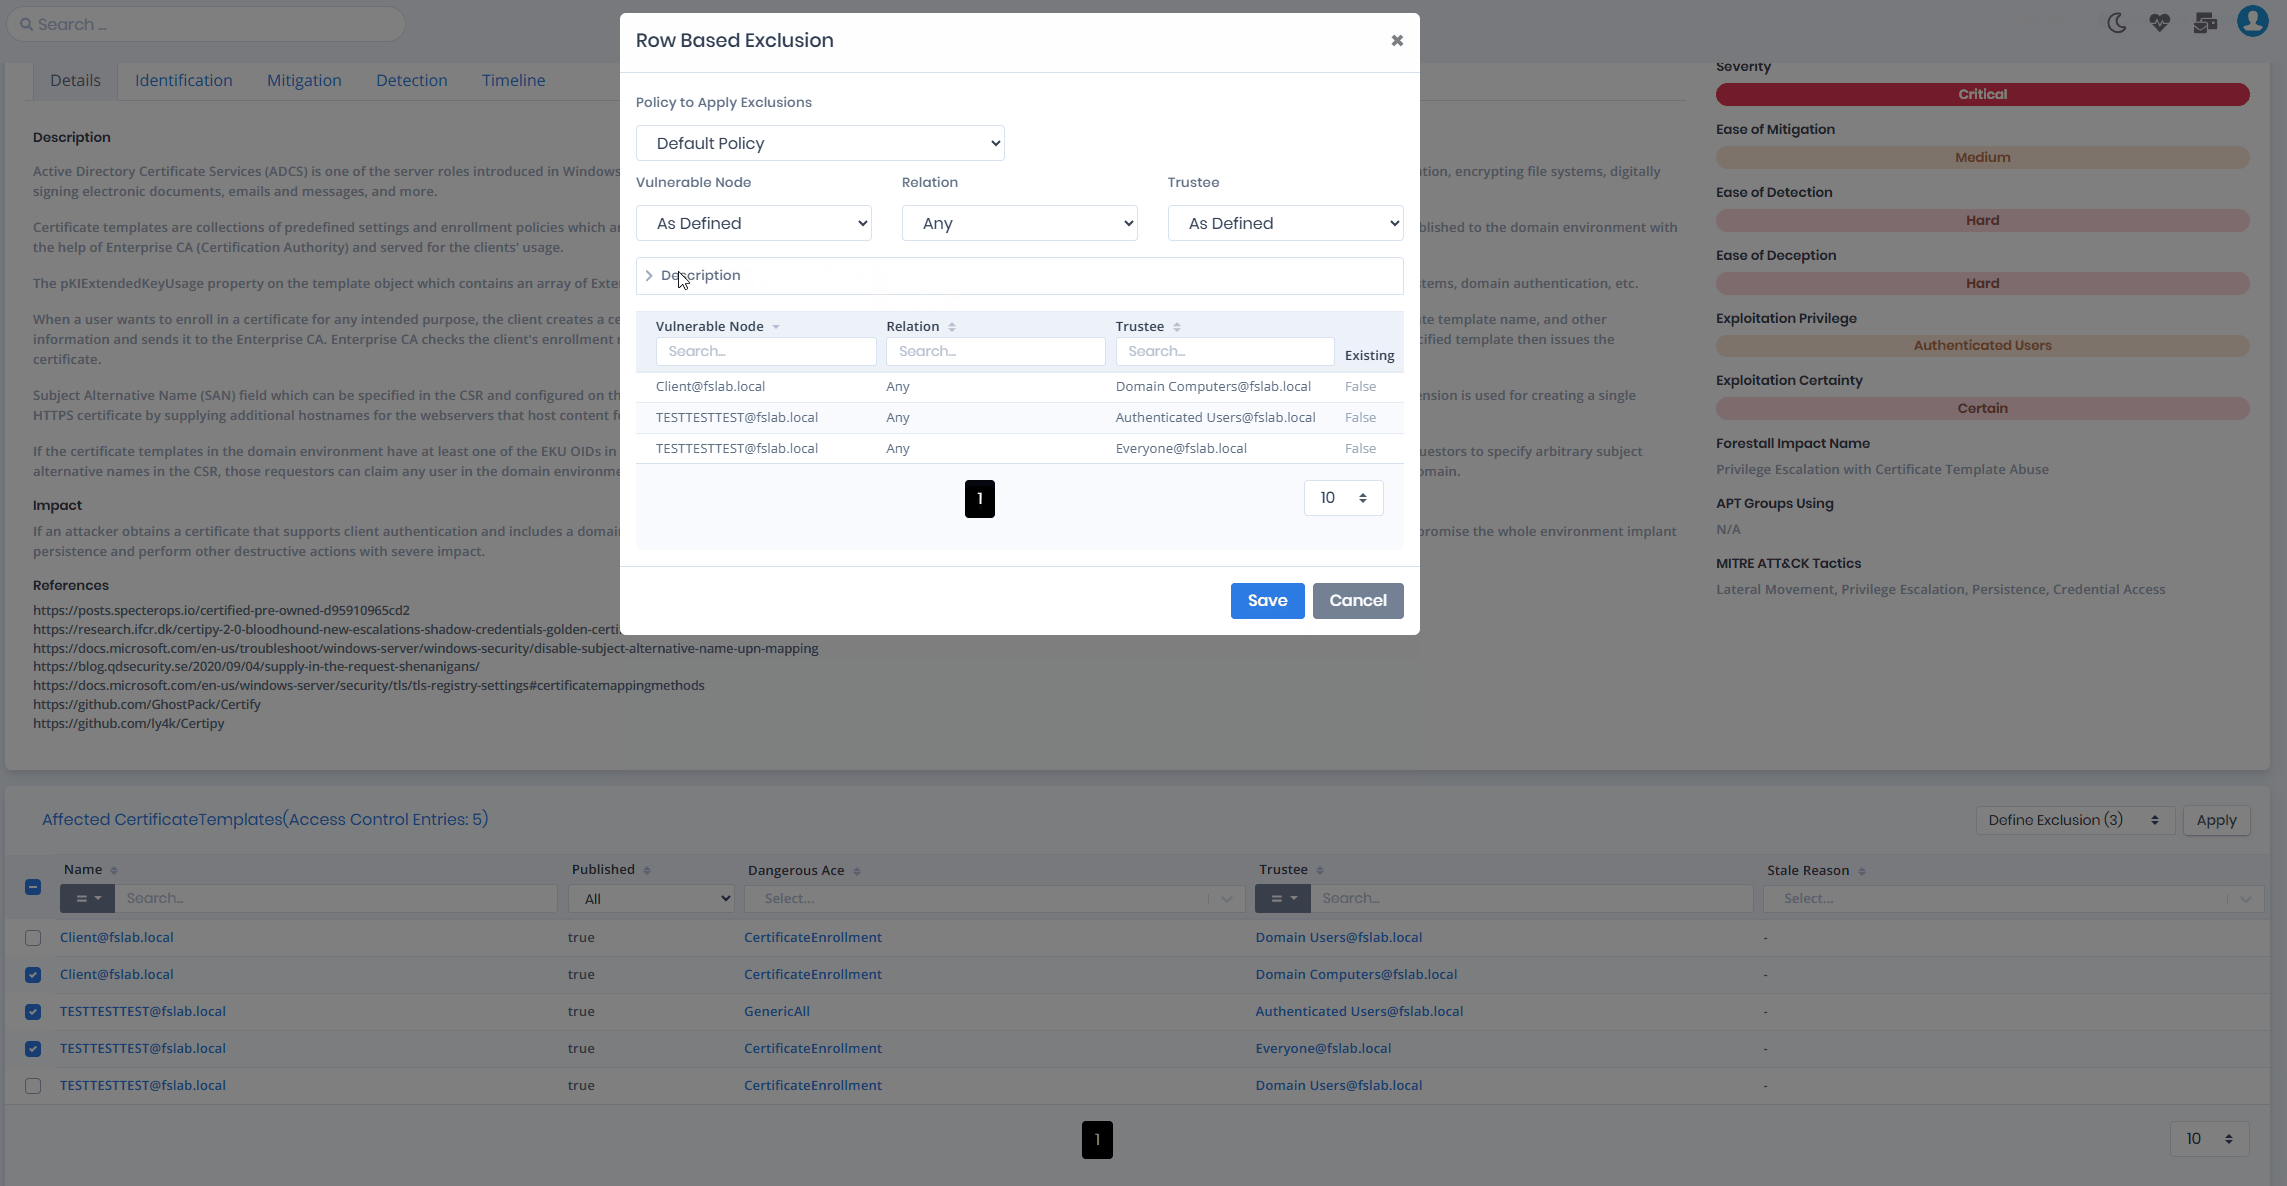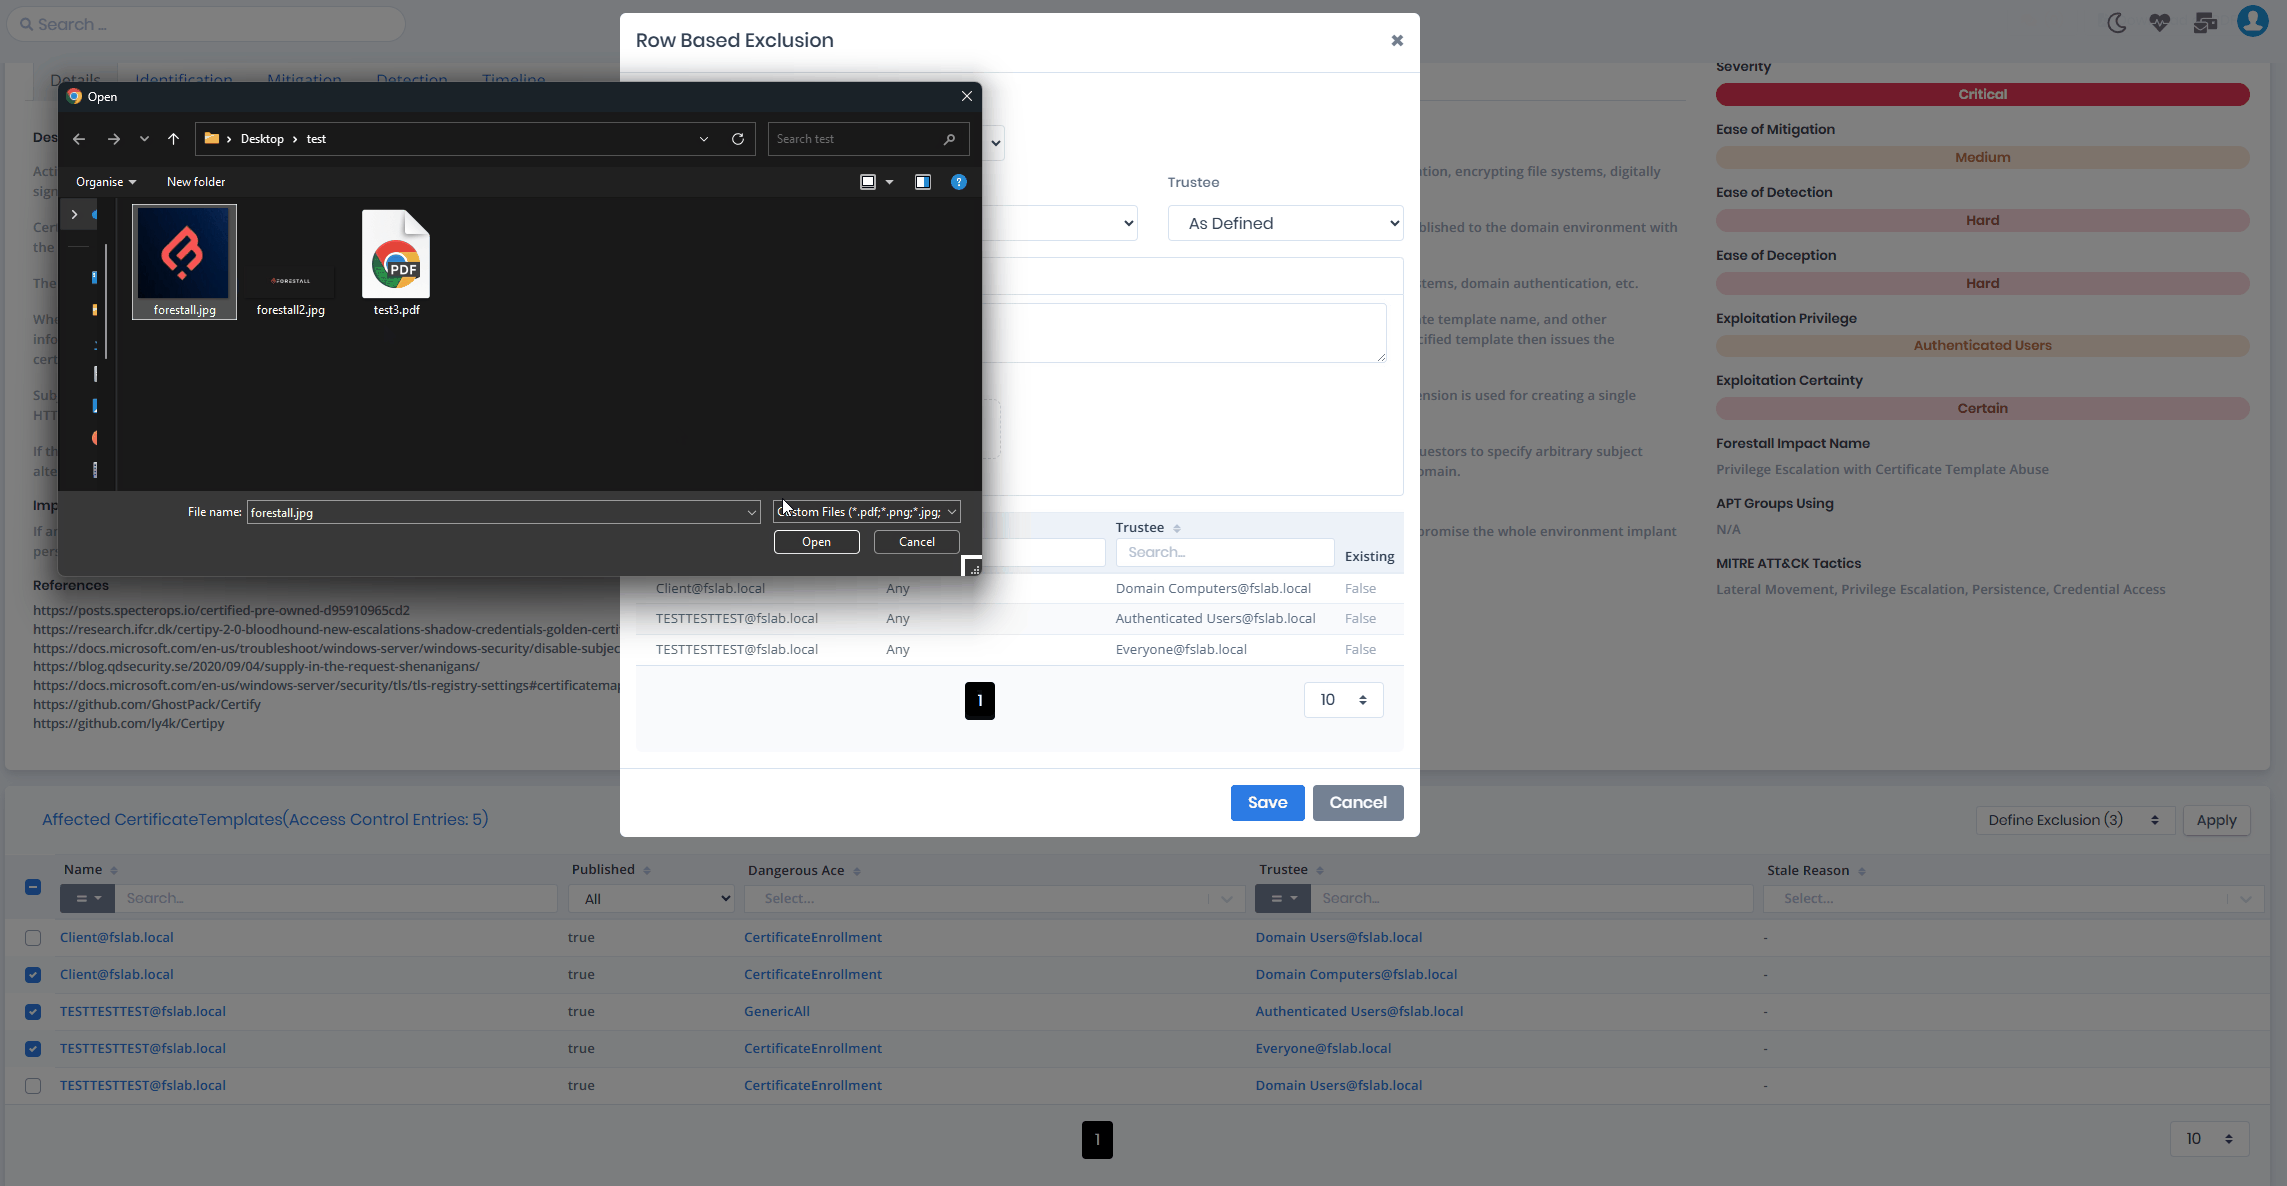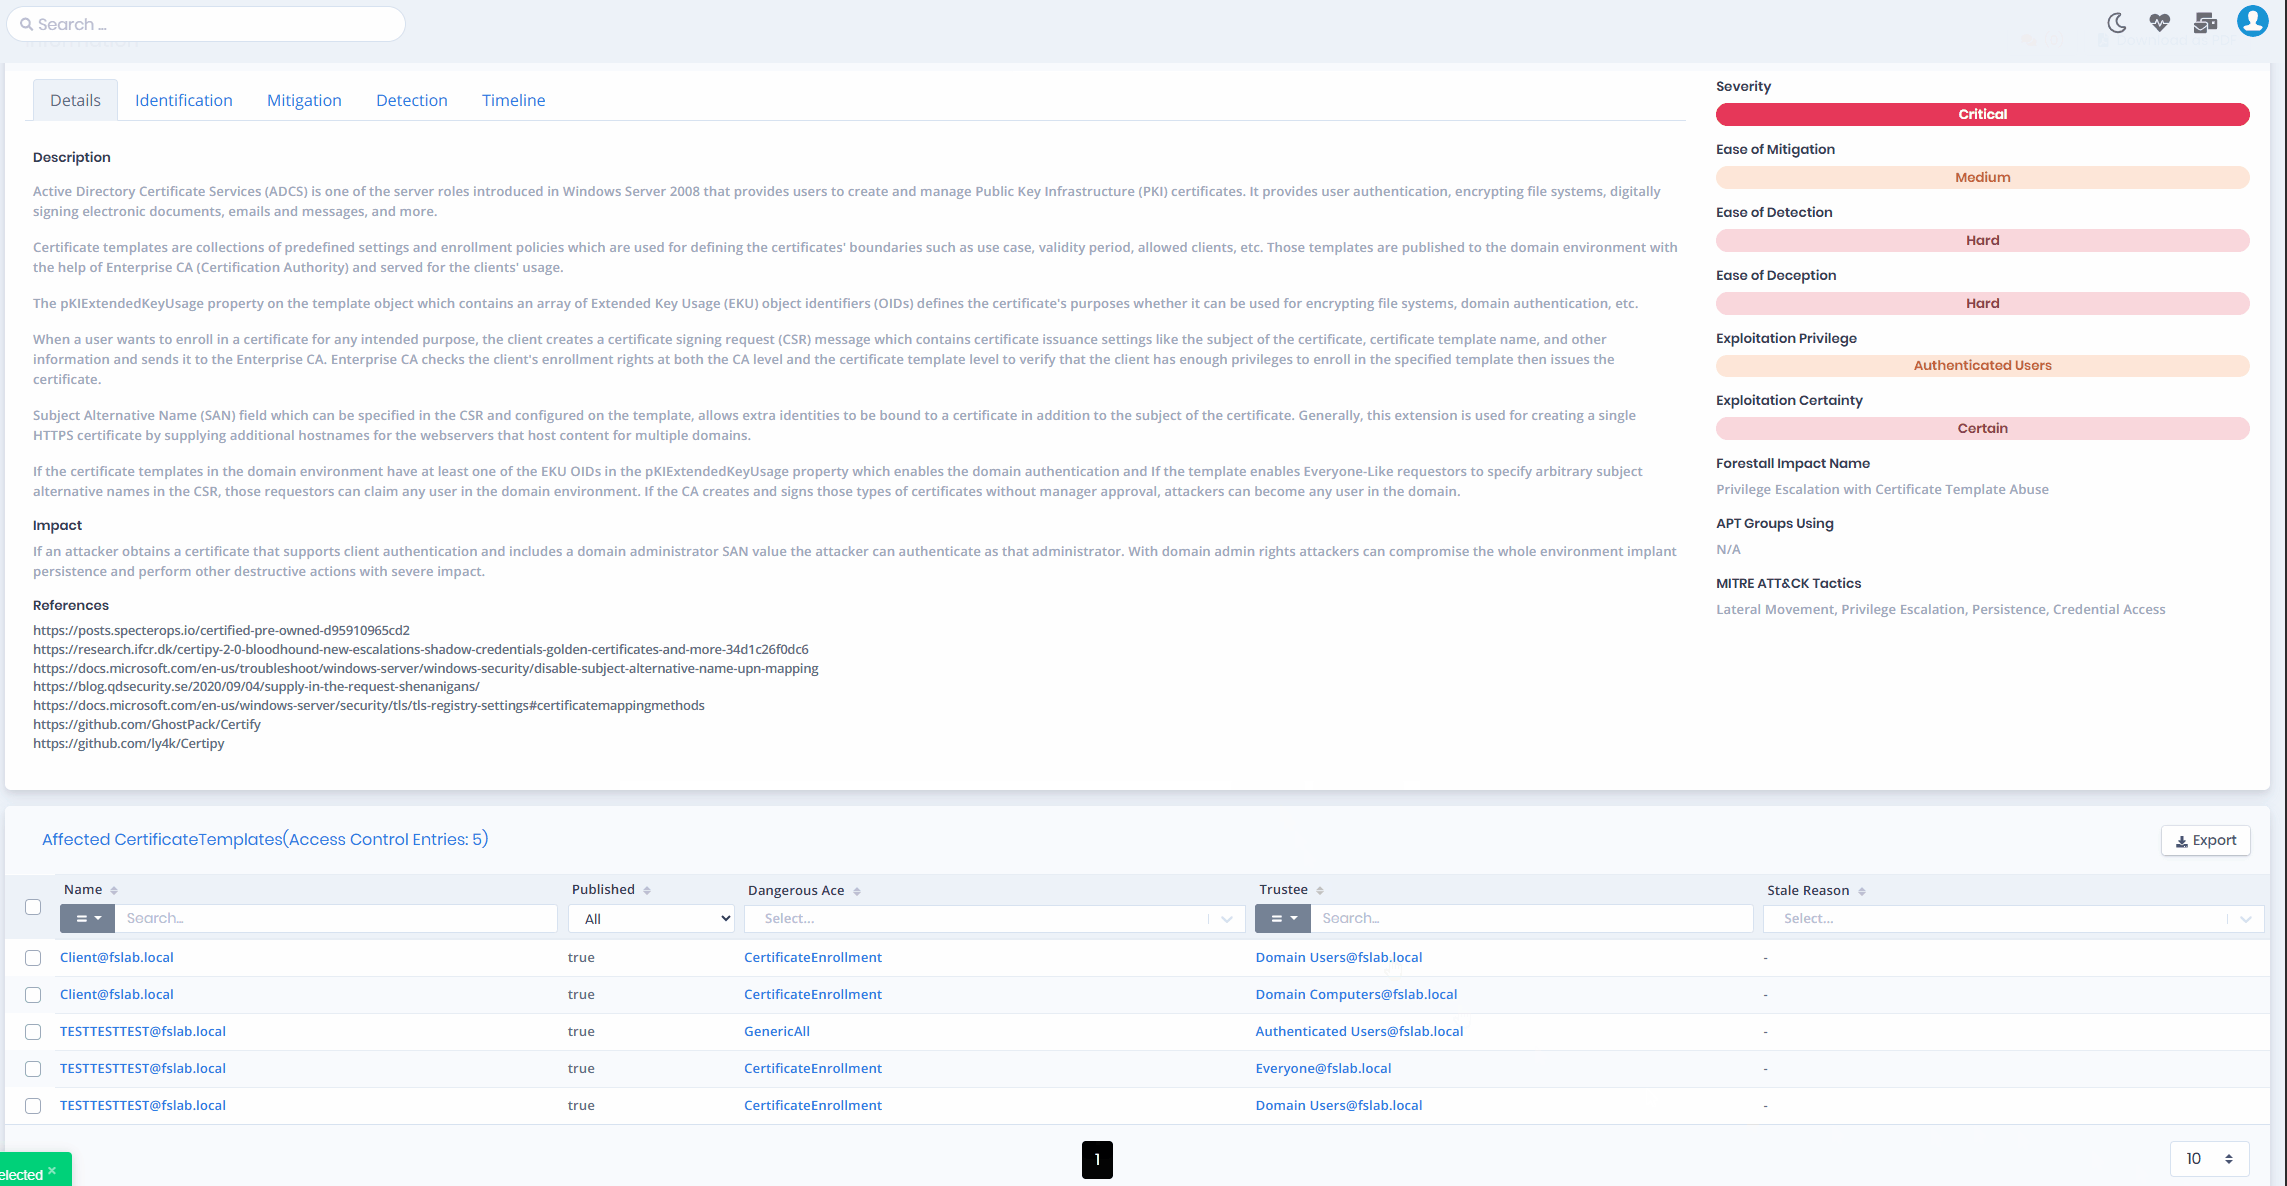
Row-Based Exclusions provide the ability to create exclusions for rows, either individually or in bulk, within a selected scan policy. Exclusions are defined based on the exclusion type and relevant criteria. By allowing exclusions to be defined on results, this feature simplifies and accelerates the exclusion definition process. These exclusions can be modified at any time through the policy settings.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-462b79defb719046e9fee37f68ec6f63a011189d%2Fgif%20affected%20row.gif?alt=media" alt=""><figcaption></figcaption></figure>

#### Row Based Exclusion Description and Files

Each row-based exclusion can include an optional description and supporting files such as PDF and image documents.

Existing descriptions and supporting files will be overwritten when the same exclusion is added again.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-175e28d7d39a2e9ecd02fe5f746e3161d182c6a6%2Frow_based_exclusion_description.gif?alt=media" alt=""><figcaption></figcaption></figure>

### **Summary Pane**

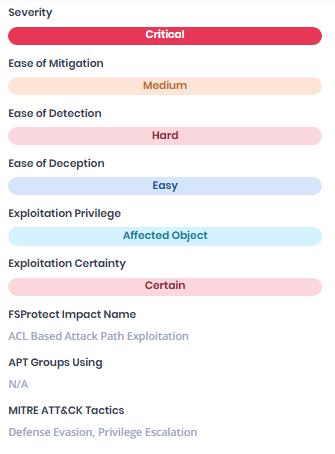
Summary pane on the right-upper side contains `Severity`, `Ease of Mitigation`, `Ease of Detection`, `Ease of Deception`,`Exploitation Privilege`, `Exploitation Certainty` ,`FSProtect Impact Name`, `APT Group Using`, and `MITRE ATT&CK Tactics`.

<figure><img src="https://3408039743-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FObpV44hoVkNmo5bFuVVL%2Fuploads%2Fgit-blob-eae5cc78a203ae5935b06f9aa521ebe0b4788c3d%2Fissues-image-11.png?alt=media" alt=""><figcaption></figcaption></figure>

**APT Group Using**: APT groups that exploit this issue to compromise Active Directory.

**MITRE ATT\&CK Tactics**: MITRE ATT\&CK Tactics related to this issue.

Details about `Severity`, `Ease of Mitigation`, `Ease of Detection`, `Ease of Deception`,`Exploitation Privilege`, `Exploitation Certainty` and `FSProtect Impact Name` metrics can be found on the [Glossary](/fsprotect/readme-1/glossary/glossary.md).